
ISO 27001 Network Security Policy
In this guide, you will learn what an ISO 27001 Network Security Policy is, how to write it yourself and I give you a template you can download and use right away.
Table of contents
- ISO 27001 Network Security Policy
- What is an ISO 27001 Network Security Policy?
- ISO 27001 Network Security Policy Example
- How to write an ISO 27001 Network Security Policy
- ISO 27001 Network Security Management Policy Template
- Everything you need to know
- How the ISO 27001 toolkit can help
- Applicability of an ISO 27001 Network Security Policy to Small Businesses, Tech Startups, and AI Companies
- Information security standards that need an ISO 27001 Network Security Policy
- List of relevant ISO 27001:2022 controls
- ISO 27001 Network Security Policy FAQ
What is an ISO 27001 Network Security Policy?
An ISO 27001 Network Security Management Policy is your company’s rulebook for keeping your computer network safe. It’s like having a security guard for all the digital roads and paths that connect your computers. This policy makes sure only the right people and devices can get in and that your data is protected while it’s moving around.
This policy is a set of guidelines that tells everyone how to protect your network. It covers things like using firewalls, setting up secure Wi-Fi, and making sure all your devices have the right security settings. The main goal is to prevent unauthorised access and protect your network from cyber threats like hackers or malware.

ISO 27001 Starter Kit
Instant download of mandatory ISMS core policies and documentation. Verified by Lead Auditors and used by 5,000+ businesses worldwide to pass Stage 1 certification first time.
ISO 27001 Network Security Policy Example
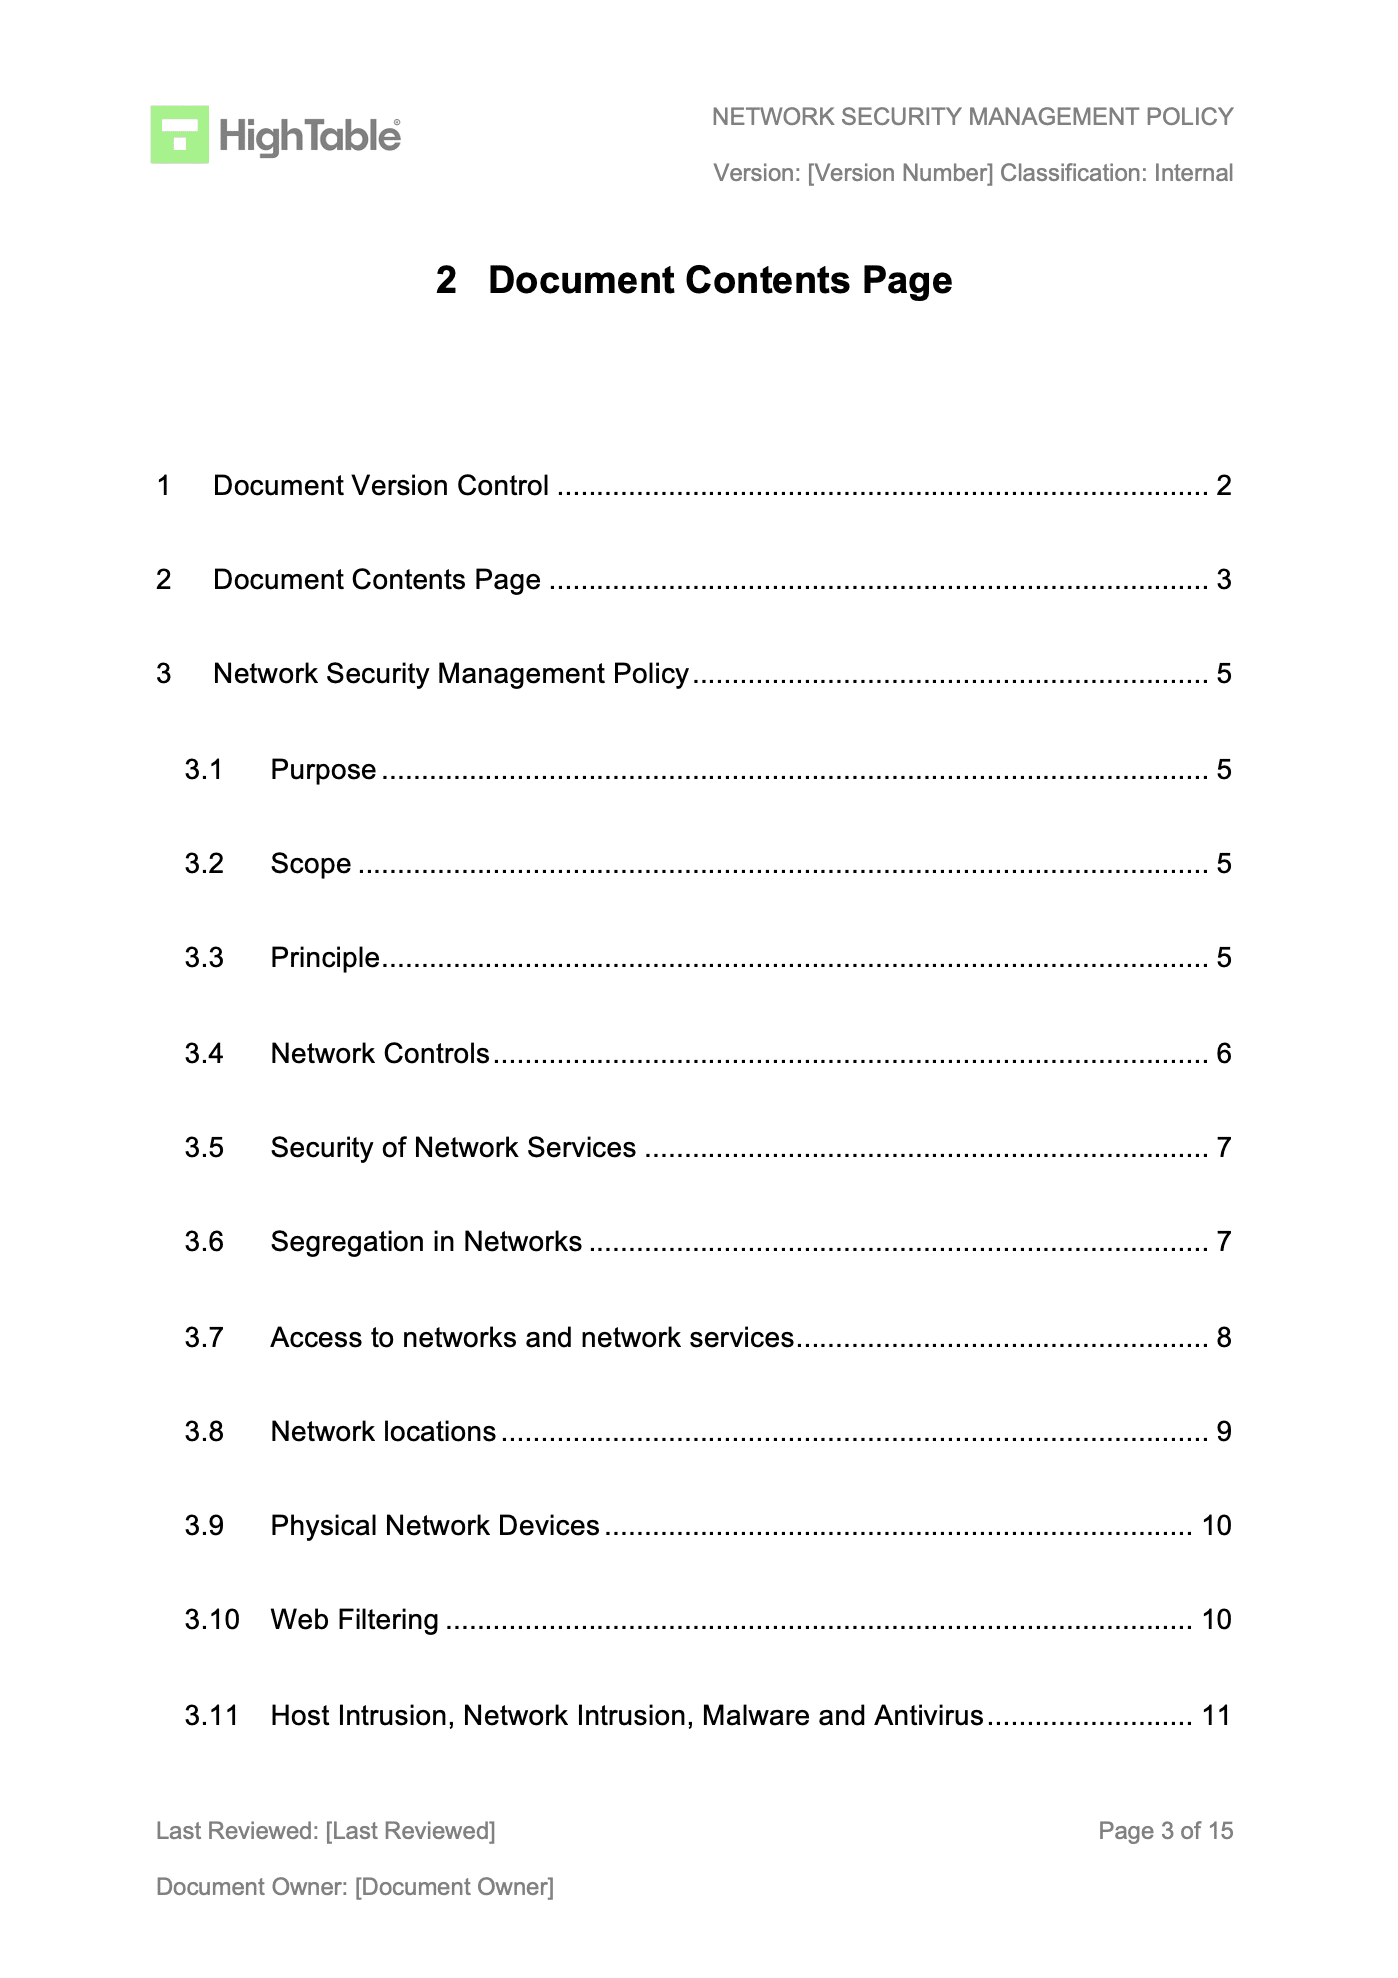
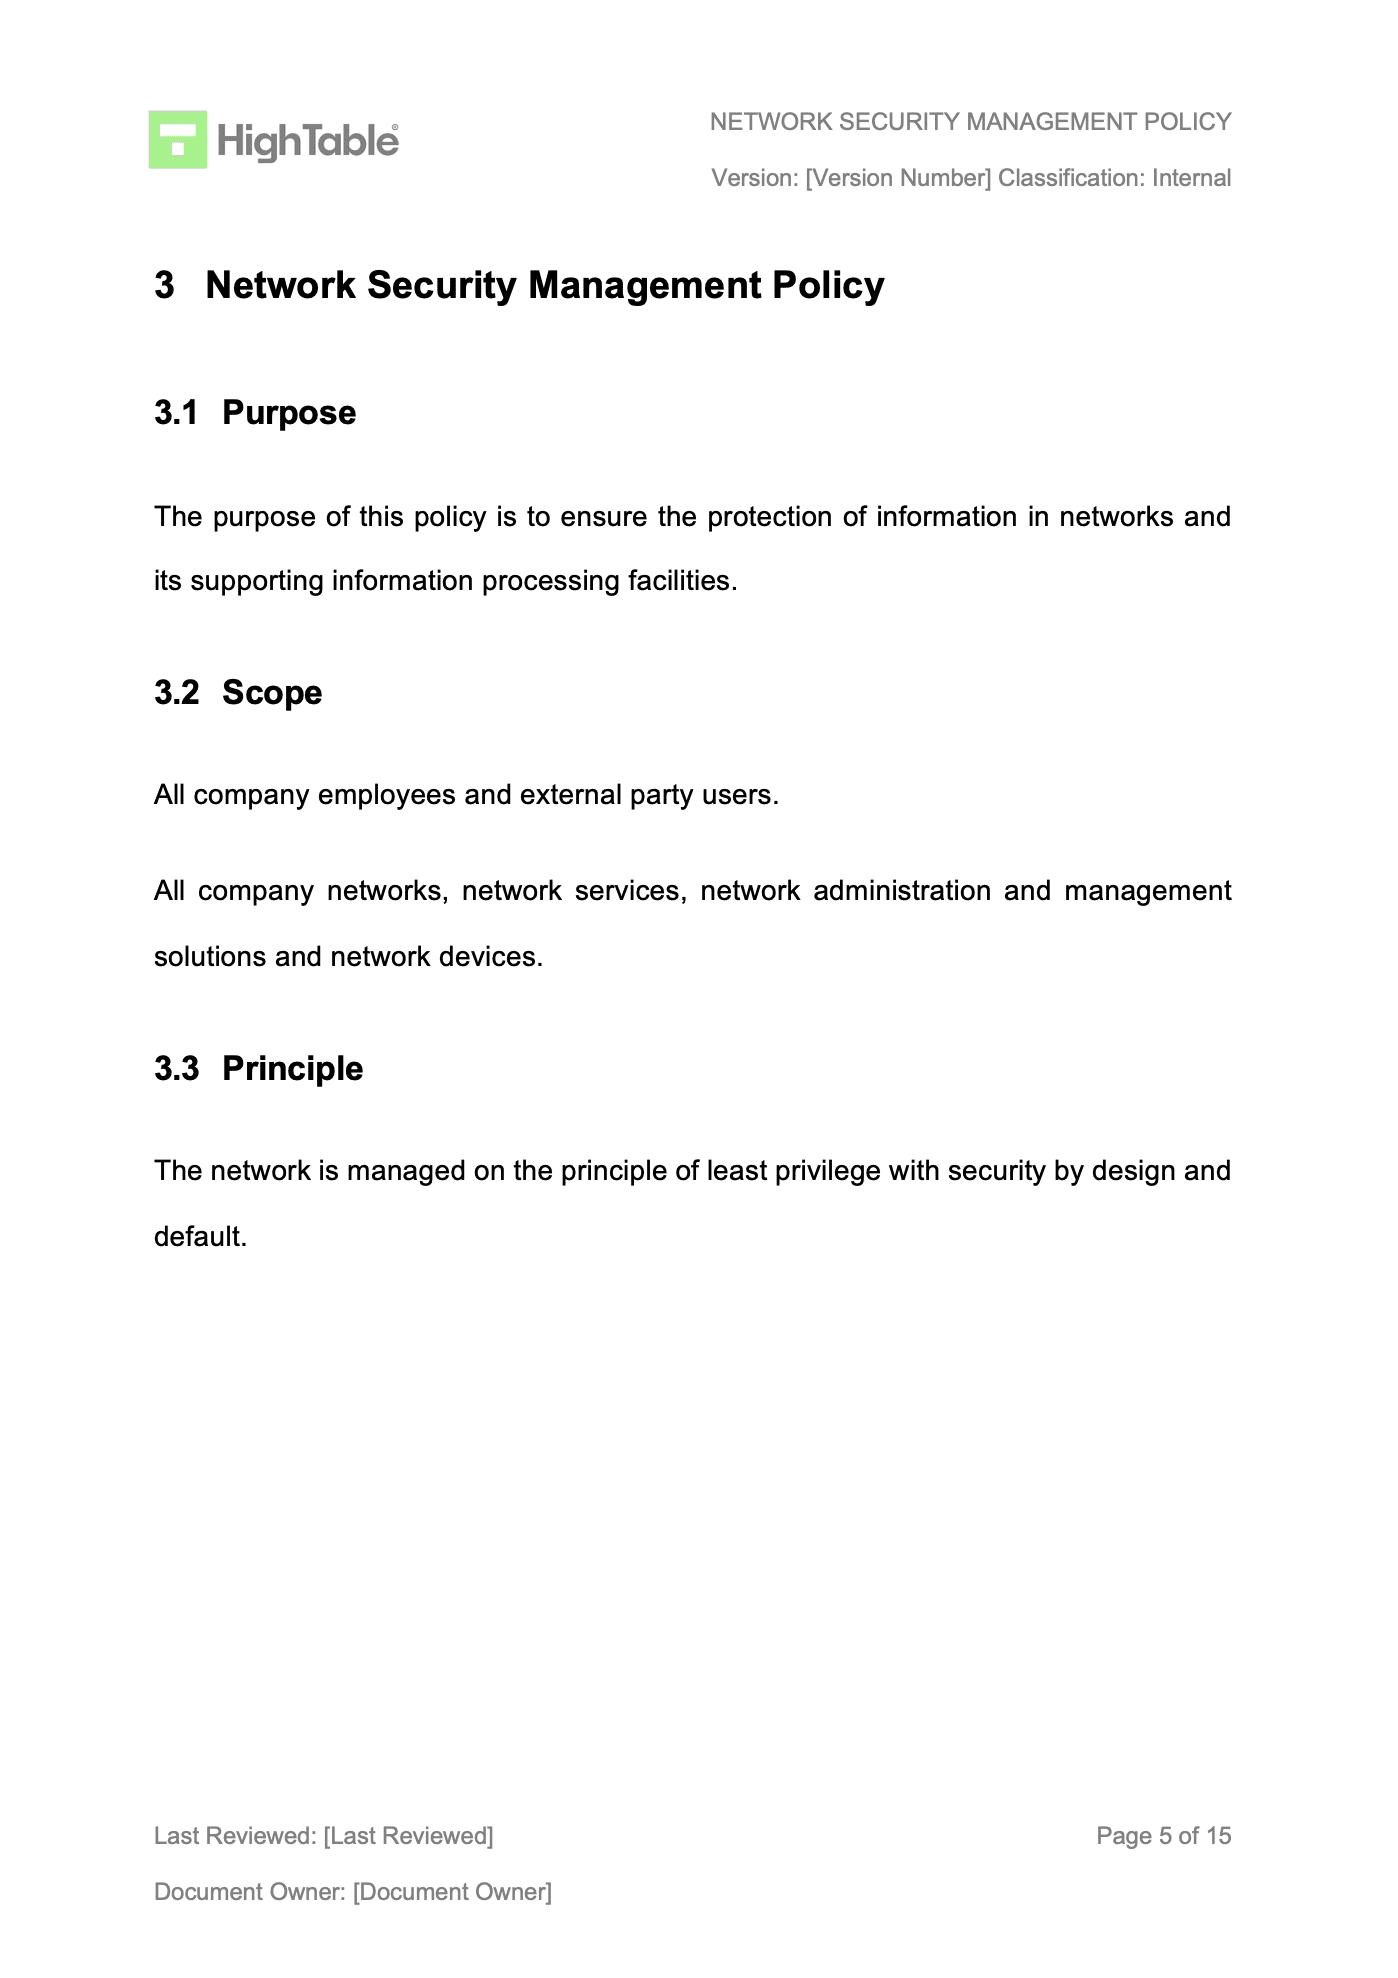
An example ISO 27001 Network Security Management Policy:
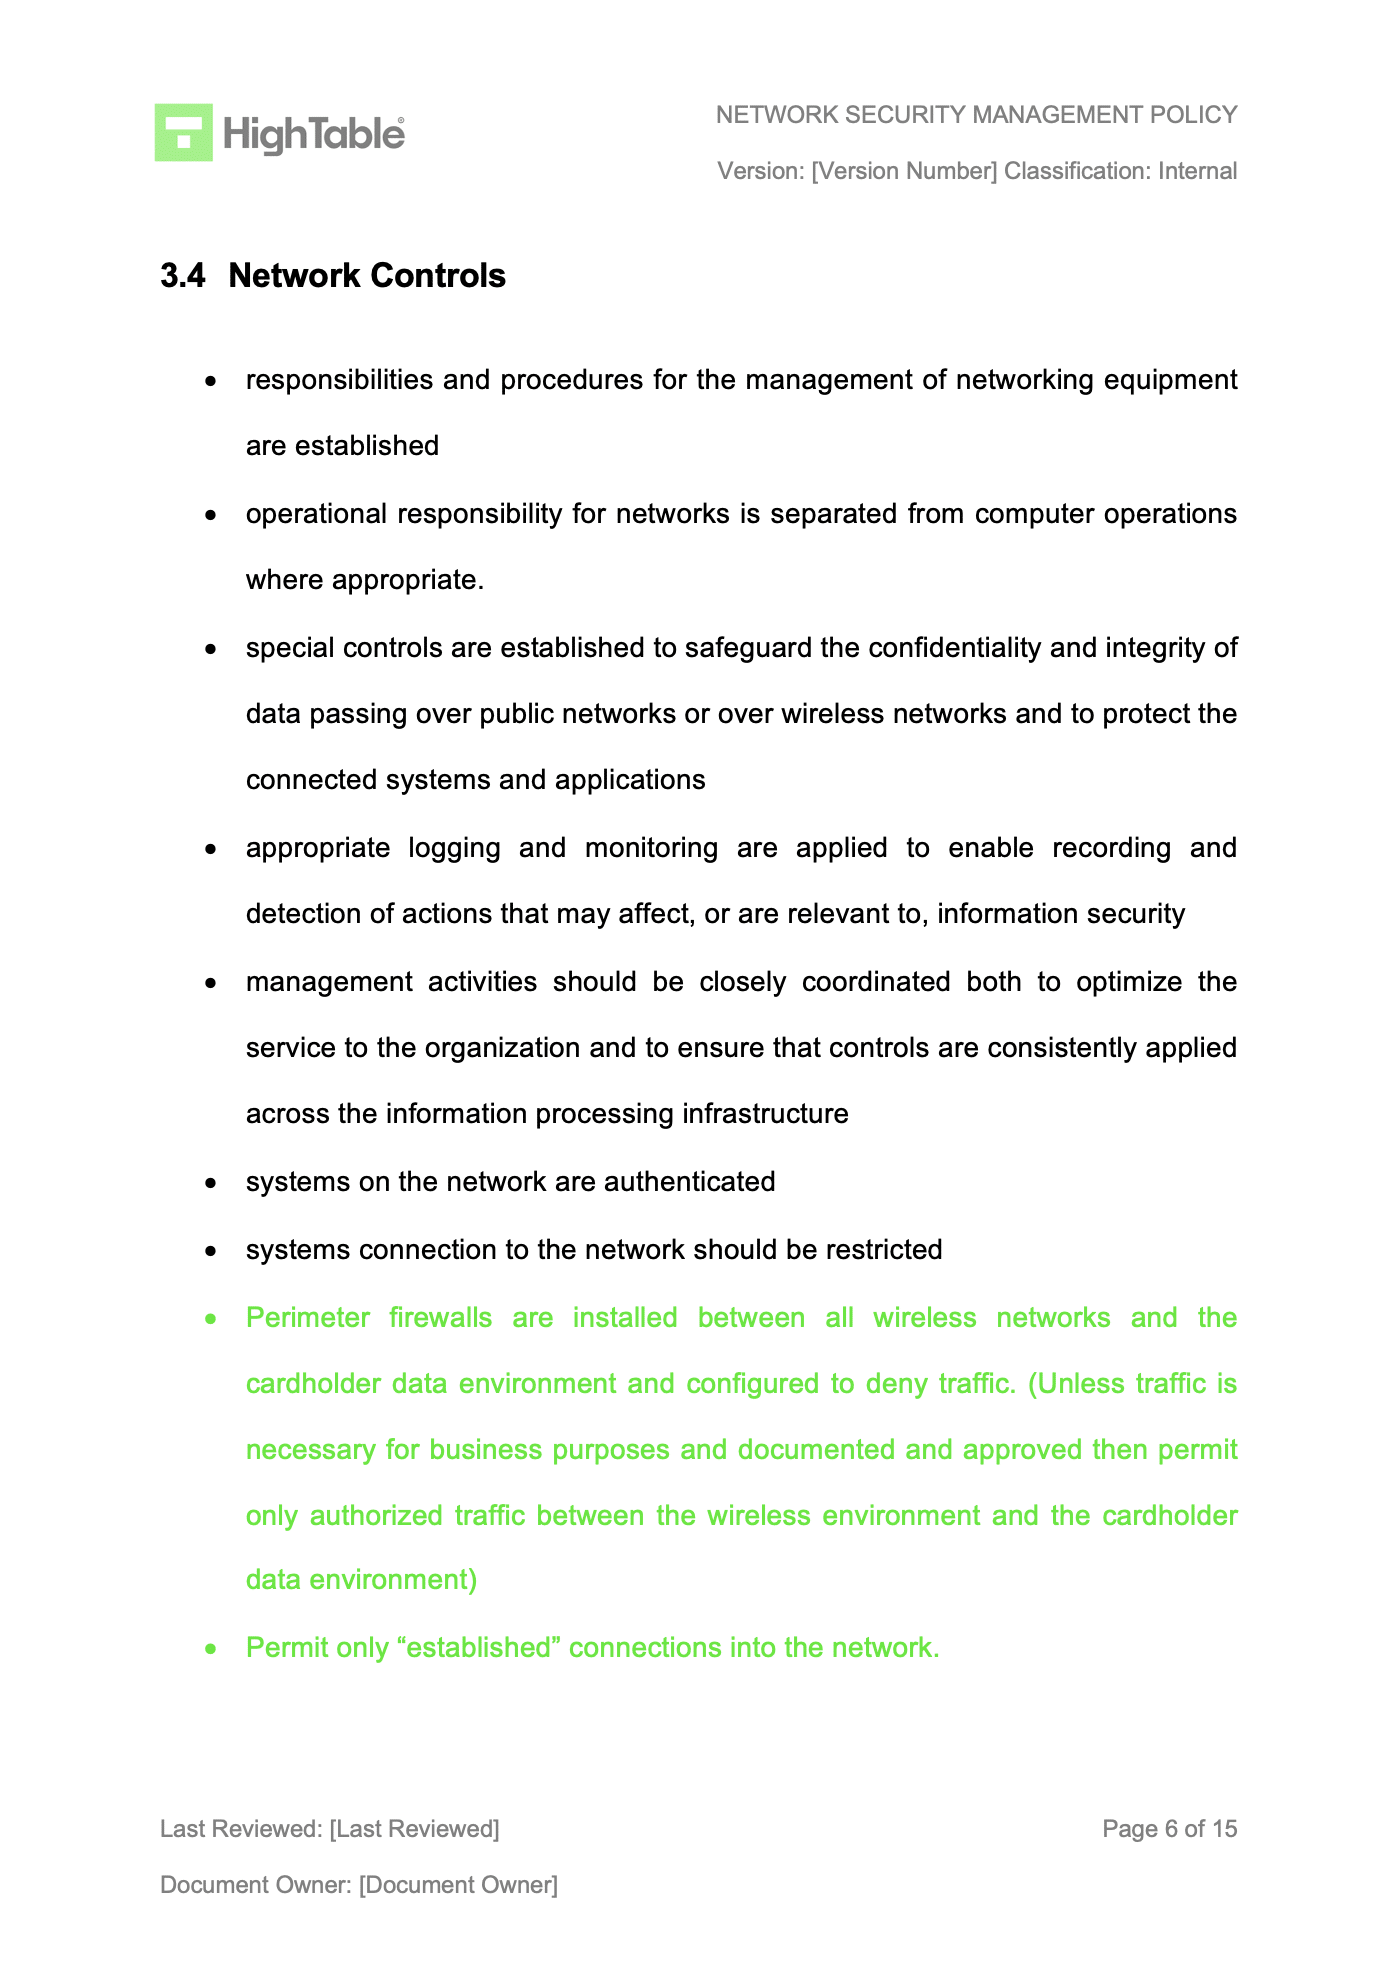
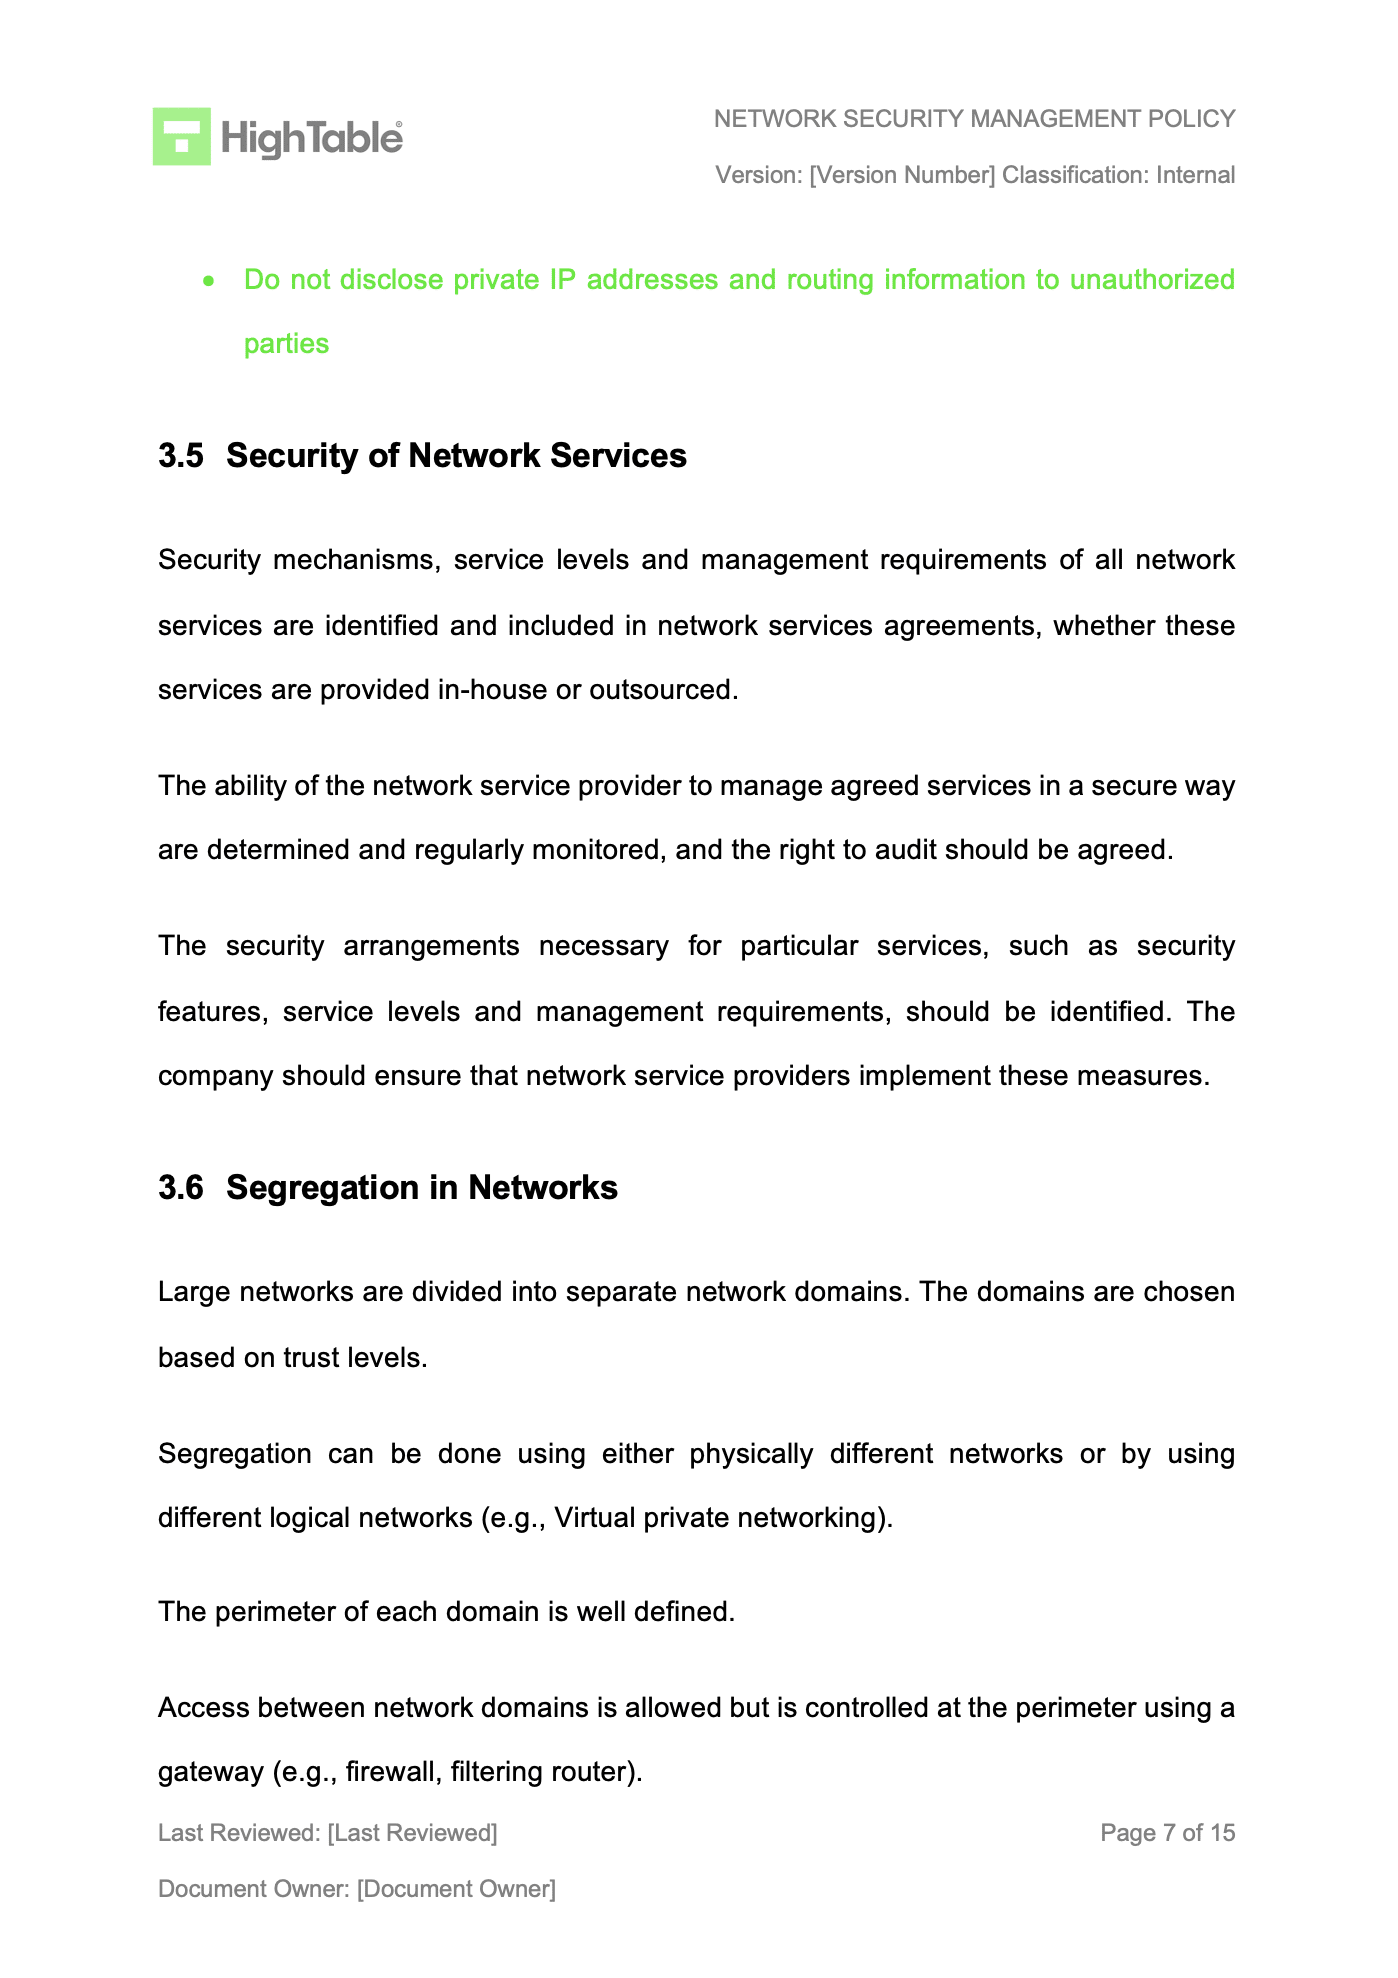
How to write an ISO 27001 Network Security Policy
Writing the policy should be easy to follow. Start by explaining the purpose of the policy. Then, create sections for different rules, like using strong passwords, connecting to a secure network, and what to do if you suspect a problem. Use simple, clear language so everyone can understand it.
Time needed: 1 hour and 30 minutes
How to write an ISO 27001 Network Security Management Policy
- Create your version control and document mark-up
- Write the ISO 27001 Network Security Management Policy Contents Page
- Write the ISO 27001 Network Security Management Policy purpose
- Write the ISO 27001 Network Security Management Policy principle
- Write the ISO 27001 Network Security Management Policy scope
- Define the network controls
- Describe the security of network services
- Explain the segregation of networks
- Set out access to networks and network services
- Describe network locations
- Explain the management of physical network devices
- Describe web filtering
- Explain host intrusion, network intrusion, malware and antivirus
ISO 27001 Network Security Management Policy Template
The ISO 27001:2022 Network Security Policy Template is designed to fast track your implementation and give you an exclusive, industry best practice policy template that is pre written and ready to go. It is included in the ISO 27001 toolkit.
Everything you need to know
Why you need an ISO 27001 Network Security Policy
You need this policy to keep your business safe from digital threats. A good network policy helps you avoid data breaches, protect customer information, and keep your systems running smoothly. It also shows customers and partners that you’re serious about security, which builds trust.
When you need an ISO 27001 Network Security Policy
You need a network security policy as soon as you start setting up your business’s network. It’s a foundational document that should be created early on. You’ll refer to it whenever you add a new device, change your network setup, or bring on new employees.
Who needs an ISO 27001 Network Security Policy?
Everyone who uses your company’s network needs to follow this policy. This includes employees, contractors, and even guests who use your Wi-Fi. The IT team or network administrator is usually in charge of writing and enforcing the policy.
Where you need an ISO 27001 Network Security Policy
This policy applies to all parts of your network, no matter where they are. This includes your office Wi-Fi, your cloud services, and any remote access tools your employees use. The rules apply everywhere your network traffic flows.
How to implement an ISO 27001 Network Security Policy
To put the policy into action, first share it with everyone in the company. You can hold a brief training session to explain the key rules. Then, you’ll set up your network to follow the policy, for example, by configuring firewalls and access controls. Finally, you’ll regularly check to make sure the rules are being followed.
How the ISO 27001 toolkit can help
An ISO 27001 toolkit is a great shortcut. It often includes pre-written policies, procedures, and forms that you can use right away. It saves you the hassle of writing everything from scratch and helps you make sure you don’t miss any important details.
ISO 27001 Toolkit
All the templates, tools, support and knowledge you need to do it yourself.
Applicability of an ISO 27001 Network Security Policy to Small Businesses, Tech Startups, and AI Companies
This policy is useful for businesses of all sizes, including small businesses, tech startups, and AI companies.
- Small Businesses: It helps you formalise how you protect your online store, customer data, and business files from hackers.
- Tech Startups: It’s crucial for managing access to your development environment, protecting your intellectual property, and ensuring your product is built on a secure foundation.
- AI Companies: It’s essential for protecting the data you use to train your models and ensuring secure connections to your cloud services and servers.
Examples of Using It for Small Business
A small accounting firm’s policy might state that all staff must use a VPN when connecting to the office network from home and that the Wi-Fi password must be changed every month.
Examples of Using It for Tech Startups
A startup creating a new app might have a policy that requires all developers to use multi-factor authentication to access the code repository and prohibits them from using public Wi-Fi without a secure tunnel.
Examples of Using It for AI Companies
An AI company’s policy might include rules for segmenting its network so that the AI training data is kept separate from the public-facing website. It would also require all cloud connections to be encrypted.
Information security standards that need an ISO 27001 Network Security Policy
This policy is a key part of ISO 27001, which is an international standard for managing information security. Other standards that need it include:
- GDPR (General Data Protection Regulation)
- CCPA (California Consumer Privacy Act)
- DORA (Digital Operational Resilience Act)
- NIS2 (Network and Information Security (NIS) Directive)
- SOC 2 (Service Organisation Control 2)
- NIST (National Institute of Standards and Technology)
- HIPAA (Health Insurance Portability and Accountability Act)
List of relevant ISO 27001:2022 controls
The ISO 27001:2022 standard has several controls related to network security:
- ISO 27001:2022 Annex A 8.20 Network Security
- ISO 27001:2022 Annex A 8.21 Security of Network Services
- ISO 27001:2022 Annex A 8.22 Segregation of Networks
- ISO 27001:2022 Annex A 8.23 Web Filtering
ISO 27001 Network Security Policy FAQ
To protect your computer network from threats.
No, it’s for any size company that has a network.
No, but it helps to have someone from your IT team involved.
You should review it at least once a year.
It can lead to security breaches, lost data, and a damaged reputation.
No, it’s a living document that you should continually use and update.
Yes, it should cover all parts of your network, including wireless connections.
A firewall is a tool that blocks unwanted traffic from entering your network.
No, it works with your software to provide a full security plan.
It provides clear evidence that you are managing your network correctly, which is crucial for audits.
Yes, having a network security policy is required.
It’s the process of dividing your network into smaller, more secure parts.
Decide who will be in charge of writing it and find a good template to start with.
Stuart Barker
ISO 27001 Ninja
Stuart Barker is a veteran practitioner with over 30 years of experience in systems security and risk management. Holding an MSc in Software and Systems Security, he combines academic rigor with extensive operational experience, including a decade leading Data Governance for General Electric (GE).
As a qualified ISO 27001 Lead Auditor, Stuart possesses distinct insight into the specific evidence standards required by certification bodies. His toolkits represent an auditor-verified methodology designed to minimise operational friction while guaranteeing compliance.
- MSc Security
- ISO 27001 Lead Auditor
- 30+ Years Exp
- Ex-GE Leader