

In this guide, you will learn what an ISO 27001 Business Continuity Policy is, how to write it yourself and I give you a template you can download and use right away.
Table of contents
- What is an ISO 27001 Business Continuity Policy?
- ISO 27001 Business Continuity Policy Example
- ISO 27001 Business Continuity Policy Template
- How to write an ISO 27001 Business Continuity Policy
- What you need to know about the ISO 27001 Business Continuity Policy
- How to implement an ISO 27001 Business Continuity Policy
- How the ISO 27001 toolkit can help
- Applicability to Small Businesses, Tech Startups, and AI Companies
- Information security standards that need an ISO 27001 Business Continuity Policy
- List of relevant ISO 27001:2022 controls
- ISO 27001 Business Continuity Policy FAQ
What is an ISO 27001 Business Continuity Policy?
An ISO 27001 Business Continuity Policy is your company’s game plan for what to do when things go wrong. It’s a simple, easy-to-follow guide that helps you get back on your feet quickly after a disaster, like a power outage or a cyberattack. The goal is to keep your business running smoothly, no matter what happens.
This policy is a set of rules and guidelines that make sure your business can keep operating even during a crisis. It covers things like what to do if your office building is unavailable, how to access critical information, and how to keep in touch with your team and customers. Think of it as your emergency survival guide for the business world.
ISO 27001 Business Continuity Policy Example
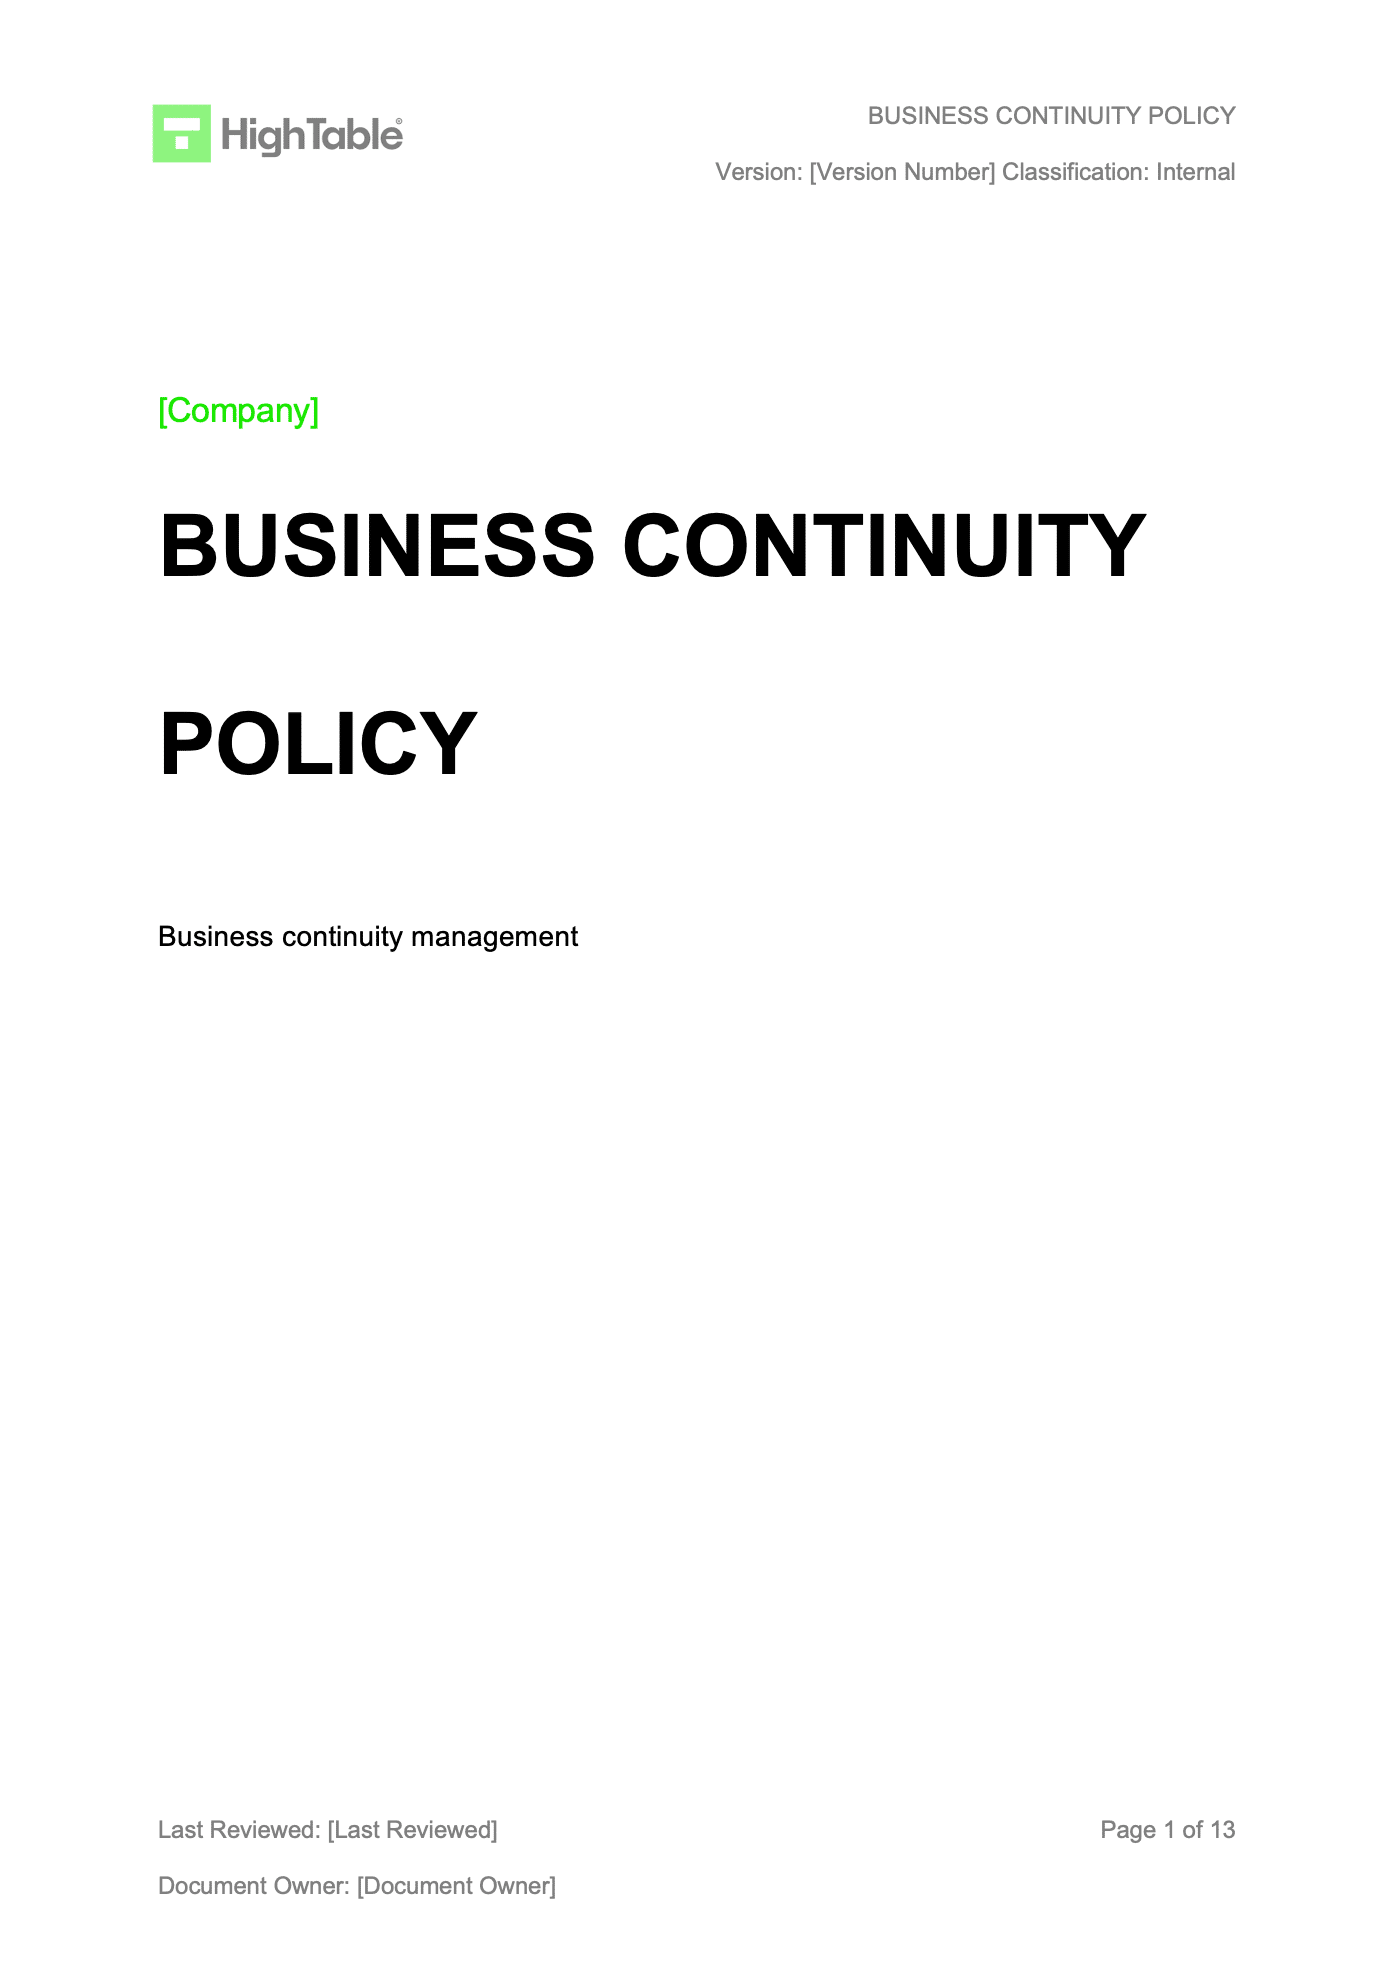
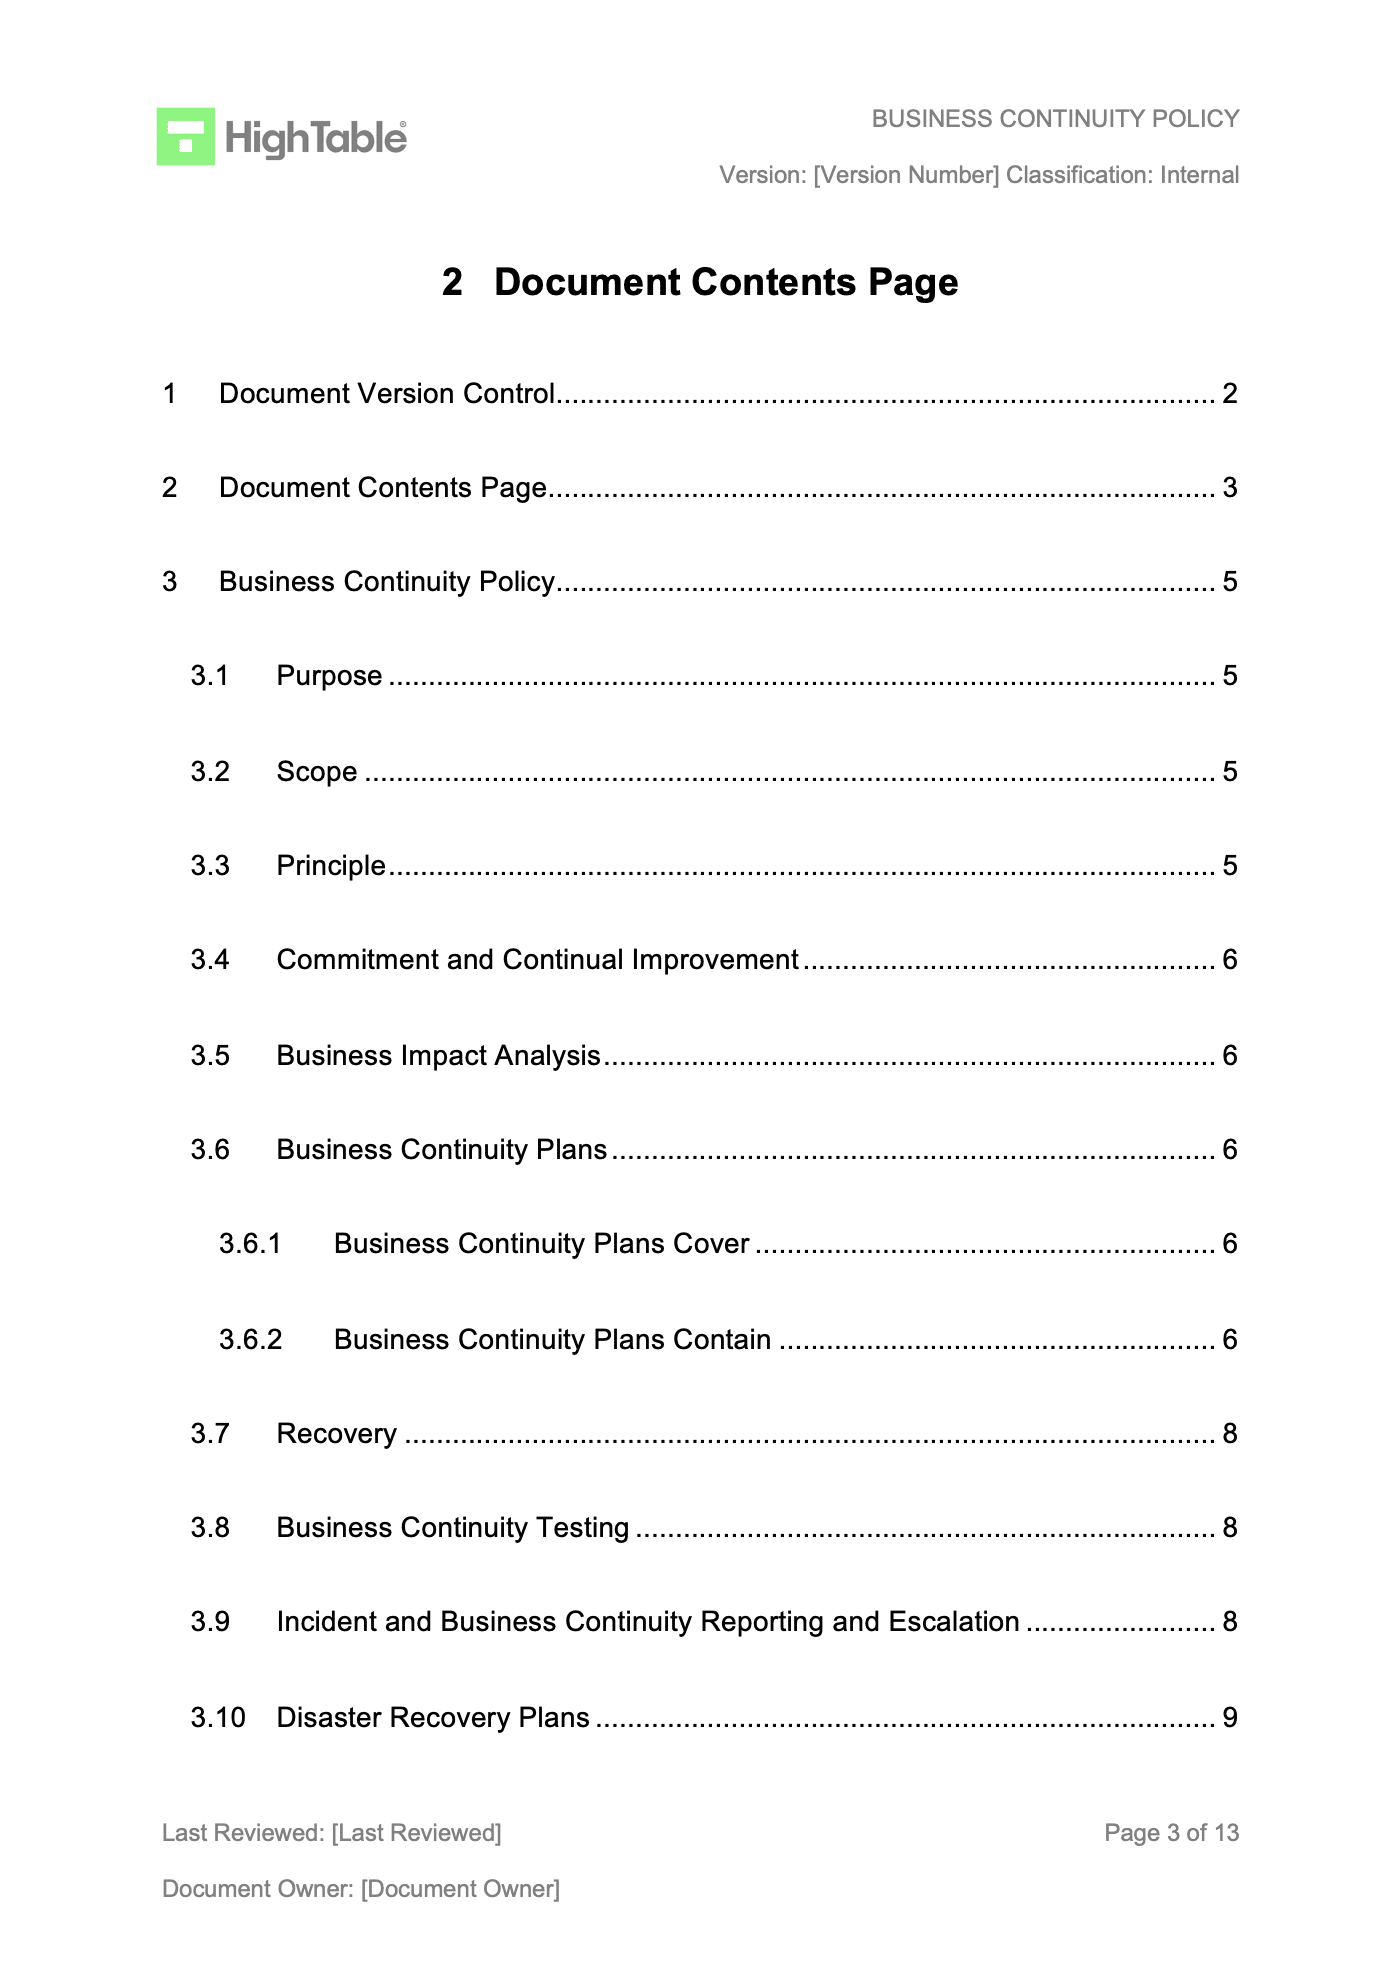
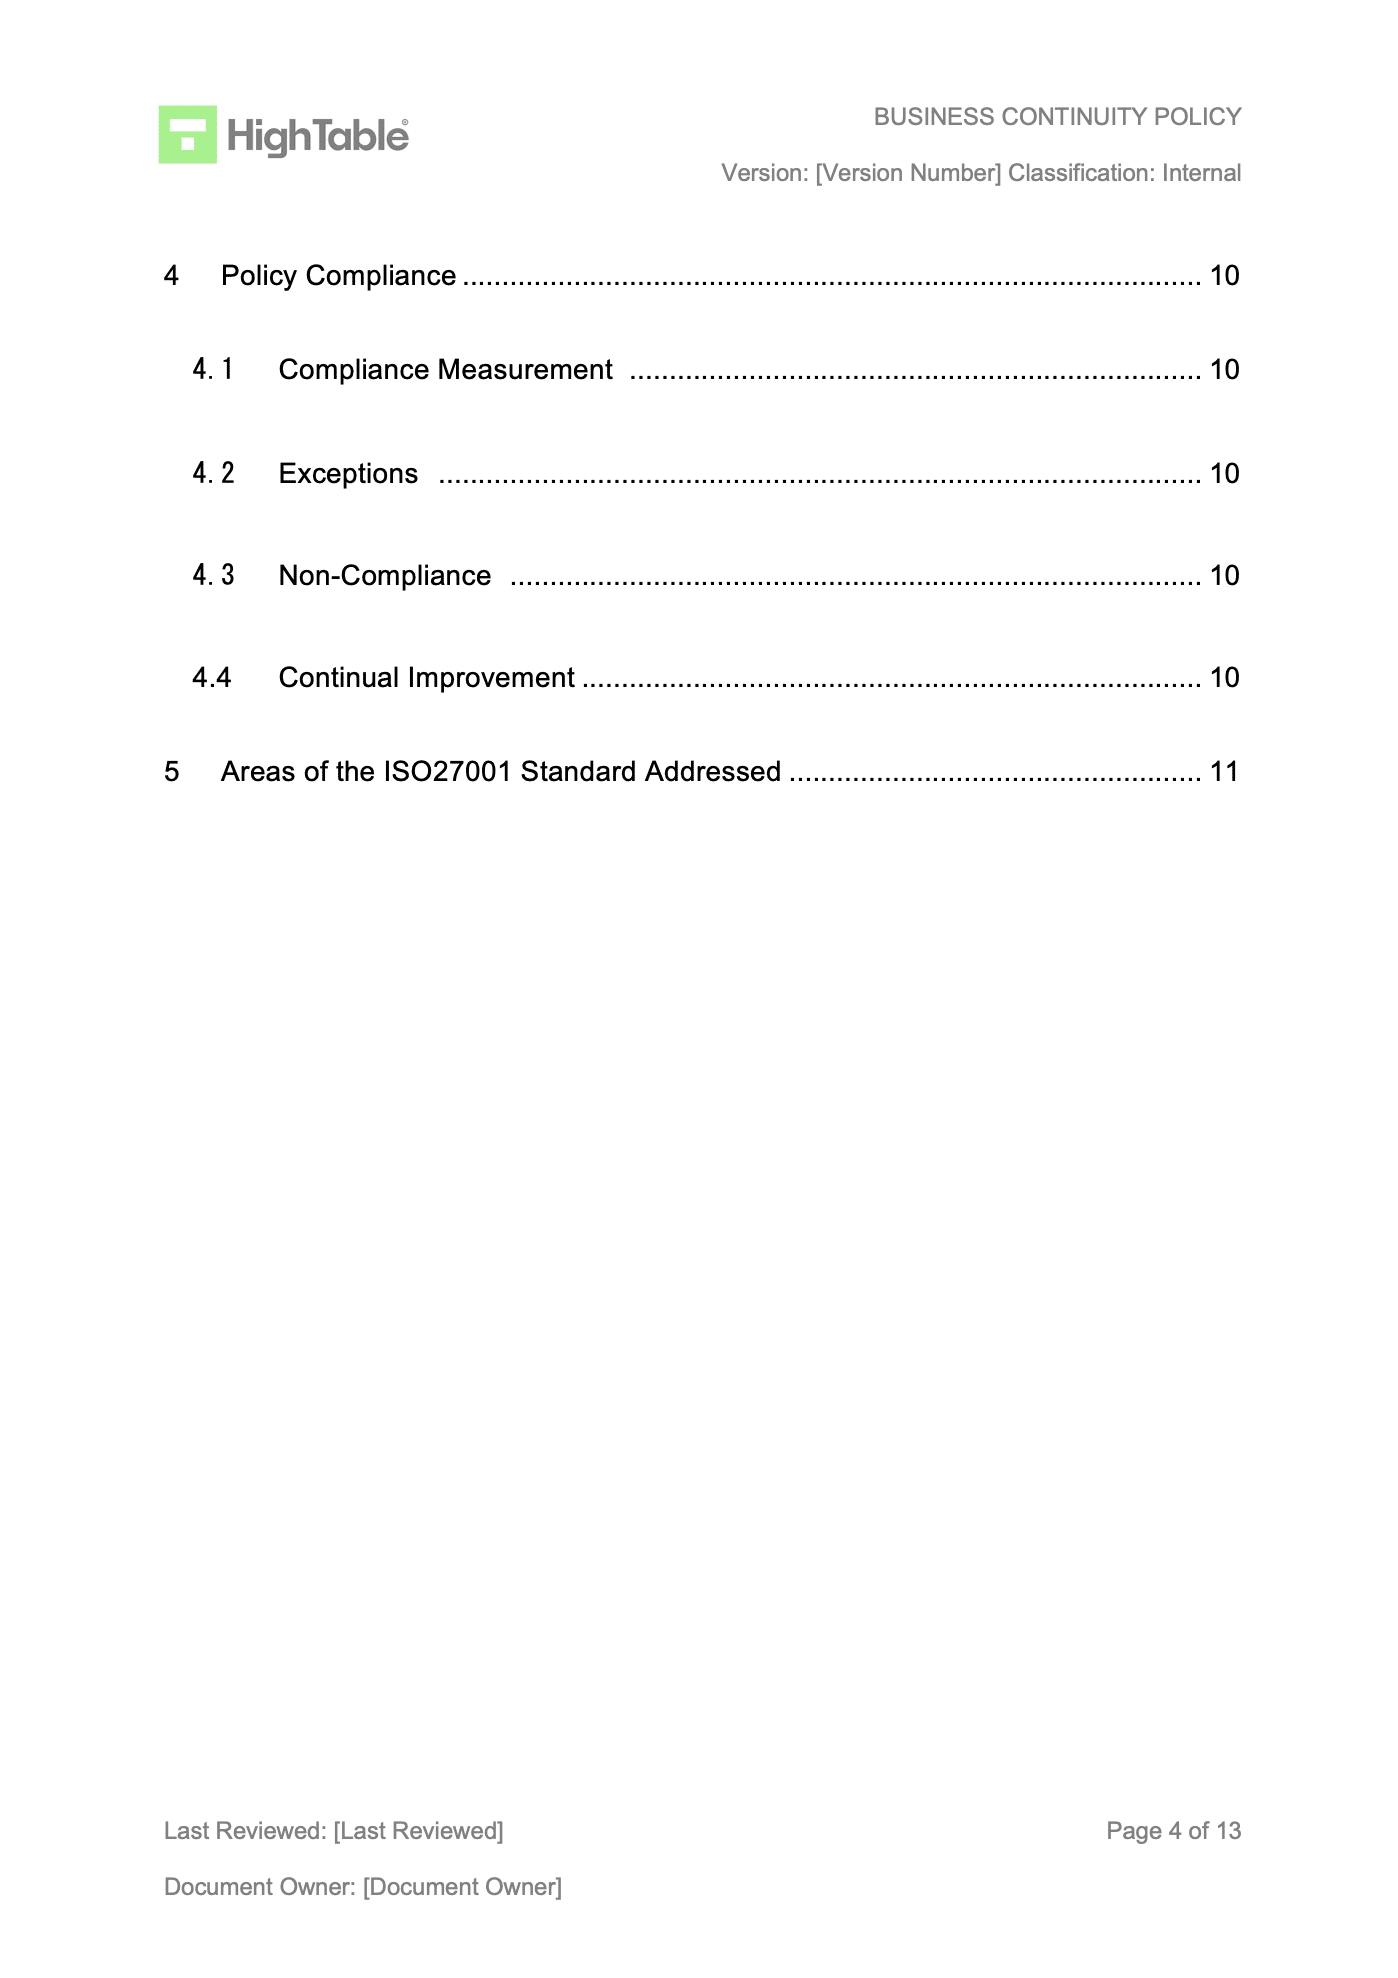
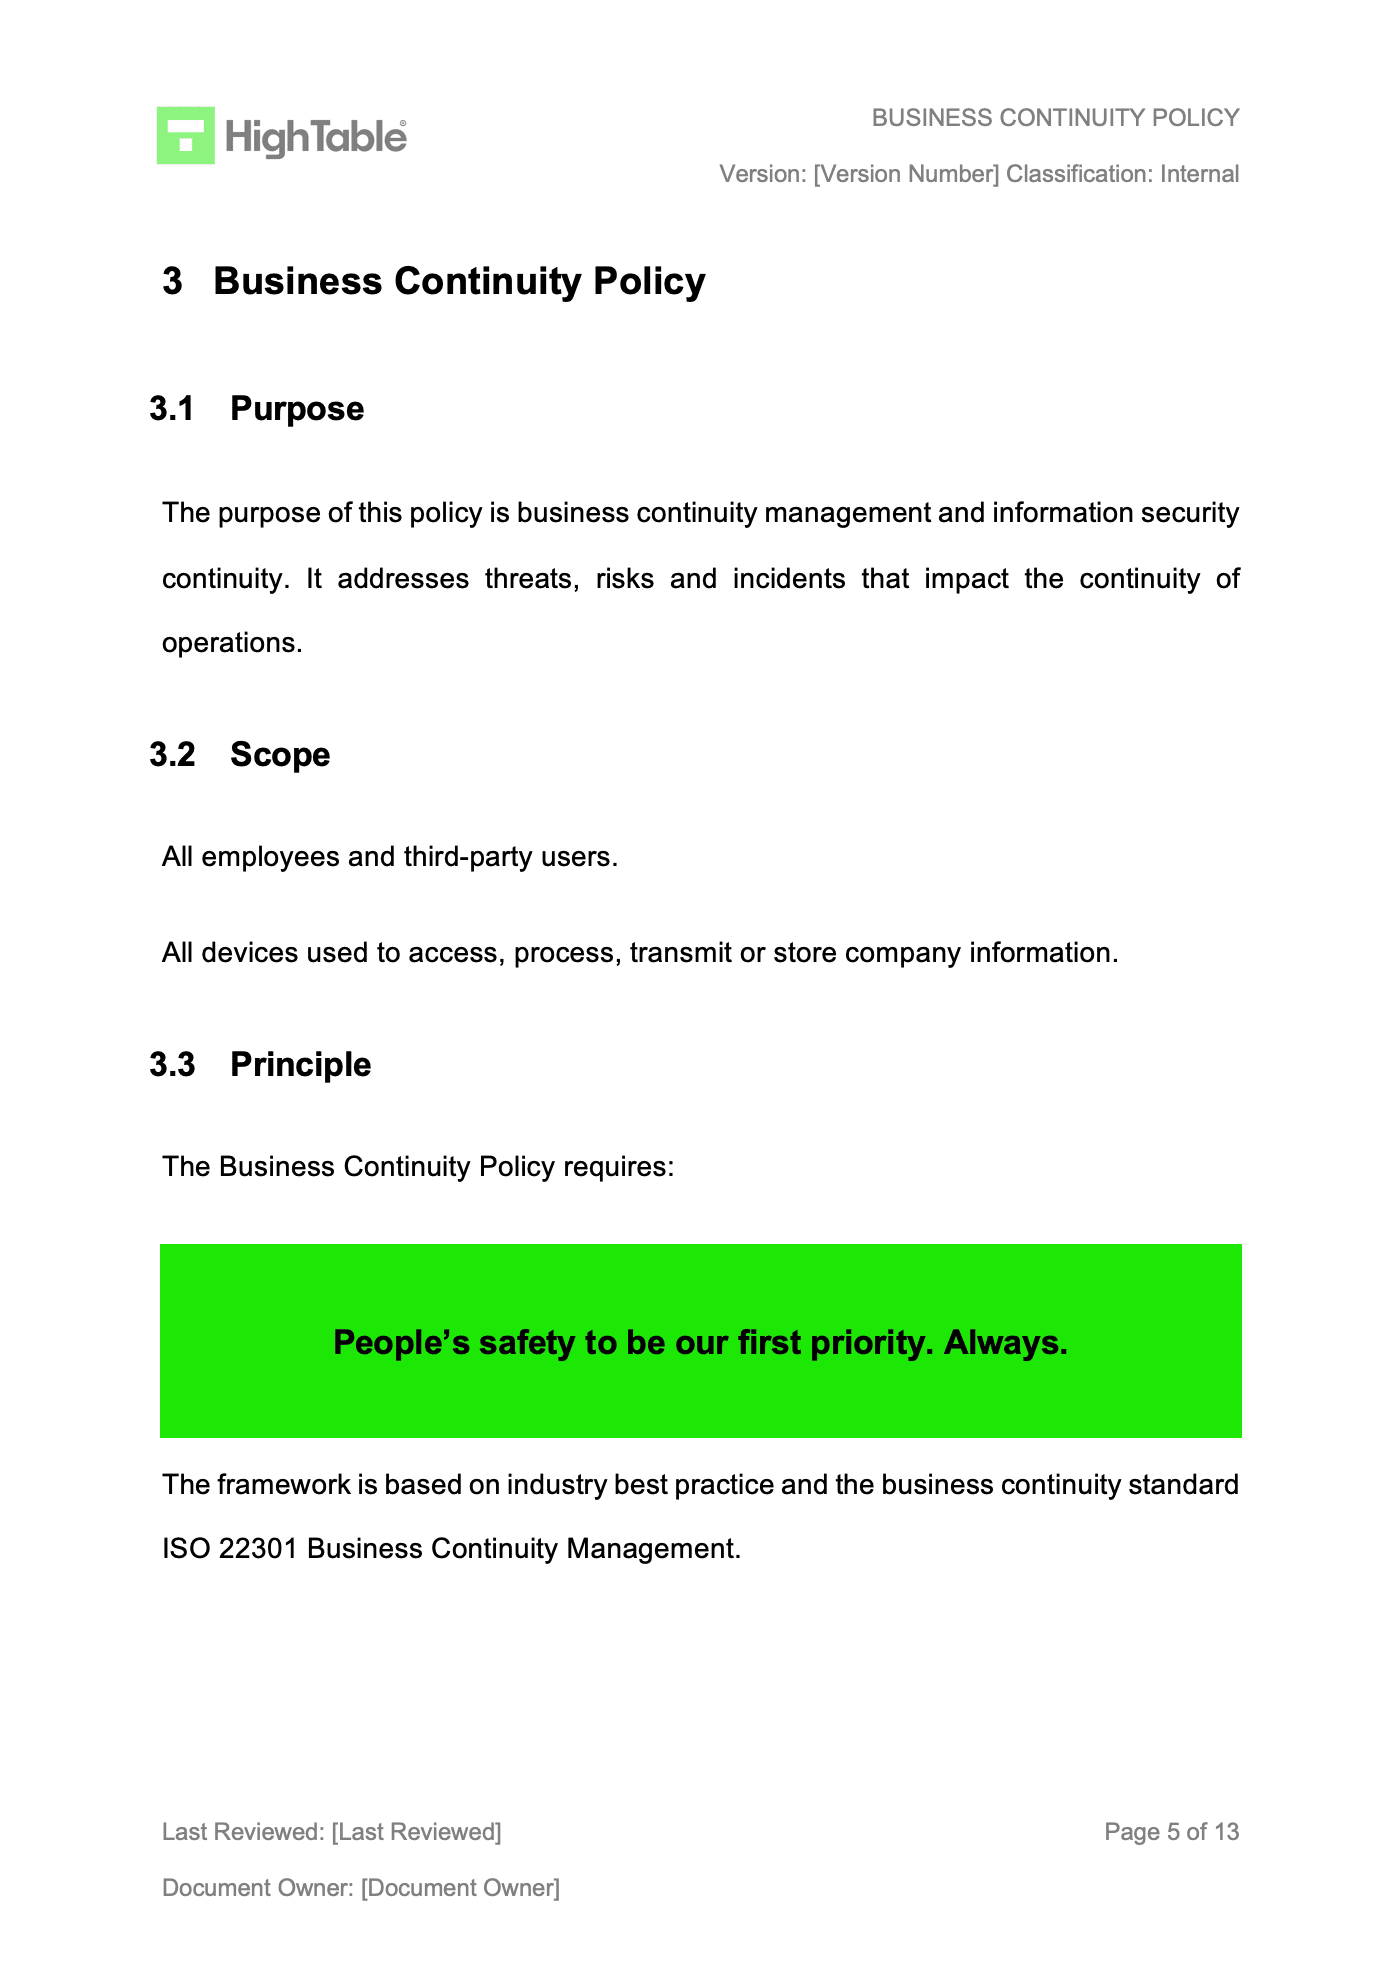
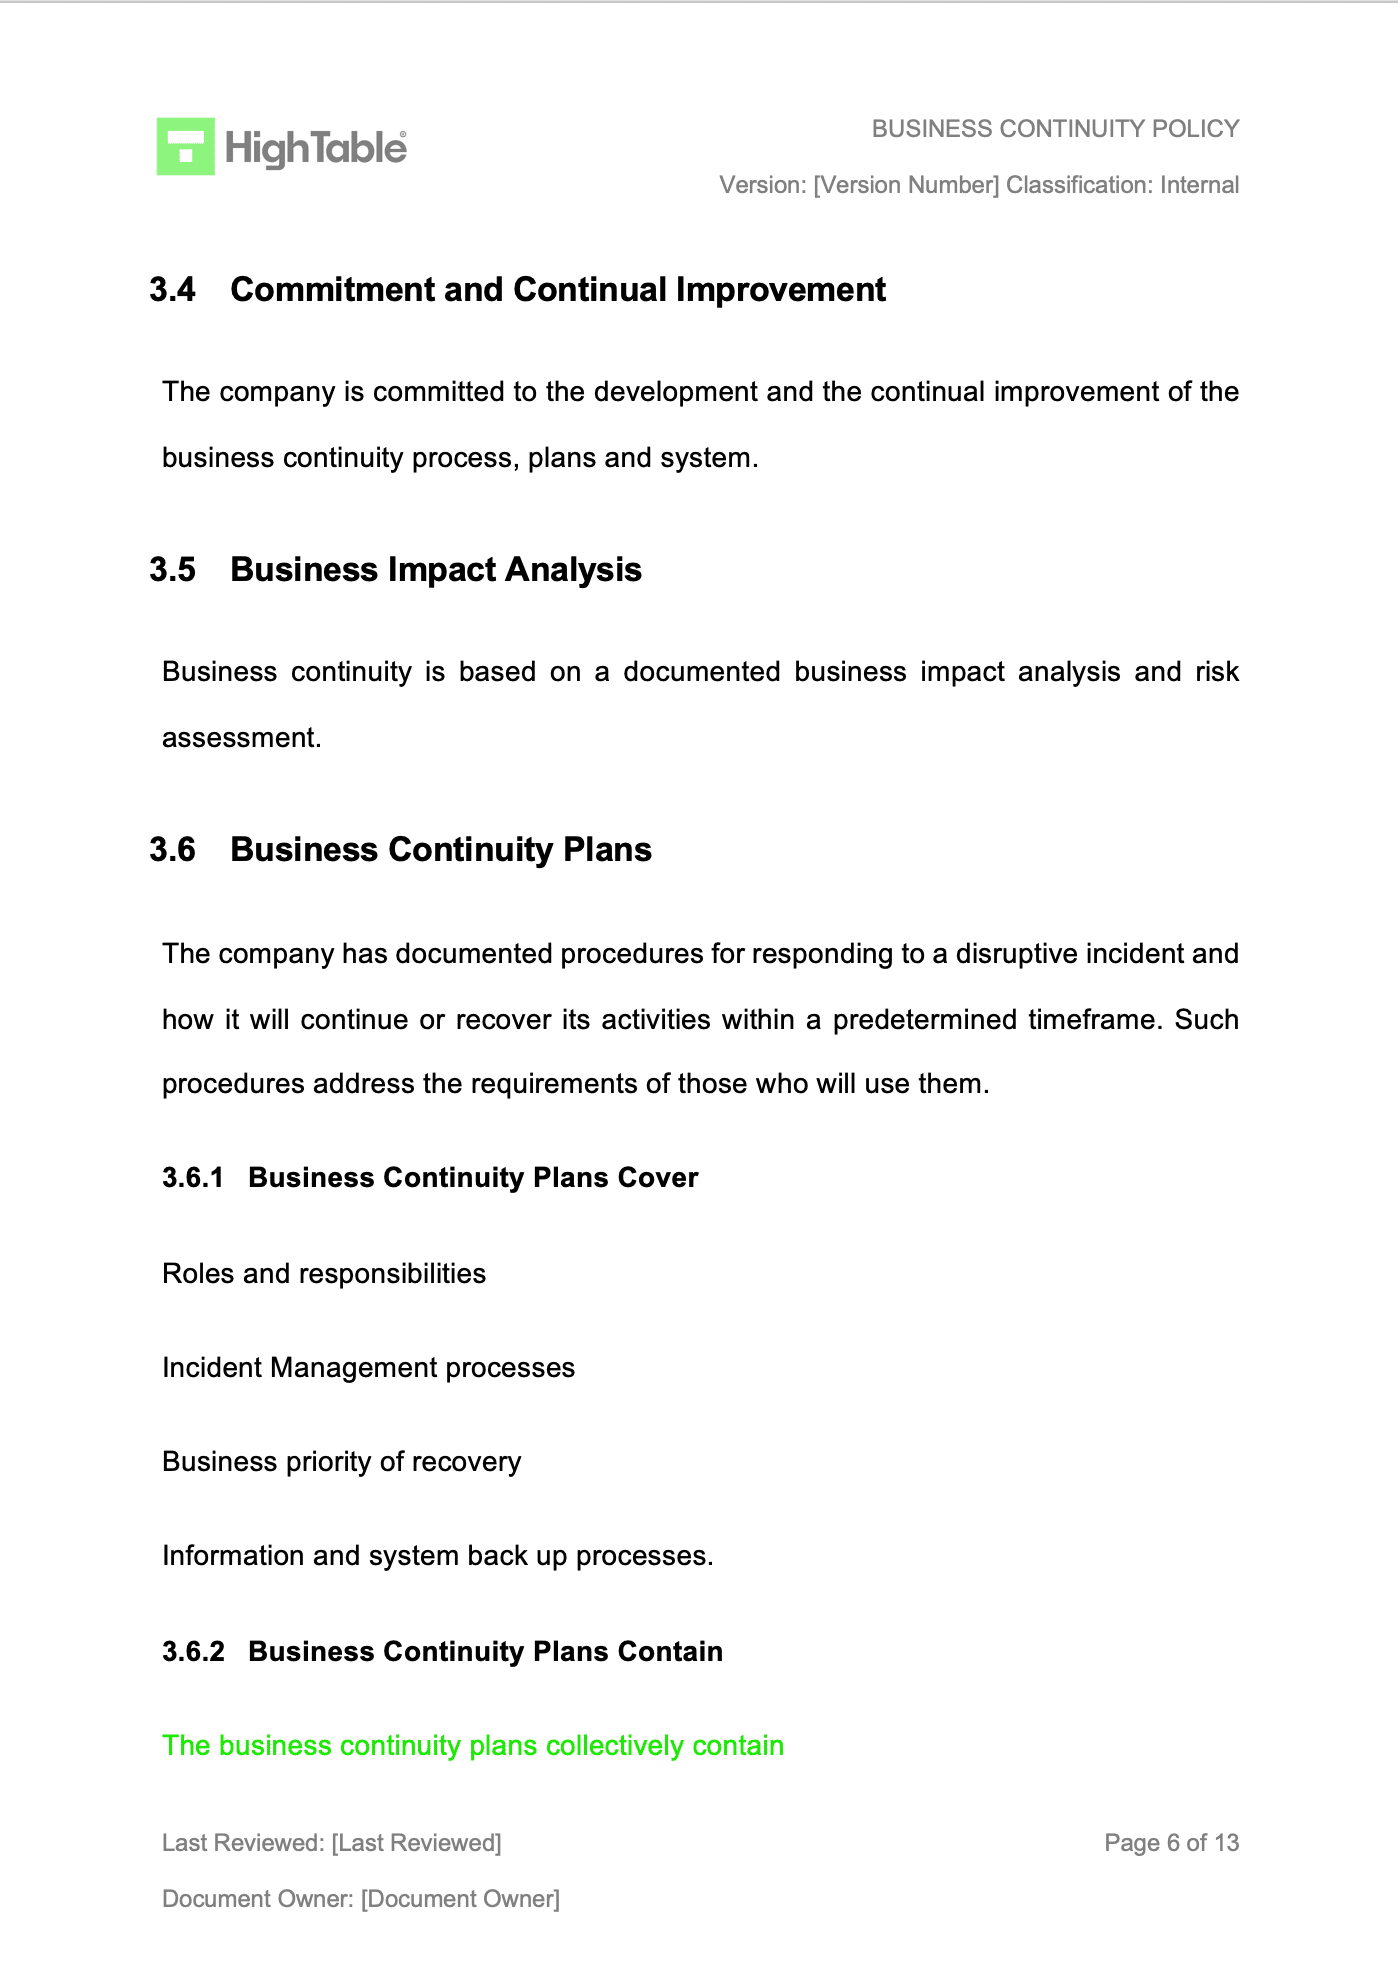
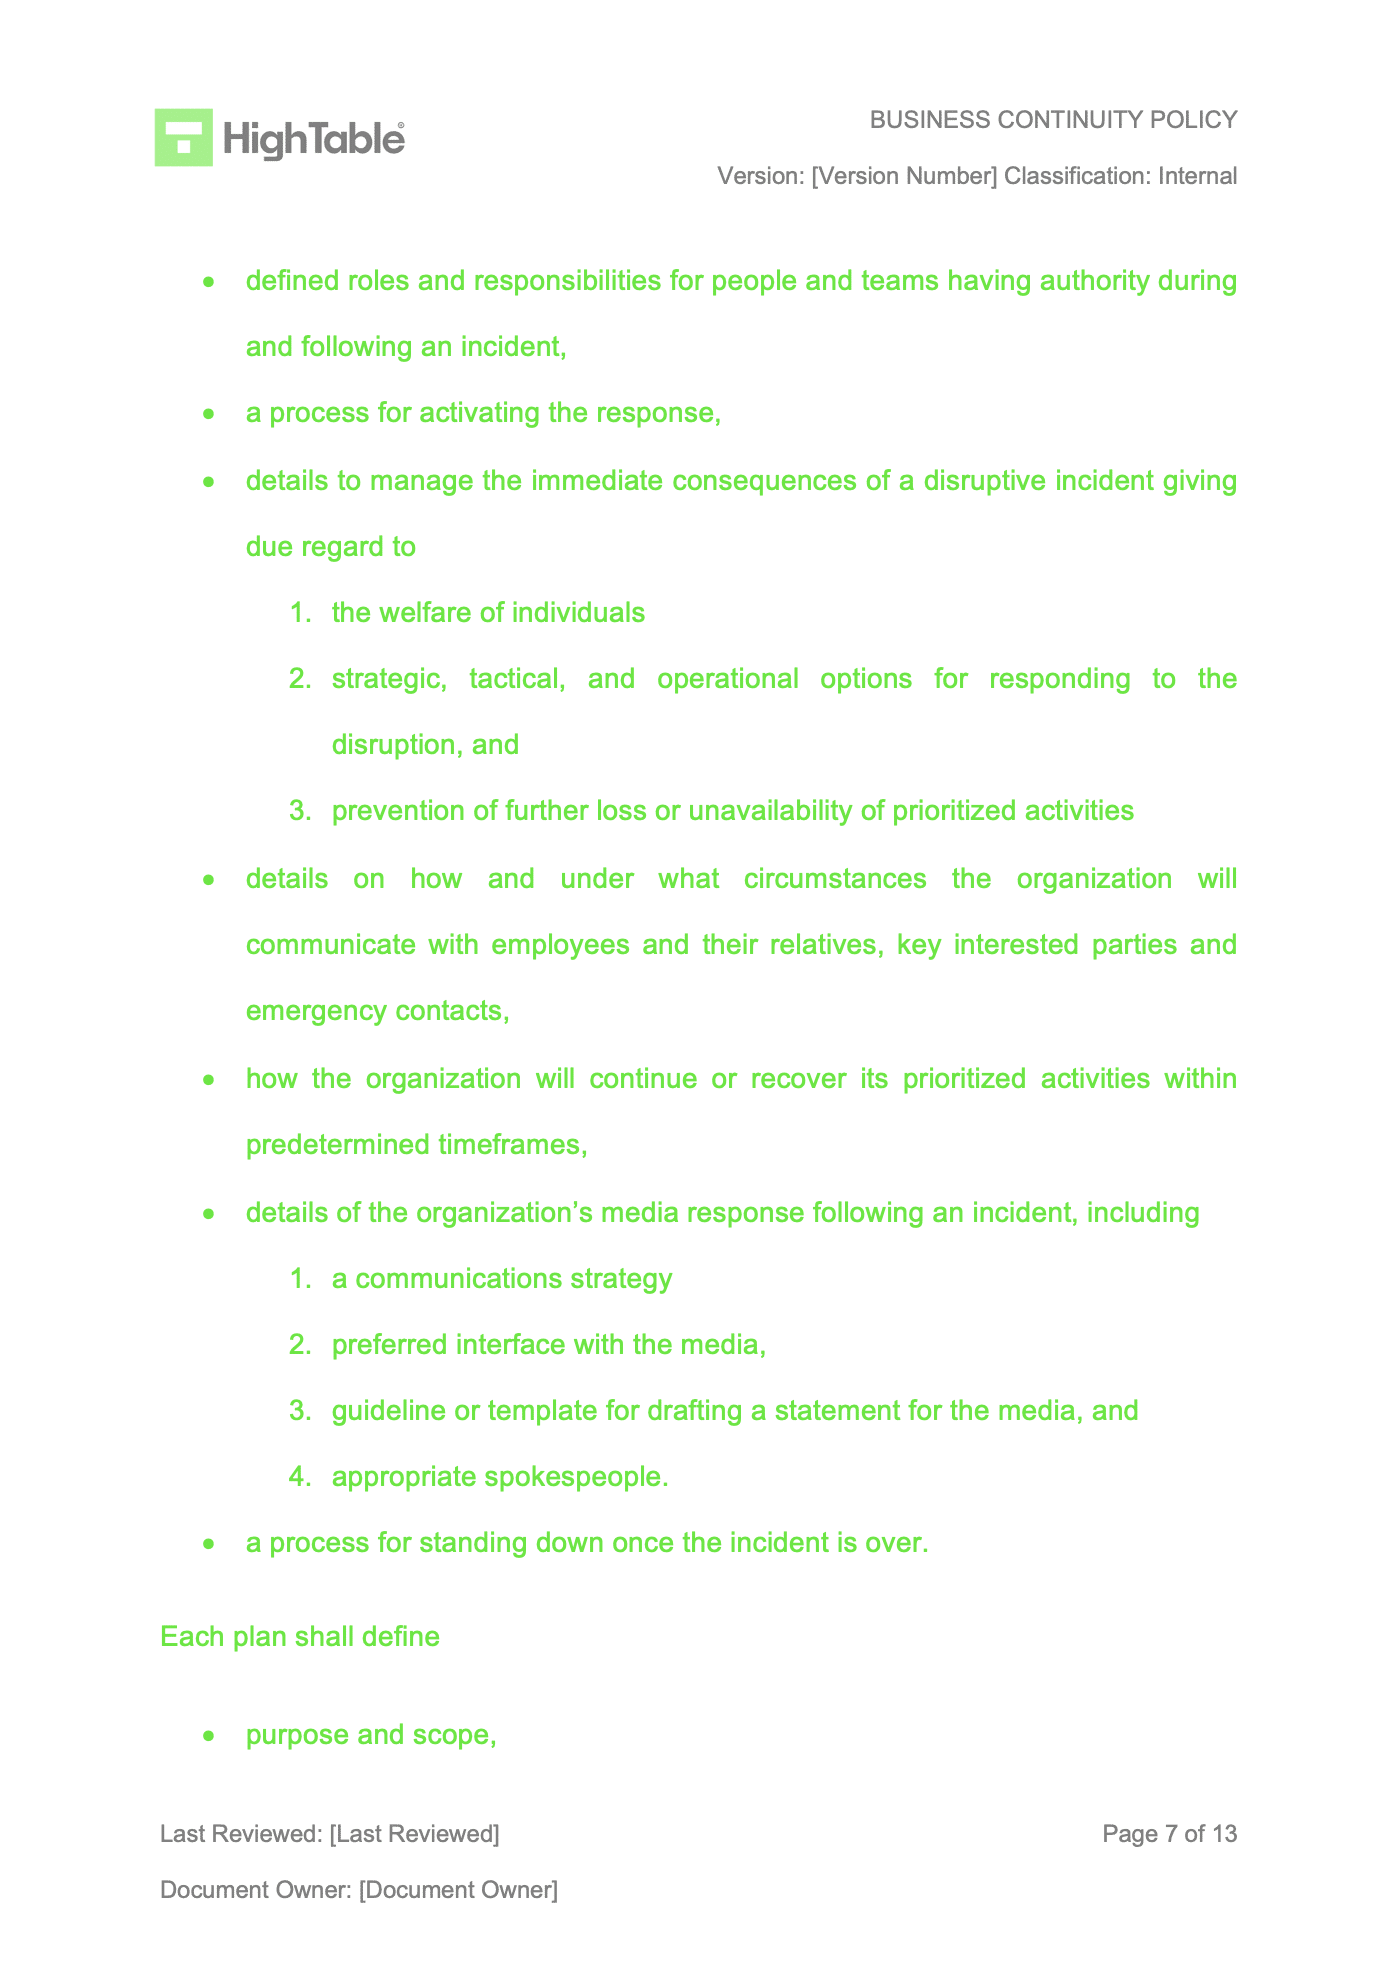
An example ISO 27001 business continuity policy:
ISO 27001 Business Continuity Policy Template
The ISO 27001:2022 business continuity template is designed to fast track your implementation and give you an exclusive, industry best practice policy template that is pre written and ready to go. It is included in the ISO 27001 toolkit.

How to write an ISO 27001 Business Continuity Policy
Keep it simple! Start by identifying the most important parts of your business and what could threaten them. Then, list the steps you’ll take to protect those parts. Use clear, simple language and create a step-by-step action plan. You can use checklists and flowcharts to make it even easier to follow.
Time needed: 1 hour and 30 minutes
How to write an ISO 27001 Business Continuity Policy
- Create your version control and document mark-up
- Write the ISO 27001 Business Continuity Policy Contents Page
- Write the ISO 27001 Business Continuity Policy Purpose
- Write the ISO 27001 Business Continuity Policy Principle
- Write the ISO 27001 Business Continuity Policy Scope
- Explain the commitment to continual improvement
- Describe the role of the Business Impact Analysis (BIA)
- Set out the approach to Business Continuity Plans
- Explain what business continuity plans cover
- Describe what business continuity plans contain
- Explain the approach to recovery
- Set out when business continuity testing occurs
- Describe the relationship between business continuity and incident management
- Show commitment to disaster recovery plans
What you need to know about the ISO 27001 Business Continuity Policy
Why you need an ISO 27001 Business Continuity Policy
You need this policy to protect your business from unexpected problems. It helps you minimise damage, reduce financial loss, and maintain trust with your customers. Having a plan in place shows that you’re responsible and prepared, which is a big plus for your reputation. It’s a proactive way to avoid a huge headache later.
When you need an ISO 27001 Business Continuity Policy
You need a business continuity policy before a disaster ever happens. You should create it when you’re first setting up your information security system and review it regularly. You’ll use it every time there’s a serious problem that could stop your business, like a natural disaster, a technical failure, or a security breach.
Who needs an ISO 27001 Business Continuity Policy?
Everyone in the company needs to be aware of this policy. While a small team or a single person might be in charge of writing it, every employee should know their role in an emergency. This includes the CEO, IT staff, and every team member who needs to keep working during a crisis.
Where you need an ISO 27001 Business Continuity Policy
This policy applies everywhere your business operates. It covers your physical office, your remote workers’ homes, and your cloud-based systems. It’s a universal guide for your team, no matter where they are.
How to implement an ISO 27001 Business Continuity Policy
First, share the policy with everyone. Hold a team meeting to walk through the plan and make sure everyone understands their role. You should also practice the plan with drills, like a test run of your backup systems. Finally, make sure to keep the policy updated, especially as your business changes.
How the ISO 27001 toolkit can help
An ISO 27001 toolkit is like a toolbox full of pre-made documents and guides. It gives you a head start on creating your policy and other important security documents, saving you a ton of time and effort. It’s a great way to make sure you don’t miss anything.
ISO 27001 Toolkit
All the templates, tools, support and knowledge you need to do it yourself.
Applicability to Small Businesses, Tech Startups, and AI Companies
This policy is useful for businesses of all sizes, including small businesses, tech startups, and AI companies.
- Small Businesses: A simple policy can ensure you can still send out invoices and serve customers if your main system goes down.
- Tech Startups: It’s crucial for keeping your app or service running and protecting customer data if there’s an outage.
- AI Companies: It’s essential for protecting your valuable data models and ensuring your AI services don’t stop working unexpectedly.
Examples of using it for small businesses
If you’re a small online shop and your website server fails, your policy might tell you to switch to a backup website, use social media to update customers, and have a list of emergency contacts for your hosting company.
Examples of using it for tech startups
For a startup with a mobile app, the policy could outline how to switch to a backup server if the main one fails. It might also specify how to alert users about the issue and when to expect a fix.
Examples of using it for AI companies
An AI company’s policy might include steps to back up large datasets in multiple locations. It would also explain how to quickly restore your AI model and its services to prevent a major disruption.
Information security standards that need an ISO 27001 Business Continuity Policy
This policy is a key part of ISO 27001, which is an international standard for managing information security. Other standards that need it include:
- GDPR (General Data Protection Regulation)
- CCPA (California Consumer Privacy Act)
- DORA (Digital Operational Resilience Act)
- NIS2 (Network and Information Security (NIS) Directive)
- SOC 2 (Service Organisation Control 2)
- NIST (National Institute of Standards and Technology)
- HIPAA (Health Insurance Portability and Accountability Act)
List of relevant ISO 27001:2022 controls
The ISO 27001:2022 standard has specific controls for business continuity:
- ISO 27001:2022 Annex A 5.29 Information security during disruption
- ISO 27001:2022 Annex A 5.30 ICT readiness for business continuity
ISO 27001 Business Continuity Policy FAQ
To keep your business running smoothly during a crisis.
No, it covers all kinds of disruptions, from power outages to cyberattacks.
The person in charge of your ISMS, but everyone must follow it.
You should review it at least once a year.
It can lead to disorganised chaos, financial loss, and a damaged reputation.
No, it’s a living document that you should continually use and update.
Yes, it should include plans for how remote teams will operate during a disruption.
A disaster is any event that could stop your business from operating normally.
The policy should specify a retention period based on legal and business requirements.
No, this single policy can be a broad guide for many different scenarios.
The policy should explain how to manage their responsibilities during a crisis.
It provides clear evidence that you are prepared for disruptions, which is crucial for audits.
Yes, having a plan for business continuity is required.
Identify the most important parts of your business and what could threaten them.
About the author
