

The ISO 27001 Secure Development Policy sets out how you manage information security in your development lifecycle to protect the confidentiality, integrity and availability of data within applications.
Table of contents
- What is it?
- ISO 27001 Secure Development Policy Example
- ISO 27001 Secure Development Policy Template
- Everything you need to know
- How to write an ISO 27001 Secure Development Policy
- How to implement it
- Applicability to Small Businesses, Tech Startups, and AI Companies
- How the ISO 27001 toolkit can help
- Information security standards that need it
- List of relevant ISO 27001:2022 controls
- ISO 27001 Secure Development Policy FAQ
What is it?
An ISO 27001 Secure Development Policy is a set of rules and guidelines that help you create software that’s safe and sound from the get-go. It’s part of the bigger ISO 27001 family, which is all about managing information security. This policy ensures that security isn’t just an afterthought but is woven into every step of your software-making process.
ISO 27001 Secure Development Policy Example
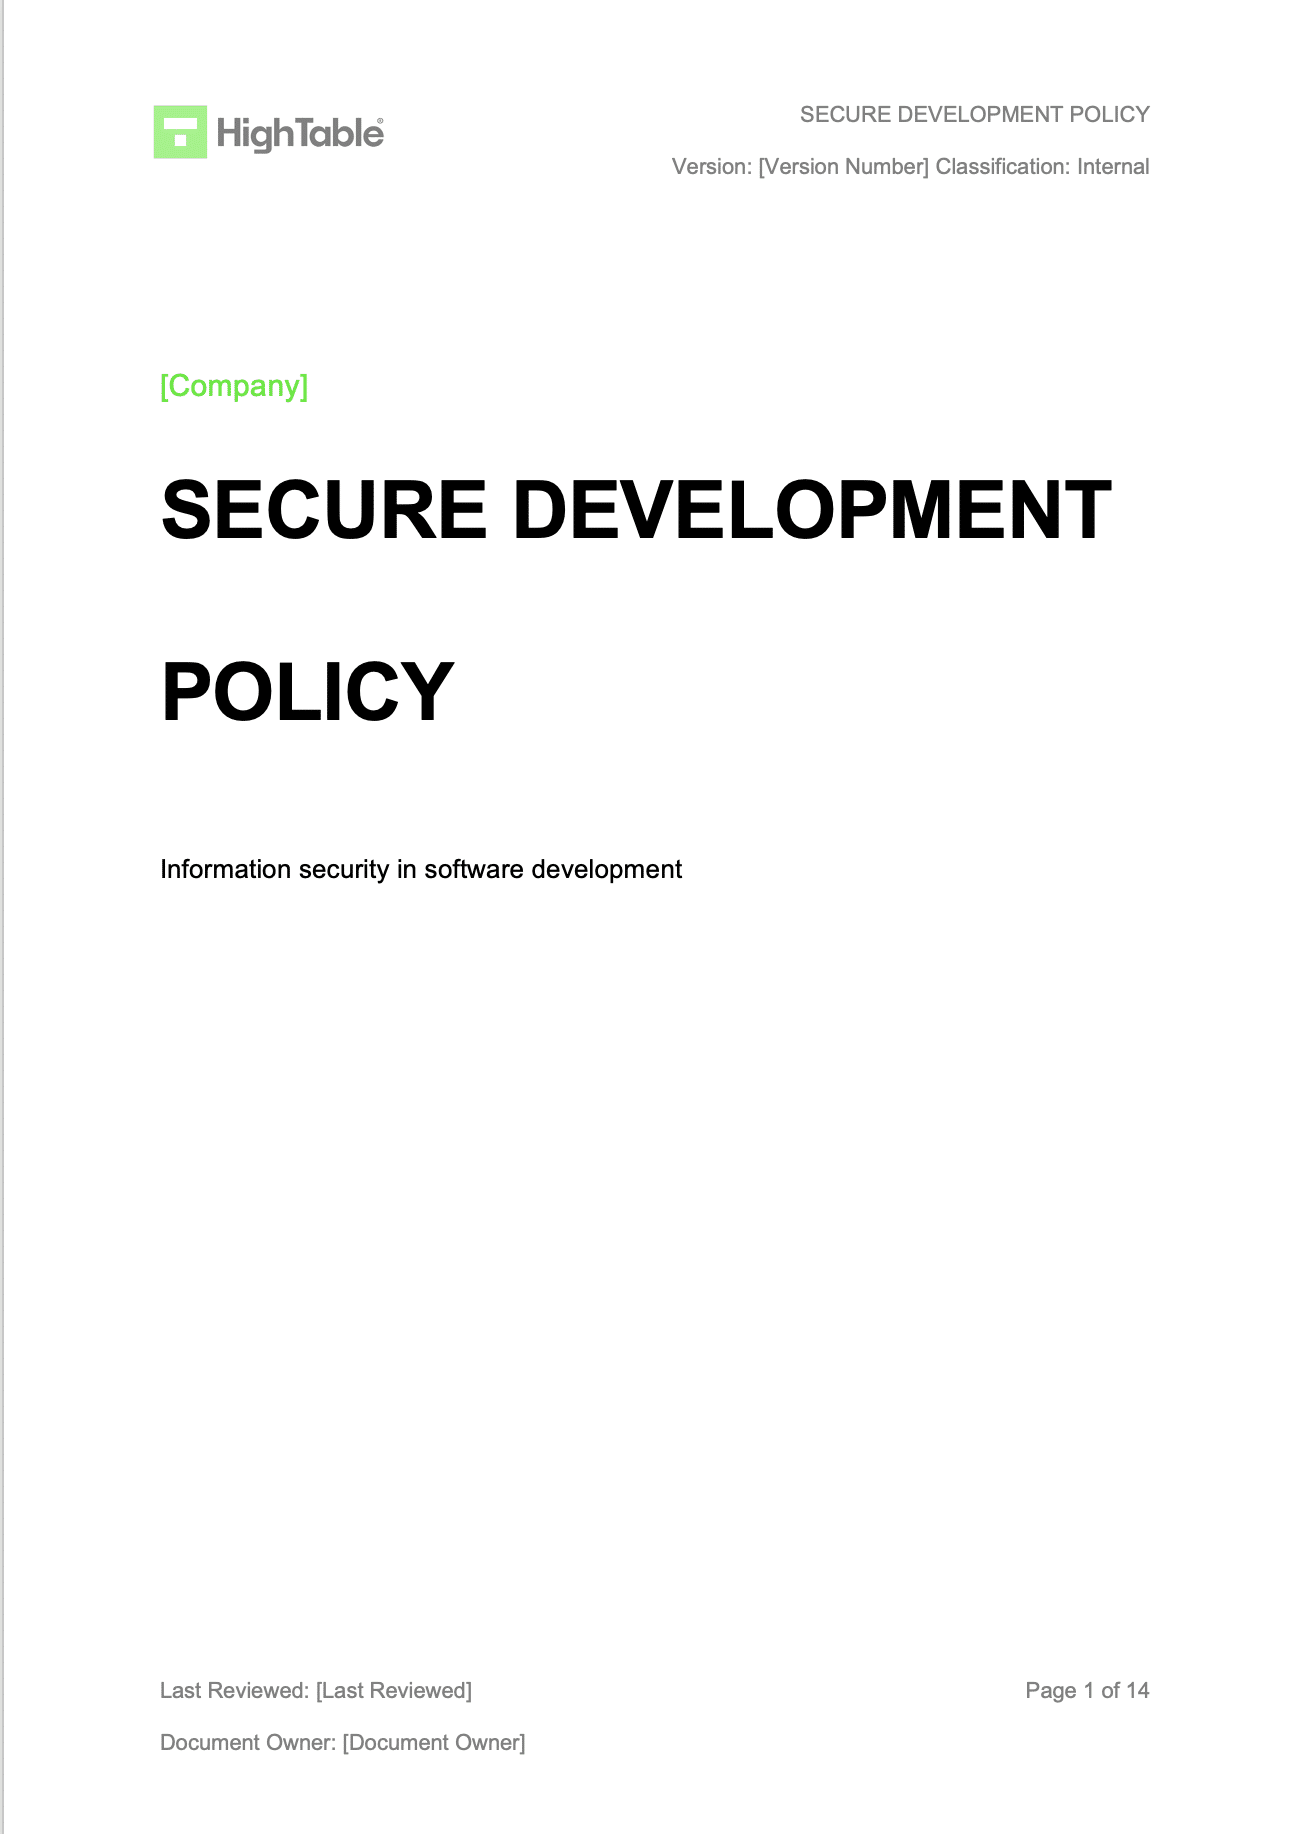
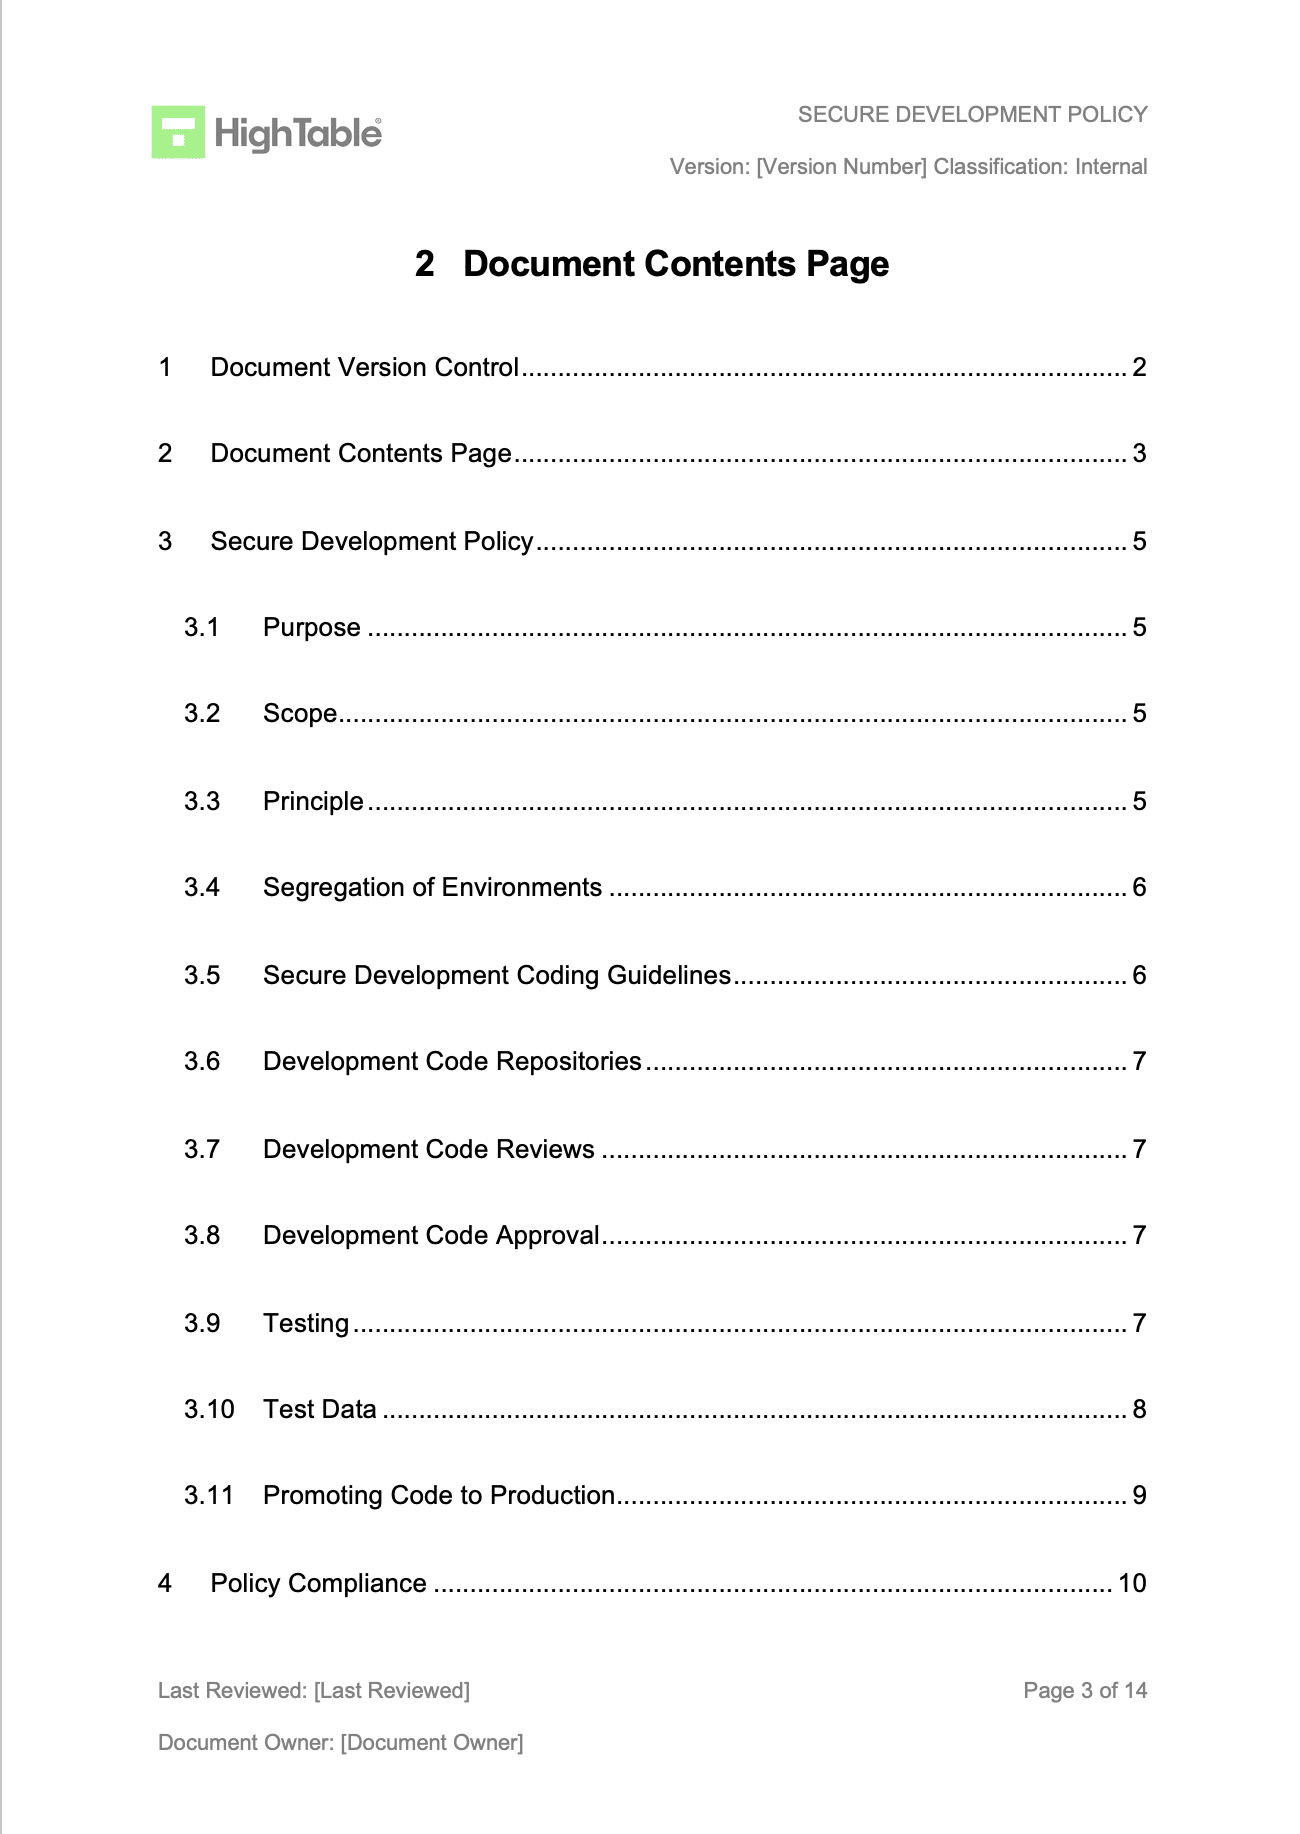
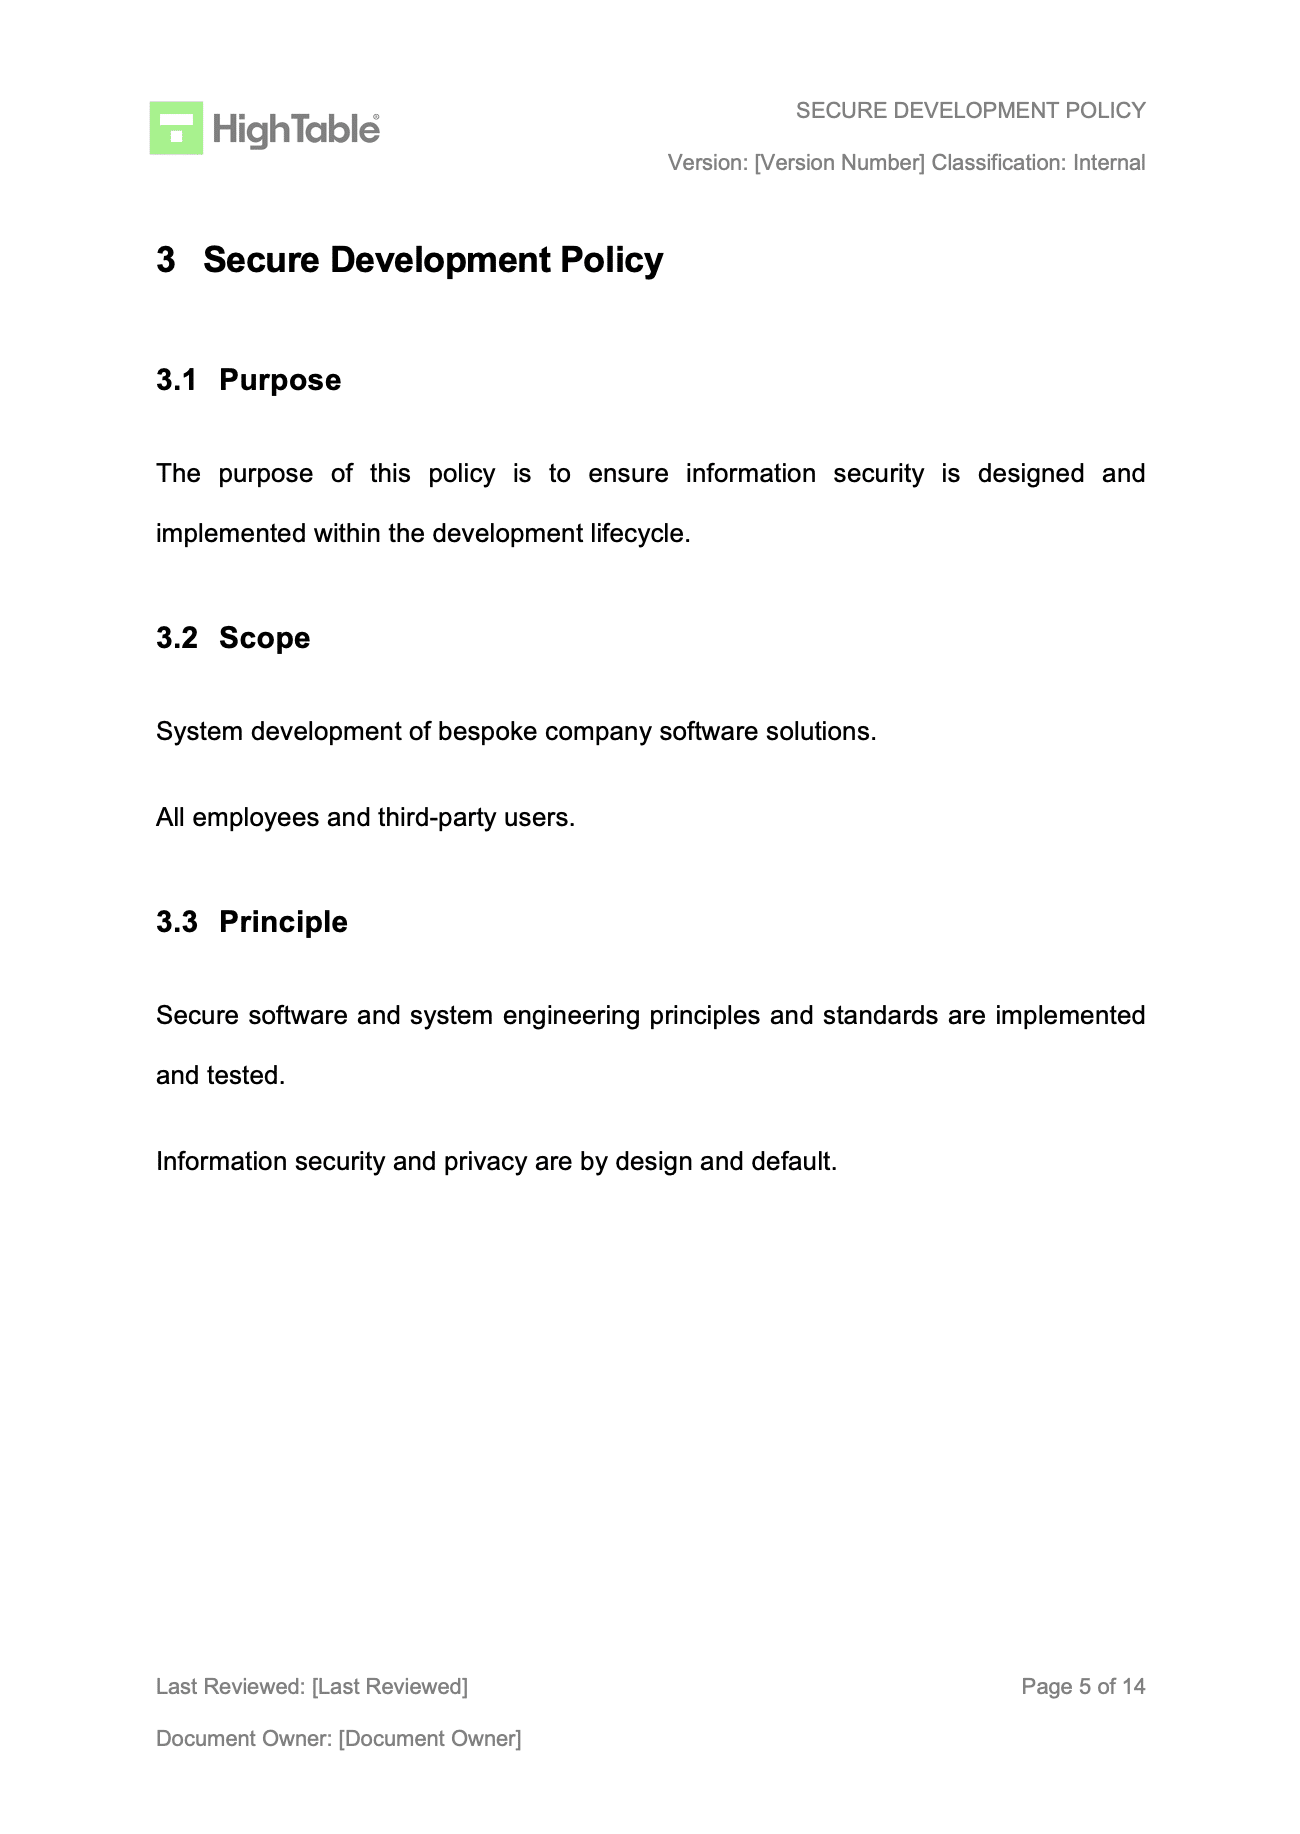
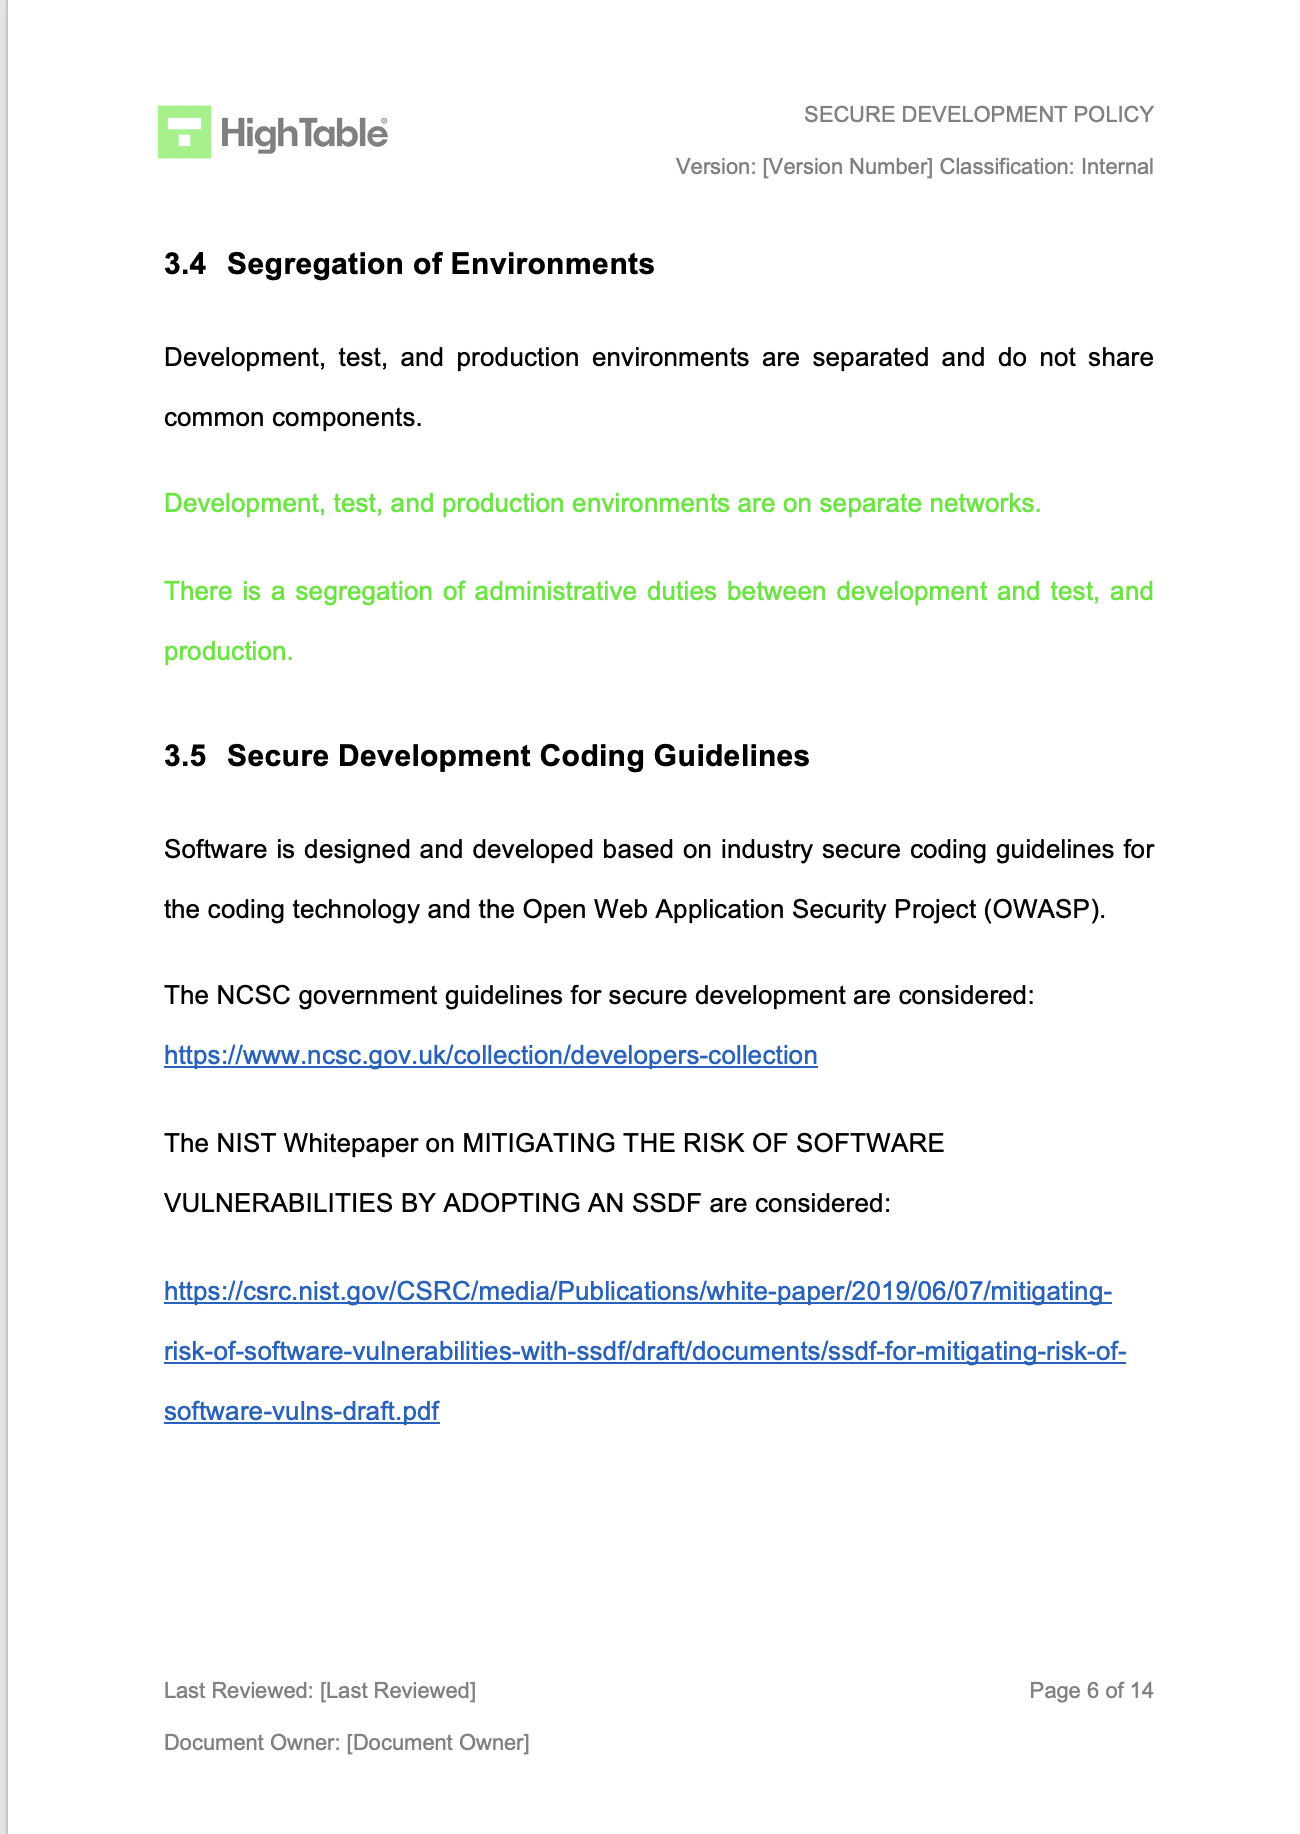
An example ISO 27001 Secure Development Policy:
ISO 27001 Secure Development Policy Template
The ISO 27001:2022 Secure Development Policy Template is designed to fast track your implementation and give you an exclusive, industry best practice policy template that is pre written and ready to go. It is included in the ISO 27001 toolkit.
You can find templates for an ISO 27001 Secure Development Policy online. These templates give you a head start. You can then change them to fit your specific business needs. Using a template can save you time and help you make sure you don’t miss anything important.
Everything you need to know
Why you need it
You need this policy because it’s way easier to build security in than to try and tack it on later. It helps you avoid costly mistakes, protects your reputation, and keeps your customers’ data safe. Plus, it shows everyone that you’re serious about security, which is a big plus for business.
When you need it
You need a secure development policy right from the start of your software journey. The earlier, the better! You’ll use it when you’re planning new features, coding, and even when you’re getting ready to launch your product. It’s a continuous process, not a one-time thing.
Who needs it?
Anyone who builds software needs this policy! This includes developers, project managers, and anyone involved in creating or maintaining your digital products. It’s a team effort to keep things secure.
Where you need it
You need this policy everywhere you create software. It’s for your office, for your remote workers, and for any tools or platforms you use for development. It’s a rulebook that follows you wherever your work takes you.
How to write an ISO 27001 Secure Development Policy
Writing a good policy is all about keeping it simple and clear. You should explain the what, why, and how of secure development. Talk about things like testing your code, managing access to sensitive info, and how to handle security issues. Use easy-to-understand language so everyone can follow it.
Time needed: 1 hour and 30 minutes
How to write an ISO 27001 Secure Development Policy
- Create your version control and document mark-up
- Write the ISO 27001 Secure Development Policy contents page
- Write the ISO 27001 Secure Development Policy purpose
- Write the ISO 27001 Secure Development Policy principle
- Write the ISO 27001 Secure Development Policy scope
- Describe the segregation of environments
- Explain the secure development coding guidelines
- Define the use of development code repositories
- Explain the approach to development code reviews
- Describe development code approval
- Define testing
- Give guidelines on the use of test data
- Explain promoting code to production
How to implement it
Implementing the policy is the fun part! You’ll train your team on the new rules, set up security checks in your workflow, and make sure everyone knows their role in keeping things secure. You’ll also want to check in regularly to make sure the policy is working and make tweaks as needed.
Applicability to Small Businesses, Tech Startups, and AI Companies
This policy is useful for businesses of all sizes, including small businesses, tech startups, and AI companies.
- Small Businesses: You might think ISO 27001 is too much, but it’s really about being smart with your resources. It gives you a structured way to think about security from the very beginning, helping you avoid costly mistakes later on. It’s a strong signal of trustworthiness to your customers and partners, which can set you apart from competitors.
- Tech Startups: Your reputation is everything. A single security incident could stop your growth cold. By following the ISO 27001 framework, you’re building a secure foundation that can handle rapid growth. It shows investors and potential clients that you’re a professional and responsible operation, which is a huge advantage.
- AI Companies: You’re handling a massive amount of data, and that comes with unique risks. ISO 27001 helps you secure the data life cycle, from collection to storage and processing. It ensures you’re protecting sensitive training data and algorithms, which are at the core of your business. This isn’t just a good idea—it’s essential for responsible AI development.
Examples of using it for small businesses
Let’s say you’re a small online shop. Your policy might include simple rules like: always use strong passwords, test your website for security holes before going live, and never store customer credit card numbers on your server.
Examples of using it for tech startups
If you’re a startup building a new app, your policy could cover things like: using secure coding practices (like input validation), doing regular security reviews of your code, and setting up a way for users to report security bugs to you.
Examples of using it for AI companies
For an AI company, your policy is super important. It might include rules like: protecting the data you use to train your models, making sure your AI can’t be tricked into doing something bad, and keeping your AI’s secrets safe from competitors.
How the ISO 27001 toolkit can help
An ISO 27001 toolkit is like a toolbox full of pre-made documents and guides. It gives you a head start on creating your policy and other important security documents, saving you a ton of time and effort. It’s a great way to make sure you don’t miss anything.
ISO 27001 Toolkit
All the templates, tools, support and knowledge you need to do it yourself.
Information security standards that need it
This policy is a key part of ISO 27001, which is an international standard for managing information security. Other standards that need it include:
- GDPR (General Data Protection Regulation)
- CCPA (California Consumer Privacy Act)
- DORA (Digital Operational Resilience Act)
- NIS2 (Network and Information Security (NIS) Directive)
- SOC 2 (Service Organisation Control 2)
- NIST (National Institute of Standards and Technology)
- HIPAA (Health Insurance Portability and Accountability Act)
List of relevant ISO 27001:2022 controls
The ISO 27001:2022 standard has specific controls that relate to secure development. Some of the most important ones include:
- ISO 27001:2022 Annex A 8.25 Secure Development Life Cycle
- ISO 27001:2022 Annex A 8.26 Application Security Requirements
- ISO 27001:2022 Annex A 8.27 Secure Systems Architecture and Engineering Principles
- ISO 27001:2022 Annex A 8.28 Secure Coding
- ISO 27001:2022 Annex A 8.29 Security Testing in Development and Acceptance
- ISO 27001:2022 Annex A 8.30 Outsourced Development
- ISO 27001:2022 Annex A 8.31 Separation of Development, Test and Production Environments
ISO 27001 Secure Development Policy FAQ
The main goal is to make sure security is a core part of your software from the very beginning.
Nope! It’s for any size company that builds software.
No, you don’t! You can use templates and get help from experts if you need it.
It can take anywhere from a few hours to a few weeks, depending on how detailed you want to be.
Not following it can lead to security breaches, lost data, and a damaged reputation.
No, it’s a living document that you should review and update regularly.
It’s a good idea to review it at least once a year.
You need to explain it in simple terms and offer training so everyone gets it.
No, it works with them. The policy tells you how to use your tools wisely.
A policy is a high-level rule, while a procedure is a step-by-step guide on how to follow that rule.
No, it’s for any kind of software, including mobile apps and desktop programs.
It protects your data, builds customer trust, and can save you from a lot of trouble later on.
The first step is to decide who will be in charge of writing and implementing it.
About the author
