
ISO 27001:2022 Annex A 8.30 (Outsourced Development) is an ISO 27001 control that requires an organisation to make sure that outsourced developments are meeting organisational information security requirements.
In this guide you will learn how to implement Outsourced Development (ISO 27001 Annex A 8.30) and pass your audit from ISO 27001 Lead Auditor Stuart Barker – author of the ultimate ISO 27001 Toolkit.
Table of contents
- Key Takeaways
- ISO 27001 Annex A 8.26 Purpose & Definition
- Outsourced Development Guidelines
- How to implement ISO 27001 Outsourced Development (Annex A 8.30)
- ISO 27001 Annex A 8.30 Toolkit & Templates
- How to audit ISO 27001 Annex A 8.30
- Conclusion
- ISO 27002:2022 Control 8.30 (Outsourced Development)
- ISO 27001 Annex A 8.30 FAQ
- Related ISO 27001:2022 Annex A Controls
- Stuart Barker
Key Takeaways
- If you hire third-party developers (agencies, freelancers, or offshore teams) to build software for you, you must supervise their security standards.
- You cannot simply trust them to “do a good job.”
- You must define your security requirements in the contract and verify they are met before accepting the final code.
ISO 27001 Annex A 8.26 Purpose & Definition
ISO 27001 Annex A 8.26 is a preventive control and a detective control to ensure information security measures required by the organisation are implemented in outsourced system development.
The ISO 27001 Standard defines ISO 27001 Annex A 8.30 as:
The organisation should direct, monitor and review the activities related to outsourced system development.
ISO/IEC 27001:2022 Annex A 8.30 Outsourced Development
Outsourced Development Guidelines
There are nine essential elements of a comprehensive Outsourced Development as covered the control guidance in ISO 27002:2022 Control 8.30 (Outsourced Development):
- The intellectual property, licensing and ownership of outsourced code
- Contractual requirements for information security and secure coding practices
- The threat model to be used to evaluate code against
- Having evidence of security and privacy capability
- Demonstrating security testing has been done
- Escrow agreements for source code as required
- The right to audit controls and processes
- Security requirements for development environments
- Laws and regulations
How to implement ISO 27001 Outsourced Development (Annex A 8.30)
This is all about managing your outsourced development and making sure that it, and they, are following your requirements for information security. This will be done by telling them what you expect, getting it into agreements such as contracts and then regularly reviewing and monitoring them to ensure that it is being done.
In addition, we treat the developers as a third party for which the following will apply:
- ISO 27001 Annex A 5.19 Information Security In Supplier Relationships
- ISO 27001 Annex A 5.20 Addressing Information Security Within Supplier Agreements
- ISO 27001 Annex A 5.22 Monitor, Review And Change Management Of Supplier Services
Licensing
Getting licensing right is key. You will have documented this and who owns code and intellectual property.
The following will apply: ISO 27001 Annex A 5.32 Intellectual Property Rights
Contracts
You will have contract in place and followed the contractual requirements for secure design, coding and test.
The following will apply: ISO27001 Annex A 8.25 Secure Development Life Cycle
You will have provided them the threat model to consider.
There will be the requirement to provide evidence, and actual evidence, that sufficient testing has been conducted.
Escrow agreements where appropriate will be defined, document and evidenced.
The right to audit will be included in the contact.
Security requirements for the development environment will be in place.
The requirements of all laws and regulations will be in place.
Outsourced Development
If you outsource your development then the third party supplier controls will apply. The main thing is to ensure they meet your requirements for secure development but all relevant controls that apply to you, will apply to them.
1. Vendor Selection and Due Diligence
Conduct thorough due diligence on potential outsourced developers, assessing their information security posture, certifications (e.g., ISO 27001, SOC 2), and track record. Include security requirements in supplier selection criteria and RFPs.
Challenges: Limited vendor transparency, difficulty evaluating vendor claims.
Solutions: Third-party audits, detailed security questionnaires, reference checks.
2. Contractual Agreements
Include comprehensive security clauses in all contracts with outsourced development vendors, defining responsibilities, liabilities, and obligations related to information security.
Challenges: Negotiating strong contracts, enforcing contractual obligations.
Solutions: Legal counsel, regular contract reviews, dispute resolution mechanisms.
3. Information Sharing & Access Controls
Implementation: Establish secure procedures for sharing sensitive information with vendors, implement robust access controls, and utilise secure communication channels.
Challenges: Data breaches, insider threats.
Solutions: Data Loss Prevention (DLP) tools, security awareness training, background checks.
4. Data Protection & Privacy
Ensure compliance with relevant data protection regulations (e.g., GDPR) when sharing data with outsourced developers. Implement appropriate data protection measures, such as data masking and encryption.
Challenges: Meeting evolving data privacy regulations, ensuring vendor compliance.
Solutions: Data processing agreements, regular privacy impact assessments, ongoing supplier monitoring.
5. Incident Management
Establish clear incident reporting procedures, develop a joint incident response plan with vendors, and conduct regular incident response drills.
Challenges: Timely incident detection and response, coordination with vendors.
Solutions: Security Information and Event Management (SIEM) systems, automated incident response tools, clear communication procedures.
6. Physical and Environmental Security
Ensure that vendors maintain adequate physical and environmental security measures, including secure facilities, access controls, and environmental controls.
Challenges: Assessing and verifying vendor physical security measures.
Solutions: On-site audits, remote monitoring of security systems, third-party security assessments.
7. Human Resources Security
Ensure that vendors have robust HR security practices, including background checks, employee security training, and secure employee onboarding and off-boarding procedures.
Challenges: Ensuring compliance with vendor HR security practices.
Solutions: Contractual requirements, regular vendor assessments, third-party HR security audits.
8. System and Application Security
Ensure that vendors have robust systems and application security controls, including secure development practices, vulnerability management, and regular security testing.
Challenges: Assessing the security of complex systems and applications.
Solutions: Penetration testing, vulnerability assessments, code reviews, secure development lifecycle (SDLC) processes.
9. Business Continuity and Disaster Recovery
Ensure that vendors have business continuity and disaster recovery plans in place to minimise the impact of disruptions on outsourced services.
Challenges: Verifying the effectiveness of vendor BCP/DR plans.
Solutions: Business impact analysis, disaster recovery drills, regular review and updates of BCP/DR plans.
10. Continuous Monitoring & Improvement
Conduct regular security audits and assessments of outsourced development activities, monitor vendor performance against agreed-upon security controls and KPIs, and continuously improve security processes.
Challenges: Maintaining visibility into vendor security practices, resource constraints.
Solutions: Third-party audits, automated monitoring tools, regular review and improvement of security controls.
ISO 27001 Annex A 8.30 Toolkit & Templates
Secure Development Policy Template
The secure development policy includes the approach to outsourced development.
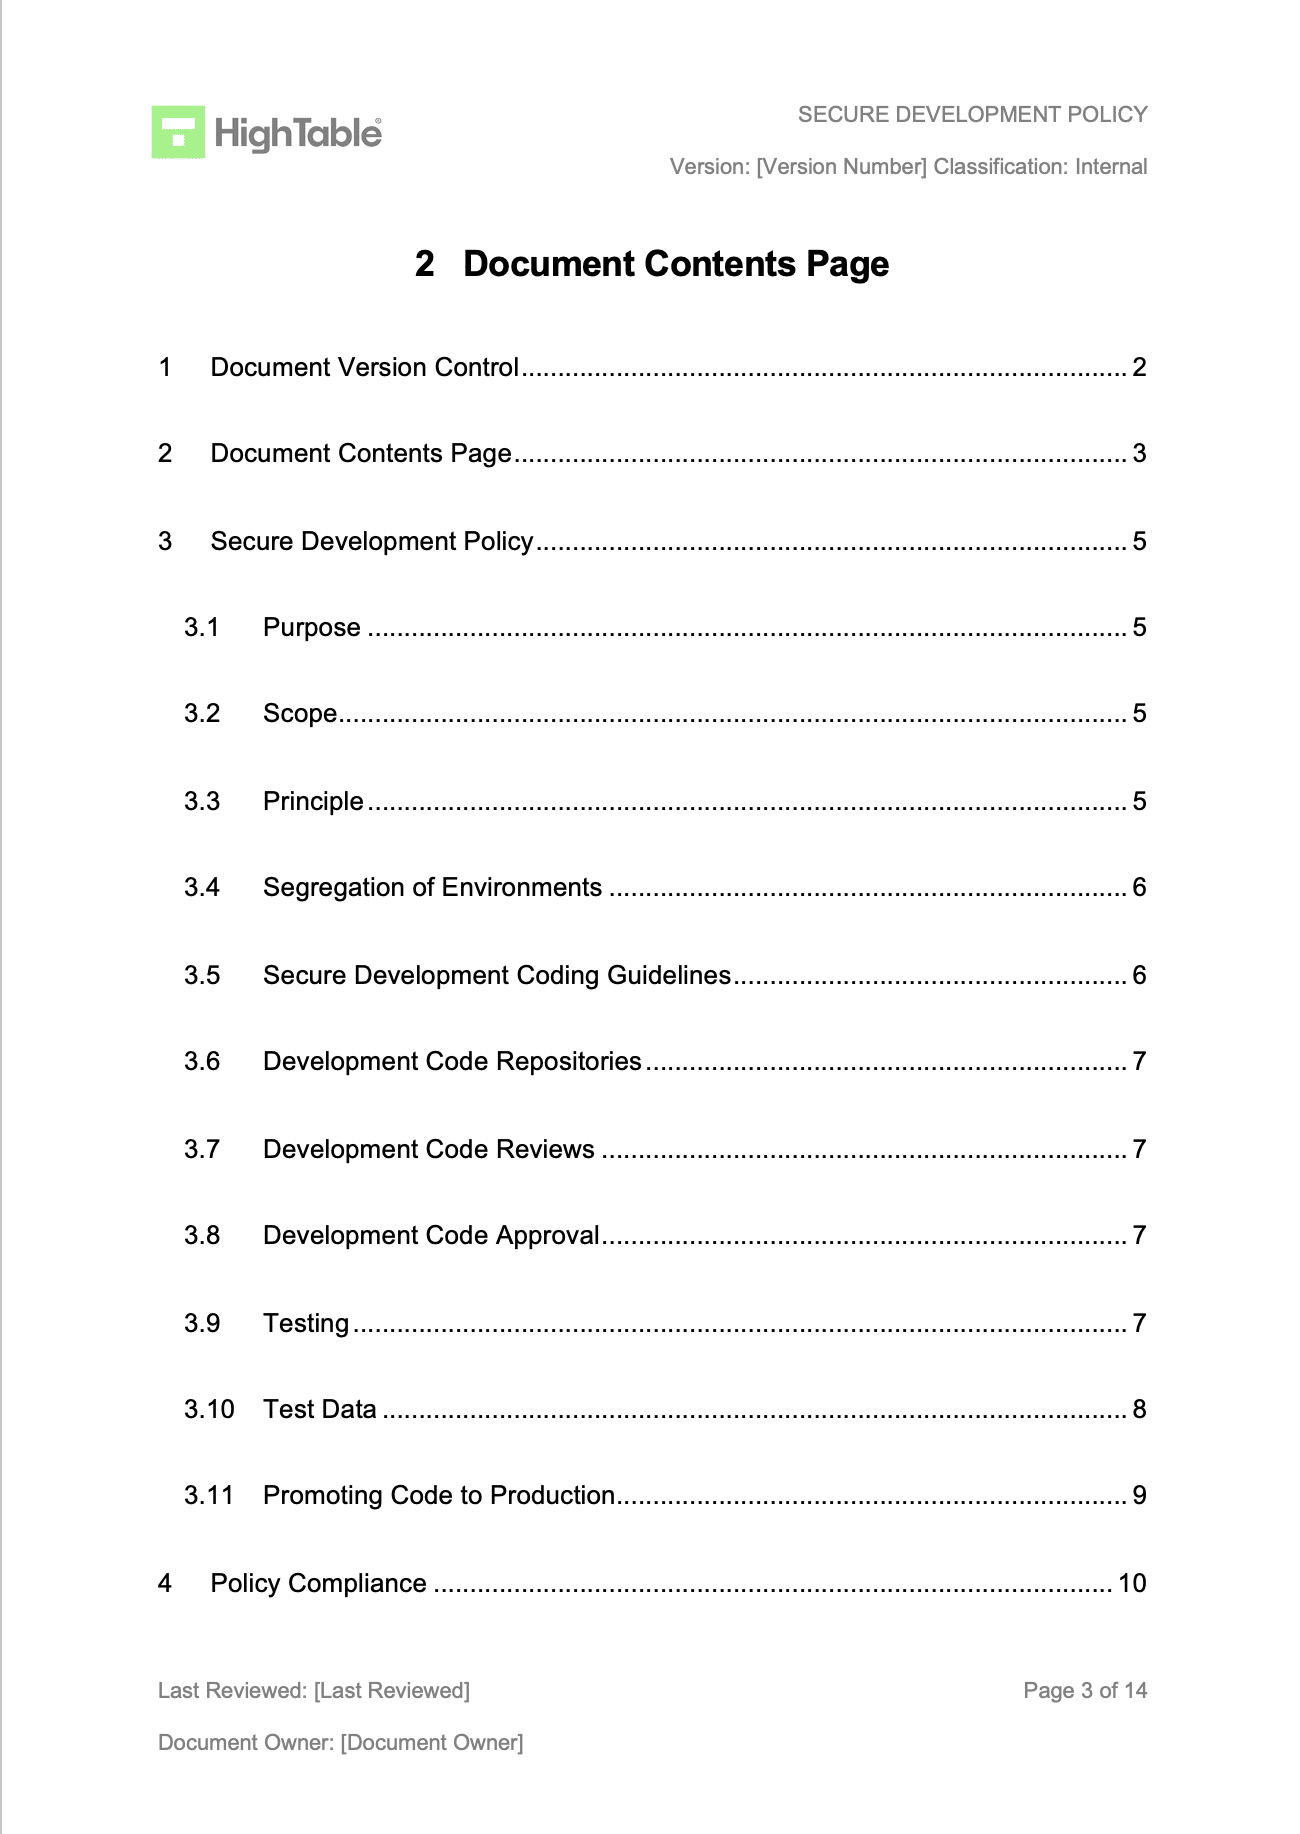
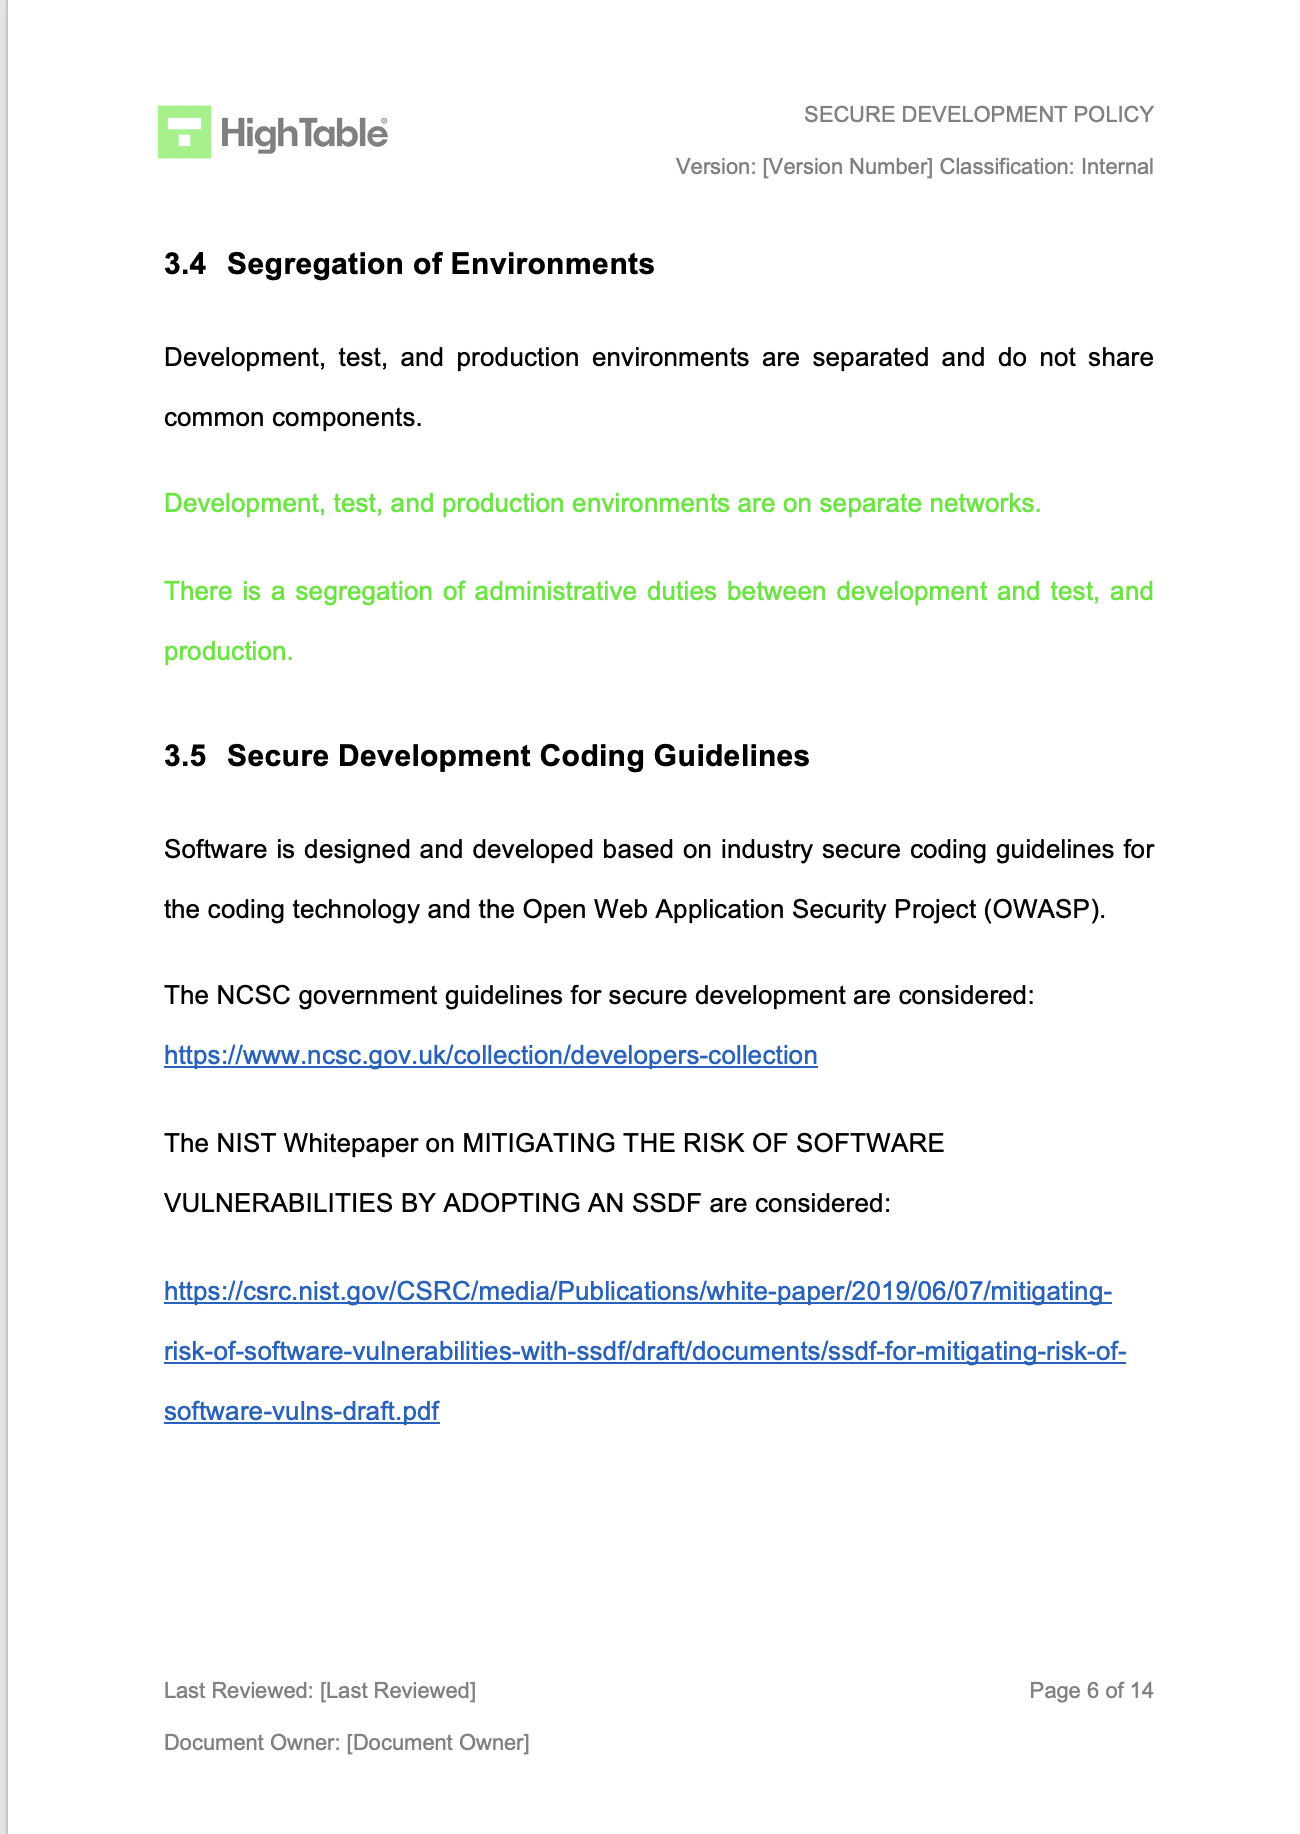
Secure Development Policy Example
An example of the ISO 27001 secure development policy.
Supplier Security Policy Template
The supplier security policy sets our your approach to manage the security of third party suppliers including outsourced developers.
Supplier Register Template
The supplier register template records your third party suppliers including your outsourced developers.
ISO 27001 Toolkit
Everything a business needs to do ISO 27001 and get ISO 27001 certified in the High Table ISO 27001 Toolkit: Business Edition.
How to audit ISO 27001 Annex A 8.30
ISO 27001 Annex A 8.30 Outsourced Development Audit Checklist
- 1. Audit the Outsourced Developer Management
- 2. Review Vendor Selection and Due Diligence
- 3. Check Contractual Agreements
- 4. Review Information Sharing & Access Controls
- 5. Ensure Data Protection & Privacy
- 6. Incident Management
- 7. Physical and Environmental Security
- 8. Human Resources Security
- 9. System and Application Security
- 10. Business Continuity and Disaster Recovery
- 11. Continuous Monitoring & Improvement
Conclusion
Many if not all of the controls that apply to this control are covered elsewhere. Be it the experience, licensing, technical controls but consider them in the context of this clause and be able to evidence them as they apply to outsourced development.
ISO 27002:2022 Control 8.30 (Outsourced Development)
ISO 27002:2022 Control 8.30 provides implementation guidance for Outsourced Development.
ISO 27001 Annex A 8.30 FAQ
Contracts must go beyond functionality and explicitly define security obligations and the right to audit. To comply with Control 8.30, your agreement should specify:
Secure Coding Standards: The vendor must follow specific guidelines (e.g., OWASP Top 10) to prevent vulnerabilities.
Testing Requirements: Mandating Static (SAST) and Dynamic (DAST) application security testing prior to delivery.
Right to Audit: Your organisation’s right to review their code, architecture, or security logs.
Intellectual Property: Clarity on who owns the code and who is responsible for fixing security bugs discovered post-launch.
Monitoring must be active and evidence-based, occurring at milestones rather than just at final delivery. Effective supervision methods include:
Regular Code Reviews: Requesting access to the repository to spot-check code quality and security practices.
vCISO / Security Reviews: Having your security team review the proposed architecture before coding begins (Security by Design).
Testing Evidence: Requiring the vendor to submit reports from their vulnerability scans before you accept the software.
It applies strictly to custom development (outsourced coding), regardless of whether it is a freelancer or a large agency.
Freelancers/Agencies: Yes. If they are writing code specifically for you, Control 8.30 applies.
COTS (Commercial Off-The-Shelf): Generally No. Buying standard software (like Microsoft Office) falls under Supplier Relationships (5.19), specifically “Information security in supplier relationships,” rather than outsourced development.
Auditors will look for evidence that you managed the security risk, rather than just the timeline or budget. Expect questions such as:
“Show me the contract where you defined the security requirements for this project.”
“How did you verify the developer followed your secure coding guidelines?”
“Did you scan the delivered code for malware or vulnerabilities before deploying it to production?”
“Show me the acceptance criteria you used to sign off on the security of this release.”
Control 8.30 is specific to the creation of software, while Control 5.19 covers the general business relationship.
Annex A 5.19 (Supplier Relationships): Focuses on the contract, access management, and general service delivery (e.g., “Do they have ISO 27001 certification?”).
Annex A 8.30 (Outsourced Development): Focuses on the product being built (e.g., “Did they sanitise inputs to prevent SQL injection?” or “Did they remove hardcoded passwords?”).
Related ISO 27001:2022 Annex A Controls
The following controls are directly related to ISO 27001 Annex A 8.30:
- ISO 27001 Monitoring, Measurement, Analysis, Evaluation: Clause 9.1
- ISO 27001 Secure Systems Architecture and Engineering Principles: Annex A 8.27
- ISO 27001 Security Testing in Development and Acceptance: Annex A 8.29
Stuart Barker
Stuart Barker is qualified ISO 27001 Lead Auditor and a veteran practitioner with over 30 years of experience in systems security and risk management. Holding an MSc in Software and Systems Security, he combines academic rigour with extensive operational experience, including a decade leading Data Governance for General Electric (GE).
Now he is founder and Lead ISO 27001 Consultant at High Table, the worlds number 1 dedicated ISO 27001 Consultancy.
