
In this guide you will learn how to implement ISO 27001 Annex A 8.25 Secure Development Life Cycle and pass your audit from ISO 27001 Lead Auditor Stuart Barker – author of the ultimate ISO 27001 Toolkit.
ISO 27001 Annex A 8.25 Secure Development Life Cycle is an ISO 27001 control that requires us to develop code and software and systems with information security designed and built in. You may hear the term – ‘security by design and default’.
Table of contents
Key Takeaways
- ISO 27001 Annex A 8.25 mandates that security is integrated into every stage of software development from the initial idea to the final release.
- It moves organisations away from “building it first and securing it later” towards a Secure Software Development Life Cycle (SSDLC), ensuring that vulnerabilities are caught early when they are cheapest to fix.
Purpose & Definition
ISO 27001 Annex A 8.25 is a preventive control to ensure information security is designed and implemented within the secure development life cycle of software and systems.
The ISO 27001 standard defines ISO 27001 Annex A 8.25 as:
Rules for the secure development of software and systems should be established and applied.
ISO27001:2022 Annex A 8.25 Secure Development Life Cycle

ISO 27001 Starter Kit
Instant download of mandatory ISMS core policies and documentation. Verified by Lead Auditors and used by 5,000+ businesses worldwide to pass Stage 1 certification first time.
ISO 27001 Annex A 8.25 Requirements and Guidance
I am not in the business of telling you how to develop either systems or software. These are professions in their own right. What I am going to do is show you want the ISO 27001 standard expects in the implementation for you to achieve ISO 27001 certification. These are on the whole, no brainers, common sense and what you would expect but let us take a look anyway.
Secure Development Policy
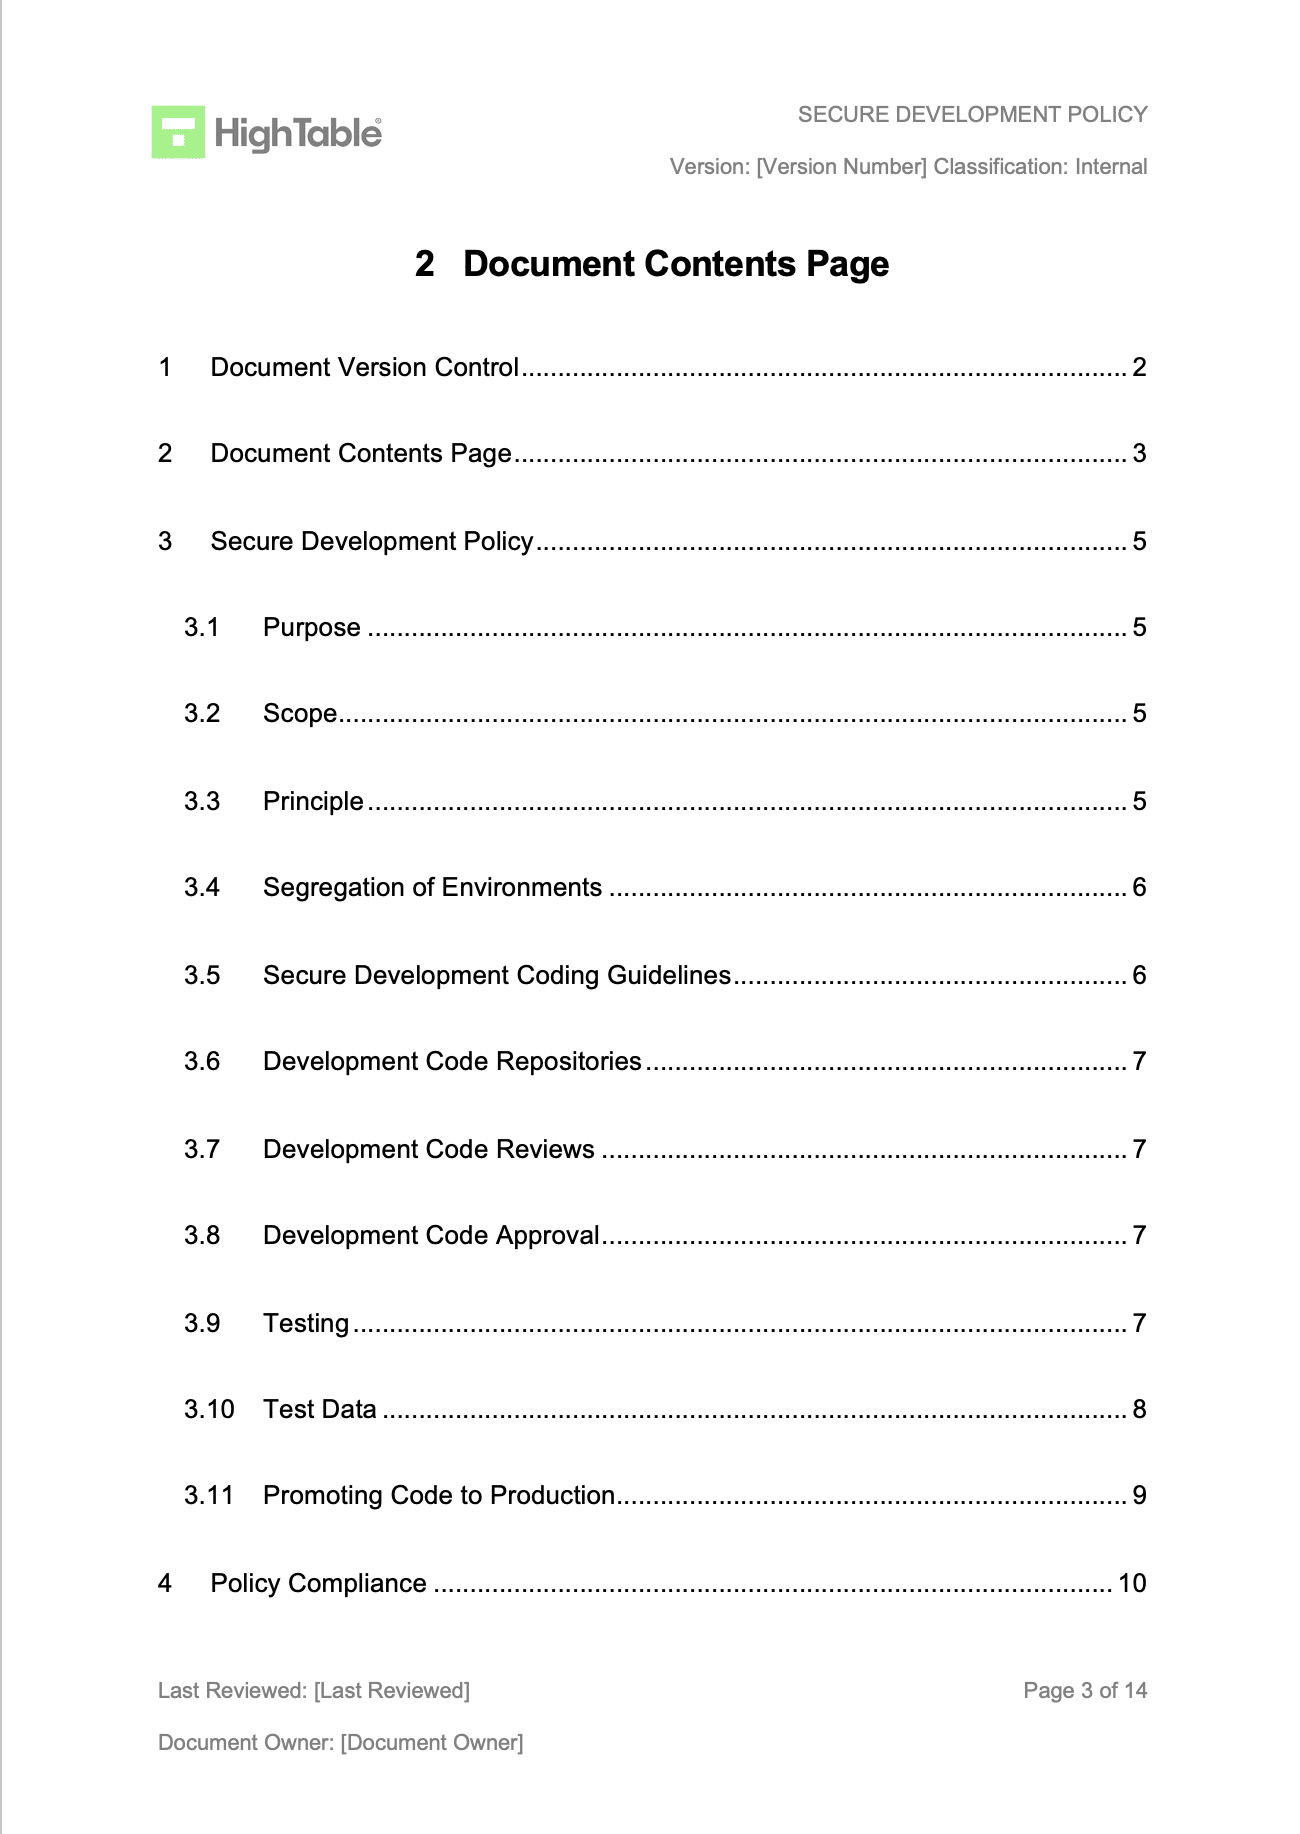
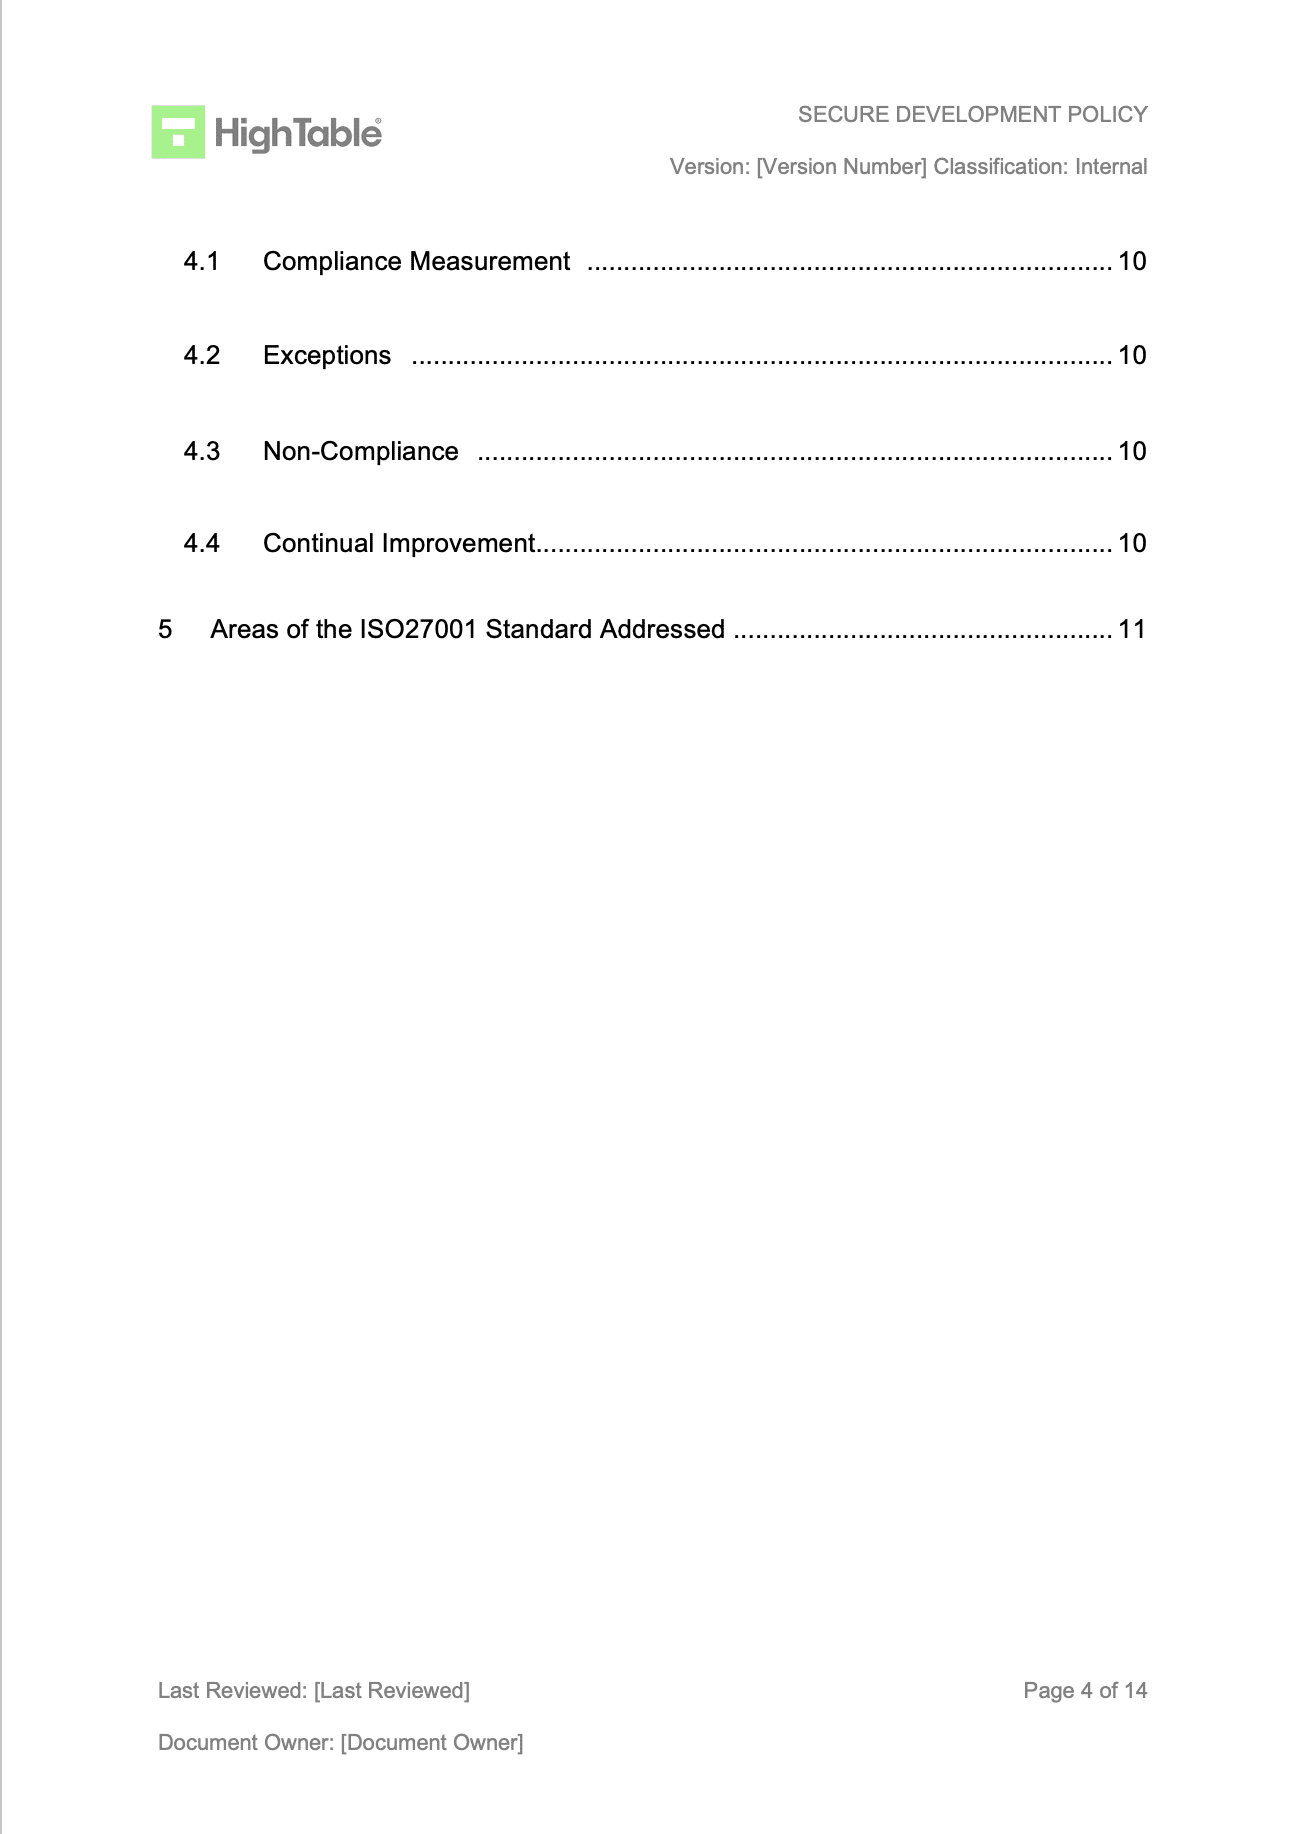
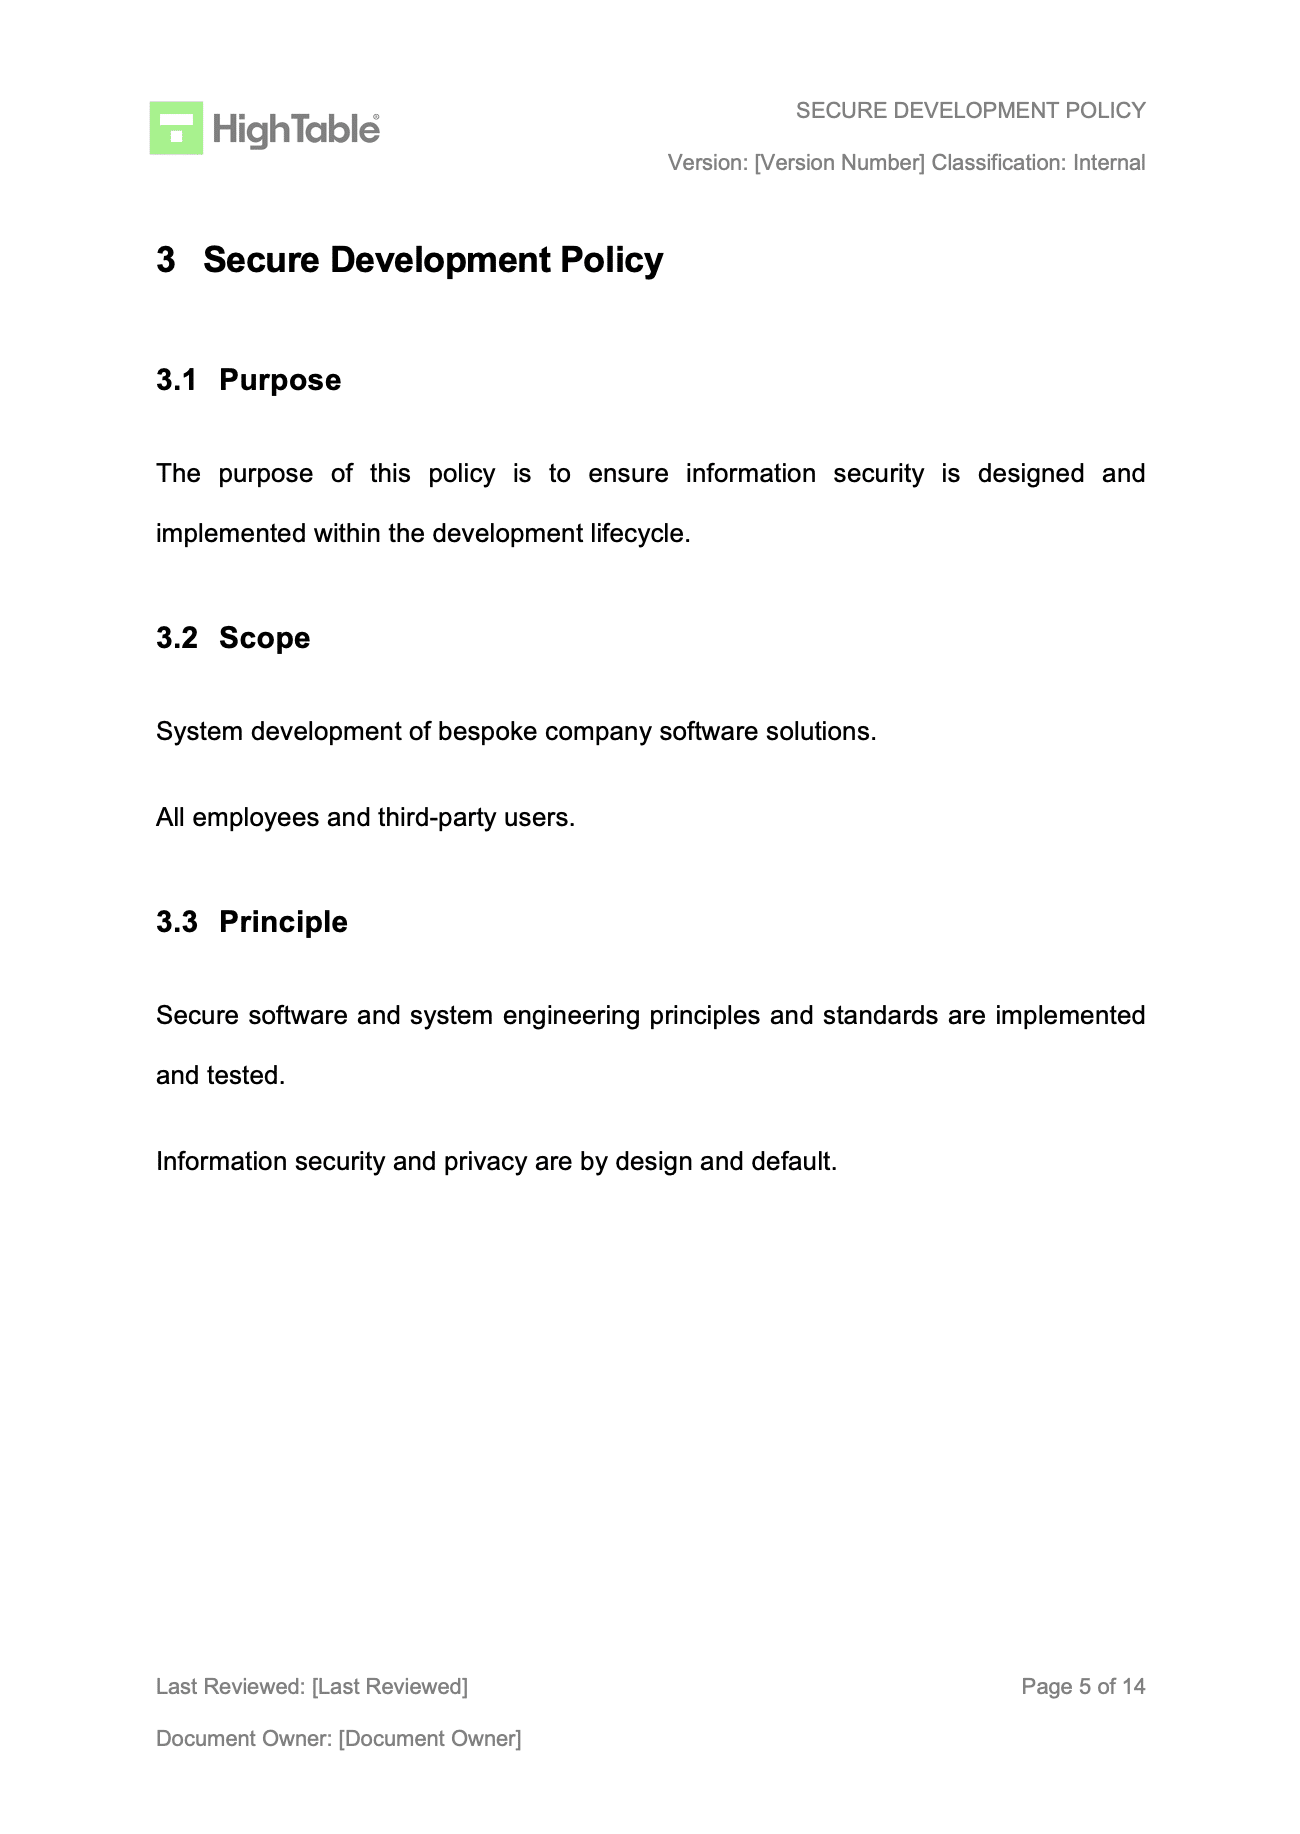
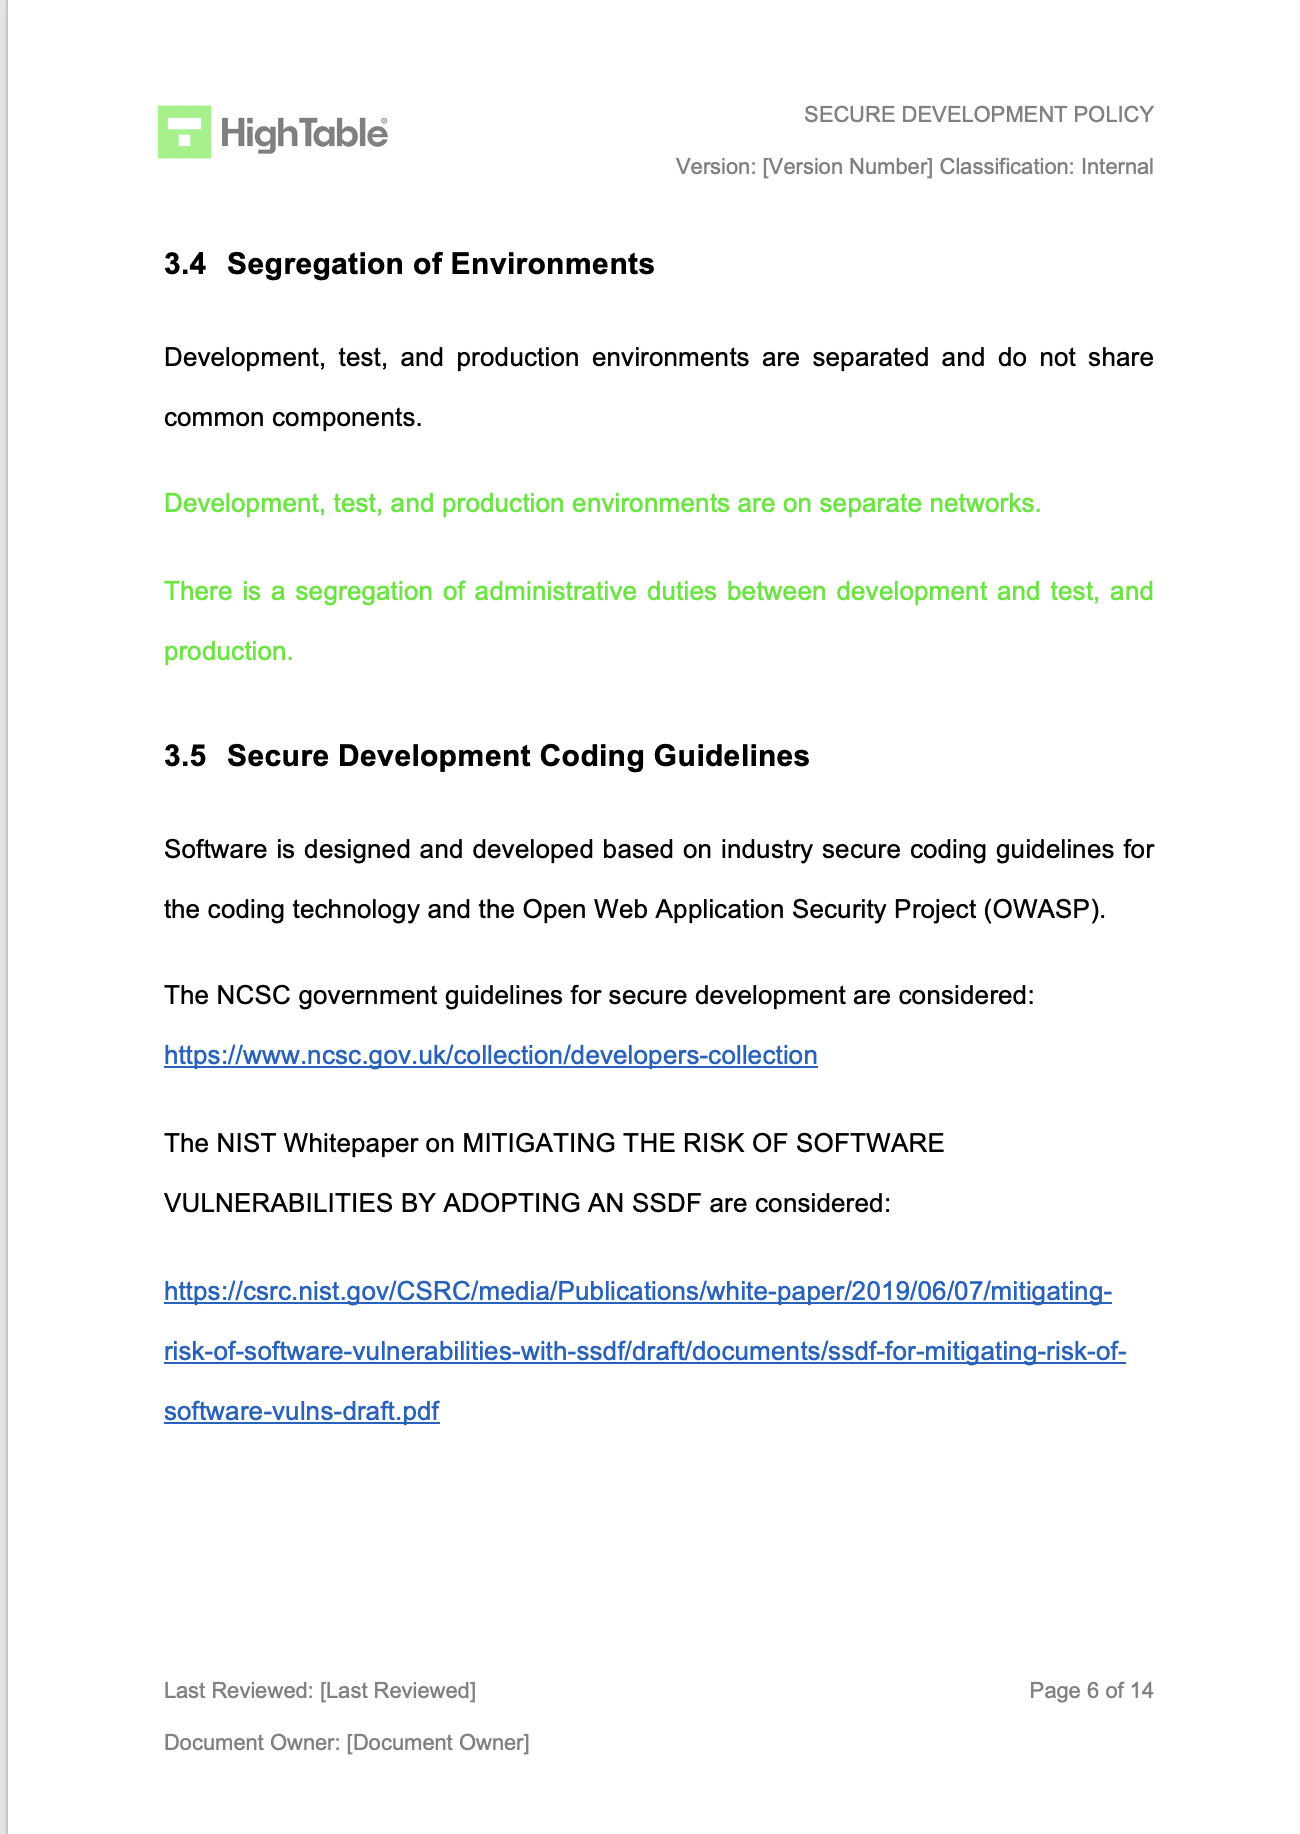
The first step is to create, or download, your secure development policy. The secure development policy set’s out what you do for information security in the context of software and systems development. It does not set out how you do it, as how you do it is covered in your processes.
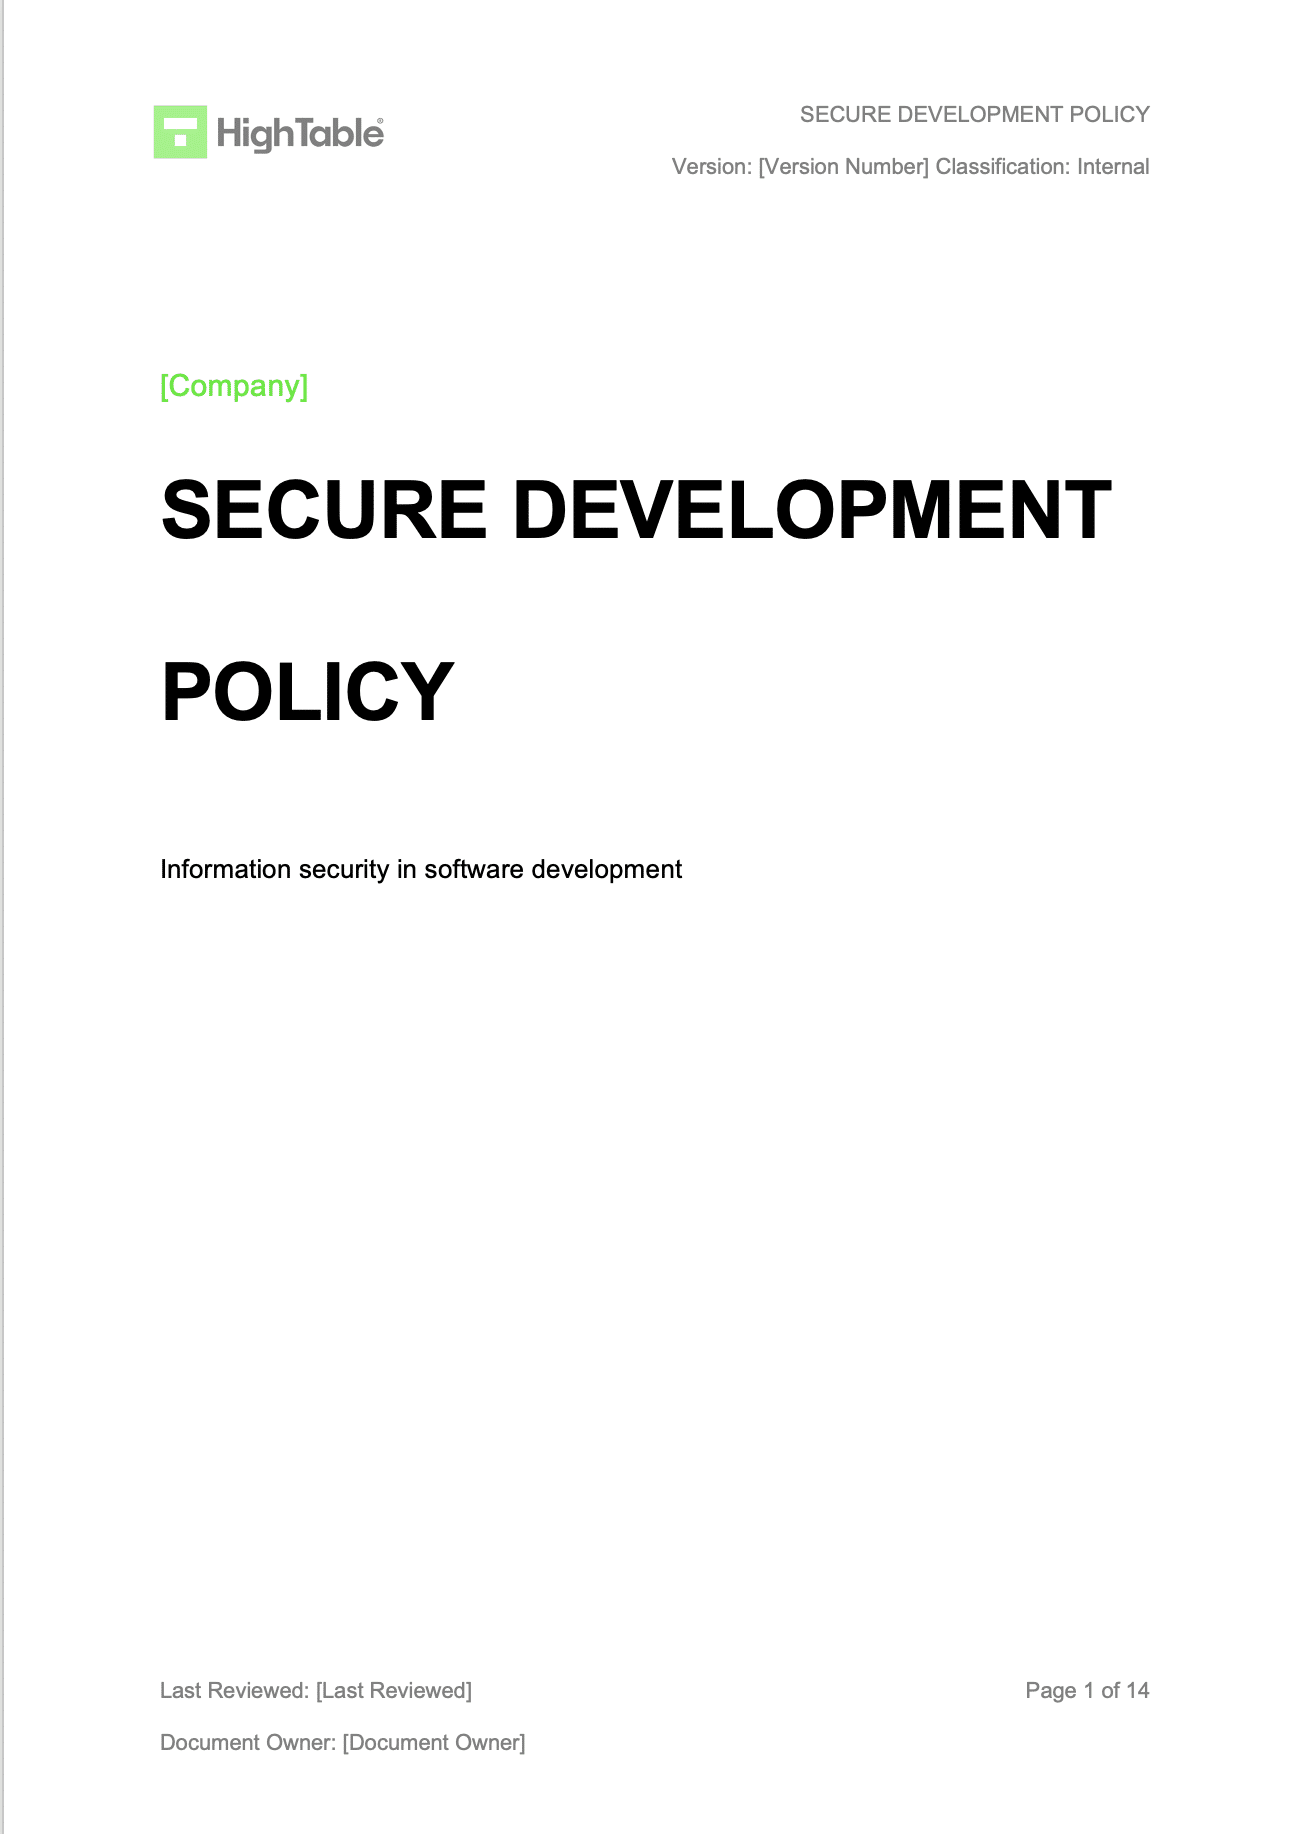
Secure Development Policy Example
An example of the ISO 27001 secure development policy.
Coding Guidelines
You are going to make sure that you have documented coding guidelines. These can be standard guidelines or industry best practice, and you likely already do this today, just make sure that this written down, communicated and available to those that need it.
Separate Environments
You are going to make sure that for the inscope developments that you have separate development, test and live environments with the appropriate management and controls in place around this. This will include the process of promoting through those environments and the authorisations and approvals and acceptance.
Specification and Design
What ever methodology you use it is likely to have a specification and design phase. I am not sure of a situation where you would not, although could, but it is at these phases that you will evidence that information security was considered. Here we place a lot of reliance on ISO 27001 Annex A 5.8 Information Security In Project Management. The same is true when it comes to security checkpoints in projects.
The advice here would be to have in your project management either a placeholder in an existing template / document or create a security specific one. Be sure you are considering things like access requirements, data transfers, technical controls, risks and risk mitigations. Have checkpoints with go / no go decisions and a process for what you do if the checkpoint fails.
Testing
All secure development will have testing. It is not our place, again, to tell you how to test as again, this is a profession in its own right but there must be a level of security testing in place that looks at the three parts of information security being confidentiality, integrity and availability.
Simple testing that can be considered here would be penetration testing, vulnerability testing, regression testing, code scanning and code testing.
Code Repositories
The configuration and management of code and code libraries should be carefully considered and documented. Many tools exist that can help with this and automate many of the tasks.
Knowledge and Experience
The standard touches on this in a number of areas, having people with the right knowledge and / or experience to perform the role. This is also true of the secure development lifecycle. Having a competency matrix and being able to point to qualifications or certifications will help. Where there are gaps a plan, such as training, should be in place but these are basic HR and people functions that are common place in any role.
Outsourced Development
If you outsource your development then the third party supplier controls will apply. The main thing is to ensure they meet your requirements for secure development but all relevant controls will apply to them.
Check Your Work?
You buit it yourself. Maybe with AI. But will it pass the audit?
Don’t gamble – let a trained ISO 27001 auditor check your work.
How to implement ISO 27001 Annex A 8.25
Establishing a Secure Development Life Cycle (SDLC) is essential for embedding security into every phase of software creation. By following these technical implementation steps, your organisation can mitigate supply chain risks and ensure compliance with ISO 27001 Annex A 8.25 standards through a proactive shift left security approach.
1. Formalise the Secure SDLC Policy and Framework
- Define and document a mandatory security framework that governs the entire software development process from initial requirement gathering to decommissioning.
- Appoint security champions within development teams to act as the primary point of contact for technical security queries and compliance checks.
- Result: A structured governance model that ensures security is not treated as an afterthought but as a core functional requirement.
2. Execute Threat Modelling and Security Requirement Analysis
- Conduct structured threat modelling sessions during the design phase using methodologies such as STRIDE to identify potential architectural flaws early.
- Document specific security requirements, including Identity and Access Management (IAM) roles and data encryption standards, for every new feature or system update.
- Result: The identification and mitigation of high level risks before the first line of code is even written.
3. Enforce Secure Coding Standards and Developer Training
- Mandate the use of industry recognised secure coding standards such as OWASP Top 10 or CERT to prevent common vulnerabilities like SQL injection and XSS.
- Provision regular security awareness training for developers to ensure they are equipped to handle modern threats and utilise secure library components.
- Result: A significant reduction in human error and the creation of a naturally resilient codebase.
4. Integrate Automated Security Testing into CI/CD Pipelines
- Configure Static Application Security Testing (SAST) and Software Composition Analysis (SCA) tools to run automatically upon every code commit or pull request.
- Enable build breakers that prevent code from progressing through the pipeline if critical or high severity vulnerabilities are detected.
- Result: Continuous security verification that provides real time feedback to developers and prevents the introduction of insecure dependencies.
5. Mandate Independent Peer Reviews and Security Sign-Off
- Require a four eyes principle for all code changes, ensuring that a second qualified developer reviews the code for both logic errors and security flaws.
- Establish a formal security sign-off process before any release is promoted to production, verified by a Technical Documentation Lead or Security Officer.
- Result: An immutable audit trail of approvals that ensures accountability and protects the integrity of the production environment.
6. Provision Isolated Development and Testing Environments
- Ensure that development, testing, and production environments are logically and physically separated to prevent the accidental exposure of live data.
- Enforce Multi-Factor Authentication (MFA) and strict access controls for any developer interacting with the staging or build infrastructure.
- Result: The elimination of cross contamination risks and the protection of sensitive production assets from unverified development code.
ISO 27001 Templates
Everything you need to do ISO 27001.
Conclusion
Many if not all of the controls that apply to this control are covered elsewhere. Be it the experience, licensing, technical controls but consider them in the context of this clause and be able to evidence them as they apply to secure development.
ISO 27001 Annex A 8.25 FAQ
A Secure SDLC ensures “checkpoints” exist at every phase of development. While specific methodologies (like Agile or Waterfall) vary, the core security stages must include:
Requirements: Defining security needs (e.g., “Must support MFA”) before building.
Design: Reviewing architecture for risks (Threat Modeling).
Development: Using secure coding standards (Annex A 8.28) and static analysis.
Testing: Verifying security with dynamic scanning and penetration testing (Annex A 8.29).
Deployment: Secure release procedures and environment separation.
Yes, the control is methodology-agnostic and applies equally to Agile, DevOps, and Waterfall. In modern DevSecOps environments, compliance is achieved by:
Automating Security: Integrating scanning tools (SAST/DAST) directly into the CI/CD pipeline.
Sprint Planning: Including security tasks or “Abuser Stories” in the product backlog.
Continuous Feedback: Fixing security bugs in real-time rather than waiting for a final audit.
Yes, you are responsible for ensuring your vendors follow a secure lifecycle, even if you don’t write the code yourself. You must enforce this through:
Contracts: Explicitly requiring the vendor to demonstrate their Secure SDLC policy.
Right to Audit: Verifying their testing reports before accepting the software.
Integration: Ensuring their delivery process matches your security requirements (Control 8.30 Outsourced Development).
SDLC covers the creation of new software, while Change Management covers modifications to existing systems.
Annex A 8.25 (Secure SDLC): Focuses on the engineering process (Requirements, Coding, Testing).
Annex A 8.32 (Change Management): Focuses on the authorization and risk assessment of deploying that change to Production. In practice, the end of the SDLC (Deployment) triggers the Change Management process.
Auditors look for evidence of a defined process, not just safe code. Expect questions such as:
“Show me your Secure Development Policy.”
“Can you demonstrate the security checkpoints in your CI/CD pipeline?”
“Show me a recent feature where security requirements were defined before coding started.”
“How do you ensure developers follow these rules?”
Related ISO 27001 Controls
About the author