
ISO 27001:2022 Clause 10.1 (Continual Improvement) is a mandatory governance requirement dictating that organizations proactively enhance the suitability, adequacy, and effectiveness of their Information Security Management System (ISMS), requiring documented evidence of proactive maturity across audit results, security metrics, and corrective actions to pass surveillance audits.
In this guide, you will learn how to implement Clause 10.1 correctly – leveraging existing engineering upgrades, tracking measurable ISMS maturity, preventing compliance stagnation, and passing your audit – with expert guidance from leading ISO 27001 consultant and certified Lead Auditor Stuart Barker, Director at HT Black Consulting (formerly High Table), the specialist ISO 27001 consultancy.
Table of contents
- Key Takeaways
- ISO 27001 Clause 10.1 Purpose & Definition
- ISO 27001 Clause 10.1 Tutorial Video
- Implementation Guide
- How to implement ISO 27001 Clause 10.1
- 1. Implement a Continual Improvement Policy
- 2. Establish a Continual Improvement Process
- 3. Define SMART Security Objectives
- 4. Implement Feedback Mechanisms
- 5. Execute a Risk-Based Internal Audit Programme
- 6. Provision an Incident Management Process
- 7. Deploy an Incident and Corrective Action Log
- 8. Conduct Systematic Root Cause Analysis (RCA)
- 9. Report to the Management Review Team (MRT)
- 10. Audit Evidence Retention and Verification
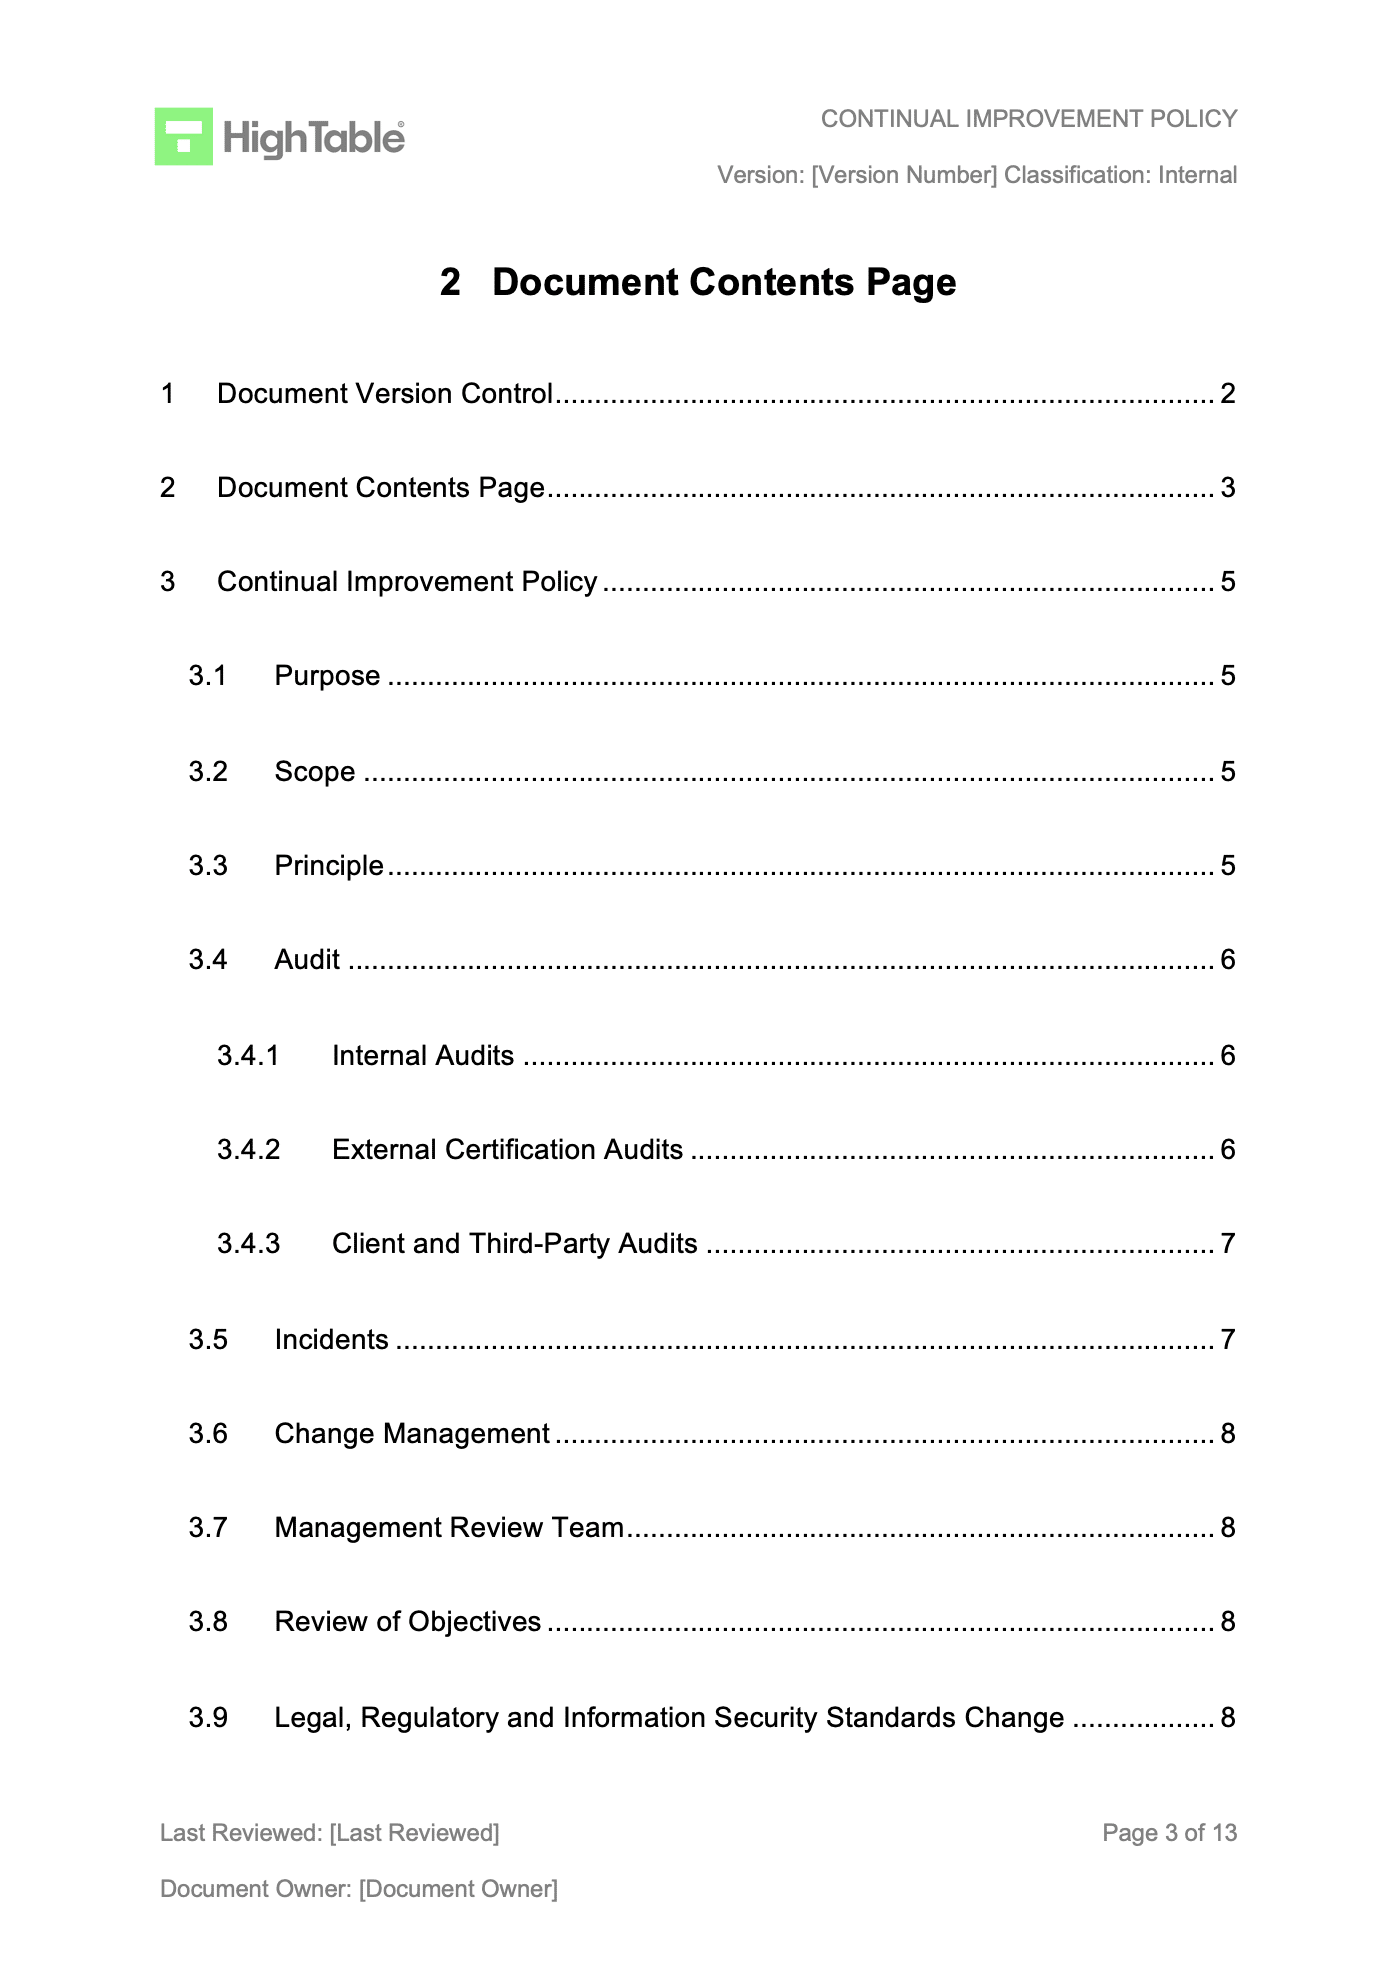
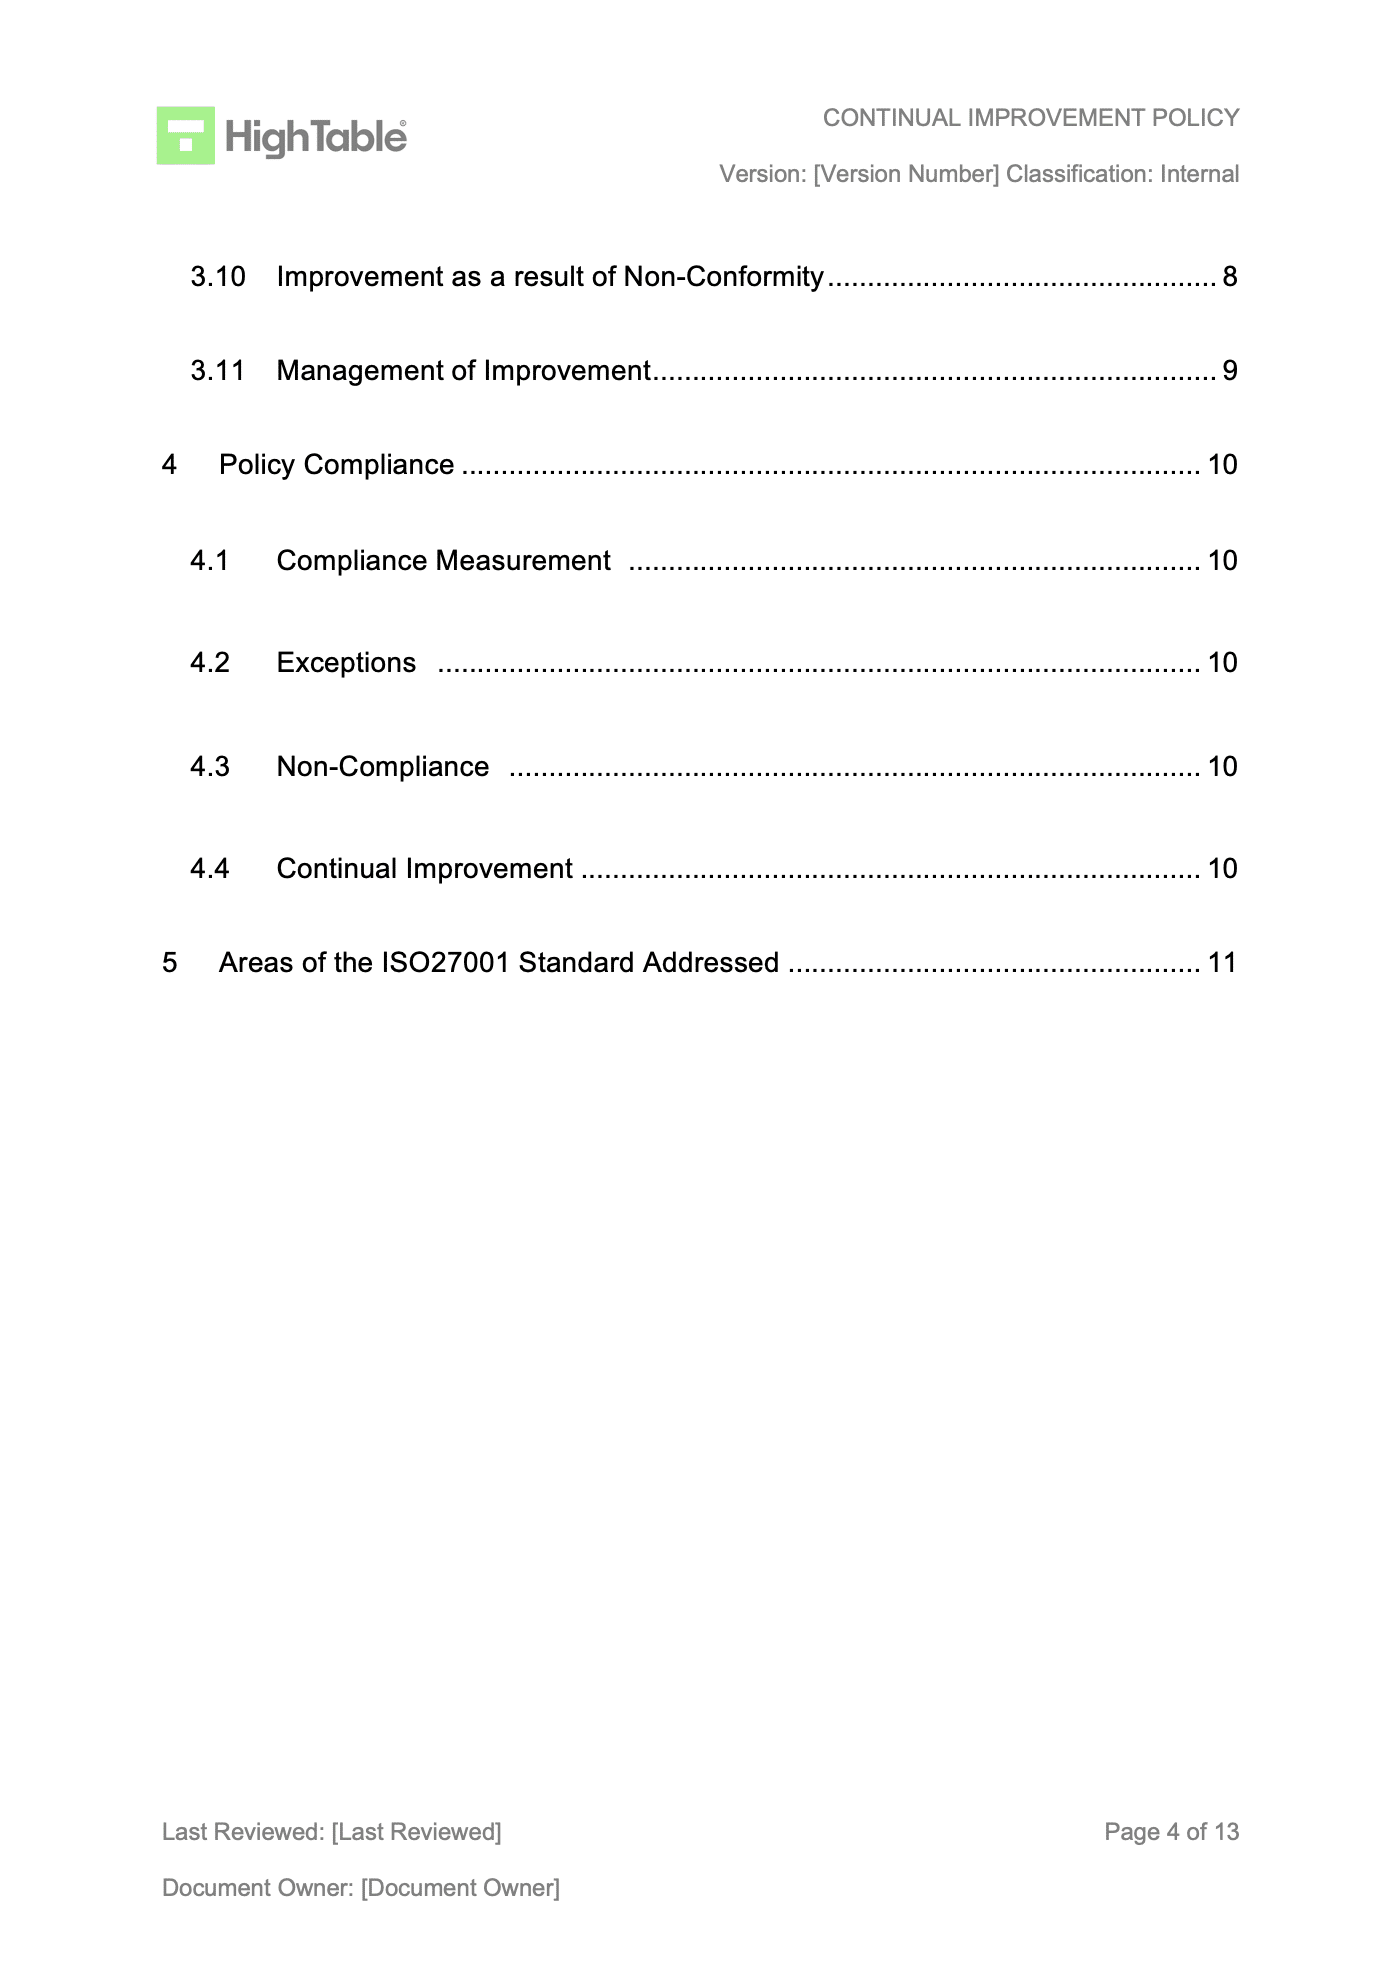
- ISO 27001 Continual Improvement Policy Example
- How to pass the ISO 27001 Clause 10.1 audit
- What the auditor will check
- Common Clause 10.1 Mistakes and How to Avoid Them
- Related ISO 27001 Controls
- ISO 27001 Clause 10.1 FAQ
Key Takeaways
- Security is never finished, it gets better over time
- It is not just fixing things that are broken
- It is proactively finding ways to make your security better, faster, and more robust
- You need it for ISO 27001 Certification
ISO 27001 Clause 10.1 Purpose & Definition
Continual Improvement is the ongoing process of enhancing your information security. It is what prevents your ISMS from becoming a paper tiger that sits on a shelf gathering dust and ensures your management system remains fit for purpose.
The Three Pillars of Improvement
- Suitability: Does the ISMS still fit your organization’s culture, processes, and technologies?
- Adequacy: Does the ISMS meet the actual security needs and risks you currently face?
- Effectiveness: Do the controls actually work to protect confidentiality, integrity, and availability?
The purpose of ISO 27001 Clause 10.1 is to make sure you have an information security management system that is fit for purpose and evolves over time as things change.
The ISO 27001 standard defines ISO 27001 Clause 10.1 simply as:
The organisation shall continually improve the suitability, adequacy and effectiveness of the information security management system.
ISO27001:2022 Clause 10.1 Continual Improvement
ISO 27001 Clause 10.1 Tutorial Video
In this free ISO 27001 Clause 10.1 training video you will learn how to implement it and pass your audit.
Implementation Guide
General
The first step is to implement the policies and process that catch the things that need improvement. These are termed non conformities.
Non conformities are deviation from the norm. A deviation from the written and agreed policies and procedures.
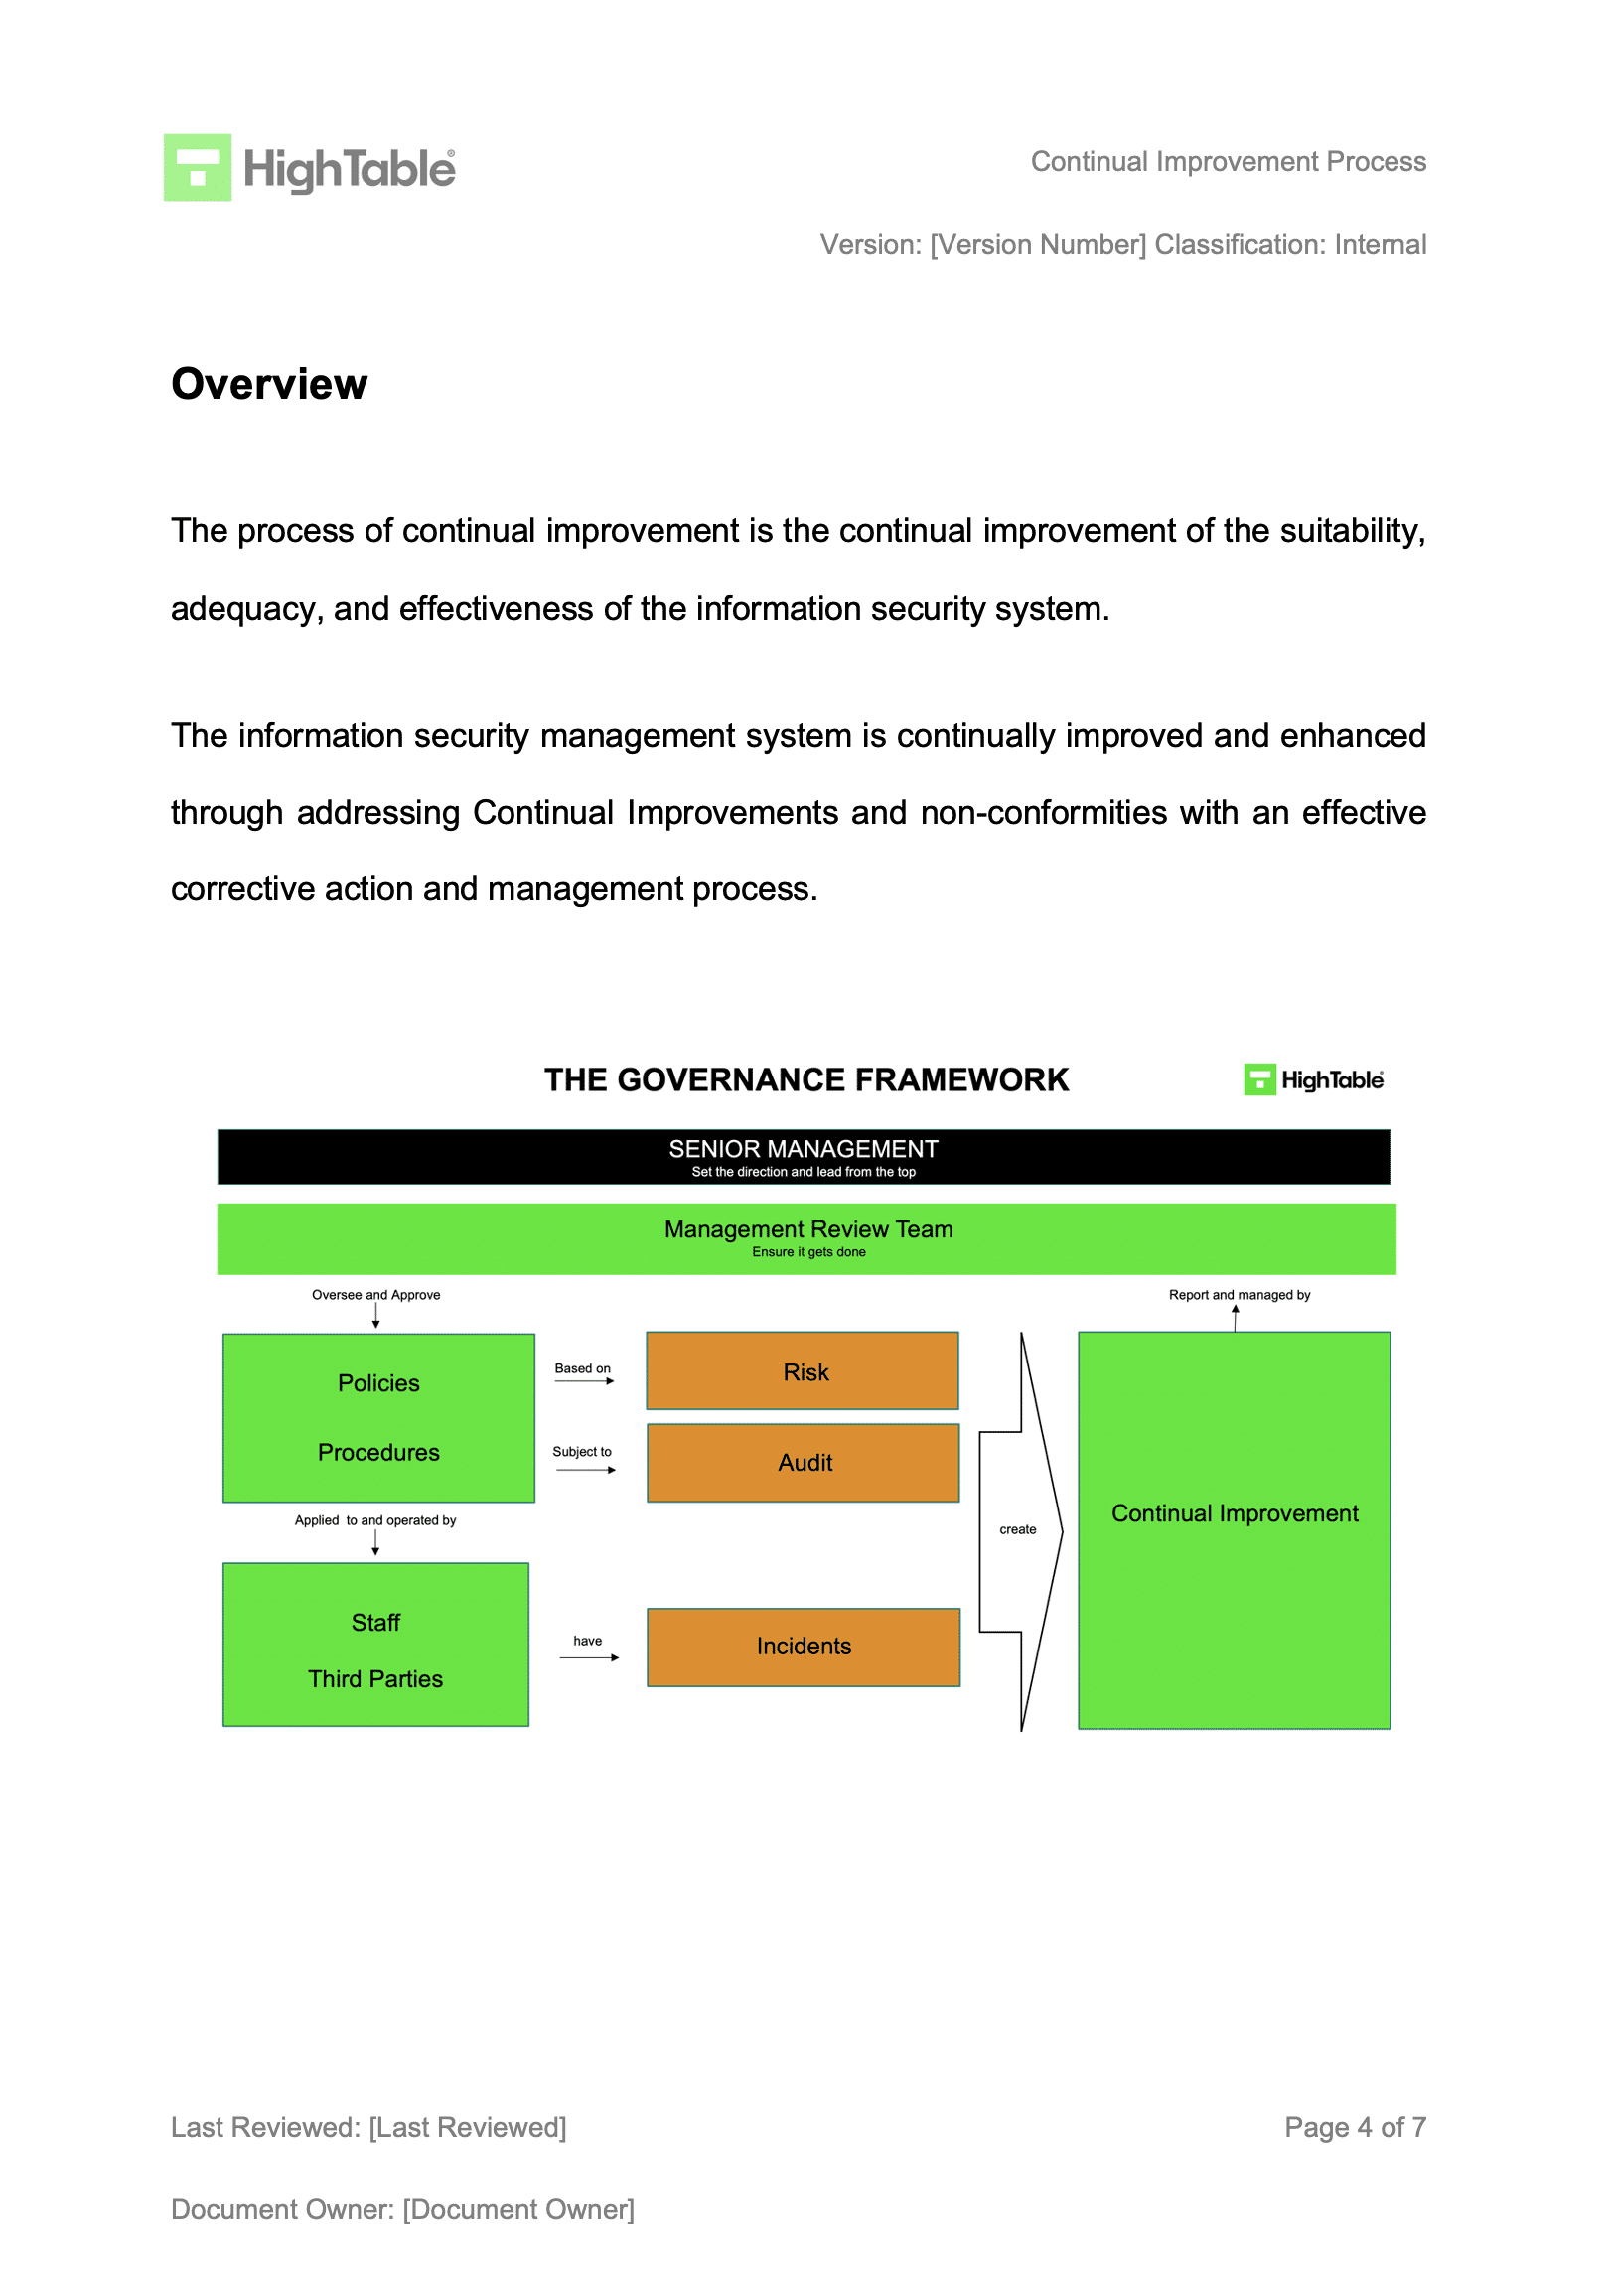
The processes that we have that find things that need improving are:
Incident Management: Incidents occur and are either a one off or symptomatic of a bigger problem. Our process will deal with the incident, then perform a root cause to see why it happened. It may then need an improvement actions such as a change to policy, procedure or a re education or an investment in tooling.
Audit: Audit is the process of independently checking that we do what we say we do. Internal audit is built into the standard. You will also have external client audits and external certification audits. A more formal process for identifying areas that need improving.
Brainstorming: A wide term that refers to just asking people. People are good at coming up with ways that our information security management system can be improved. Ask them.
When we find something that has gone wrong we take appropriate actions to ensure that this does not and cannot occur again. This may include risk management and accepting that it may occur, if the cost of action is too high. That would require us to follow the risk management process and seek to get approval and sign off of the management review team.
We find the use of an incident and corrective action log is ideal for managing this process. The benefits of having an effective log that meets the requirements of the ISO 27001 standard whilst also efficiently handling the process are worth it.
Implement a Continual Improvement Policy
We need an ISO 27001 Continual Improvement Policy. Policies are statements of what we do, not how we do it which is covered in the process documents.
Implement a Continual Improvement Process
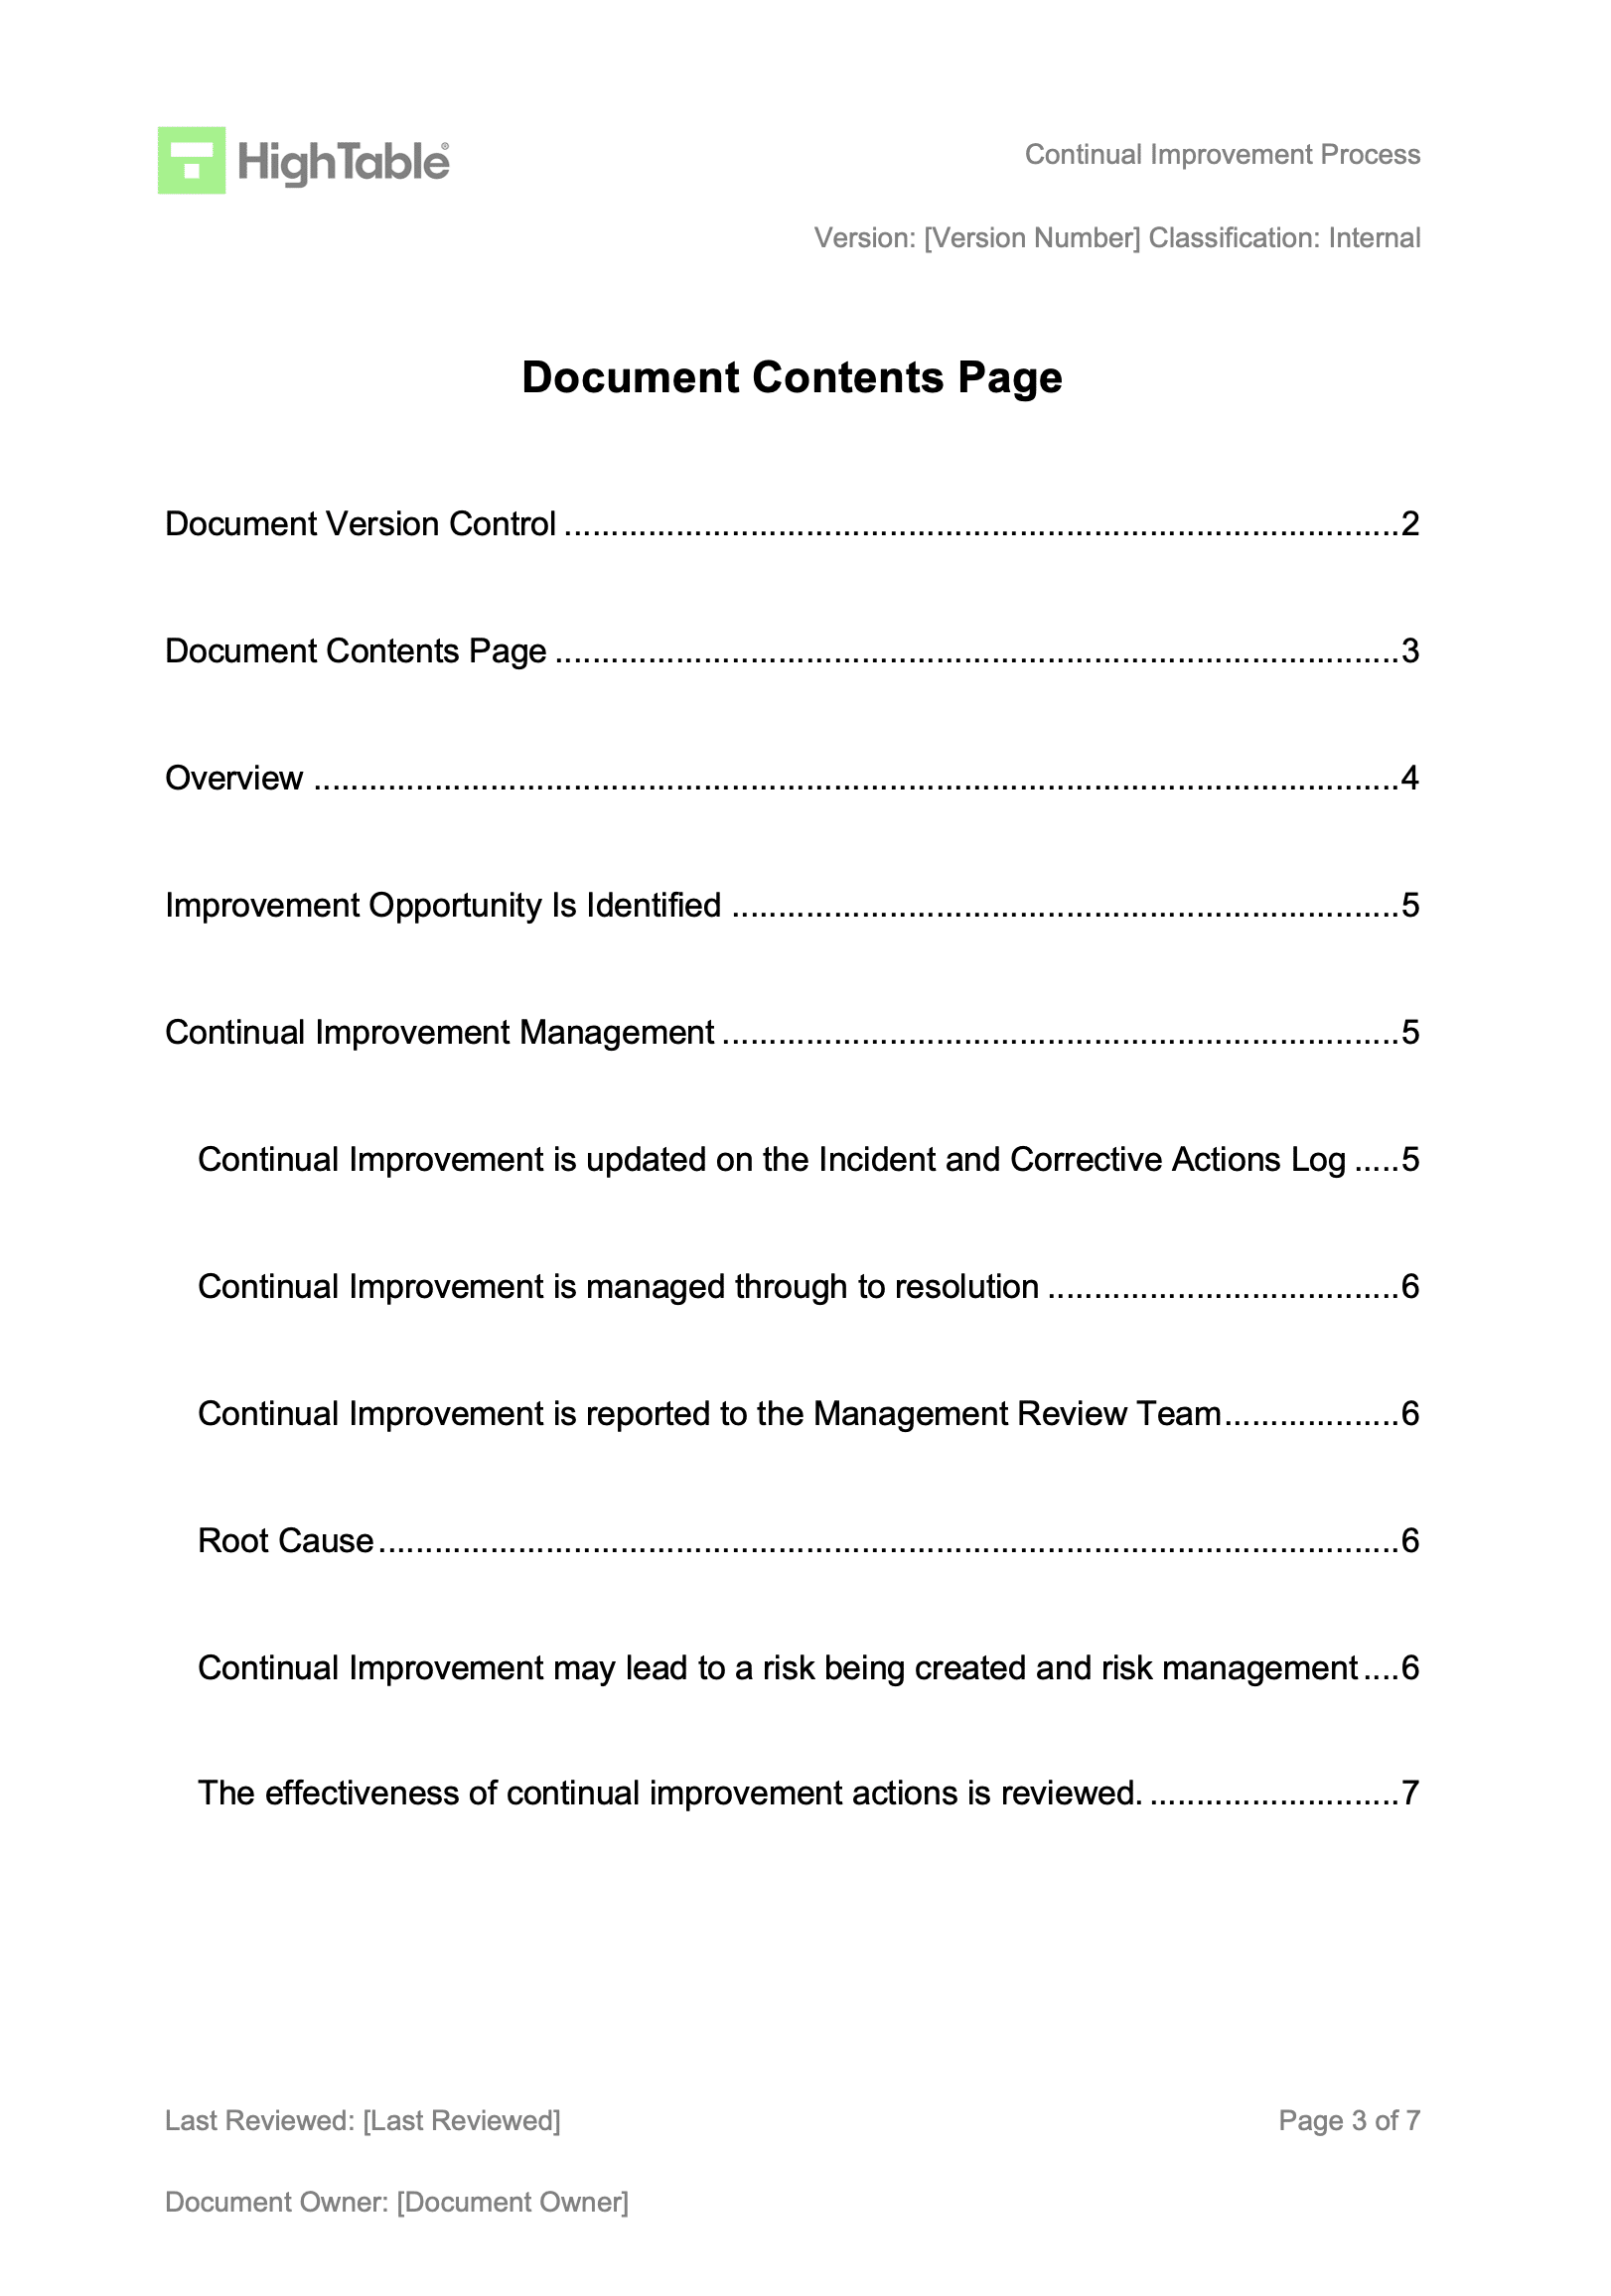
This is the heart of Clause 10.1 and the foundation of meeting the requirements for continual improvement. Included in the ISO 27001 Toolkit but show here for as an example of the process you need.
Implement An Incident And Corrective Action Log
Implement an Internal Audit Process
Internal audit is the primary way we check that our information security management system is effective and the way we identify things that need to be improved. It is a requirement of the standard in ISO 27001 Clause 9.2 Internal Audit.
Implement an Incident Management Process
Incident management is a core part of continual improvement that requires a documented process. It is include in the ISO 27001 Toolkit but for an example the following:
ISO 27001 Clause 10.1 Process Explained
Continual improvement is not a happy accident, it is a managed process. You must have a way to ingest ideas, evaluate them, and implement the ones that add value.
| Step Ref | Process Step | Action Required | Deliverable |
|---|---|---|---|
| 1 | Identify Opportunity | Gather data from metrics (9.1), audit findings (9.2), staff suggestions, or new technology reviews. | Improvement Log Entry |
| 2 | Assess Feasibility | Determine if the improvement is worth the cost. Will it reduce risk? Will it save time? | Cost/Benefit Analysis |
| 3 | Plan Implementation | If approved, treat it like a project. Assign an owner, a budget, and a deadline. | Project Plan / Action Item |
| 4 | Verify Effectiveness | After implementation, check the metrics. Did the change actually improve the ISMS? | Performance Report |
How to implement ISO 27001 Clause 10.1
Based on my experience and what I have seen work well the following are the best practice implementation steps to implement ISO 27001 Continual Improvement.
Built by an Expert ISO 27001 Consultancy
Prefer a DIY approach or have an internal team ready to execute? As a specialized ISO 27001 consultancy, we built this battle-tested ISMS toolkit for teams under 10. Stop building from scratch with generic templates—get the exact audit-ready documentation our ISO 27001 consultants use in the field.

✓ Complete ISMS Policies & Controls
✓ Built for Lean Internal Teams
✓ Guaranteed Certification Audit Success
1. Implement a Continual Improvement Policy
- Action: Define a high-level ISO 27001 Continual Improvement Policy that outlines the organisational commitment to security evolution.
- Result: A clear statement of intent that provides the mandate for all subsequent improvement activities and satisfies auditor requirements for leadership commitment.
- Technical Requirement: Ensure the policy is approved by the Management Review Team and communicated to all staff via the ISMS portal.
2. Establish a Continual Improvement Process
- Action: Document a repeatable ISO 27001 continual improvement process based on the Plan-Do-Check-Act cycle.
- Result: A structured methodology that ensures fundamental changes are made to prevent the recurrence of security nonconformities.
- Requirement: Map the process to ISO 27001 Clause 10.1 to ensure full alignment with the standard.
3. Define SMART Security Objectives
- Action: Set specific, measurable, achievable, relevant, and time-based (SMART) objectives for your ISMS performance.
- Result: Data-driven benchmarks that allow the organisation to objectively measure the success of improvement initiatives.
- Technical Requirement: Link objectives to key performance indicators (KPIs) within your security dashboard or SIEM.
4. Implement Feedback Mechanisms
- Action: Establish formal channels for employees, customers, and stakeholders to report security concerns or suggest process enhancements.
- Result: Identification of “on-the-ground” security risks and operational inefficiencies that automated tools might miss.
- Requirement: Provision an anonymous reporting tool or a dedicated security suggestions mailbox.
5. Execute a Risk-Based Internal Audit Programme
- Action: Deploy an ISO 27001 Clause 9.2 Internal Audit plan that evaluates the entire ISMS at least annually.
- Result: Independent verification of control effectiveness and the identification of gaps before they are found by external auditors.
- Technical Requirement: Include technical vulnerability scans and IAM role reviews as part of the audit evidence collection.
6. Provision an Incident Management Process
- Action: Implement a robust ISO 27001 Annex A 5.26 Incident Management Process.
- Result: Rapid containment of security breaches and the generation of vital data used to drive systemic improvements.
- Requirement: Define clear escalation paths and ROE (Rules of Engagement) for the Incident Response Team.
7. Deploy an Incident and Corrective Action Log
- Action: Utilise a centralised incident and corrective action log to track every identified nonconformity from discovery to closure.
- Result: A comprehensive audit trail that demonstrates to certification bodies that your organisation actively manages and resolves security failures.
- Technical Requirement: Ensure the log captures root cause analysis, ownership, and target remediation dates.
8. Conduct Systematic Root Cause Analysis (RCA)
- Action: Apply formal RCA techniques, such as the 5 Whys, to every significant incident or audit finding.
- Result: Elimination of the underlying cause of a failure rather than just treating the symptom, preventing future recurrence.
- Requirement: Document the RCA findings directly within the Corrective Action Log for auditor review.
9. Report to the Management Review Team (MRT)
- Action: Present improvement data, audit results, and incident trends to the MRT during ISO 27001 Clause 9.3 Management Reviews.
- Result: High-level oversight and resource allocation for major improvement projects, ensuring security remains aligned with business goals.
- Requirement: Formally minute all decisions, including any changes to the ISMS scope or resource requirements.
10. Audit Evidence Retention and Verification
- Action: Verify the effectiveness of every implemented improvement and archive the supporting evidence.
- Result: Definitive proof of a functioning “continual improvement” culture, which is essential for maintaining ISO 27001 certification.
- Technical Requirement: Retain logs of updated asset registers, revised MFA configurations, and updated training records.
ISO 27001 Continual Improvement Policy Example
An example of a continual improvement policy for ISO 27001 Clause 10.1
How to pass the ISO 27001 Clause 10.1 audit
You demonstrate compliance to ISO 27001 Clause 10.1 Continual Improvement by having effective policy and process in place and having documented evidence that those processes have operated effectively. What this means is that you need policy and process for the identifiers of nonconformities, being:
- Incident management
- Audit (both internal audit and external audit)
And you need policy and process to deal with the nonconformities being
To demonstrate evidence you will have a series of documents and records
- Incident tickets on your associated help desk systems
- Change tickets that support any changes that have been made
- The complete incident and corrective action log that is used to manage nonconformities
- Meeting minutes from the Management Review Team meetings where all of he above have been shared and minuted
What the auditor will check
The auditor is going to check a number of areas for compliance with Clause 10.1. Lets go through them
1. That you have a corrective action process
When a non conformity is identified you need to be able to manage it. The auditor will look at the process and a sample of recent corrective actions to ensure they followed the process and they were managed effectively. Were they recorded? Were they added to the corrective action log? Were they managed? Were they reported to the management review team? Were any corrective actions checked to ensure they were effective?
2. That you have a corrective action log
You need an effective way to record corrective actions and continual improvements. A corrective action log is a simple way to do it but how ever you do it ensure that you have evidence of continual improvement in operation.
The High Table ISO 27001 Internal Audit.
ISO 27001 strictly requires impartiality – you cannot audit your own work. If you implemented the ISMS, you must use an independent expert before the certification body arrives. Book your ISO 27001 Internal Audit with High Table and let Lead Auditor Stuart Barker’s team guarantee your certification readiness.
✓ 100% Independent & Impartial
✓ Conducted by Certified Lead Auditors
✓ Fixed-Price, Zero-Friction Process

Common Clause 10.1 Mistakes and How to Avoid Them
In my experience, the top 3 mistakes people make for ISO 27001 Continual Improvement are:
| The Mistake | Why it Fails the Audit | The Auditor’s Solution |
|---|---|---|
| 1. No Evidence of Improvement | Claiming you improved but having no log or minutes to prove it. | If it isn’t written down, it didn’t happen. Ensure every improvement is minuted in Management Reviews. |
| 2. No Defined Process | Relying on ad-hoc “good ideas” rather than a structured approach. | Document a simple Continual Improvement Process that defines inputs, outputs, and approval steps. |
| 3. Process vs. Reality Gap | Having a policy that says you review improvements monthly, but actually doing it annually. | “Say what you do, do what you say.” Align your documentation with your actual working practices. |
Related ISO 27001 Controls
To ensure your Information Security Management System (ISMS) is not just a collection of static documents but a living, breathing framework, you must understand how Clause 10.1 interacts with the rest of the ISO 27001 standard.
- ISO 27001 Clause 9.2 Internal Audit
- ISO 27001 Annex A 5.26 Response To Information Security Incidents
- ISO 27001 Annex A 5.36 Compliance With Policies, Rules And Standards For Information Security
- ISO 27001 Clause 6.1.1 Planning General
ISO 27001 Clause 10.1 FAQ
The ISO 27001 standard requires that the organisation shall manage when things go wrong, manage the consequences of things going wrong, identify why it went wrong and put in place measures to stop it from happening again.
You evidence compliance to the ISO 27001 Clause 10.1 Continual Improvement with an incident and corrective action log and being able to demonstrate that you identify when things go wrong, put things right, identify why it went wrong and put in place measures so it does not happen again.
Yes. Senior management and leadership are informed of non conformities. This is usually via the management review team meeting.
Yes. Non conformities require a root cause analysis to identify why they happened and to help to identify what can be done to prevent it from happening again.
You can classify non conformities to help you to prioritise the order in which to tackle them and the recommended actions you should take. This would be aligned with the risk management process.
Technically yes but by doing nothing you are accepting risk and therefore you would follow your risk management process with sign off and acceptance by the management review team.
Non conformities are reported via the incident management process.
Yes you can pass the ISO 27001 certification if you have non conformities as long as they are being effectively managed and reported.
Stuart Barker
Lead ISO 27001 Consultant
Stuart Barker is a qualified ISO 27001 Lead Auditor, ISO 27001 Lead Implementer and veteran practitioner with over 30 years of experience in systems security and risk management. Holding an MSc in Software and Systems Security, he combines academic rigour with extensive operational experience, including a decade leading Data Governance for General Electric (GE).
He is the founder of High Table (operating as HT Black Consulting) and the Lead Consultant driving the specialist ISO 27001 Consultancy, delivering expert advisory, internal audits, and battle-tested ISMS frameworks for technology companies, small business and startups.