
ISO 27001 Backup Policy
In this guide, you will learn what an ISO 27001 Backup Policy is, how to write it yourself and I give you a template you can download and use right away.
Table of contents
- ISO 27001 Backup Policy
- What is an ISO 27001 Backup Policy?
- ISO 27001 Backup Policy Example
- ISO 27001 Backup Policy Template
- How to write an ISO 27001 Backup Policy
- Evertything you need to know
- How the ISO 27001 toolkit can help
- Applicability of an ISO 27001 Backup Policy to Small Businesses, Tech Startups, and AI Companies
- Information security standards that need an ISO 27001 Backup Policy
- List of relevant ISO 27001:2022 controls
- ISO 27001 Backup Policy FAQ
What is an ISO 27001 Backup Policy?
This policy is a set of rules that tells you and your team exactly how to back up your data. It covers what data to back up, how often to do it, where to store the copies, and who is in charge of the process. Its main purpose is to protect your information from things like hardware failure, natural disasters, or even a simple mistake.

ISO 27001 Starter Kit
Instant download of mandatory ISMS core policies and documentation. Verified by Lead Auditors and used by 5,000+ businesses worldwide to pass Stage 1 certification first time.
ISO 27001 Backup Policy Example
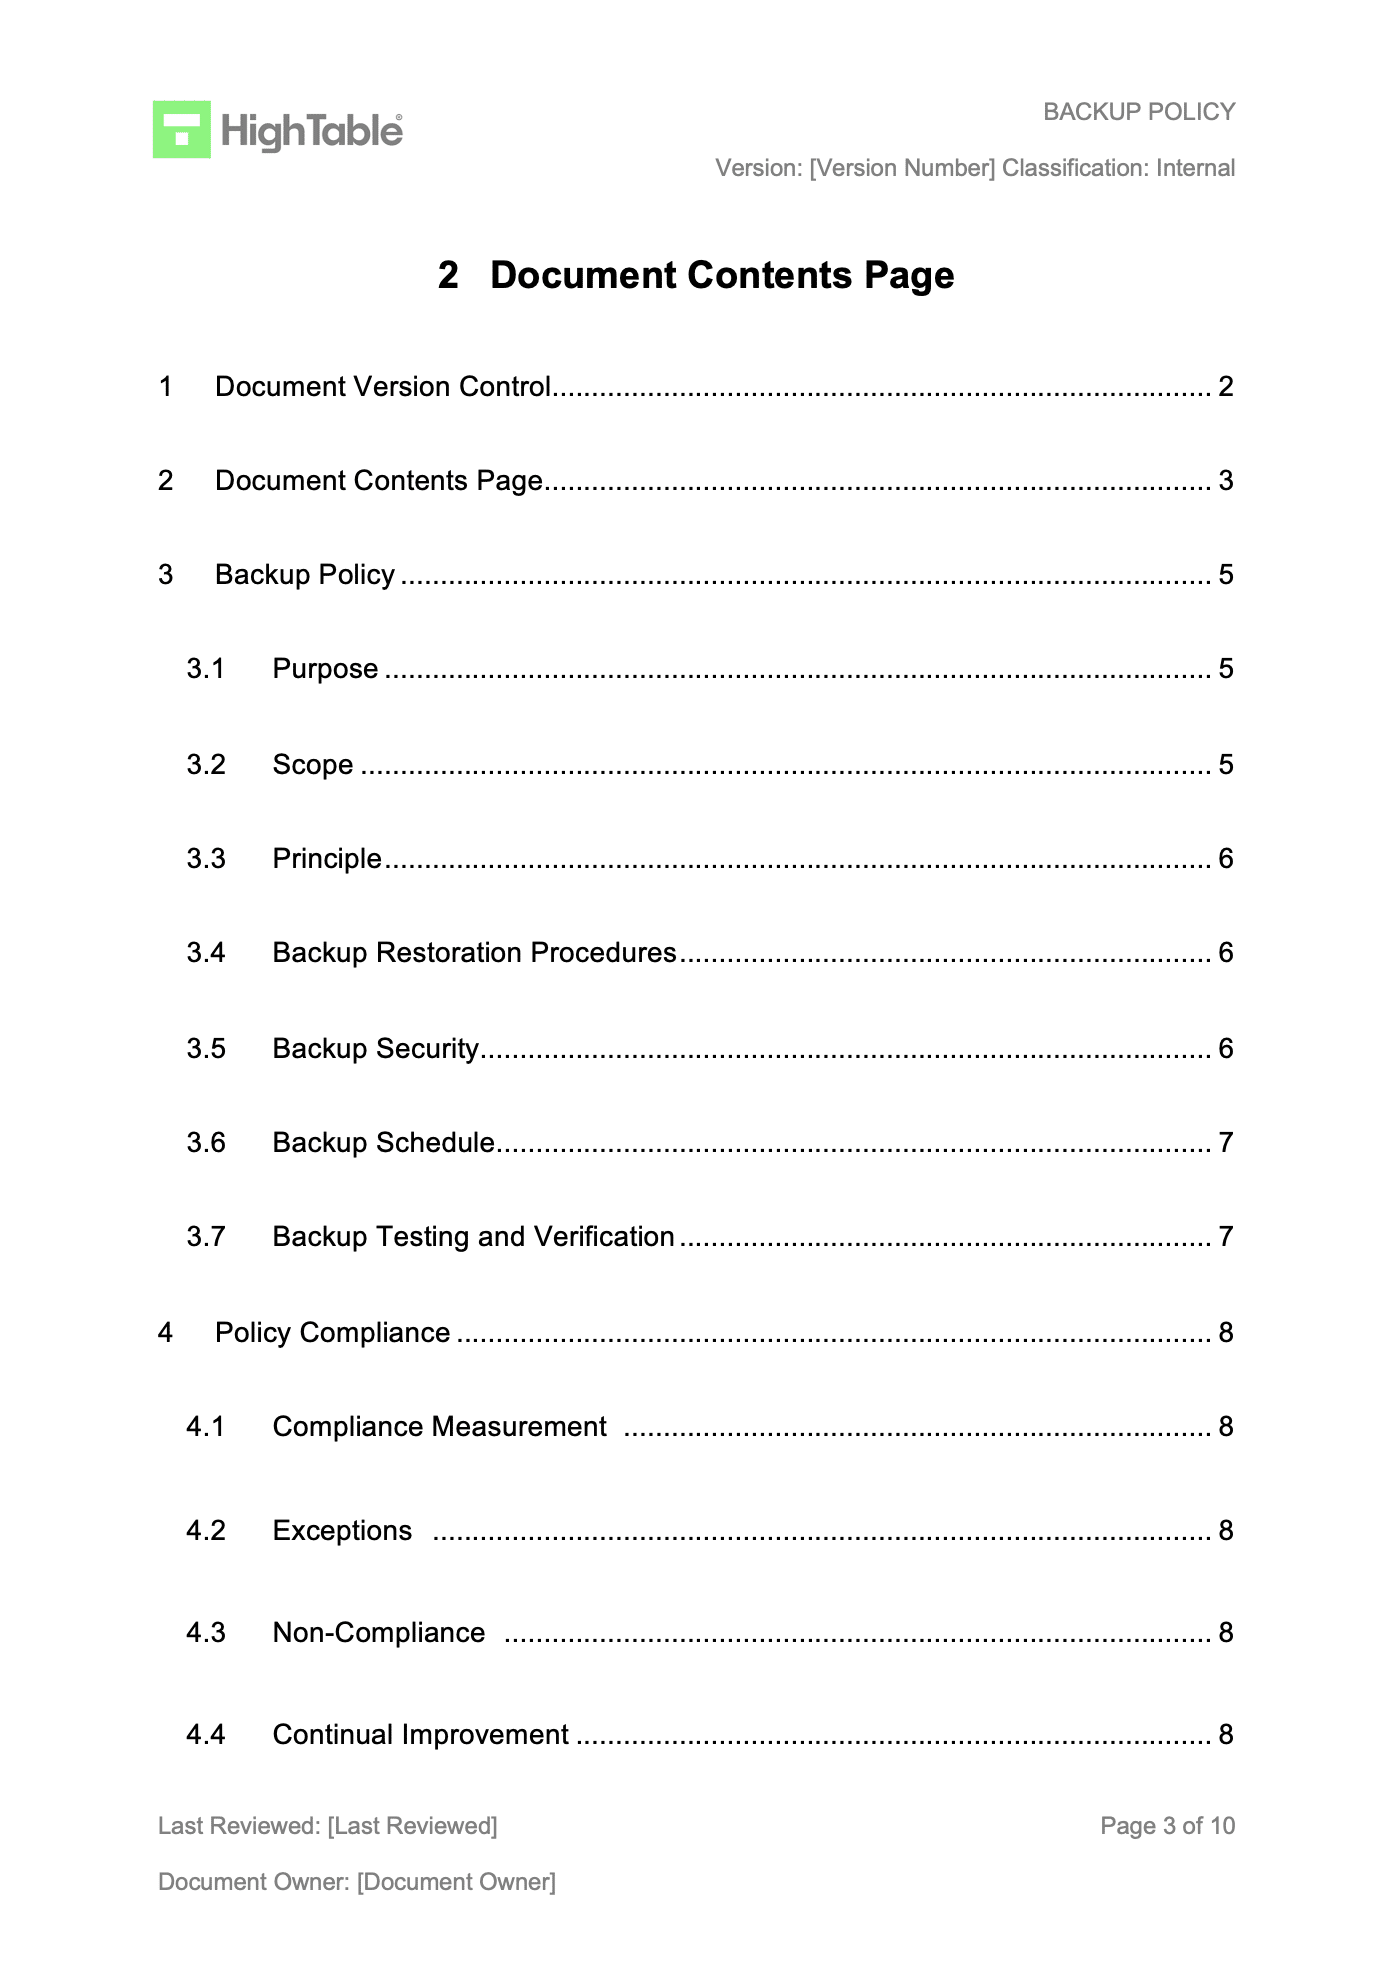
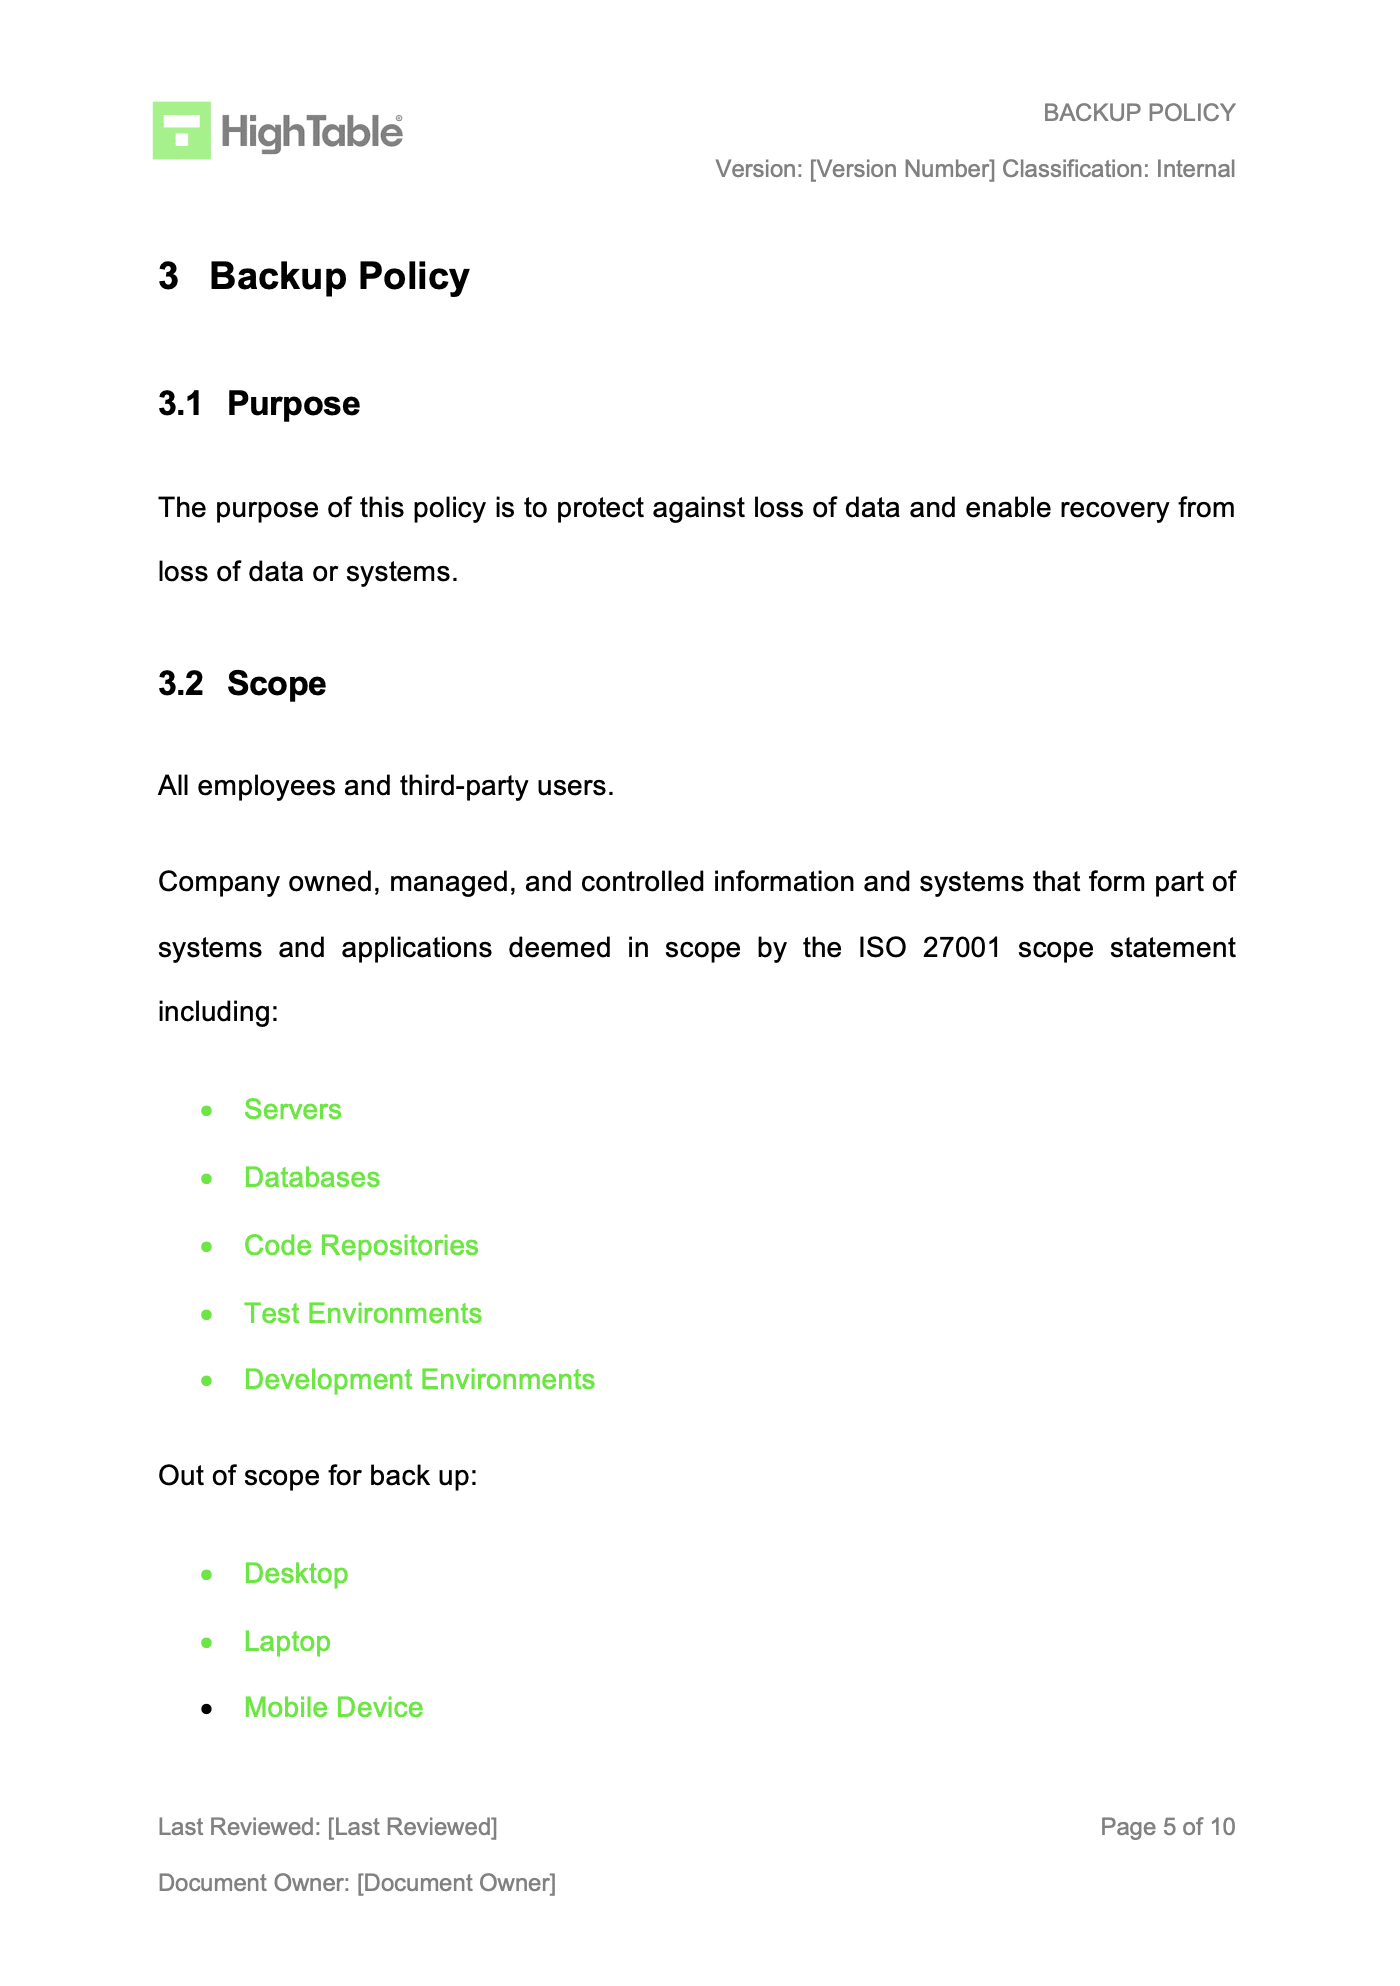
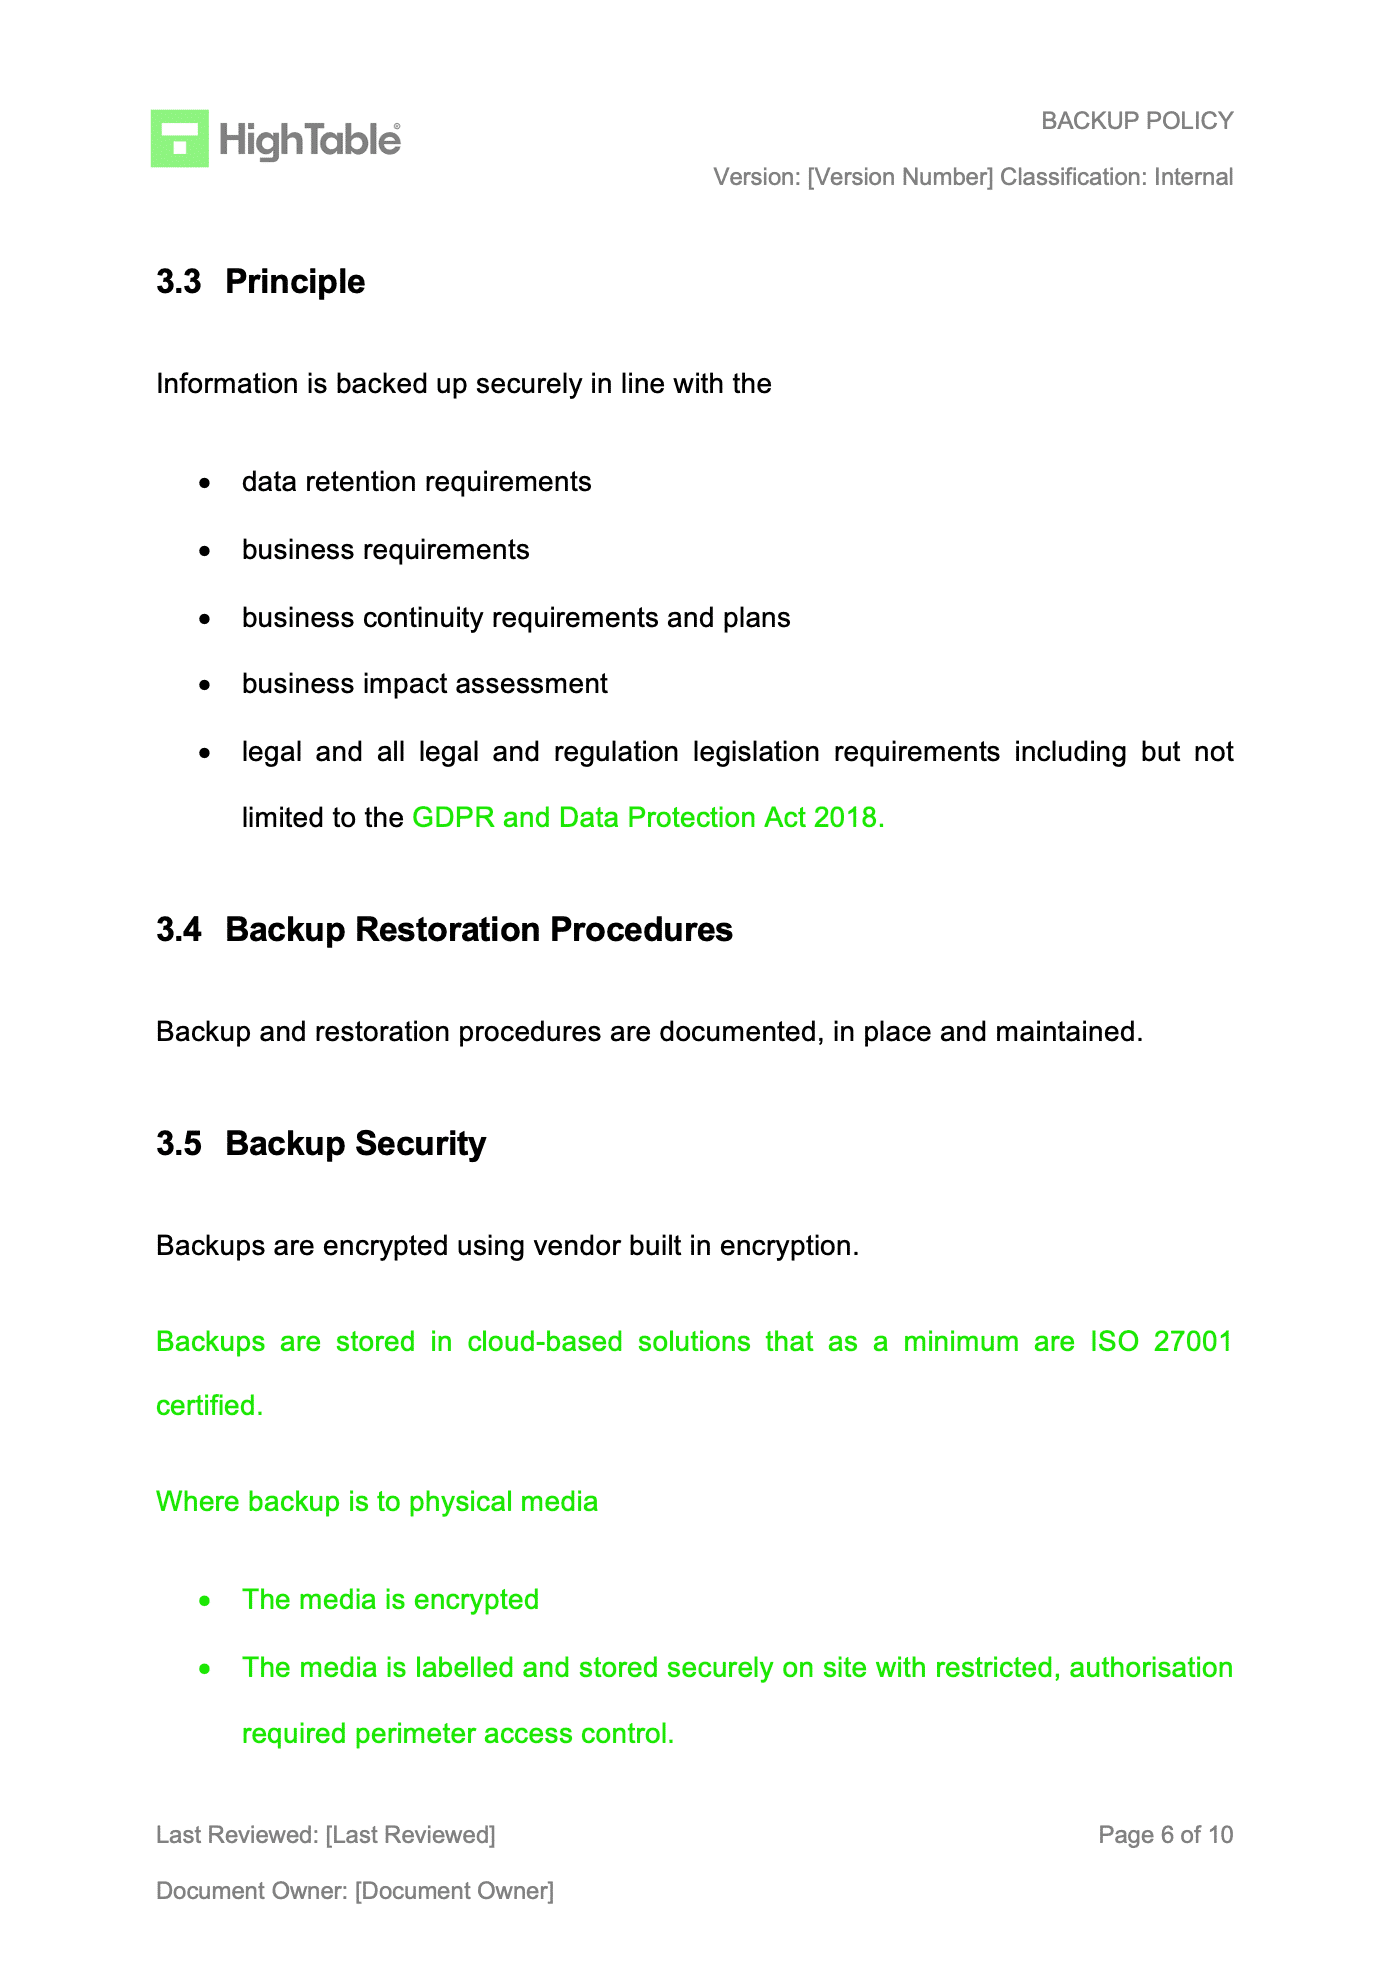
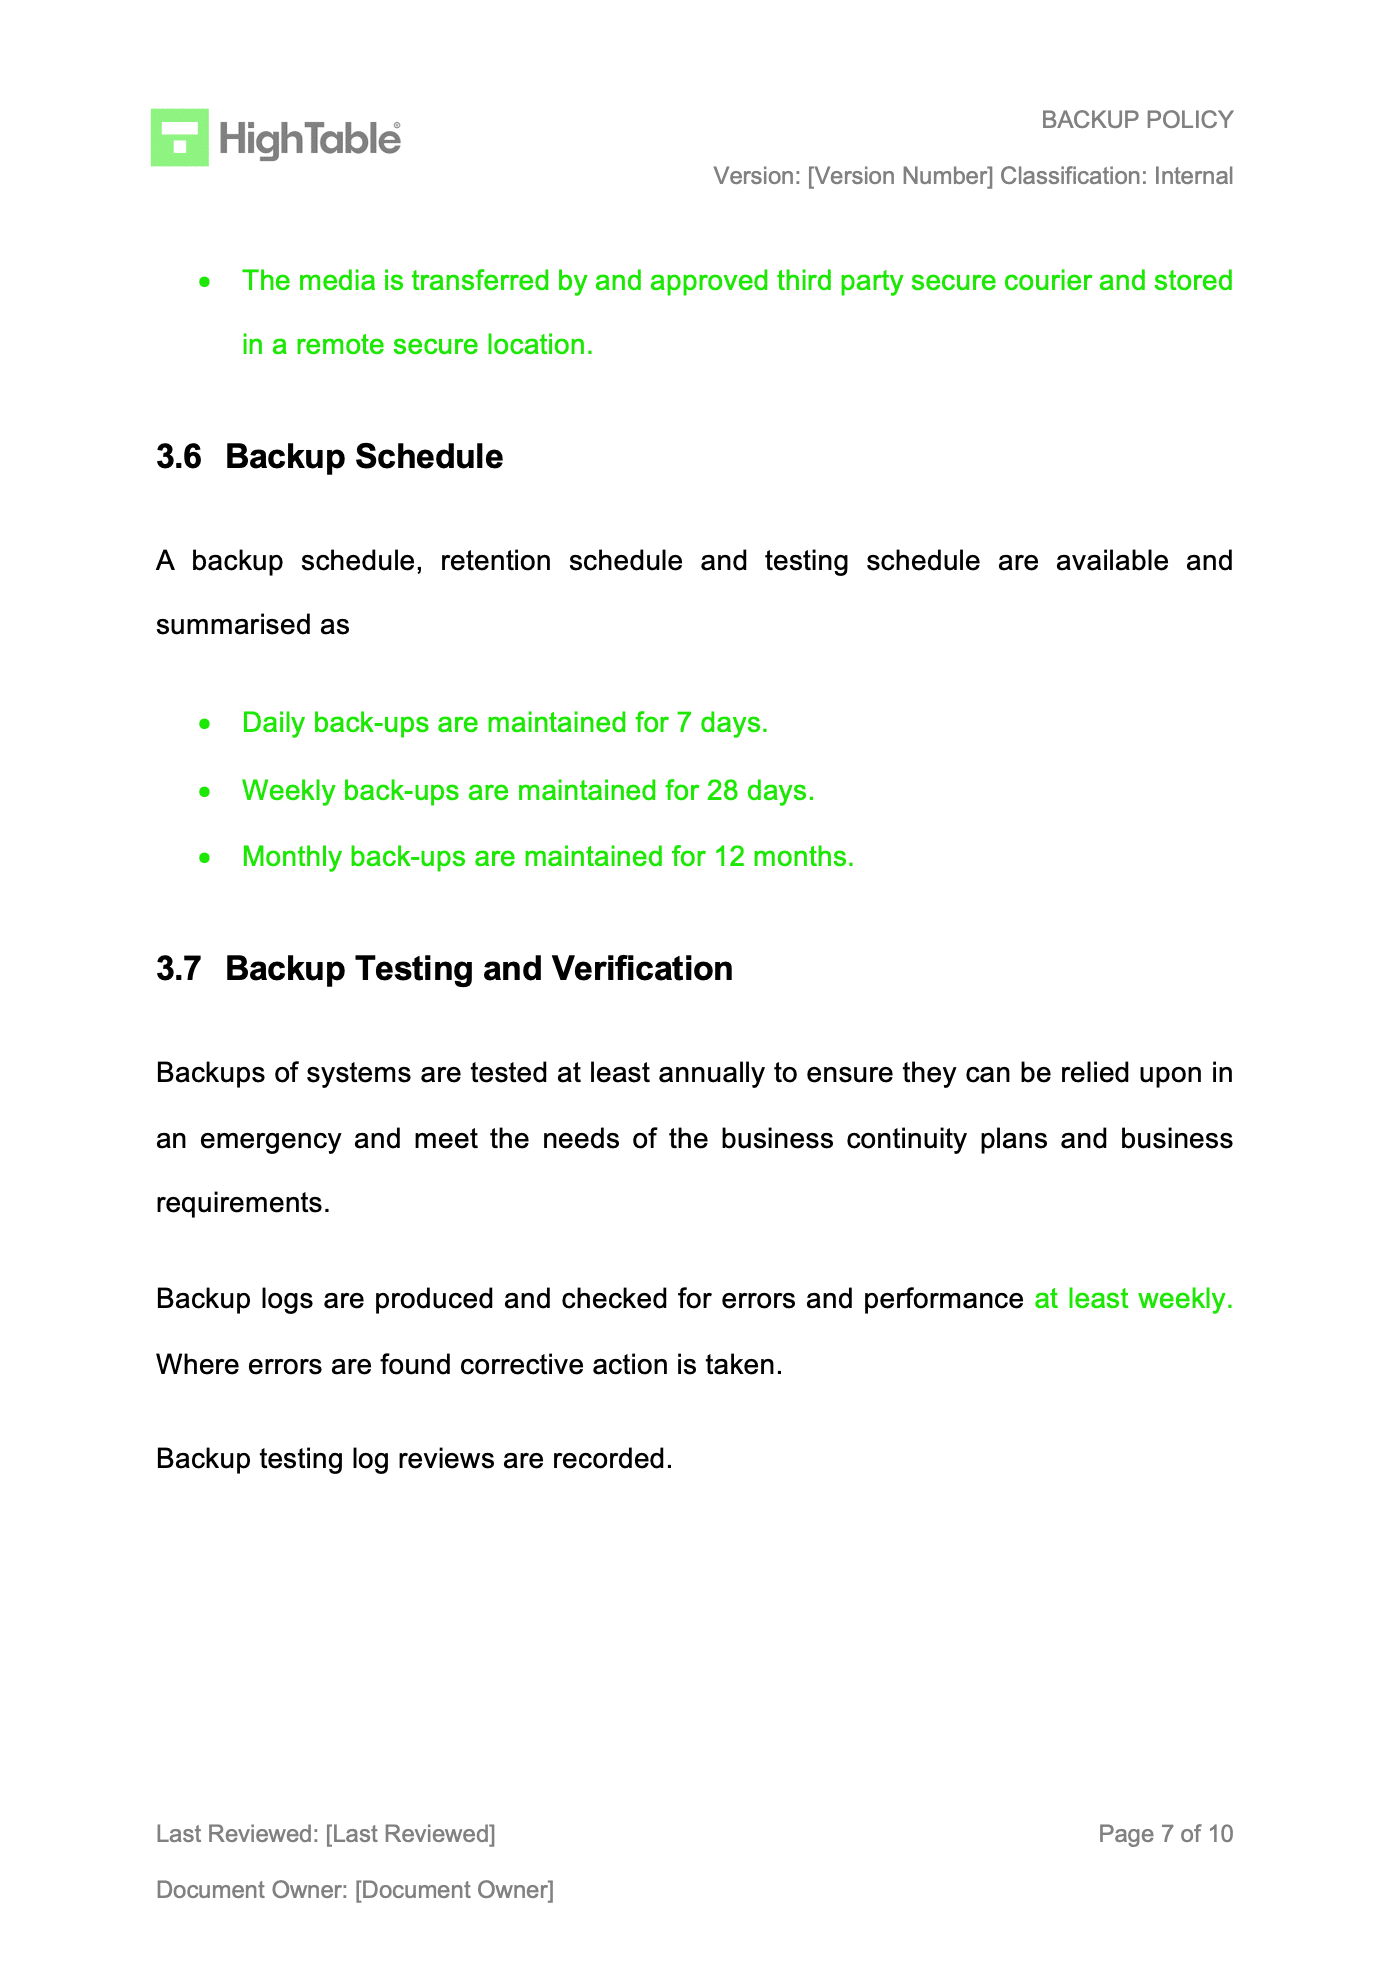
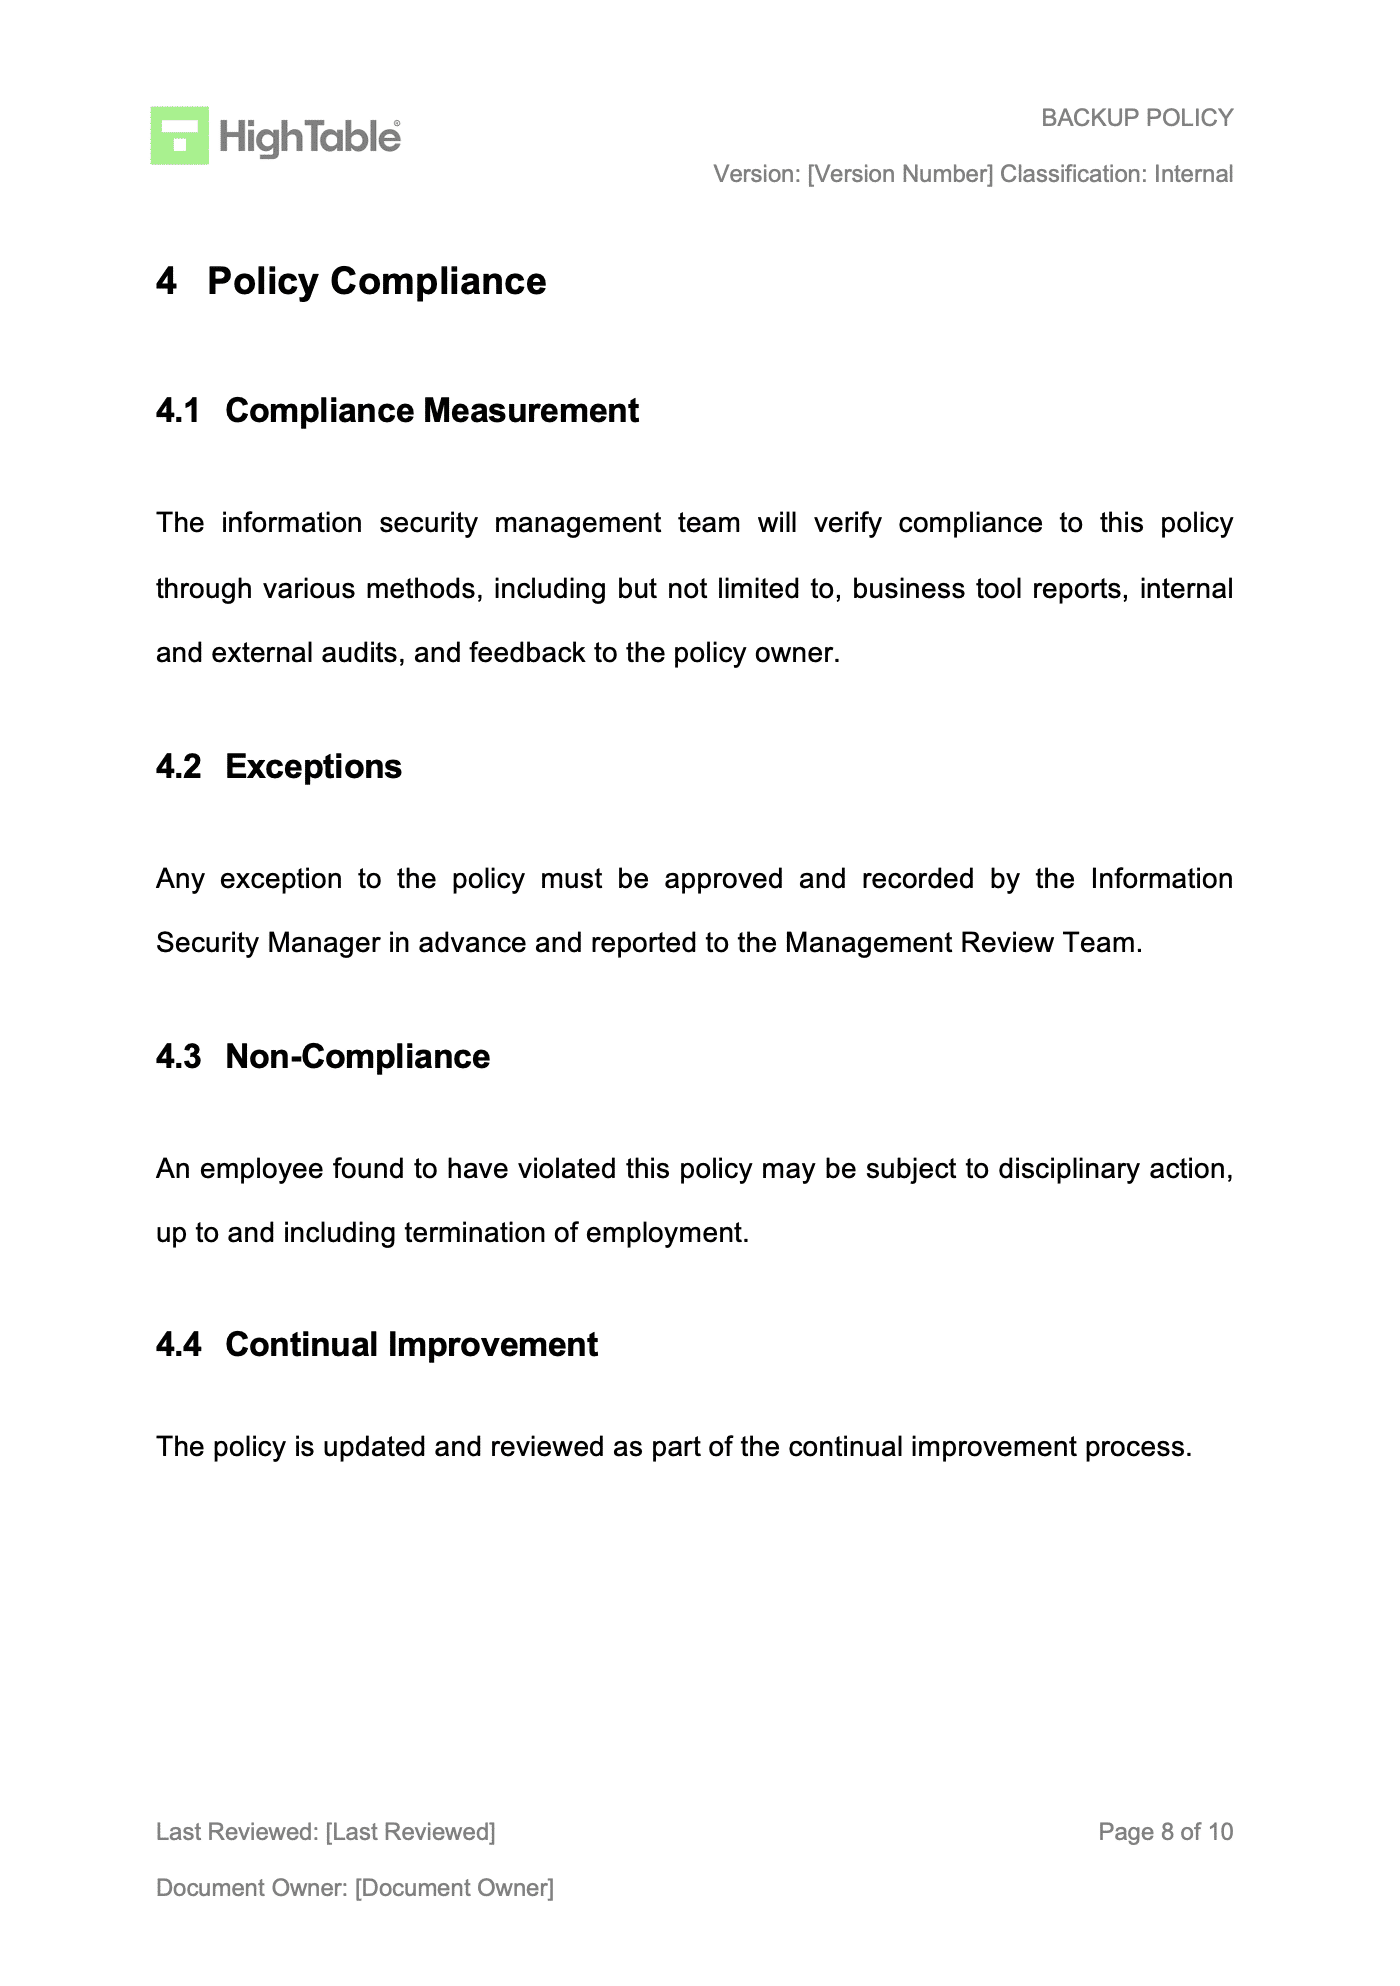
An example of a real world ISO 27001 Backup policy:
ISO 27001 Backup Policy Template
Taking years of experience I created the ISO 27001 Backup Policy Template as a real world practical template that takes the requirements of the standard and industry best practice. It is included in the ISO 27001 toolkit but you can download it standalone here.

How to write an ISO 27001 Backup Policy
Writing a good backup policy should be simple. Start by listing the types of data that need to be backed up. Then, specify how often you’ll back it up (daily, weekly, etc.) and where the backups will be stored (e.g., in a secure cloud service). Finally, explain how you’ll test your backups to make sure they work. Use simple language so everyone can understand it.
Time needed: 4 hours
How to write a backup policy
- Create your version control and document mark-up
- Document the purpose of the ISO 27001 Backup Policy
- Set out the principle on which the ISO 27001 Backup Policy is based
- Define the ISO 27001 Backup Policy Scope
- Set out the approach to backup restoration procedures
- Explain the backup security controls
- Set out the backup schedule
- Explain the approach to backup testing and verification
Evertything you need to know
Why you need an ISO 27001 Backup Policy
You need this policy to keep your business running smoothly no matter what. Without a good backup plan, losing data could be a disaster for your business. This policy helps you avoid costly downtime, protects your reputation with customers, and makes sure you can recover from a problem quickly and easily.
When you need an ISO 27001 Backup Policy
You need this policy from the very start of your business. It’s not something you can just set and forget. You’ll use it regularly, for example, whenever you need to schedule a new backup or when you’re testing your ability to restore data. It’s a continuous process to keep your information safe.
Who needs an ISO 27001 Backup Policy?
Everyone in your company who handles data should know about this policy, but your IT team or a designated person will be responsible for carrying it out. This includes people who manage servers, databases, and even your employees who save files on their computers.
Where you need an ISO 27001 Backup Policy
This policy applies to all the places where you store your data. This includes your company’s servers, cloud storage accounts, and even individual laptops or tablets that have important information on them. It’s a rulebook that covers all your data, wherever it lives.
How to implement an ISO 27001 Backup Policy
To put the policy into action, you’ll first choose your backup software or service. Then, you’ll set up a schedule for your backups. You’ll also need to train your team on their roles and do regular practice runs to make sure you can restore your data if you ever need to. This is a crucial step!
How the ISO 27001 toolkit can help
An ISO 27001 toolkit is a great shortcut. It includes all of the business continuity and back up documents that you need.
ISO 27001 Toolkit
All the templates, tools, support and knowledge you need to do it yourself.
Applicability of an ISO 27001 Backup Policy to Small Businesses, Tech Startups, and AI Companies
This policy is a must-have for any size company. Here’s how it applies:
- Small Businesses: It ensures that client lists, financial records, and other critical business data are safe.
- Tech Startups: It protects your code, product data, and customer information from being lost.
- AI Companies: It’s essential for backing up your valuable training data sets and AI models.
Examples of using it for small businesses
A small retail shop’s policy might state that all sales records are backed up to the cloud every night, and these backups are tested once a month to ensure they can be restored.
Examples of using it for tech startups
A startup building a mobile app might have a policy that all source code is backed up to a secure online repository every hour and that a full copy of the database is made daily.
Examples of using it for AI companies
An AI company’s policy might require that their massive data sets and machine learning models are backed up weekly to a separate, offline storage location to protect them from cyberattacks.
Information security standards that need an ISO 27001 Backup Policy
This policy is a key part of ISO 27001, which is an international standard for managing information security. Other standards that need it include:
- GDPR (General Data Protection Regulation)
- CCPA (California Consumer Privacy Act)
- DORA (Digital Operational Resilience Act)
- NIS2 (Network and Information Security (NIS) Directive)
- SOC 2 (Service Organisation Control 2)
- NIST (National Institute of Standards and Technology)
- HIPAA (Health Insurance Portability and Accountability Act)
List of relevant ISO 27001:2022 controls
The ISO 27001:2022 standard has a specific control for this topic:
- ISO 27001 Annex A 8.13 Information Backup: This control is all about having a formal process for backing up your information. It ensures that you’ve identified what needs to be backed up, that you’re doing it regularly, and that you have a plan to recover the data.
ISO 27001 Backup Policy FAQ
To protect your data from being lost.
Yes, if your laptop has important company data on it.
It depends on how often your data changes, but at least daily for most businesses.
A backup is a copy made specifically for recovery, and it’s part of a bigger plan.
No, you should store them in a different, secure location.
You could lose important data and face business downtime.
No, it’s a living document that you should continually use and update.
You should test them regularly, like once a quarter.
It’s how much data you can afford to lose.
It’s how quickly you need to get your data back.
No, one policy can cover all your systems.
It provides clear evidence that you are protecting your data, which is crucial for audits.
Yes, a backup process is a required control.
Identify all the data you need to back up.
About the author
