In this guide you will learn how to implement ISO 27001 Annex A 8.24 Use of Cryptography and pass your audit from ISO 27001 Lead Auditor Stuart Barker – author of the ultimate ISO 27001 Toolkit.
ISO 27001 Annex A 8.24 Use of Cryptography is an ISO 27001 control that requires us to define and manage the rules associated with cryptography, which in laymen’s terms is encryption.
Table of contents
Key Takeaways
- ISO 27001 Annex A 8.24 does not require you to be a mathematician or write your own encryption algorithms.
- Instead, it requires you to define rules for how and when you use encryption to protect the confidentiality, integrity, and authenticity of your information.
- It ensures that you are using the right keys, keeping them safe, and following the law.
Purpose & Definition
ISO 27001 Annex A 8.24 is a preventive control to ensure proper and effective use of cryptography to protect the confidentiality, authenticity or integrity of information according to business and information security requirements, and taking into consideration legal, statutory, regulatory and contractual requirements related to cryptography.
The ISO 27001 standard defines ISO 27001 Annex A 8.24 as:
Rules for the effective use of cryptography, including cryptographic key management, should be defined and implemented.
ISO27001:2022 Annex A 8.24 Use of Cryptography

ISO 27001 Starter Kit
Instant download of mandatory ISMS core policies and documentation. Verified by Lead Auditors and used by 5,000+ businesses worldwide to pass Stage 1 certification first time.
ISO 27001 Annex A 8.24 Requirements and Guidance
The implementation of cryptography can be as simple or as difficult as you want to make it. Let us take a look at some of the considerations and guidance.
Technical Implementation
You will implement the technology required to realise what you have set out in your topic specific policies. The best approach is the use of industry standard technologies and usually that means the built in product features of technology that you already have.
As part of the technical implementation you will implement endpoint encryption and this is, where feasible, for all endpoints including mobile devices.
The Law
The main overriding factor of any implementation of this controls is the law. The laws around encryption and cryptography vary around the world and even within countries so it is paramount that what ever you are going to do, you get checked and signed of by a legal professional and keep evidence of the advice that you received.
Standards
When using encryption it is likely that you will use default and off the shelf technology but you should consider and record that standards that you are following and include in that information on cipher strength, algorithms used.
Key Management
This is an important step as the keys are the things that can cause you a lot of problems if they are compromised or even if you forget what they are. The implementation of a robust key management process is therefore, pardon the pun, key.
There are many steps to consider in the management of keys so let us list out the common ones that you will need to address.
- Generating keys
- Issuing keys
- Obtaining Public Keys
- Distributing keys
- Storing keys
- Changing keys
- Updating keys
- Dealing with key compromise
- Dealing with key loss
- Revoking keys
- Recovering keys
- Backing up keys
- Destroying keys
- Logging key management activity
- Monitoring key management activity
- Responding to legal requests for keys
Practical Real World
This really is going to depend but for most small business this requirement really comes down to encrypting devices and this is usually with standard or built in technology. The management of keys is often built in and easy to implement. The advice would be that unless you need something overly sophisticated keep it simple. Have HTTPs on your website, encrypt traffic, rely on the network technology of the likes of Azure and AWS and the apps that use that all these days are connections over encrypted links. Be able to show how the keys are managed in line with the above key management process requirements which again is usually easy to do and built into the technology that you are using.
The questions most asked at audit is, what if you loose the key, who knows what the key is, where is the key stored and is the key stored securely.
Cryptographic Objectives
The objectives of cryptography may seem common sense but lets us examine them.
You are looking to ensure the confidentiality of data as the main objective. We want to reduce the risk of a data breach, of data being intercepted and if it is intercepted we want that data to be useless.
It can be the case that cryptography can ensure non-repudiation, which means that we can provide evidence of events or actions.
Finally it can be used to authentication, to grant access only to the right people or resources or entities.
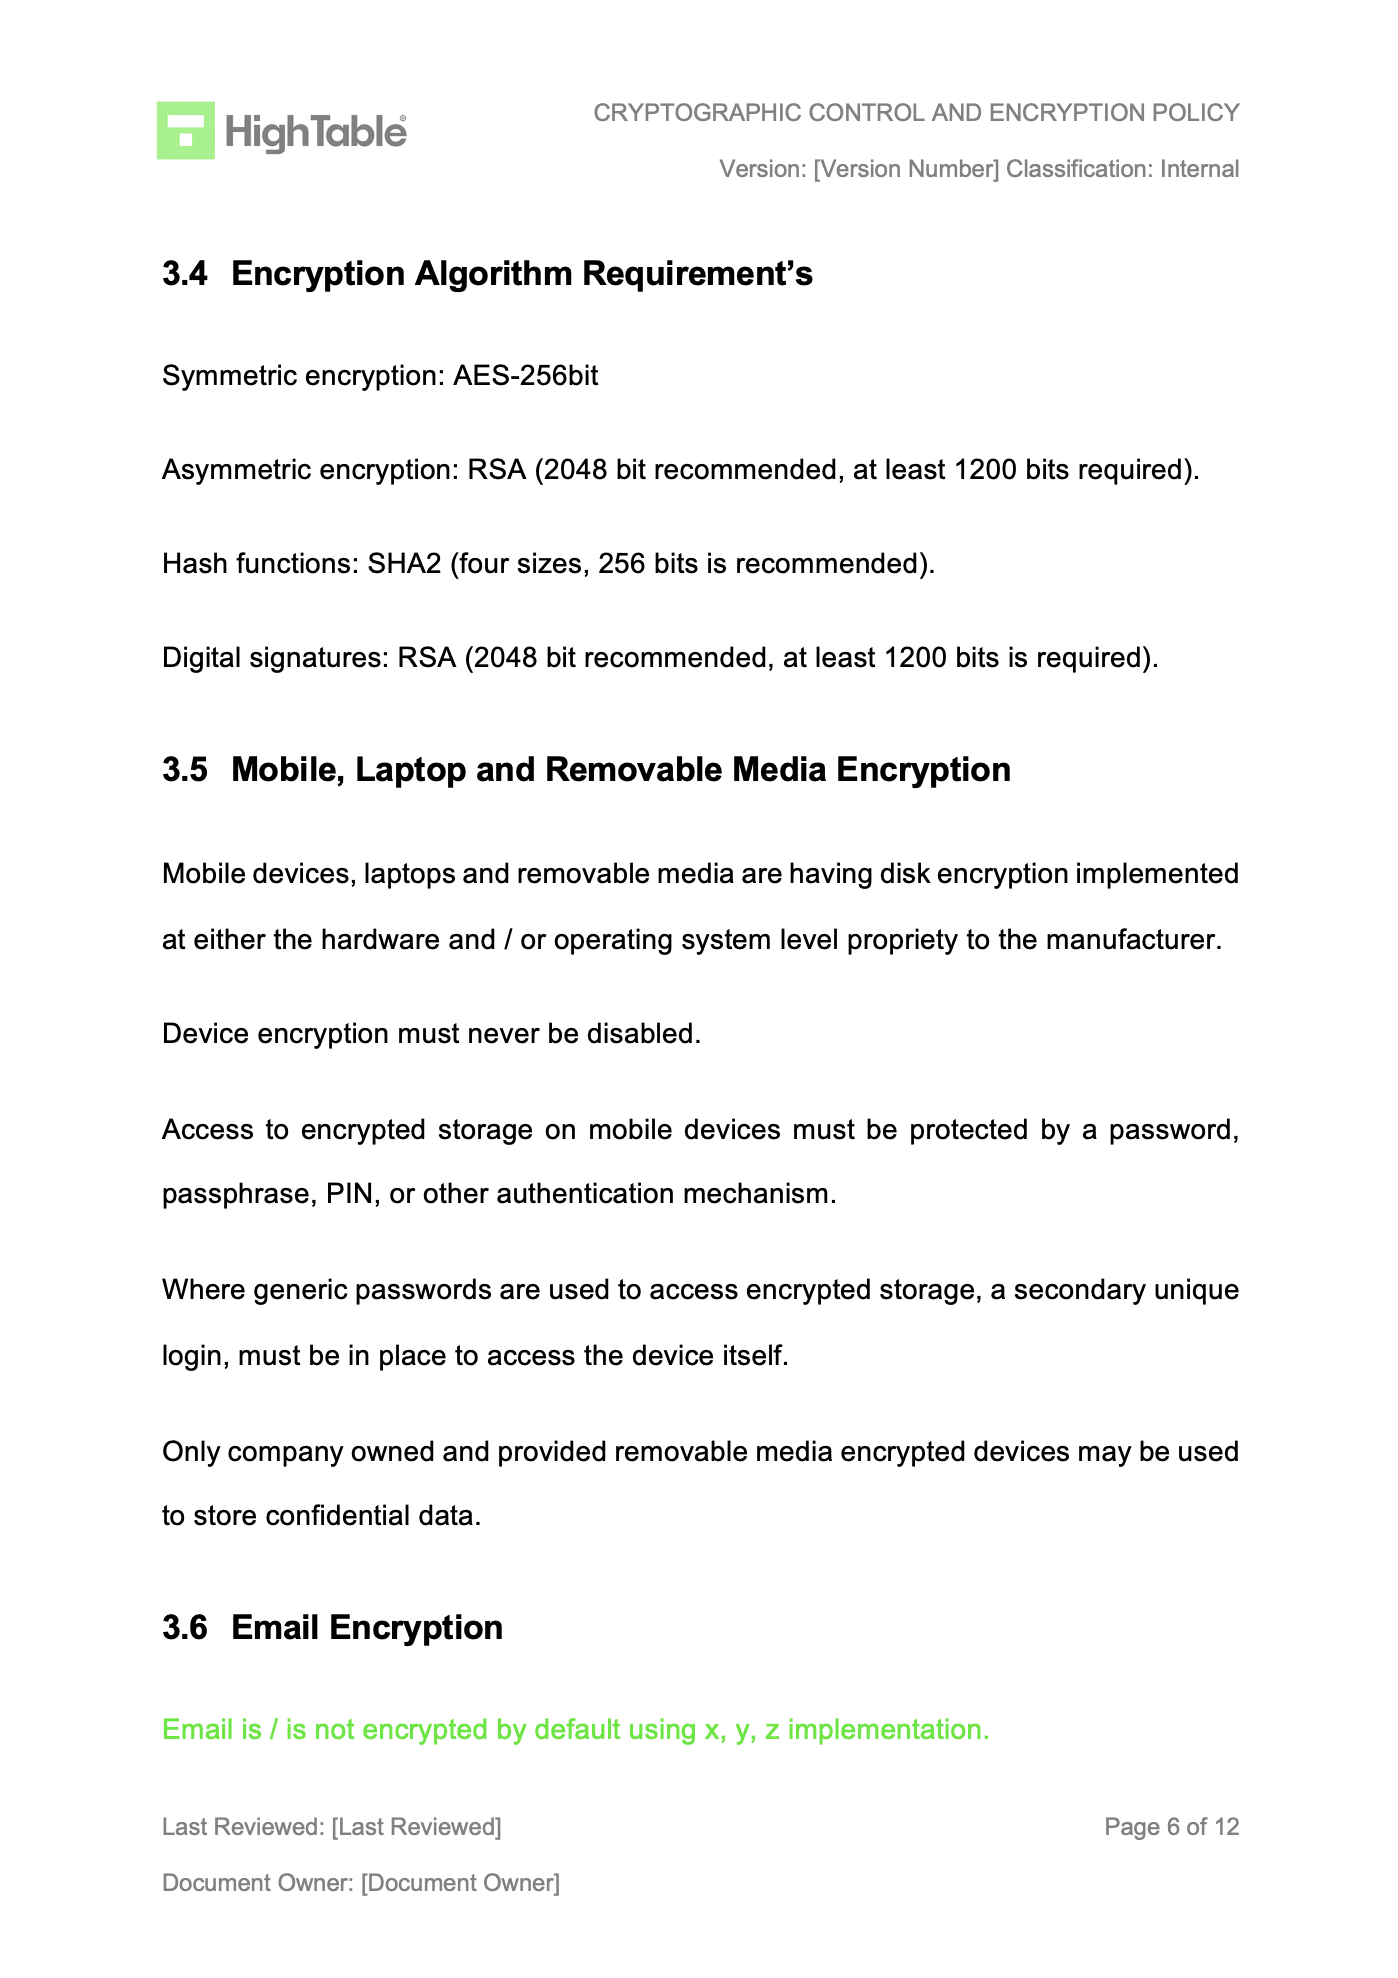
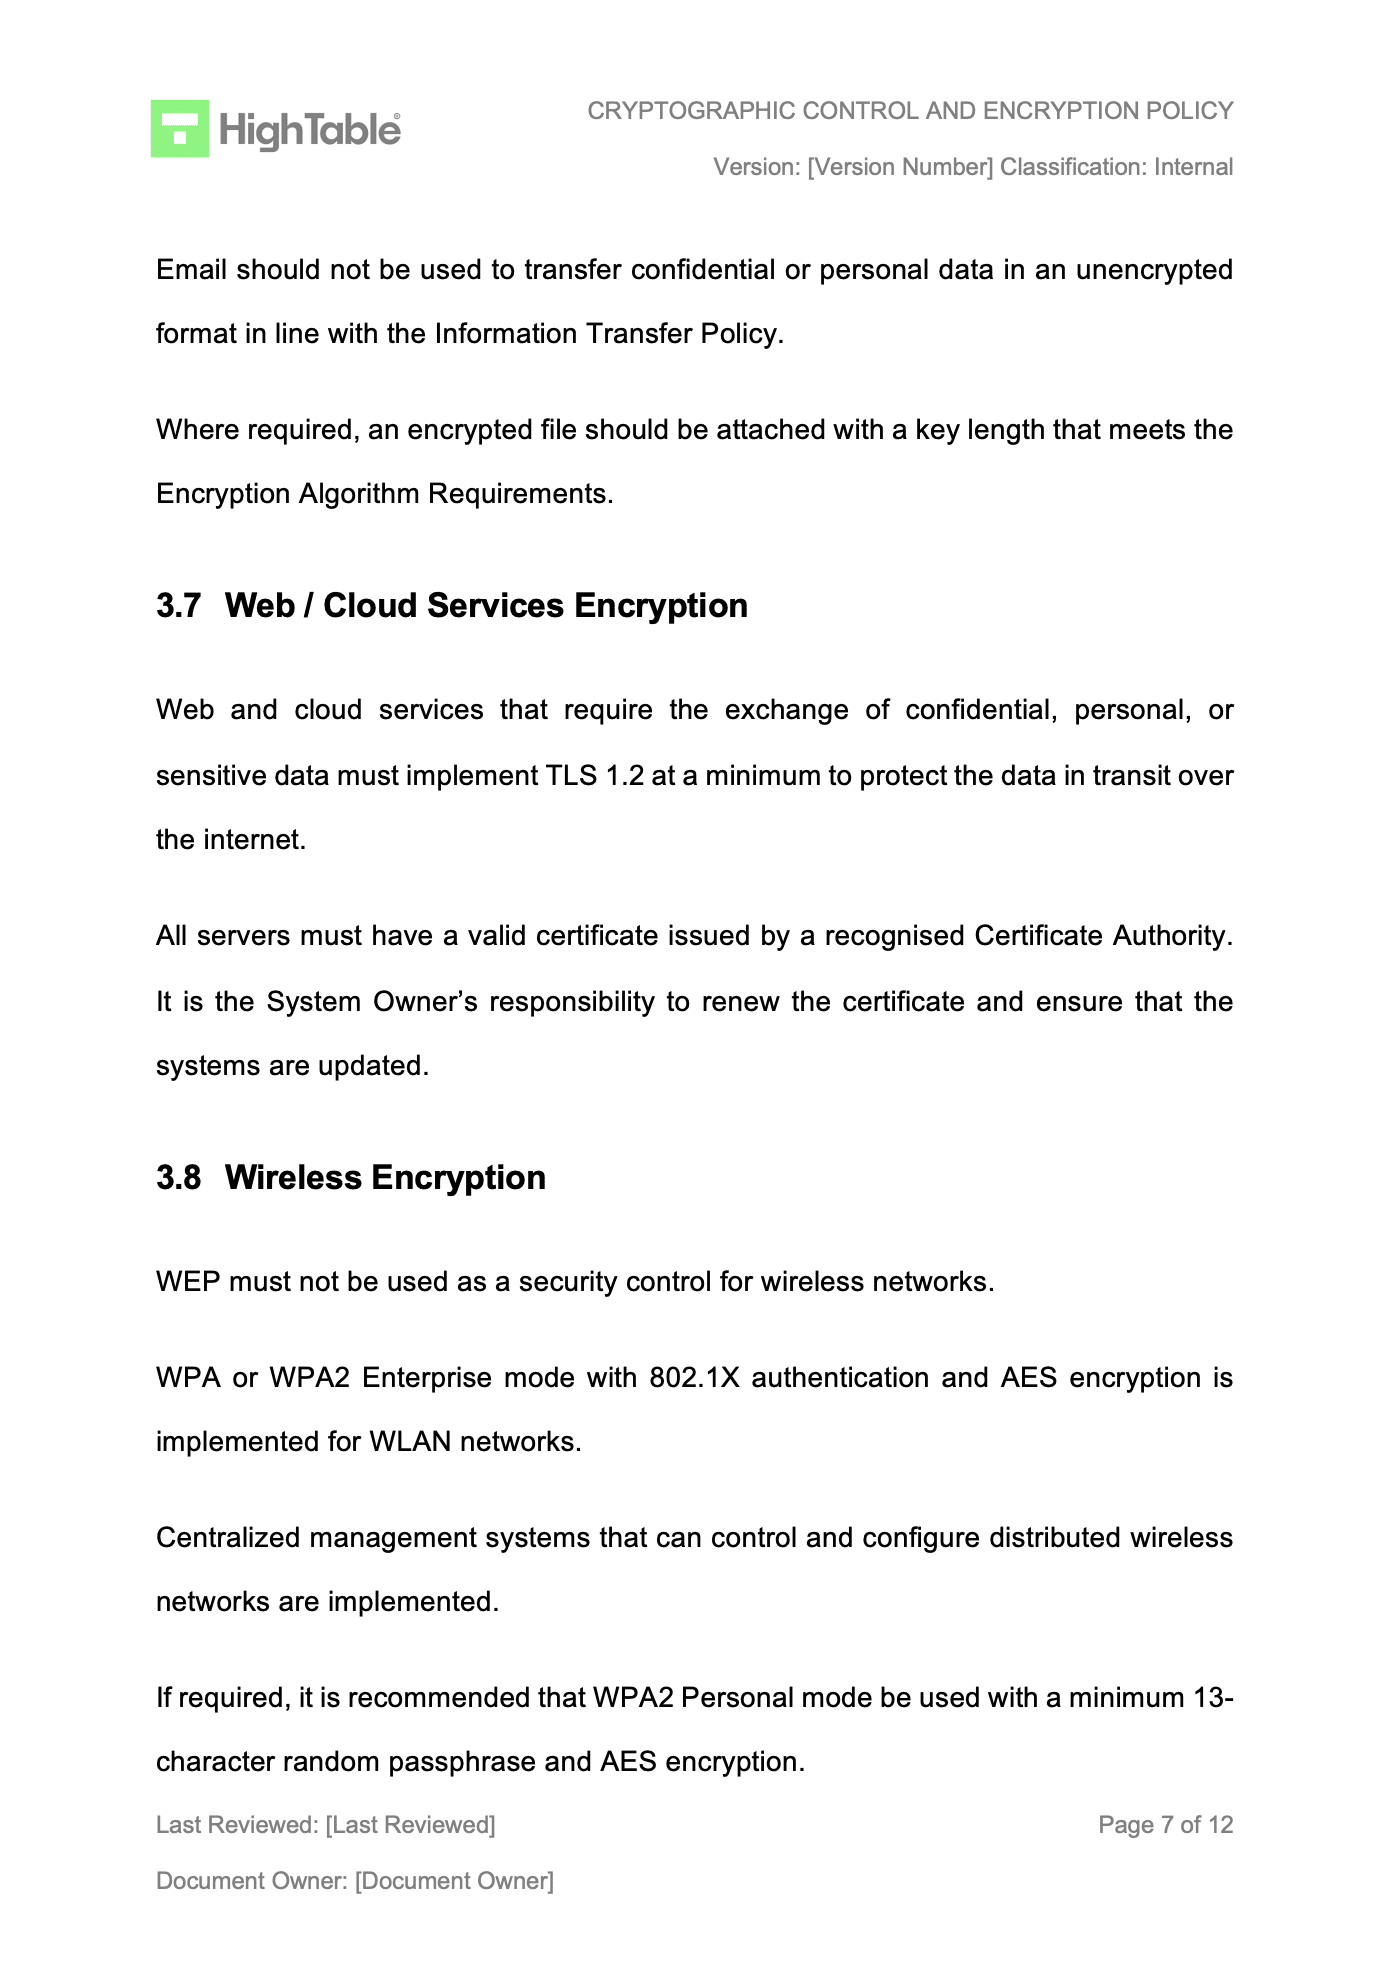
Cryptographic Control and Encryption Policy Template
To meet the requirements of this particular ISO 27001 clause you are going to need a topic specific policy for cryptography and for key management.
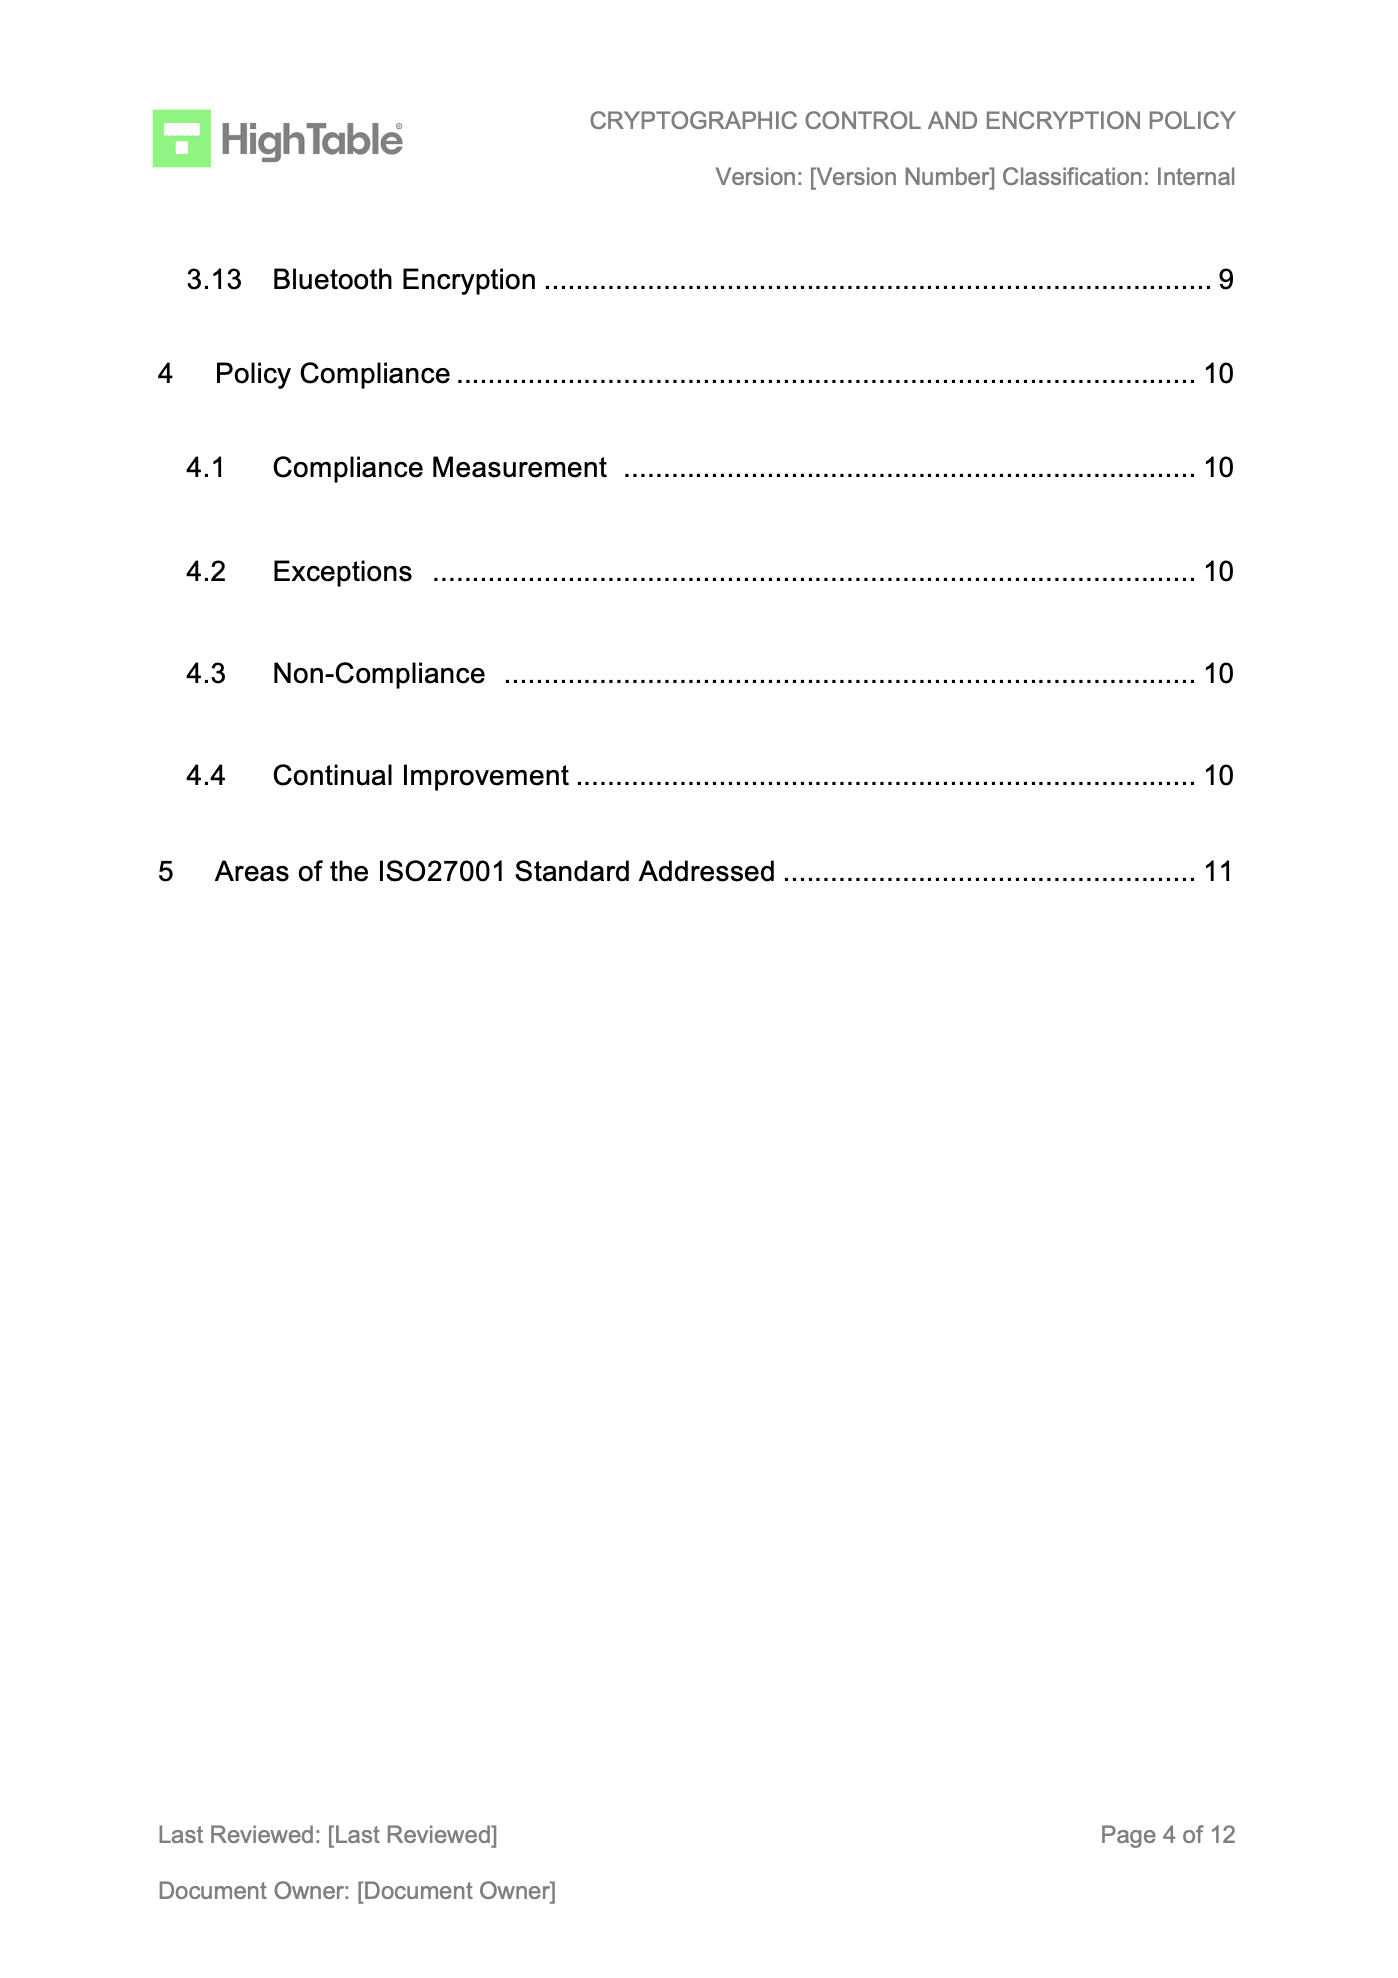
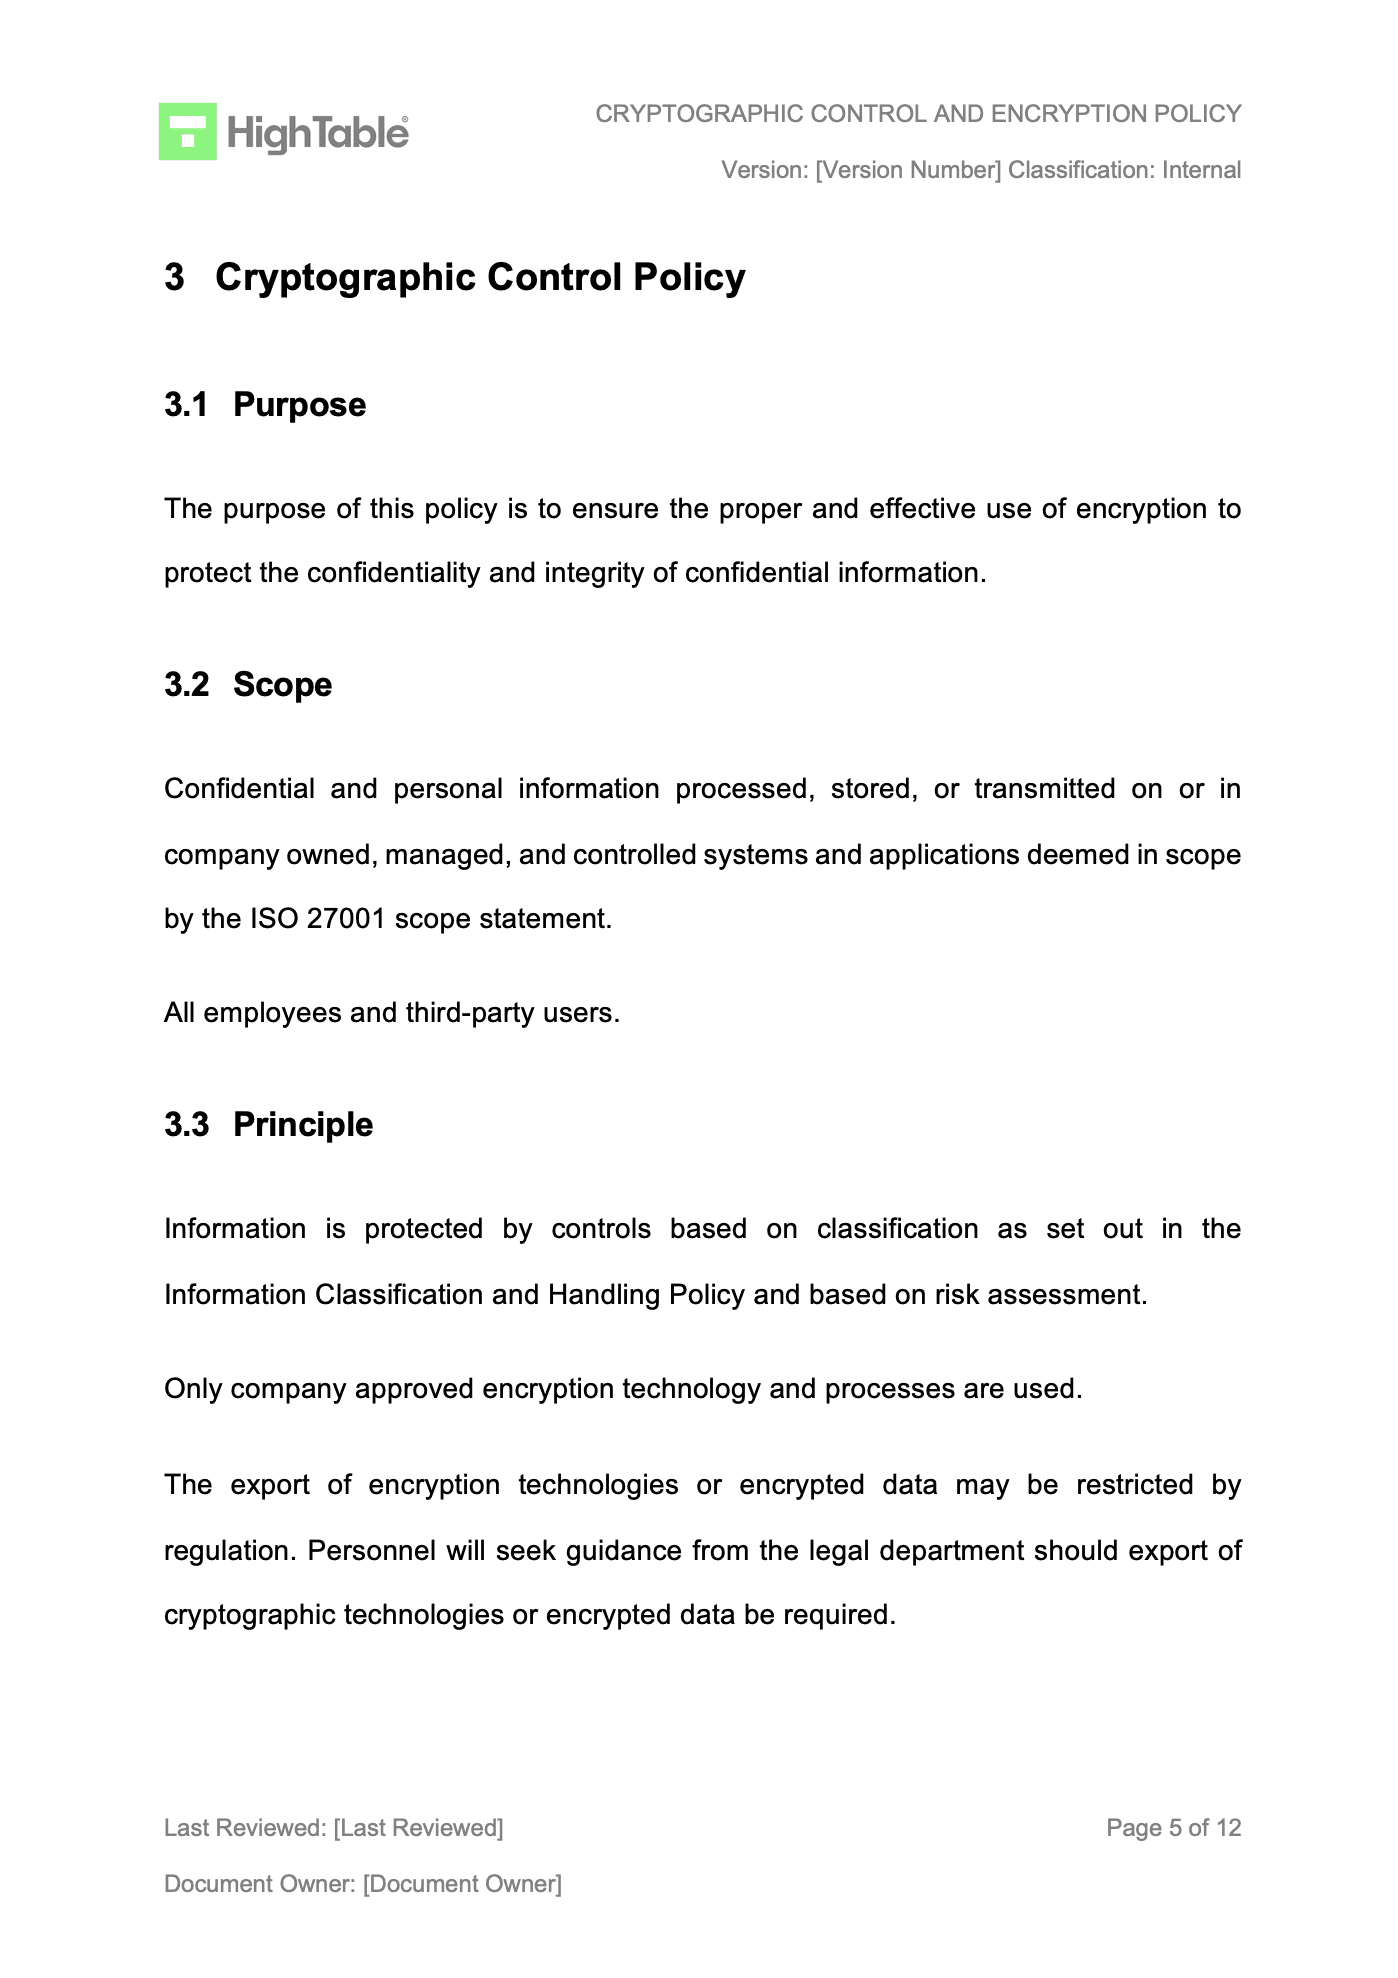
Cryptographic Control and Encryption Policy Example
An example of the ISO 27001 Cryptographic Control and Encryption Policy.
Key Management Policy Template
Information Classification Policy Template
More information on the requirements of the standard is covered in ISO 27001 Annex A 5.12 Classification Of Information and there is a handy ISO 27001 Information Classification and Handling Policy Beginner’s Guide
How to implement ISO 27001 Annex A 8.24
1. Formalise a Cryptographic Usage Policy
- Document a formal policy defining the types of information requiring cryptographic protection, including data at rest, in transit and in use.
- Specify the required encryption levels and approved algorithms (e.g. AES-256, RSA-4096) based on the sensitivity of the data and risk assessments.
- Result: A consistent organisational standard that ensures all cryptographic controls are applied uniformly and legally.
2. Provision a Centralised Key Management System (KMS)
- Deploy a dedicated Key Management System or Hardware Security Module (HSM) to automate the generation, storage and distribution of cryptographic keys.
- Establish clear technical procedures for key rotation, archival and destruction to prevent the use of compromised or outdated keys.
- Result: Reduced risk of unauthorised data access due to manual key handling errors or weak storage practices.
3. Enforce Encryption for Data in Transit and at Rest
- Mandate the use of TLS 1.3 or higher for all network communications and verify that all internal and external API endpoints require encrypted connections.
- Provision Full Disk Encryption (FDE) and database-level encryption for all storage media containing sensitive or personally identifiable information (PII).
- Result: Comprehensive protection of information assets against interception and physical theft of hardware.
4. Restrict Access to Cryptographic Keys via IAM and MFA
- Apply the Principle of Least Privilege by assigning specific Identity and Access Management (IAM) roles to users and services that require key access.
- Require Multi-Factor Authentication (MFA) for any administrative actions performed within the KMS or HSM environment.
- Result: Prevention of lateral movement and unauthorised decryption of sensitive data by malicious actors or compromised accounts.
5. Implement Digital Signatures and Integrity Checks
- Utilise digital signatures to verify the authenticity of software builds, legal documents and critical configuration files.
- Configure automated hashing algorithms (e.g. SHA-256) to perform periodic integrity checks on sensitive system files and databases.
- Result: Assurance that critical information and software have not been tampered with or modified by unauthorised parties.
6. Execute Regular Cryptographic Audits and Reviews
- Conduct periodic technical reviews of your cryptographic infrastructure to ensure that algorithms remain secure against modern brute-force attacks.
- Formalise an incident response plan specifically for “Compromised Key” scenarios, including immediate revocation and re-encryption procedures.
- Result: A dynamic and resilient cryptographic posture that evolves to meet new security threats and technological advancements.
Check Your Work?
You buit it yourself. Maybe with AI. But will it pass the audit?
Don’t gamble – let a trained ISO 27001 auditor check your work.
ISO 27001 Templates
Further Reading
About the author