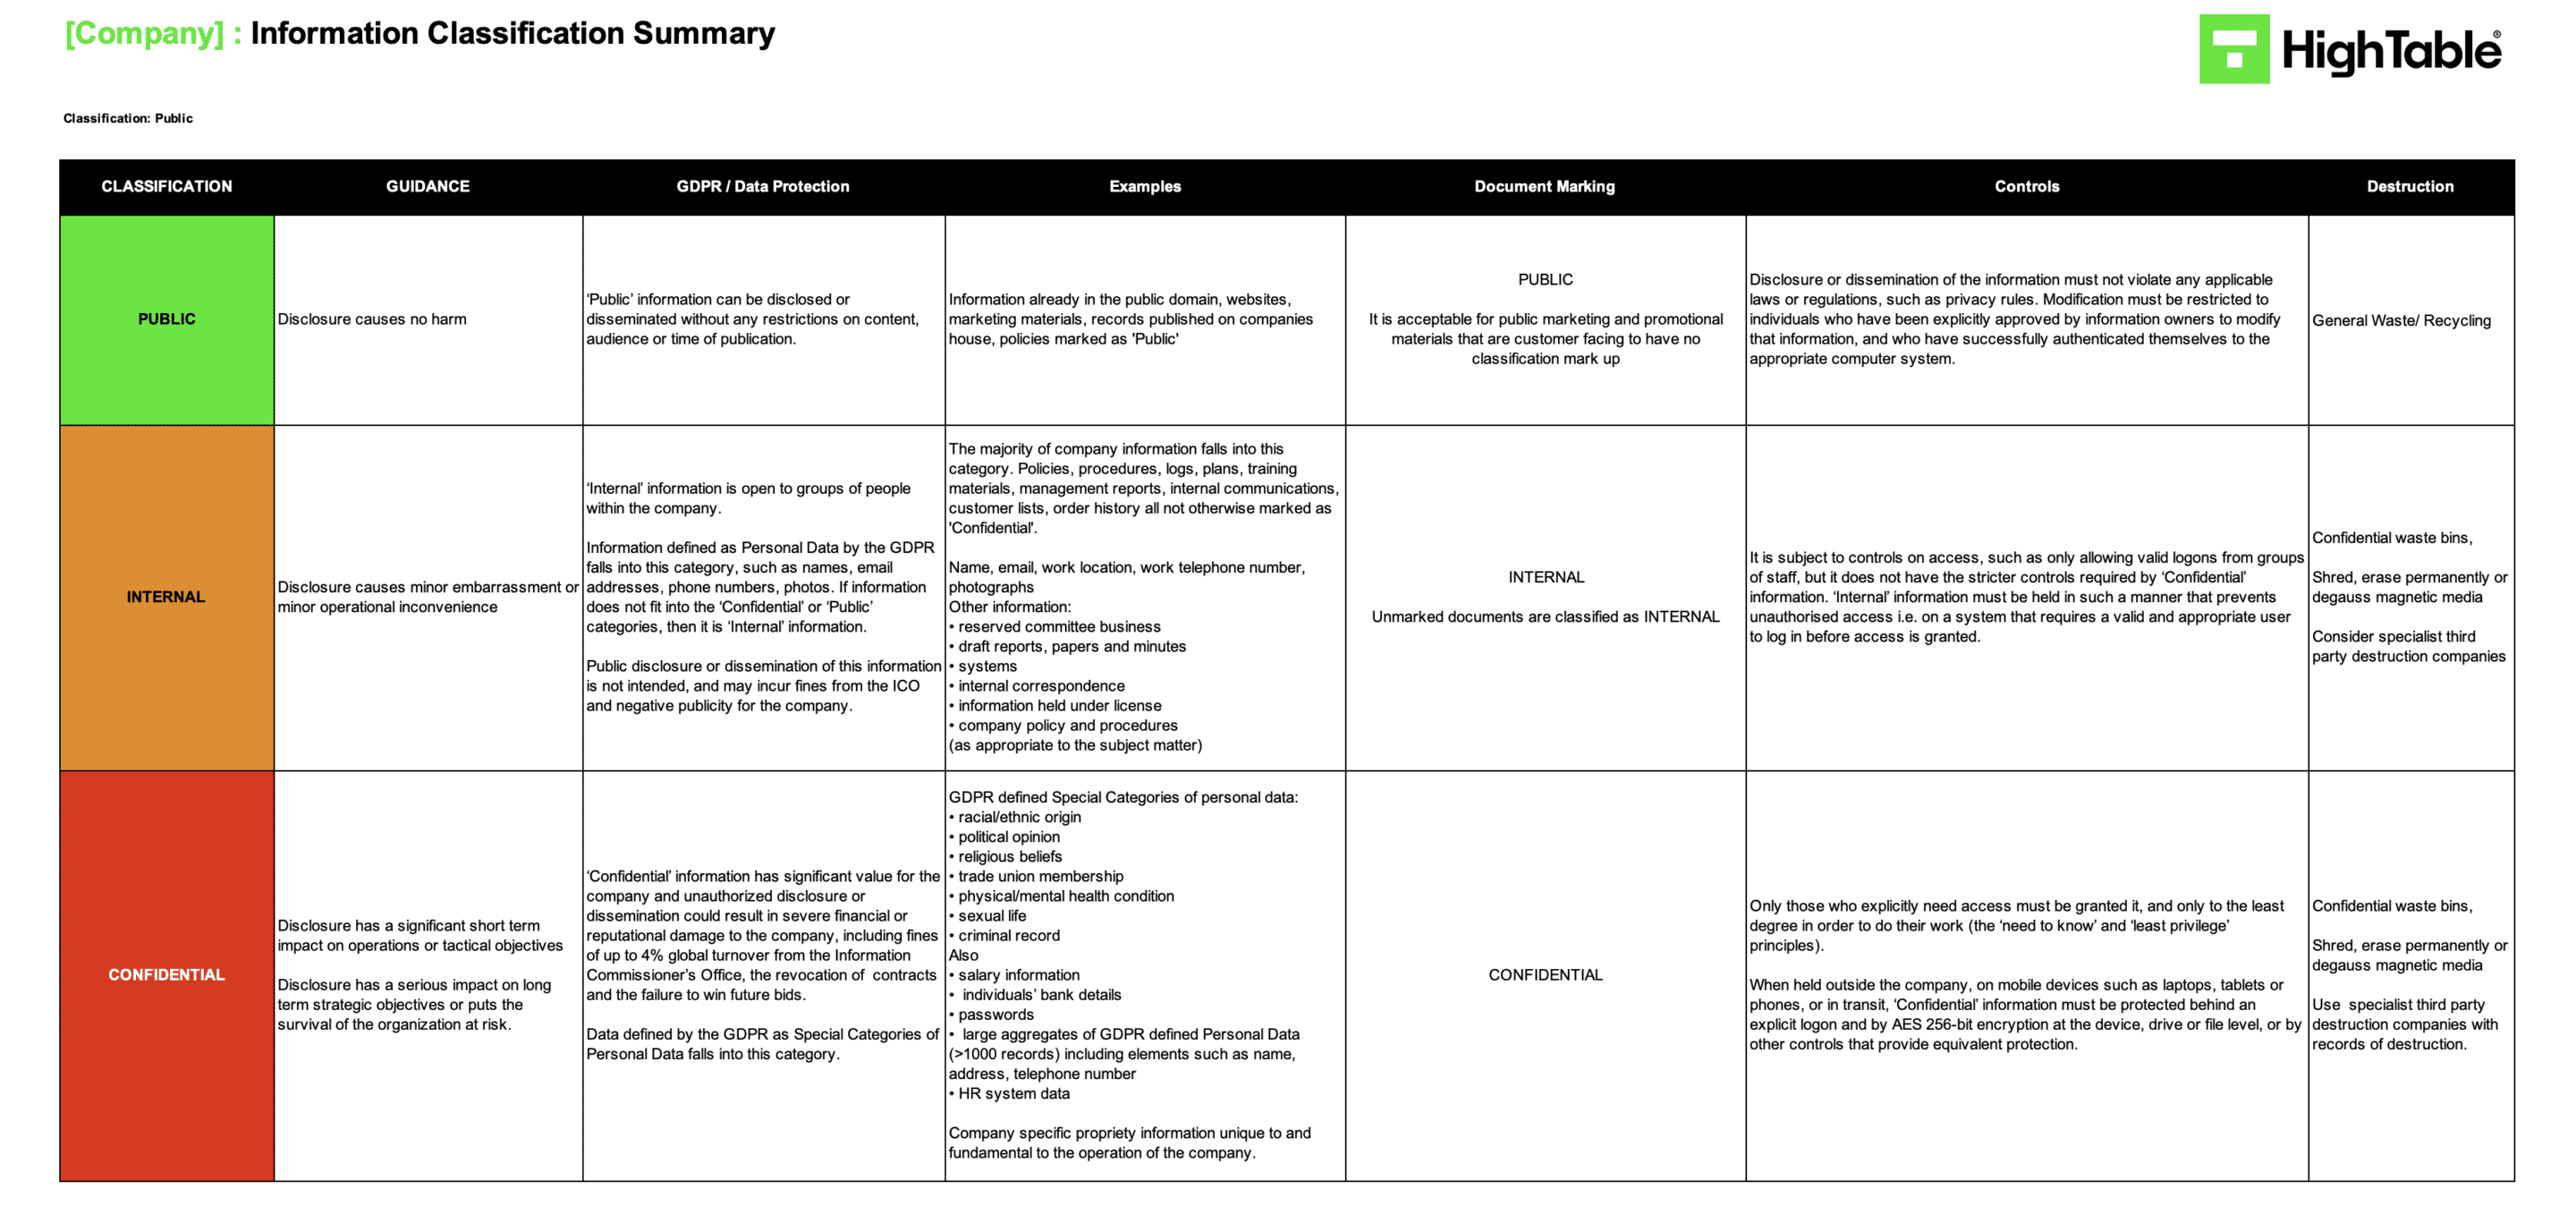
ISO 27001:2022 mandates that you protect information based on its value and sensitivity. If you don’t classify your data, you risk over-protecting low-value items or, more dangerously, under-protecting your business-critical assets.
Why Information Classification Matters
Classification is the first step in effective risk management. By using this summary template, you can ensure that:
- Resources are Allocated Correctly: High-value data receives the strictest security controls.
- Employees Understand Responsibilities: Clear labels (Public, Internal, Confidential) dictate exactly how data should be handled, shared, and stored.
- Compliance is Visible: Auditors can quickly assess your classification policy during the certification audit.
What is Included?
This template takes a “keep it simple” approach, which is vital for maintaining compliance in a small team. You get:
- Classification Scheme: A pre-defined structure that works for 99% of businesses.
- Handling Examples: Practical scenarios for how to treat data at each sensitivity level.