
ISO 27001:2022 Clause 7.2 (Competence) is a mandatory operational enablement requirement dictating that organizations determine the necessary competence of personnel affecting information security performance, ensure they are qualified through education, training, or experience, and retain documented evidence to pass certification audits.
In this guide, you will learn how to implement Clause 7.2 correctly – defining practical role competencies, closing skill gaps with targeted training, retaining clean audit evidence without HR matrix bloat, and passing your audit – with expert guidance from leading ISO 27001 consultant and certified Lead Auditor Stuart Barker, Director at HT Black Consulting (formerly High Table), the specialist ISO 27001 consultancy.
Table of contents
- ISO 27001 Clause 7.2 Purpose & Definition
- ISO 27001 Clause 7.2 Video Tutorial
- How to implement ISO 27001 Clause 7.2
- The Role of External Consultants and Outsourcing
- ISO 27001 Clause 7.2 Templates
- How to build your own competence matrix
- How to pass the ISO 27001 Clause 7.2 audit
- ISO 27001 Clause 7.2 FAQ
- Further Reading
ISO 27001 Clause 7.2 Purpose & Definition
The purpose of ISO 27001 Clause 7.2 Competence is to make sure that the people you have working on the information security management system (ISMS) have the skills, knowledge and experience to do it.
The organisation shall: a) determine the necessary competence of person(s) doing work under its control that affects its information security performance; b) ensure that these persons are competent on the basis of appropriate education, training, or experience; c) where applicable, take actions to acquire the necessary competence, and evaluate the effectiveness of the actions taken; and d) retain appropriate documented information as evidence of competence.
ISO 27001:2022 Clause 7.2 Competence
What is does it mean? It means you have people on the team when we’re running your information security management system (ISMS) that know how to run the management system.
You cannot have ISO 27001 and go for certification if nobody knows any anything about ISO 27001, they’ve got no experience in ISO 27001 and they’ve got no knowledge in ISO 27001.
Requirement
ISO 27001 Clause 7.2 Video Tutorial
In this video tutorial you will learn how to implement ISO 27001 Clause 7.2 and pass your audit.
How to implement ISO 27001 Clause 7.2
Step 1: Formalise ISMS Roles and Accountability
- Action: Define specific information security duties for every role using a granular Accountability Matrix (RASCI). Assign ownership for Clause 7.1 resources and Annex A controls.
- Result: Ensures clear ownership of ISO 27001 controls and prevents ambiguity regarding who is responsible for critical tasks such as risk assessments or incident response.
- Technical Requirement: Update job descriptions to include specific ISMS responsibilities and map these to your Role-Based Access Control (RBAC) definitions to ensure segregation of duties.
Step 2: Define Technical and Legal Competency Requirements
- Action: Document the exact qualifications, experience, and skills required for each role. This includes internal technical skills (e.g., AWS security, firewall config) and external legal requirements (e.g., GDPR, Data Protection).
- Result: Creates a measurable standard for assessing staff. It also clarifies where external support, such as outsourced legal counsel or virtual DPOs, is necessary to meet competence obligations.
- Technical Requirement: Specify required certifications (e.g., CISSP, CISM, ISO 27001 Lead Auditor) and formalise contracts for outsourced legal competence where in-house expertise is absent.
Step 3: Conduct a Competency Gap Analysis
- Action: Audit your current workforce’s capabilities against your defined baselines using a Competency Matrix. Identify where incumbents lack necessary certifications or documented experience.
- Result: Generates a prioritised list of vulnerabilities where a lack of knowledge could lead to non-conformity.
- Technical Requirement: Utilise a structured Competency Matrix to visualise data, ensuring every person affecting the ISMS has a corresponding record of skill validation.
Step 4: Execute Targeted Training and Resourcing
- Action: Address identified gaps by implementing ISO 27001 Lead Implementer/Auditor training for internal staff or engaging specialist ISO 27001 consultants for complex phases like establishment and certification.
- Result: Mitigates human risk by ensuring the correct resource is used at the correct lifecycle phase, balancing internal development with external expertise.
- Technical Requirement: Create formal Training Plans within your Learning Management System (LMS) or engage High Table consultants to bridge high-risk competency gaps during the implementation phase.
Step 5: Centralise and Validate Audit Evidence
- Action: Archive all proofs of competence, including certificates, quizzes, and induction checklists, in a retrievable format.
- Result: Guarantees a smooth audit process by providing instant verification that competence is being actively managed and evolved.
- Technical Requirement: Maintain a digital register of Continuing Professional Development (CPD) logs and third-party competence contracts (e.g., legal/security operations) within your HR or GRC repository.
Built by an Expert ISO 27001 Consultancy
Prefer a DIY approach or have an internal team ready to execute? As a specialized ISO 27001 consultancy, we built this battle-tested ISMS toolkit for teams under 10. Stop building from scratch with generic templates—get the exact audit-ready documentation our ISO 27001 consultants use in the field.

✓ Complete ISMS Policies & Controls
✓ Built for Lean Internal Teams
✓ Guaranteed Certification Audit Success
The Role of External Consultants and Outsourcing
It can be useful to rely on the competence of third parties. If you engage with third parties and consultants then this is a fast track to the evidence of competence for the areas that they cover.
ISO 27001 Clause 7.2 Templates
For ISO 27001 Clause 7.2 Competence the entire ISO 27001 toolkit is relevant but in particular the following templates directly support this ISO 27001 clause:
ISO 27001 Competency Matrix Template
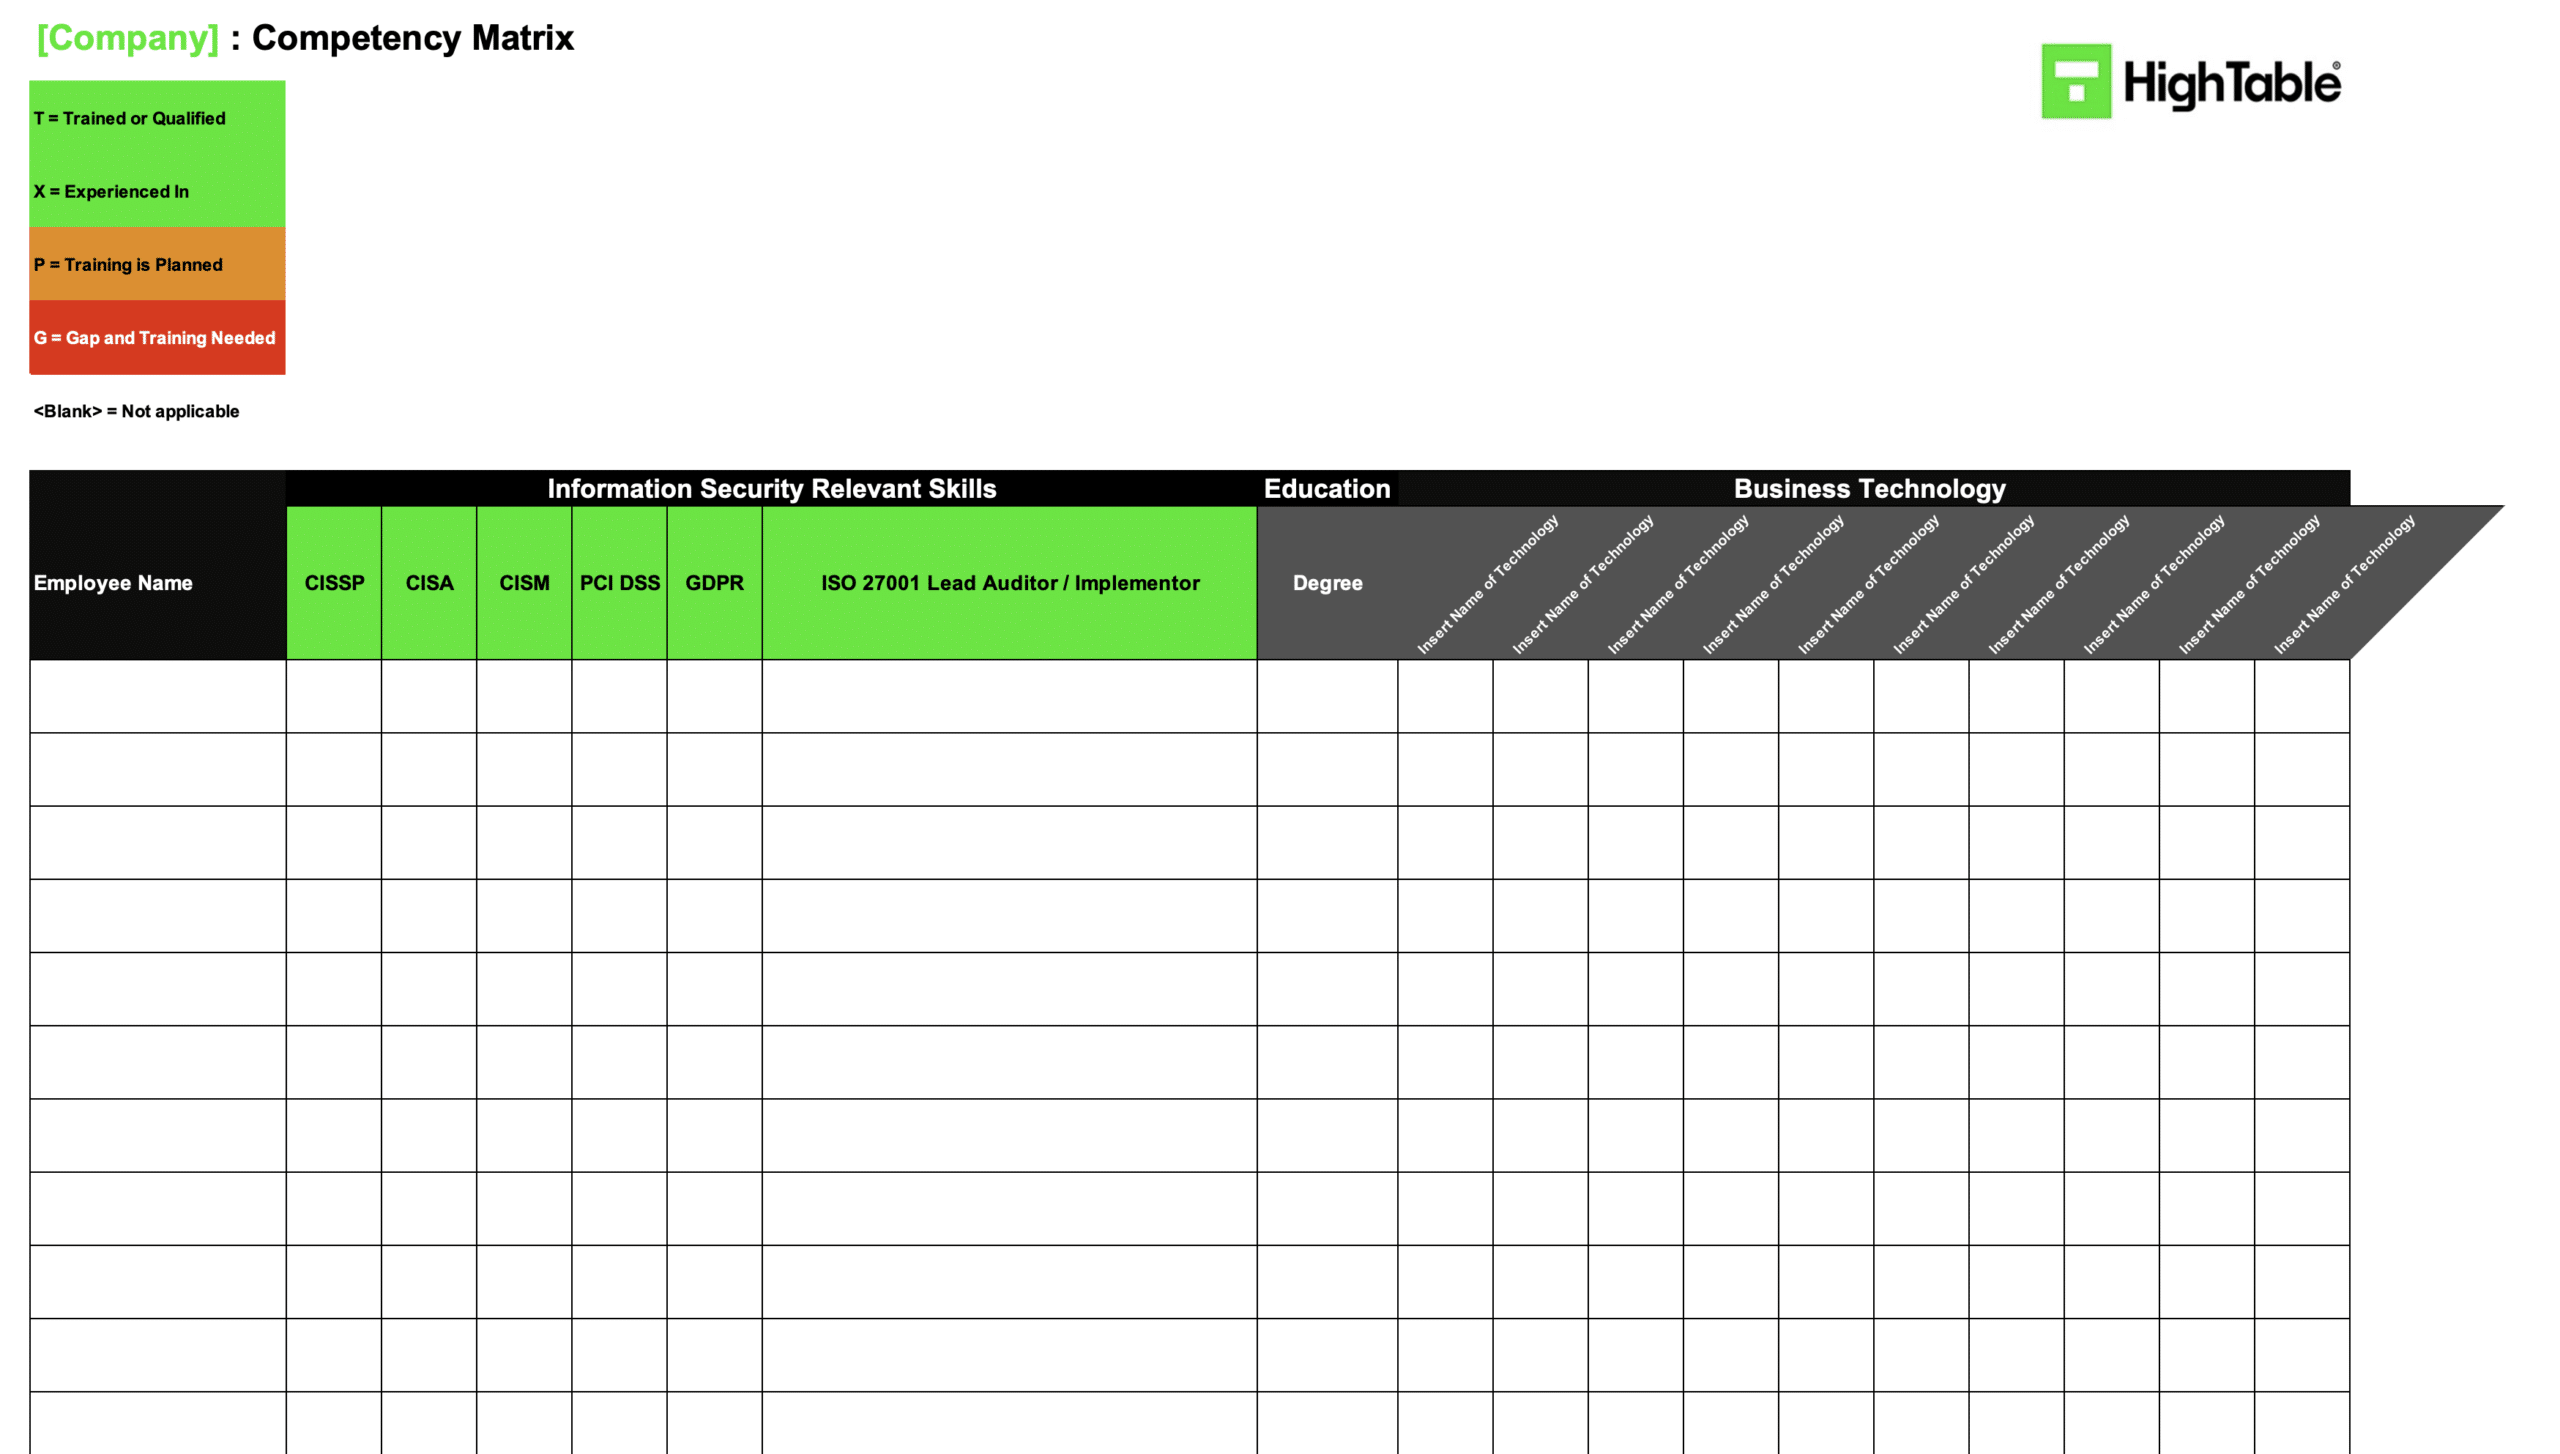
The ISO 27001 competency matrix template is used to record the employees and the skills that they have, the skills they require and any training needs. It is directly supports clause 7.2 and is a key document to meeting it.
ISO 27001 Accountability Template
The ISO 27001 accountability template records which employees are accountable and responsible for the information security management system and all of the ISO 27001 Annex A controls. It is a key document in identifying and recording who is doing what and is used along with the competency matrix to record the skills and experience they have for the areas that they have been assigned.
ISO 27001 Training Policy Template
The ISO 27001 training policy template is a supporting document that sets out the organisations approach to training and commitment to ensuring employees have the skills and experience that they need to perform the roles that they have been assigned to.
ISO 27001 Competency Matrix
How to build your own competence matrix
How to pass the ISO 27001 Clause 7.2 audit
To pass an audit of ISO 27001 Clause 7.2 Competence you are going to
- Understand the requirements of ISO 27001 Competence
- Identify the roles you need
- Allocate people to roles
- Assess the competency of people to perform those roles
- Address competency gaps through training or bringing in specialist help
The High Table ISO 27001 Internal Audit.
ISO 27001 strictly requires impartiality – you cannot audit your own work. If you implemented the ISMS, you must use an independent expert before the certification body arrives. Book your ISO 27001 Internal Audit with High Table and let Lead Auditor Stuart Barker’s team guarantee your certification readiness.
✓ 100% Independent & Impartial
✓ Conducted by Certified Lead Auditors
✓ Fixed-Price, Zero-Friction Process

ISO 27001 Clause 7.2 FAQ
ISO 27001 Clause 7.2, also known as the competence clause, requires organizations to determine the necessary competence of people doing work under their control that affects information security performance. This means the organization must identify the skills, knowledge, and experience needed for each role that impacts the Information Security Management System (ISMS), ensure that people in those roles possess them, and keep documented evidence of their competence.
Great news. There are no changes to ISO 27001 Clause 7.2 in the 2022 update.
Competence (Clause 7.2) is about having the specific knowledge, skills, and experience to perform a job effectively, especially as it relates to information security. It’s a role-specific requirement. Awareness (Clause 7.3) is about ensuring all people under the organization’s control are aware of the information security policy, their contribution to the ISMS, and the implications of not conforming. Awareness is a universal requirement for all personnel, while competence is targeted to specific roles.
The best way is to record the skills of your resources in a Competency Matrix.
You can demonstrate competence by providing documented evidence such as:
Job descriptions that outline required skills.
Resumes or CVs showing relevant experience.
Training records, certificates, or qualifications.
Records of on-the-job training or mentoring programs.
Performance reviews that assess security-related tasks.
Auditors may also conduct interviews to verify that personnel understand their responsibilities.
A competency matrix is a tool, usually a spreadsheet, that maps personnel roles and responsibilities to the required skills, knowledge, and experience for information security. While it’s not explicitly required by the standard, it’s considered best practice because it provides a clear, documented way to demonstrate compliance with Clause 7.2, identify skill gaps, and manage training needs.
If an organization identifies a competence gap, Clause 7.2 requires them to take action. This may include:
Providing training, such as workshops, e-learning courses, or seminars.
Offering mentoring or on-the-job guidance from experienced staff.
Encouraging professional development and obtaining certifications.
Reassigning roles or hiring new, competent personnel.
The organization must also evaluate the effectiveness of these actions.
No, the standard does not require everyone to be an information security expert. It only requires that personnel are competent for the work they do that affects the ISMS. For example, an IT administrator needs technical security skills, while a call centre agent needs training on how to handle customer data securely and validate identities.
ISO 27001 doesn’t specify a frequency, but competence should be reviewed regularly to ensure it remains current with evolving threats and changes in roles or technologies. This can be done as part of annual performance reviews, during internal audits, or when new security risks are identified.
A non-conformity in Clause 7.2 means the organization hasn’t sufficiently demonstrated that its personnel are competent to manage information security risks. This could be due to a lack of documented evidence, skill gaps, or ineffective training. The organization would then be required to implement corrective actions to address the issue and show evidence of improvement to the auditor.
Yes, absolutely. The standard explicitly states that competence can be based on appropriate “education, training, or experience.” Experience is a crucial component, and organizations should document it through job descriptions, performance reviews, or other records that highlight the individual’s history and accomplishments related to information security.
Yes. Many companies seek the help of qualified, experienced third party suppliers to help with ISO 27001.
Yes, there are many reputable training courses for ISO 27001 Lead Auditor and ISO 27001 Lead Implementor.
To build competence without breaking the bank, consider these strategies:
Internal training: Have experienced employees mentor or train their colleagues.
Knowledge sharing: Create forums or sessions for team members to share insights on emerging threats and best practices.
Free resources: Encourage self-study using free online resources, articles, and government-provided security guides.
Cross-training: Allow employees to work on different security projects to broaden their experience.
Further Reading
Stuart Barker
Lead ISO 27001 Consultant
Stuart Barker is a qualified ISO 27001 Lead Auditor, ISO 27001 Lead Implementer and veteran practitioner with over 30 years of experience in systems security and risk management. Holding an MSc in Software and Systems Security, he combines academic rigour with extensive operational experience, including a decade leading Data Governance for General Electric (GE).
He is the founder of High Table (operating as HT Black Consulting) and the Lead Consultant driving the specialist ISO 27001 Consultancy, delivering expert advisory, internal audits, and battle-tested ISMS frameworks for technology companies, small business and startups.