
In this guide, you will learn what an ISO 27001 Acceptable Use Policy is, how to write it yourself and I give you a template you can download and use right away.
Table of contents
- What is an Acceptable Use Policy?
- Acceptable Use Policy Template
- Importance of Acceptable Use Policy
- What should an acceptable use policy contain?
- How to write and implement an acceptable use policy
- Acceptable Use Policy for Employees
- Acceptable Use Policy for Business
- ISO 27001 Acceptable Use Policy Example
- ISO 27001 Acceptable Use Policy FAQ
What is an Acceptable Use Policy?
There are things that we do and do not want people to do with company computers, systems and data. The acceptable use policy set’s out what we expect and explains it in simple terms.
An acceptable use policy would be read by everyone that uses the company systems and a signed acceptance of the policy would be kept.
It is about accountability, responsibility and respect.
The acceptable use policy ensures people understand what is expected of them when using company resources.
The ISO 27001 requirement for acceptable use is covered in ISO 27001 Annex A 5.10 Acceptable Use of Information and Other Associated Asset.
Acceptable Use Policy Template

This ISO 27001 Acceptable Use Template is pre written with what good looks like for acceptable use.
Importance of Acceptable Use Policy
The acceptable use policy is important as it sets out clearly and in written form what you expect to happen. If you don’t tell people what you expect of them then how can you expect them to do it?
Communicating what is expected is a key step in any HR disciplinary process with many not being enforceable or actionable if you have not told people what to do and got them to accept that they understand what is being asked.
The ISO 27001 standard wants you to have the acceptable use policy in place, communicated, and accepted by staff as part of your ISO 27001 certification. It actually forms part of a wider set of required information security policies that are all included in the ISO 27001 toolkit.
What should an acceptable use policy contain?
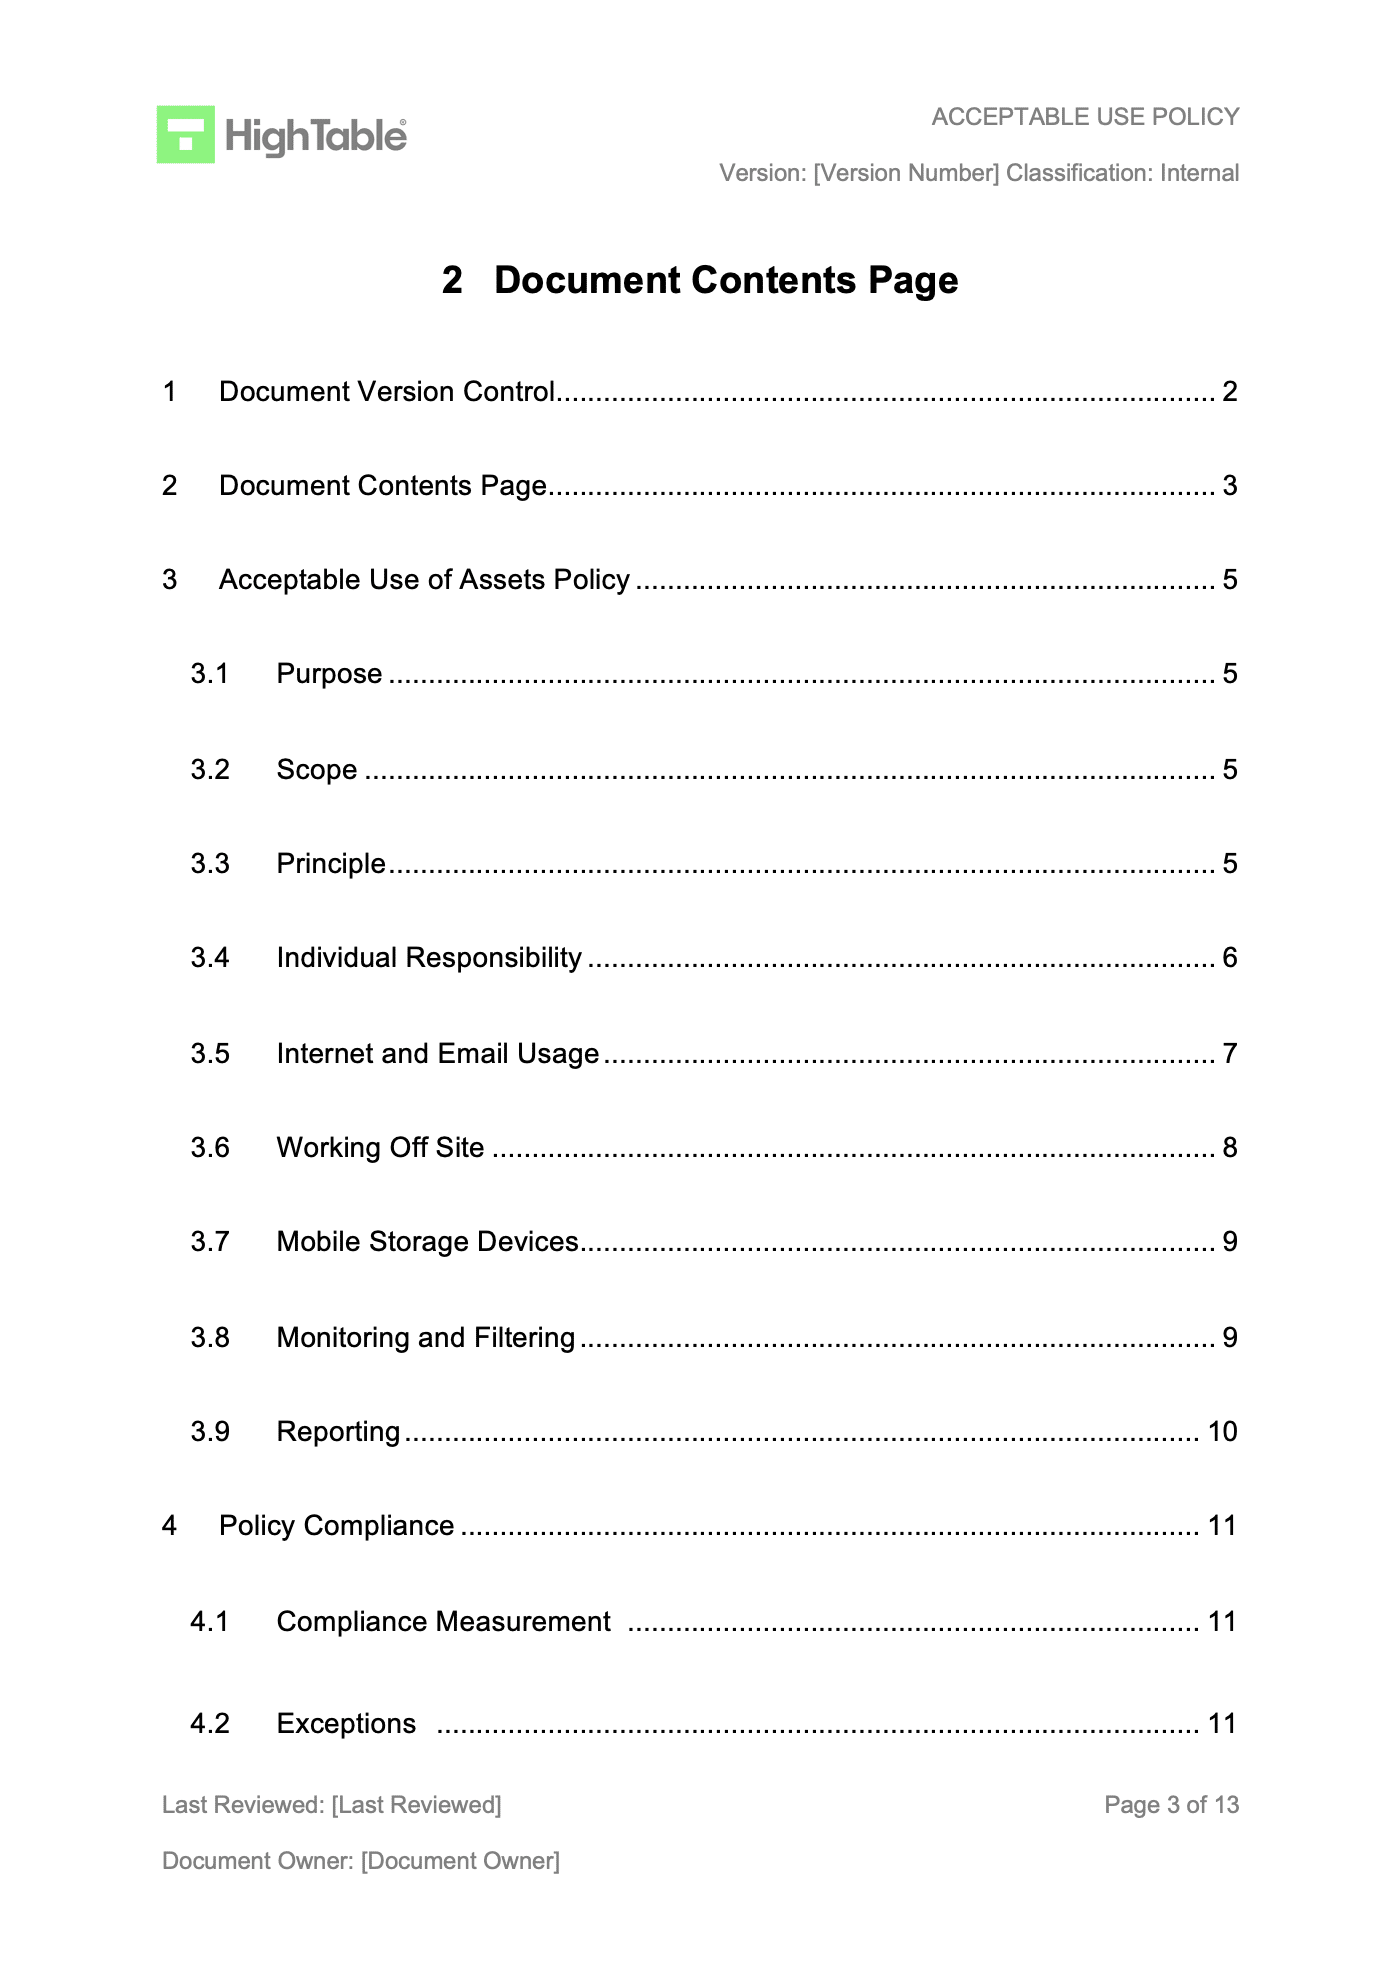
The acceptable use policy is required to be presented in a certain way. What we mean by that is that the policy is expected to have certain document markup. Document mark up is just a fancy words for having certain information on the policy. It will need version control, a version number, an owner, an information security classification. An example acceptable use policy table of contents would look something like this:
Document Version Control
Document Contents Page
Purpose
Scope
Acceptable Use of Assets Policy
Principle
Individual Responsibility
Internet and Email Usage
Working Off Site
Mobile Storage Devices
Monitoring and Filtering
Reporting
Policy Compliance
Compliance Measurement
Exceptions
Non-Compliance
Continual Improvement
How to write and implement an acceptable use policy
To implement an ISO 27001 Acceptable Use Policy, you must define the rules for asset interaction, obtain formal employee sign-off, and establish enforcement mechanisms. This ensures that all personnel understand their security responsibilities regarding corporate hardware, software, and data handling to mitigate insider threats and legal liabilities.
1. Identify your company assets
Identify what assets your company has. This will be both software and hardware. It can include premises. What are the assets that your business uses to conduct its business.
2. Prioritise your company assets
Once you identify what assets you rely on to conduct business priorities them based on the importance to the business, the classification of the data that is stored, processed or transmitted through them and the risk they pose to you. An example would be email that would be classed as high importance to the company and probably classed as confidential.
3. Set rules for the assets based on the priority
With the list of assets and the prioritisation set about writing the rules of what people can and cannot do with those assets. If you rely on email for critical client communication you are unlikely to want people to use their email to sign up to newsletters, conduct on line shopping and other personal business that increases the risk of spam and phishing attacks that would then compromise your organisation. The rules are to reduce risks. Being respectful to the needs of the employee find the right balance and set the rules of acceptable use.
4. Review and approve the acceptable use policy
The policy should be formally reviewed and formally approved. It would normally be approved at the management review meeting but you want to ensure that it has the sign off of the HR department and of senior management as a minimum. This gets the agreement that these are the rules that we are going to operate by.
5. Communicate the acceptable use policy to all staff
Consider as part of your required communication plan the different ways and timings that are appropriate to you to communicate the acceptable use policy. Make sure it is store somewhere that people can easily access it at any time and that they can, indeed, access it.
6. Get evidence that the staff have accepted the acceptable use policy
Using your acceptance methodology get staff to accept that they have read and understand the policy and accept its terms. Maintain evidence of this for future audit and potential disciplinary process.
Acceptable Use Policy for Employees
The acceptable use policy for employees balances the needs of the business with the needs of the employees. It is not wrong to allow certain things to happen. It just might not be best practice. Take for example using company assets to run a side hustle. That is probably something you don’t want to allow and want to write into policy. But it maybe that you are ok with it in your business. Take the time to balance what is right for the business and what is right for the employee.
Acceptable Use Policy for Business
The acceptable use policy for business is about protecting the business. It is easy to take it too far to the point the employee cannot do their job. As above you want to find the right balance between protecting the business and respecting the employees.
DO IT YOURSELF ISO27001
Stop Spanking £10,000’s on Consultants and Platforms
ISO 27001 Acceptable Use Policy Example
This is an example ISO 27001 Acceptable Use Policy:
ISO 27001 Acceptable Use Policy FAQ
The acceptable use policy applies to all staff, contracts and third parties that access or use company assets.
People cannot be expected to follow guidelines and rules unless you tell them what they are. The acceptable use policy is used to inform people of what is, and what is not, expected of them. The misuse of computer equipment and information can have legal, regulatory and repetitional consequences for the organisation.
Yes. It is a key document in the protection of the organisation. Often part of the HR processes of onboarding it is also embedded in the culture of the organisation and resigned up to annually.
A free example ISO 27001 acceptable use policy PDF can be found at High Table: The ISO 27001 Company.
It can. It depends on the organisation. The use of computer equipment for personal use can be included with the rules and limits set and clearly explained. There is rarely if ever a case for the personal use of information and data.
The acceptable use policy covers what is and what is not allowed by employees when it comes to using the companies asset such as software, hardware, premises.
If you break the acceptable use policy first you would investigate why it happened. You would raise and incident and corrective action and follow the process. It maybe that the outcome of that process is to engage with HR to activate your internal disciplinary process.
You write the policy based on the needs of the business and the employee. Then you review and approve the policy by senior management and HR. Then you communicate the policy to all staff and get evidence that they have accepted the policy. You would include the policy in your annual communication plan and your annual information security training and awareness.
You create the acceptable use policy in a word processor such as Microsoft Word or Google Docs.
No. Computer use and email use form part of the normal acceptable use policy
An AUP policy is an acceptable use policy. It is another name for the same thing.
Stuart Barker
ISO 27001 Ninja
Stuart Barker is a veteran practitioner with over 30 years of experience in systems security and risk management. Holding an MSc in Software and Systems Security, he combines academic rigour with extensive operational experience, including a decade leading Data Governance for General Electric (GE).
As a qualified ISO 27001 Lead Auditor, Stuart possesses distinct insight into the specific evidence standards required by certification bodies. His toolkits represent an auditor-verified methodology designed to minimise operational friction while guaranteeing compliance.

- MSc Security
- ISO 27001 Lead Auditor
- 30+ Years Exp
- Ex-GE Leader