ISO 27001 Information Security Policy Template

The headline governance policy required for ISO 27001 certification. Authored by ISO 27001 Lead Auditor Stuart Barker, this audit-ready Information Security Policy Template in Microsoft Word (.docx) sets your management approach, executive commitment, and high-level control framework in plain English.

  • Instant Download: Editable Microsoft Word format (.docx)
  • Audit-Ready: Fully aligned with ISO 27001:2022 (Clause 5.2 & Control A.5.1), NIS2, DORA, and GDPR
  • Includes Leadership Statement: Pre-written Chief Executive Statement of Commitment and policy governance rules
  • Fast Deployment: Add your logo, brand names, review marked sections, and deploy in under 1 hour
  • 100% Human Authored: Written entirely by Stuart Barker. Not generated, edited, or polished by AI.
  • Auditor Verified: Built from real-world lead auditor experience.
  • Certification Body Proven: Formatted to satisfy accredited certification bodies first time.


$ 5.00

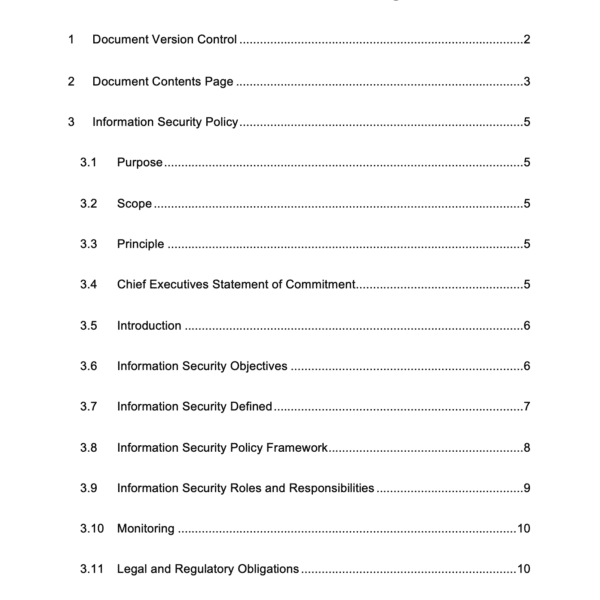
ISO 27001 Information Security Policy Page 1
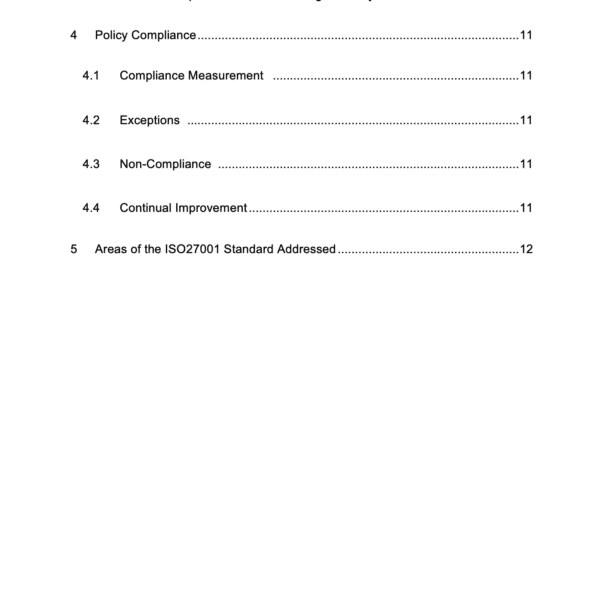
ISO 27001 Information Security Policy Page 2
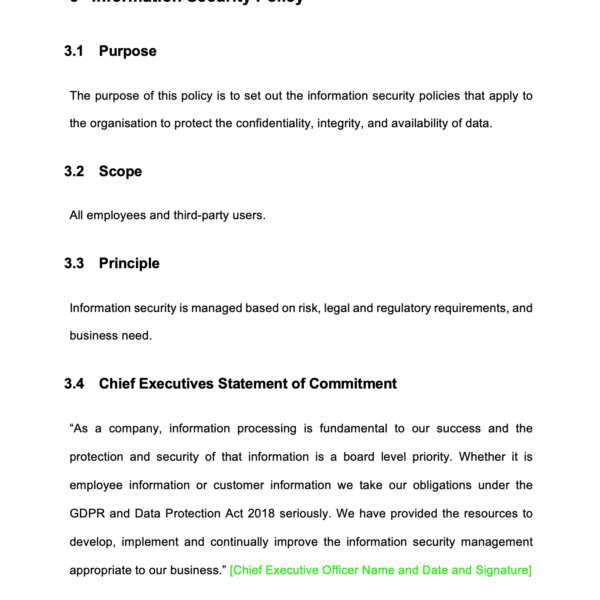
ISO 27001 Information Security Policy Page 3
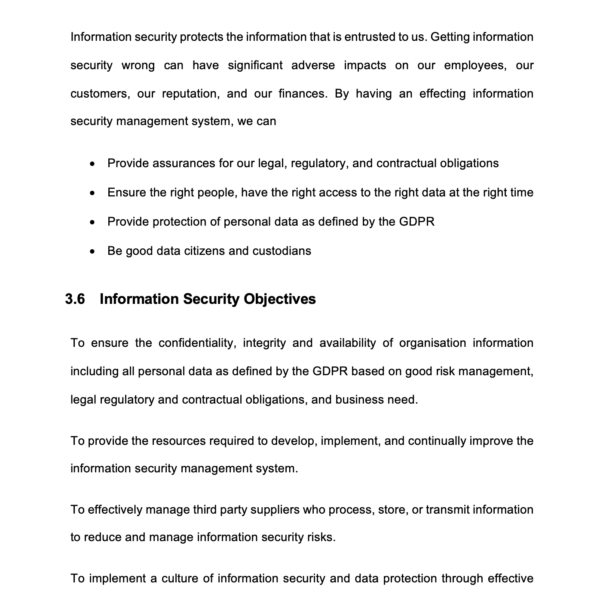
ISO27001 Information Security Policy Introduction Page
ISO27001 Information Security Policy Page 4
ISO27001 Information Security Policy Example 6
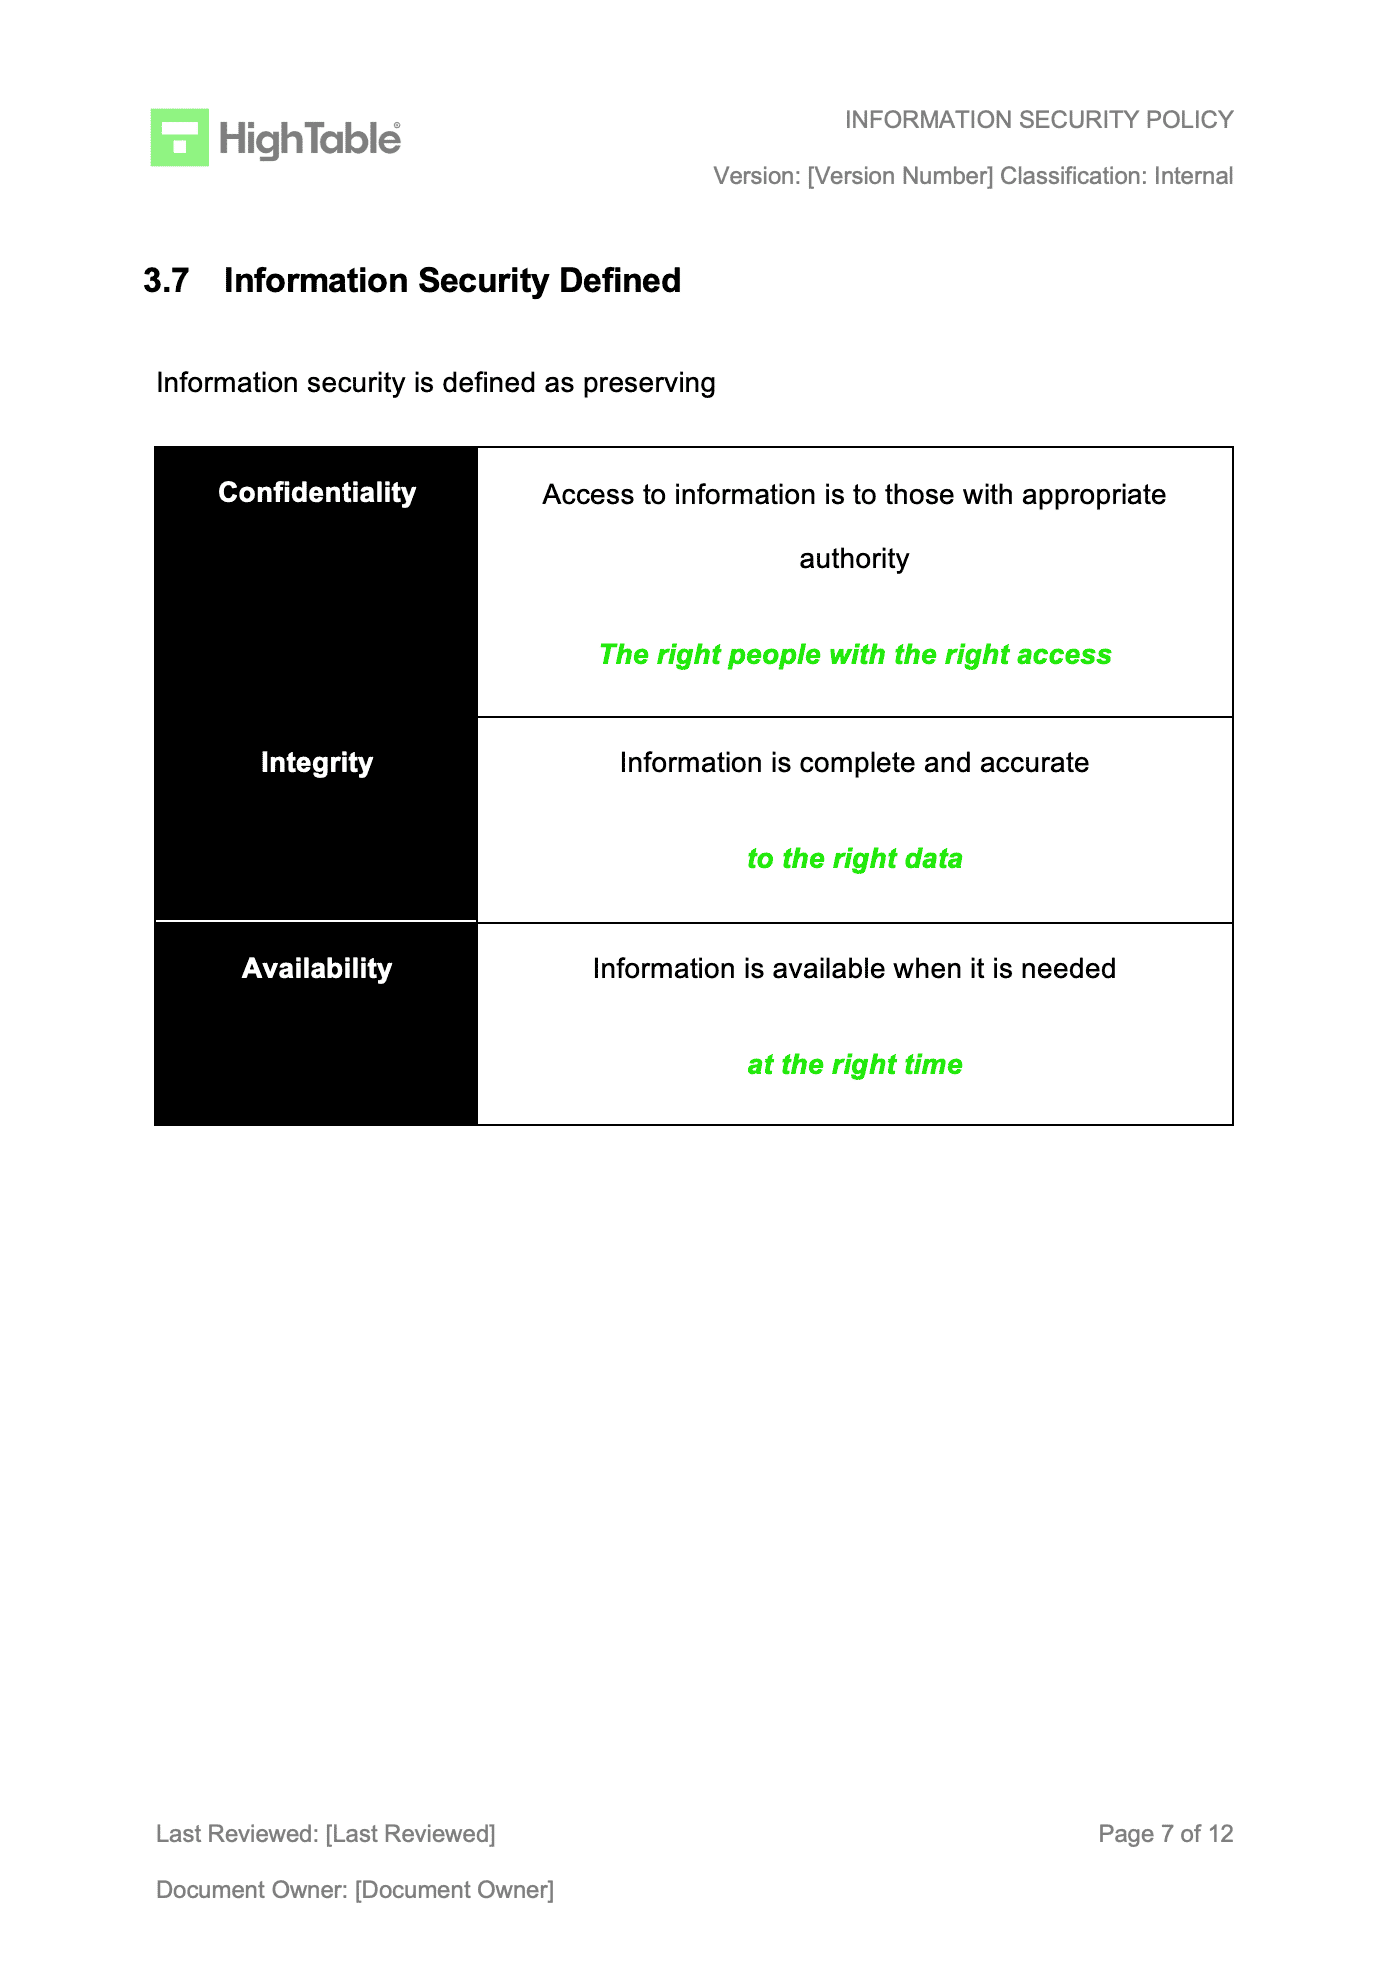
ISO27001 Information Security Policy Page 5
ISO27001 Information Security Policy Example 7
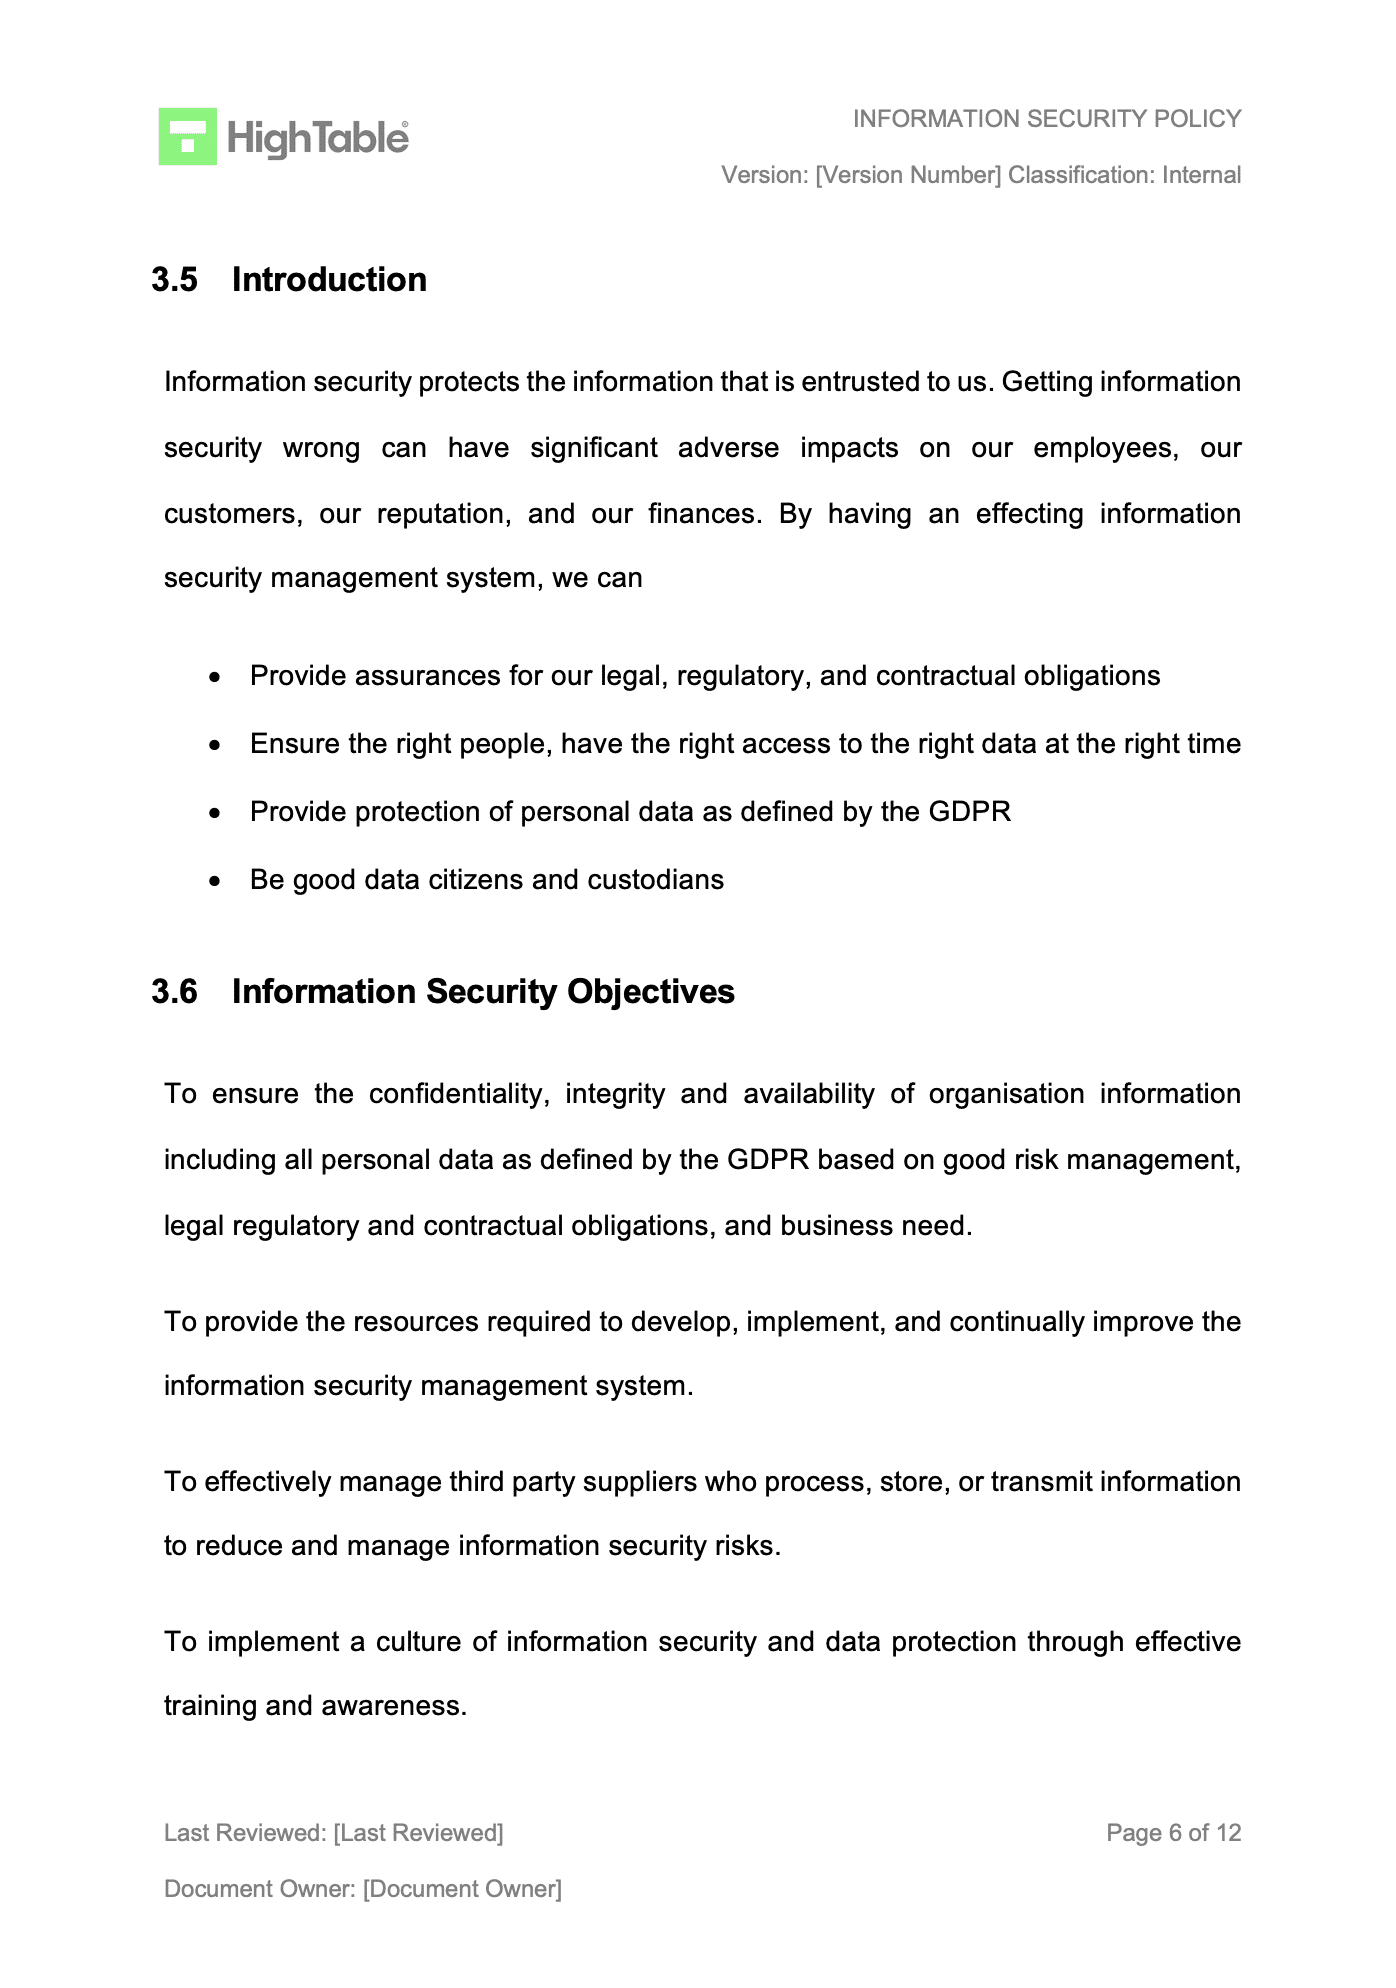
ISO27001 Information Security Policy Page 6


Why You Need a Headline Information Security Policy

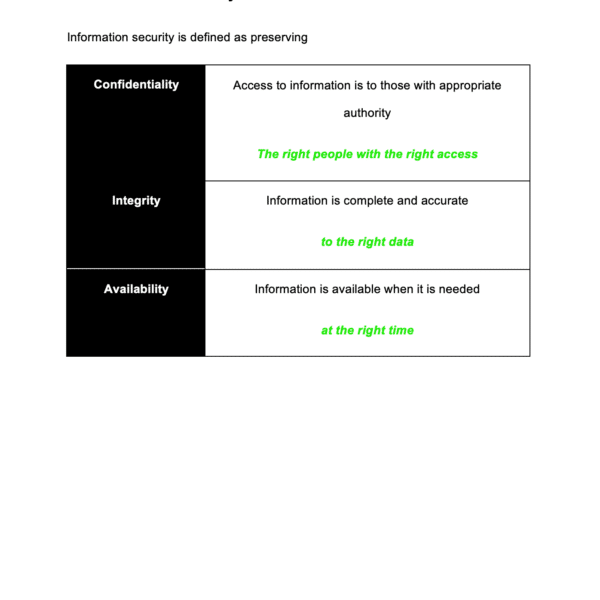
The Information Security Policy is the master cornerstone of your Information Security Management System (ISMS). It represents your leadership’s formal commitment to data confidentiality, integrity, and availability. Certification auditors require this document before reviewing any operational controls.

Rather than drafting complex corporate waffle from scratch, our template delivers a lean, practical framework that staff understand and auditors approve. Simply customise your scope and leadership roles, and you are ready to publish.

Why Auditors & Practitioners Choose This Template

  • Audit-Ready: Mapped directly to ISO 27001:2022 Clause 5.2 (Policy), Annex A 5.1 (Policies for Information Security), and Control 5.36.
  • Multi-Standard Compliance: Satisfies core governance requirements for GDPR, SOC 2, DORA, and NIS2.
  • Includes Implementation Assets: Comes with the Implementation Guide and ISO 27001 Implementation Checklist.
  • Fully Editable: Clean Microsoft Word (.docx) format ready to rebrand in under 60 minutes.

What’s Inside the Download?

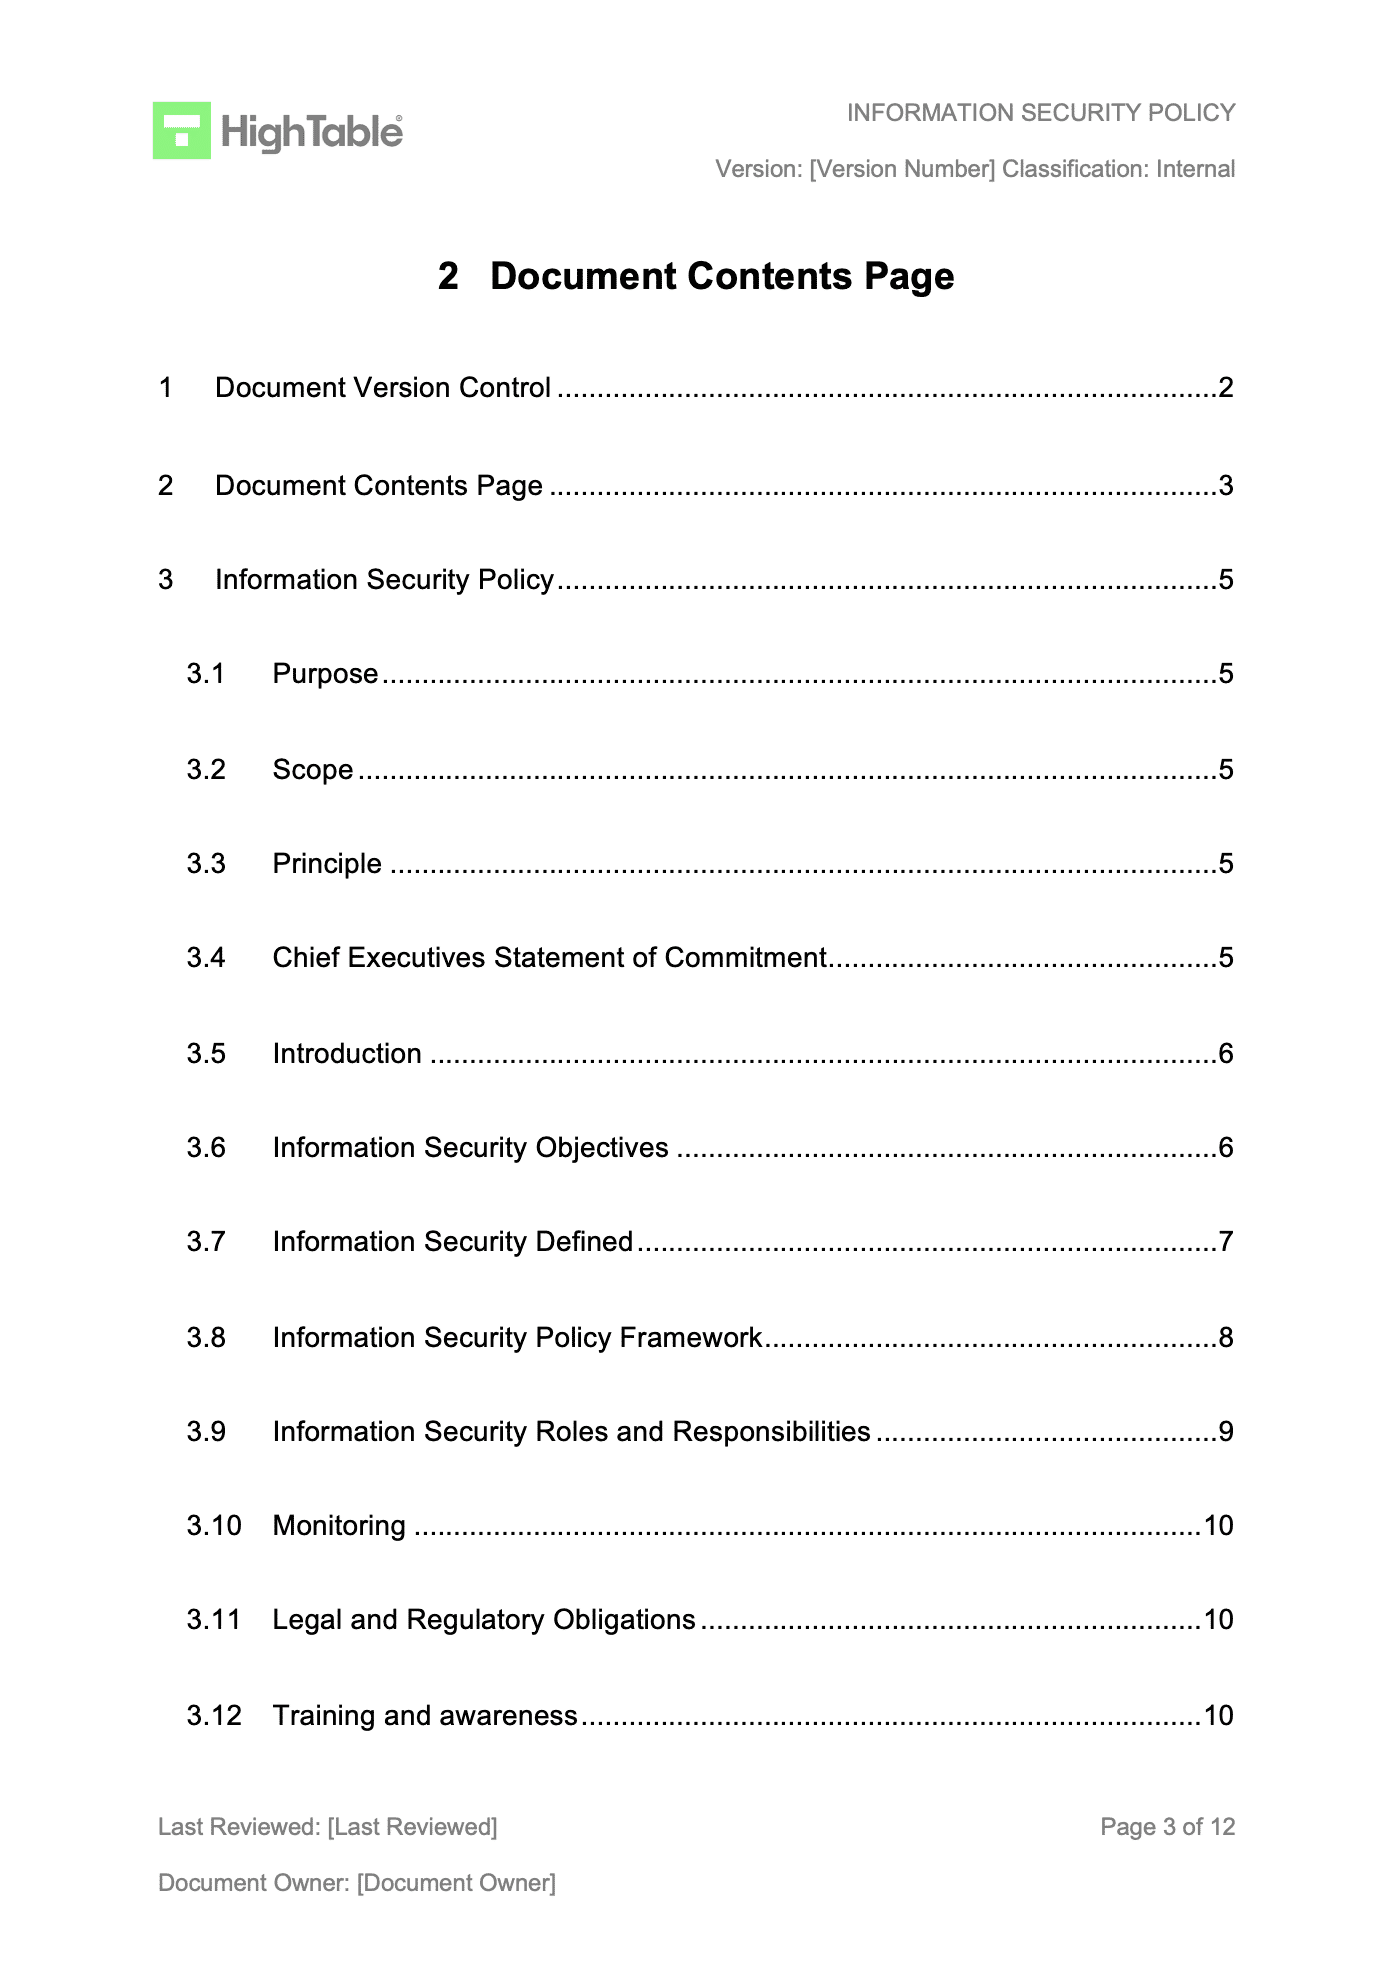
  • Document Version Control
  • Document Contents & Scope
  • Information Security Purpose
  • CEO Statement of Commitment
  • Information Security Objectives
  • Roles and Responsibilities Matrix
  • Legal & Regulatory Obligations
  • Training and Awareness Protocol
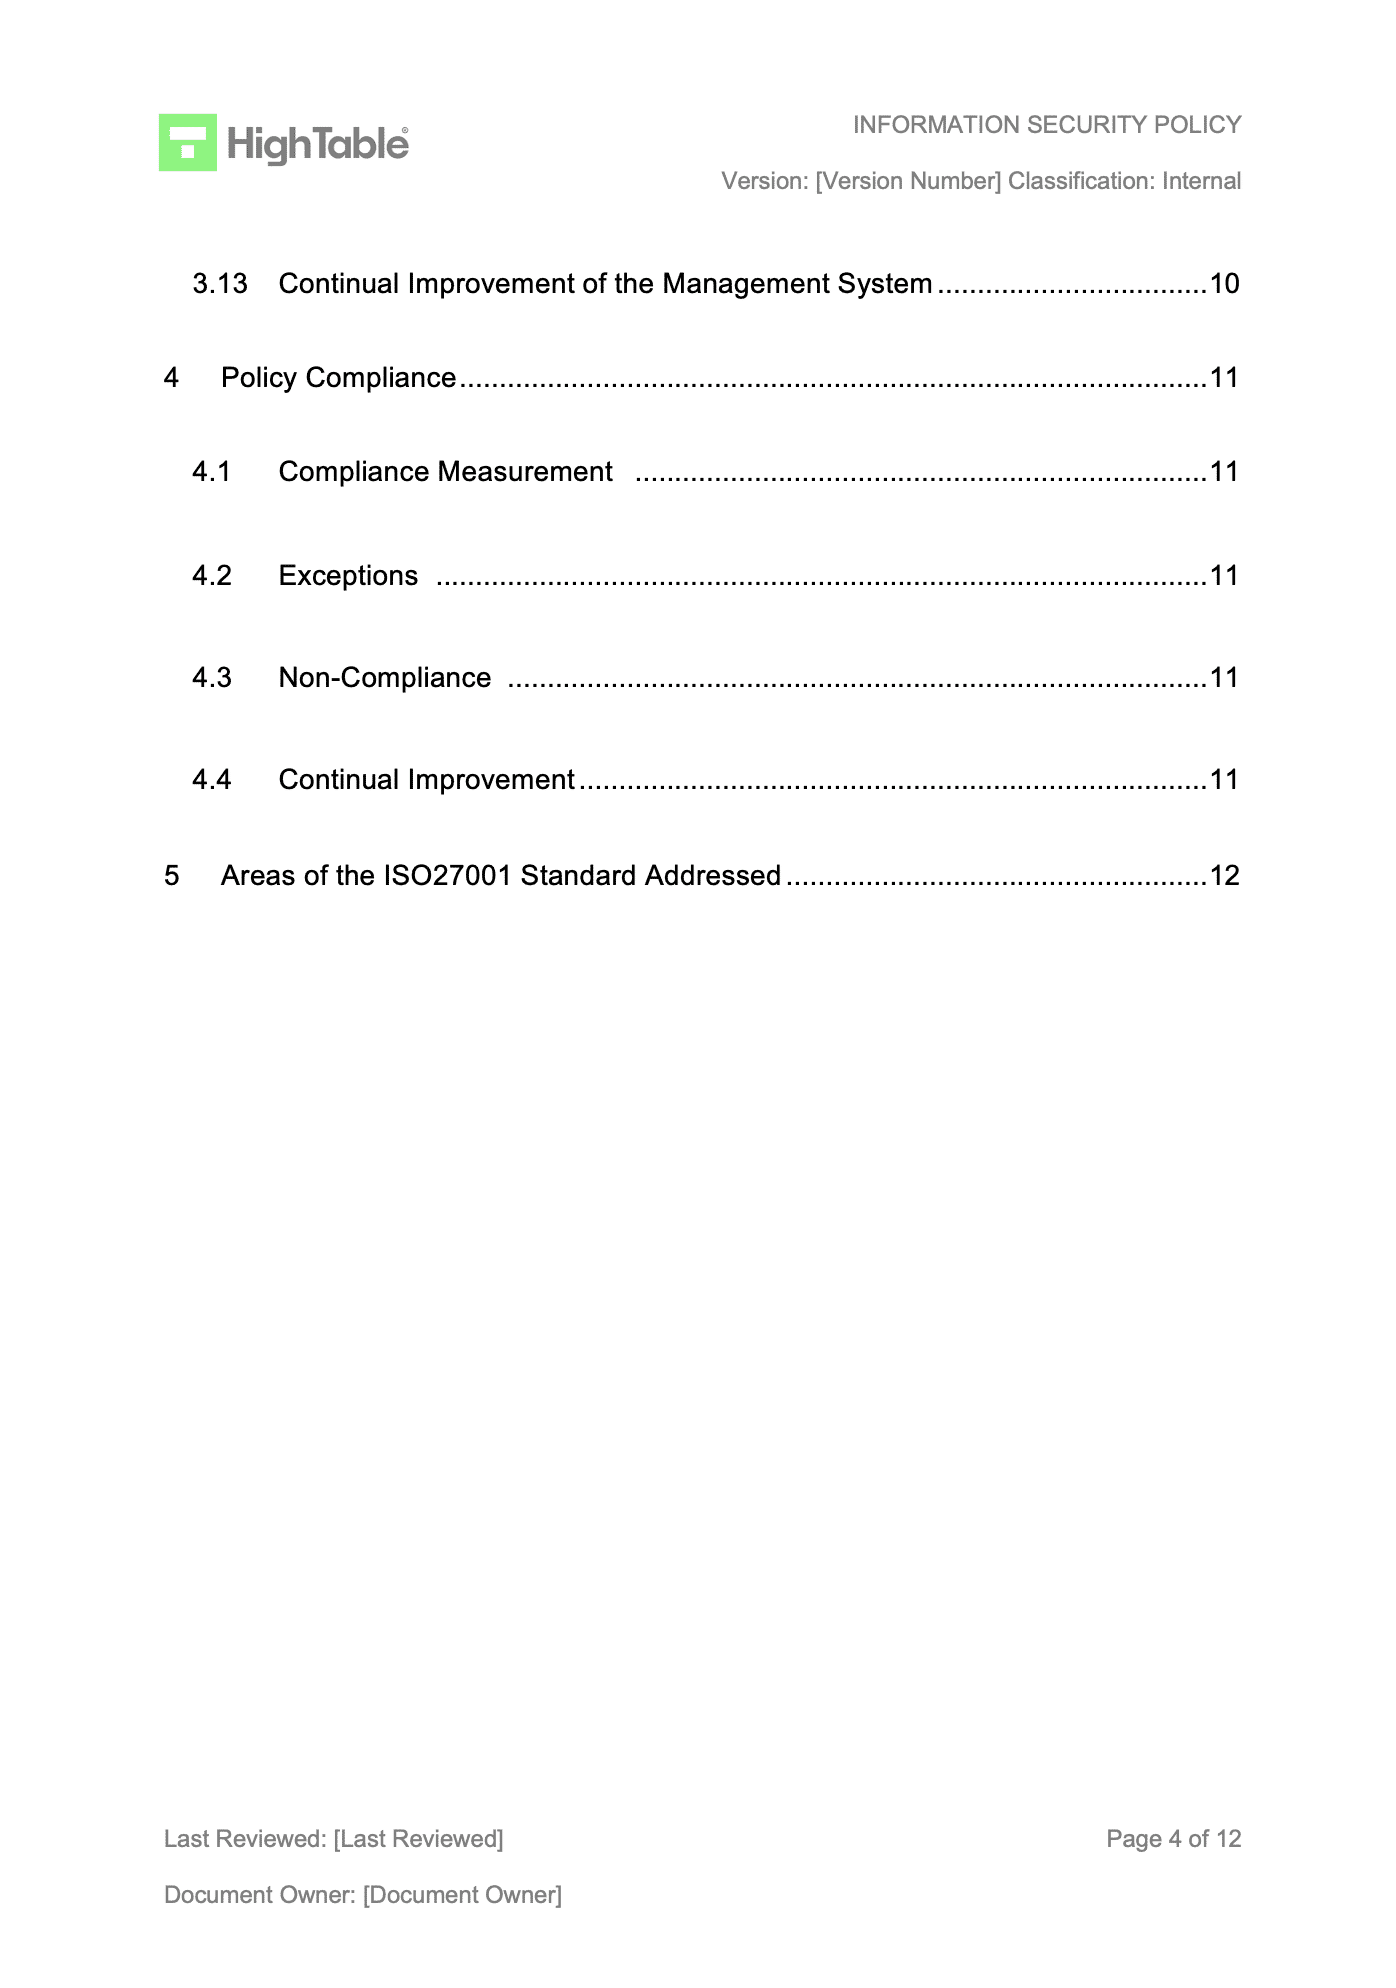
  • Policy Compliance & Measurement
  • Exceptions & Non-Compliance Rules
  • Continual Improvement Framework
  • ISO 27001 Control Mapping Summary
Shopping Basket
Scroll to Top