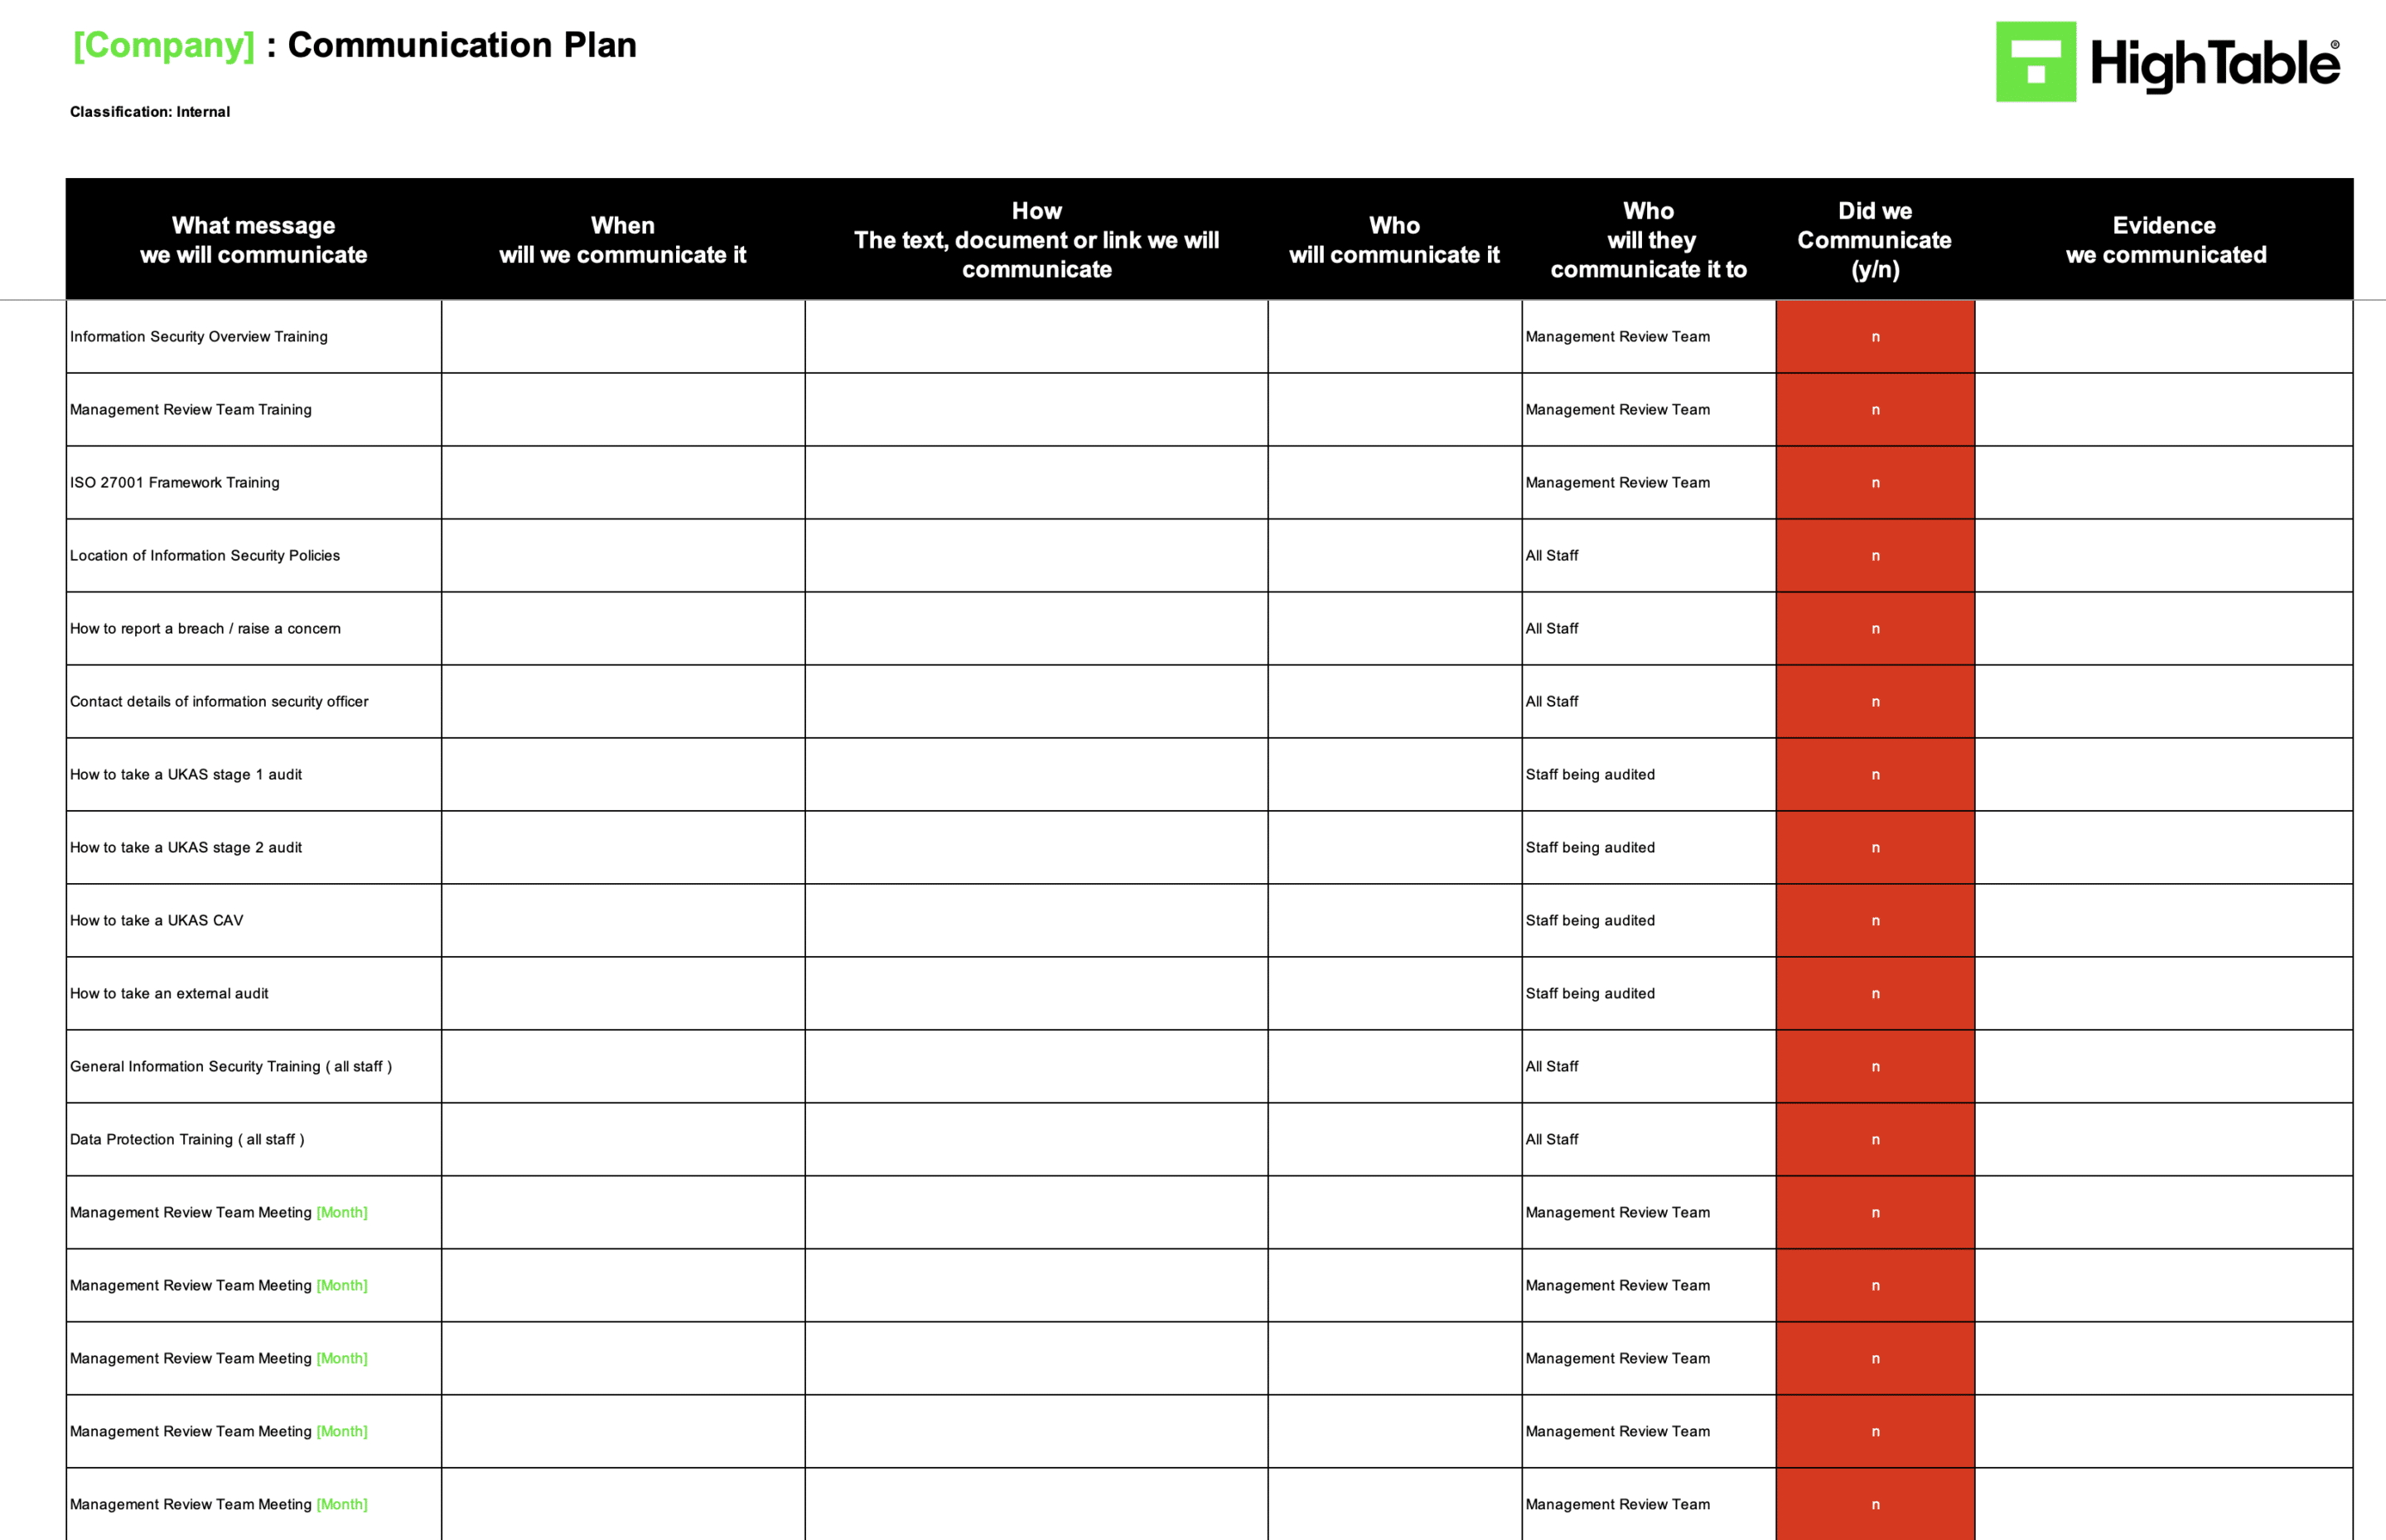
ISO 27001 certification isn’t just about technical controls; it’s about culture. Clause 7.4 requires that you proactively manage communications about your Information Security Management System (ISMS). If you cannot show auditors that you have communicated security expectations to the right people at the right time, you are at risk of a non-conformity.
Why You Need a Communication Plan
A formal communication plan removes ambiguity. It ensures that critical security messages like policy updates, incident reports, and awareness campaigns reach the intended audience effectively. Our template allows you to:
- Identify Stakeholders: Determine who needs to know what and when.
- Standardise Messaging: Ensure consistent communication across your organisation.
- Provide Audit Trails: Record communication activity as evidence of an operational ISMS.
ISO 27001 Communication Plan Template Example