

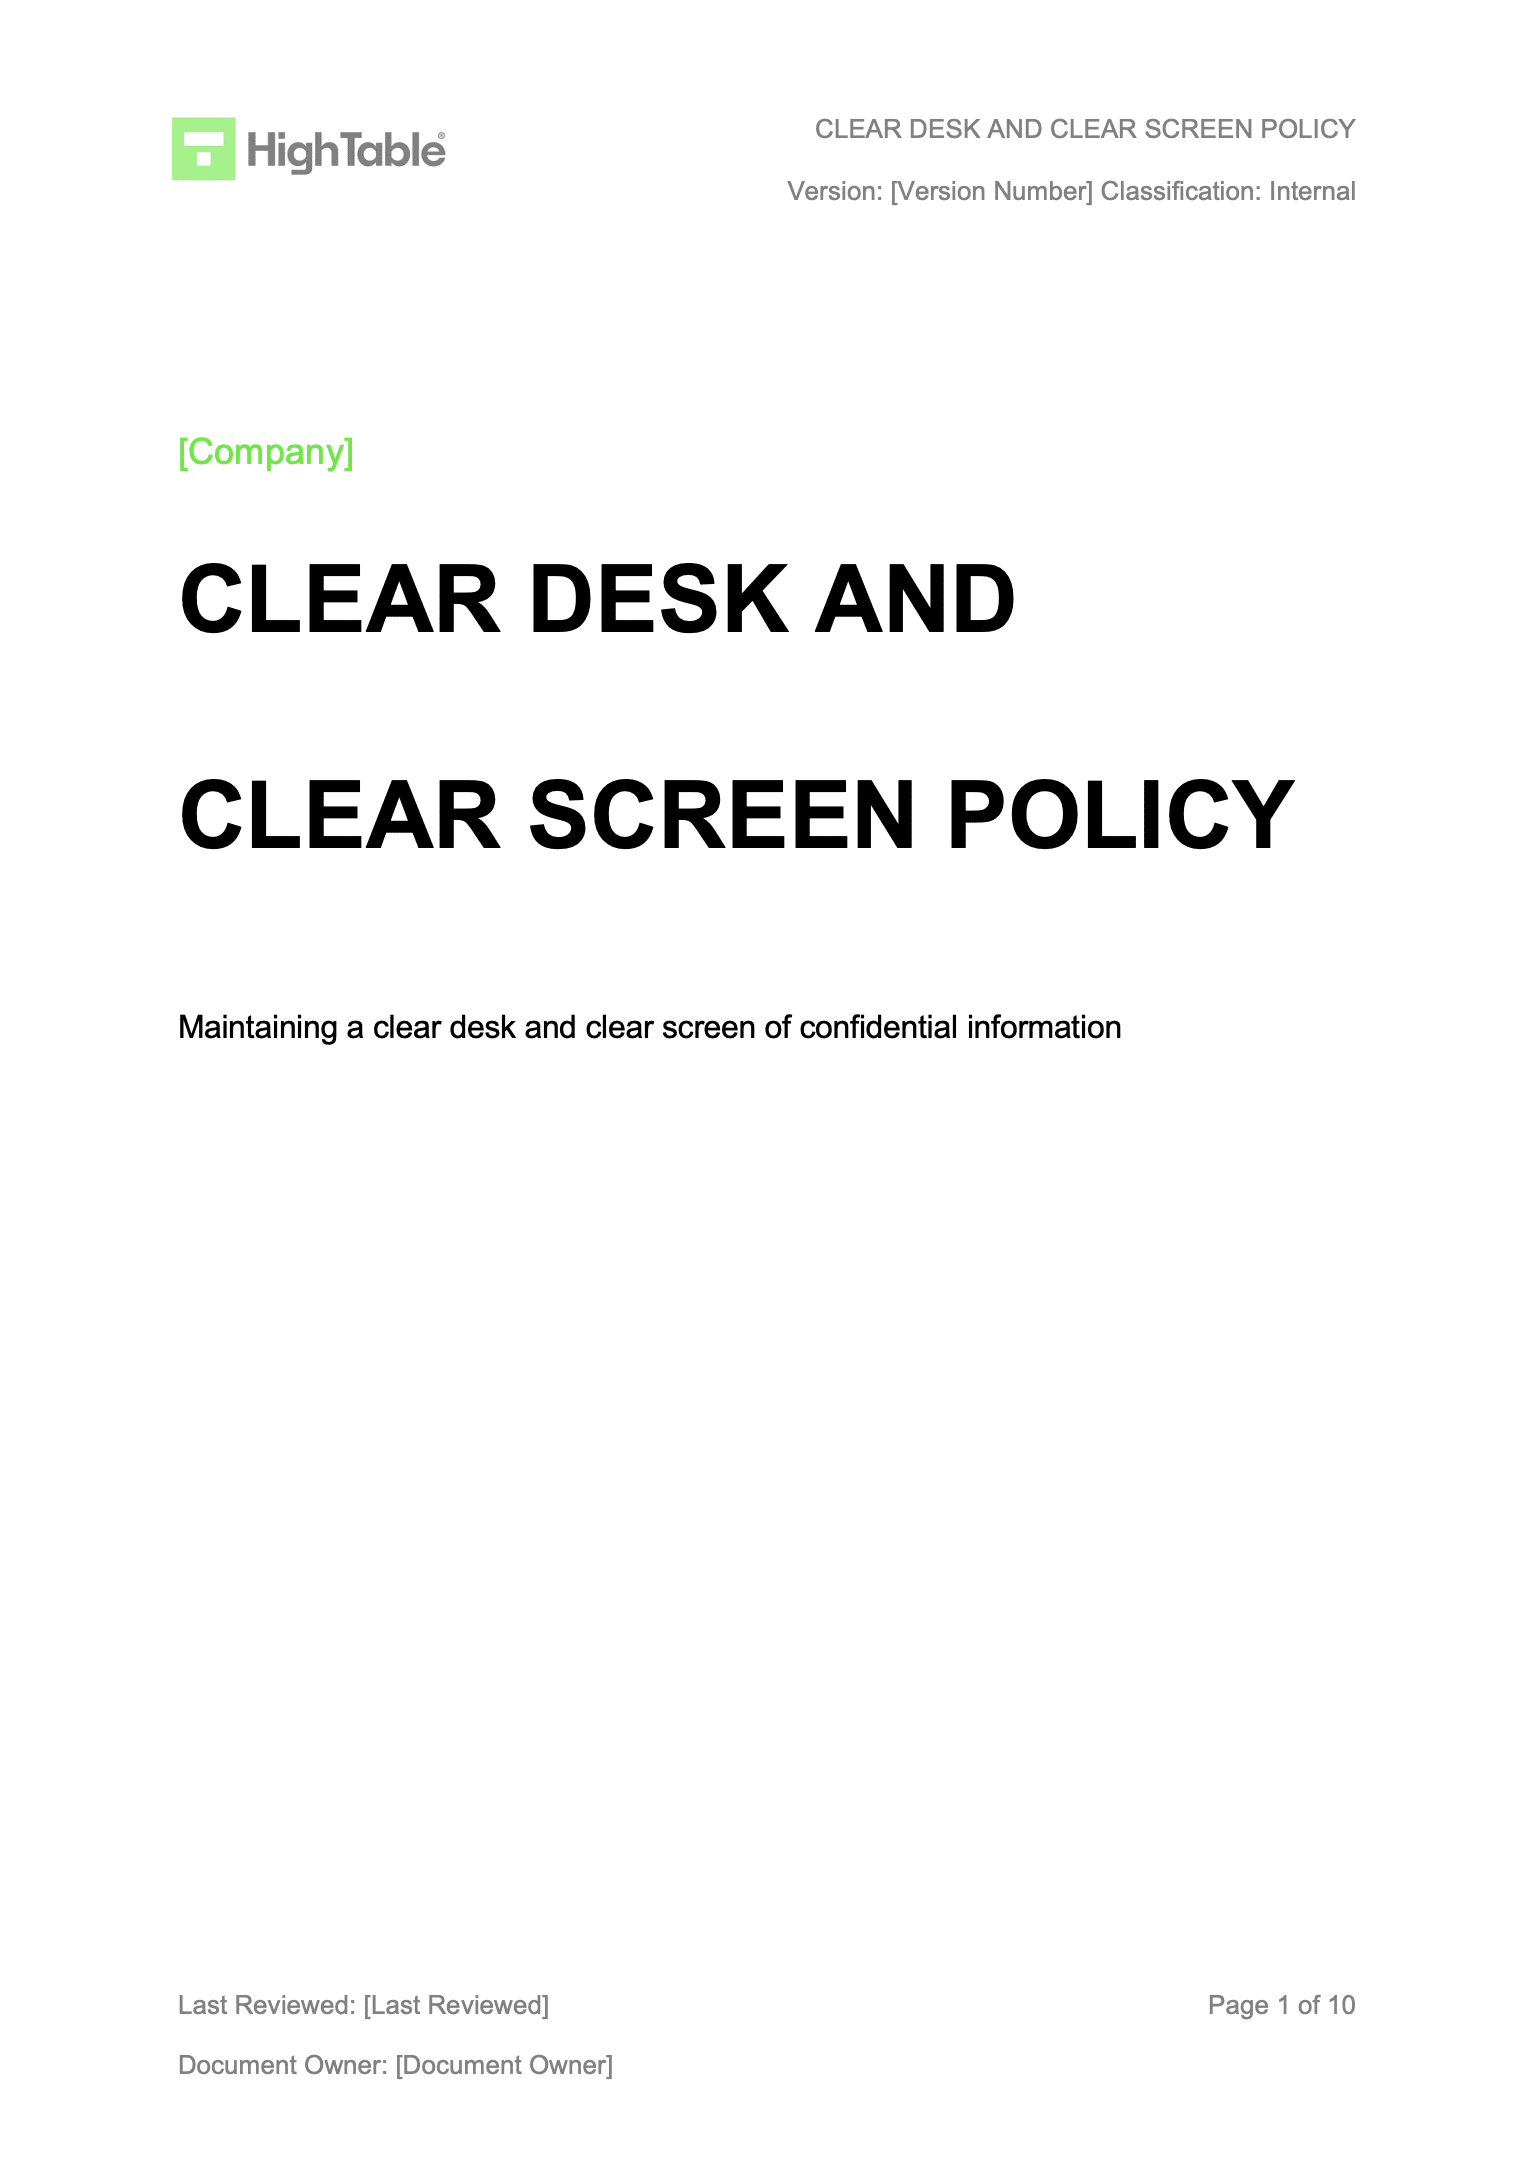
The Clear Desk and Clear Screen Policy protects your business from visual data breaches, data theft, and compliance audit failures. It sets simple, enforceable expectations for unattended devices, physical paperwork, and screens across both corporate offices and home working environments.
A required operational control under ISO 27001:2022, this document is ready to deploy immediately to staff, contractors, and certification auditors.
Why Start with Policy Templates Before Automation?
If you are an early-stage tech business, AI company, or startup with under 10 people, buying expensive compliance platforms like Vanta or Drata straight away is usually premature. You need to establish and understand your operational rules first.
- Define Your Operations: Put proven, real-world policies in place before configuring automated scanning tools.
- Keep Overhead Low: Avoid paying heavy recurring software fees while building out your core security baseline.
- Retain Total Ownership: Keep clean Word documents that your business controls independently of any vendor lock-in.
What the Template Covers
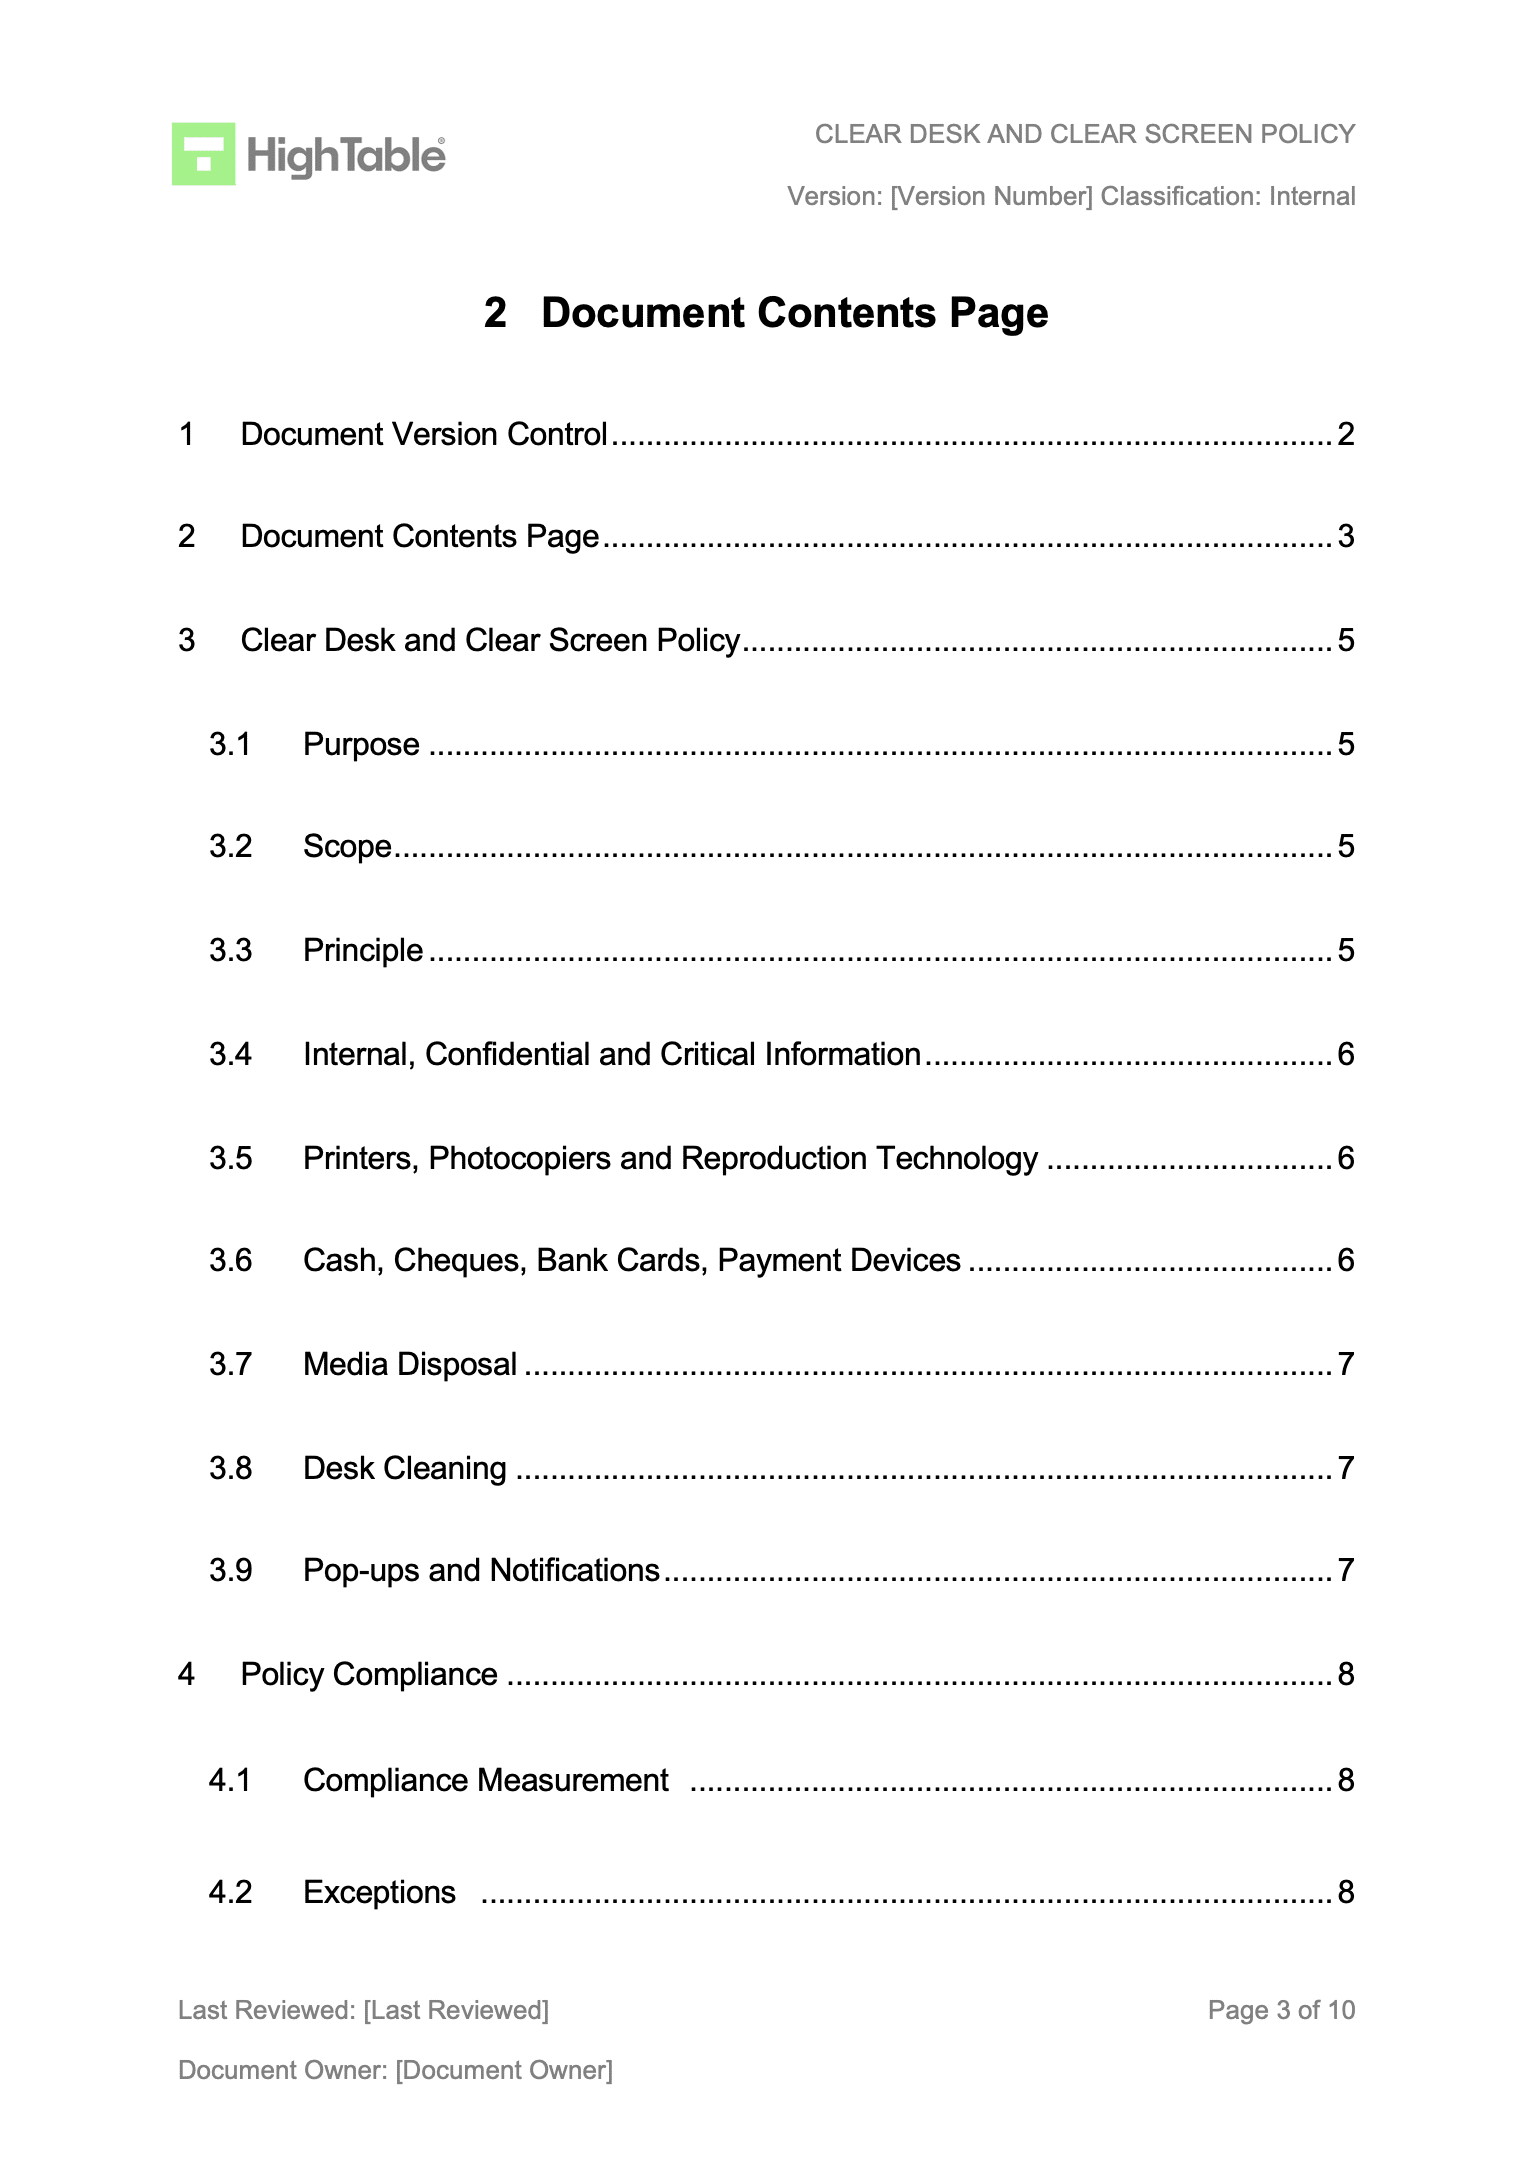
This template provides complete coverage for ISO 27001:2022 Control 7.7 without unnecessary jargon:
- Clear Screen Rules: Automatic screen locking, session timeouts, and password-protected screensavers.
- Clear Desk Controls: Physical document protection, locking away sensitive media, and clean whiteboard protocols.
- Remote and Home Working: Practical physical security rules when working in shared spaces, coffee shops, or home offices.
- Printing and Disposal: Secure printing practices and immediate shredding of sensitive paperwork.
- Compliance and Roles: Clear governance, exception workflows, and incident reporting steps.
ISO 27001 Clear Desk Policy Template FAQ
The Information Clear Desk Policy is in Microsoft Word format
No. The Clear Desk Policy Template is designed to be easy to implement and easy to configure. It comes with an easy to follow step by step guide. You are provided with a free hour of training if you need it.
It depends on what you are trying to achieve. It works as a stand alone policy but is designed to be part of a pack of information security policies that meet the needs of your business. We sell The ISO 27001 Policy Template Bundle at a significant discount.
The policy is sold stand alone as it serves a specific purpose and often people just want this one policy. When you deploy information security policies into your organisation you may not need all of the policies so we make them available individually. The benefits of having individual policies are: 1. They can be shared only with the people that need the information 2. They can be allocated an owner to update them 3. You can deploy only the policies you need. In addition the 2022 update to the ISO 27001 standard explicitly calls out having a headline policy and subordinate policies.
We estimate that on average it will take you less than 1 hour. The templates require information that you know so there is nothing complicated.
Payments are handled entirely through Stripe. They are very secure. We do not handle the payment transaction. We do not store, process or transmit your card holder data.