
In this guide you will learn how to implement ISO 27001 Clause 7.4 Communication and pass your audit from ISO 27001 Lead Auditor Stuart Barker – author of the ultimate ISO 27001 Toolkit.
Table of contents
- Purpose and Definition
- FREE ISO 27001 Clause 7.4 Training Video
- What is ISO 27001 Clause 7.4?
- The 5 W’s of ISO 27001 Communication
- How to implement ISO 27001 Clause 7.4
- 10 real world examples of ISO 27001 Communications
- ISO 27001 Communication Plan Example
- ISO 27001 Clause 7.4 Resources Templates
- How to pass the ISO 27001 Clause 7.4 audit
- Related Controls & Clauses
- ISO 27001 Clause 7.4 FAQ
- Further Reading
Purpose and Definition
The purpose of ISO 27001 clause 7.4 Communication is to make sure you have an information security communication plan and that you act on that plan.
The ISO 27001 standard defines ISO 27001 Clause 7.4 Communication as:
The organisation shall determine the need for internal and external communications relevant to the information security management system including: a) on what to communicate; b) when to communicate; c) with whom to communicate; d) how to communicate
ISO 27001:2022 Clause 7.4 Communication

ISO 27001 Starter Kit
Instant download of mandatory ISMS core policies and documentation. Verified by Lead Auditors and used by 5,000+ businesses worldwide to pass Stage 1 certification first time.
FREE ISO 27001 Clause 7.4 Training Video
What is ISO 27001 Clause 7.4?
ISO 27001 Clause 7.4 is communication and it focuses on sharing key aspects of the information security management system (ISMS) with relevant individuals. While certain communications are mandatory under the standard, others are highly recommended for a robust ISMS.
Communication can take various forms, including written and verbal methods. Organisation should leverage a diverse range of communication approaches tailored to their specific style, culture, and target audience. This variety is crucial for maximising effectiveness, as individuals respond differently to various communication styles.
Effective communication offers several key benefits:
- Enhanced Security: By informing individuals about risks and providing clear guidance, organisations empower them to make informed decisions, exercise sound judgment, and protect both themselves and the organisation.
- Fostering a Culture of Information Security: Training and awareness are fundamental to a strong information security posture. Effective communication, combined with training initiatives, significantly reduces information security risks and incidents.
ISO 27001 Toolkit
All the templates, tools, support and knowledge you need to do it yourself.
The 5 W’s of ISO 27001 Communication
There are numerous ways to communicate and raise awareness, and the most effective methods will depend on your company culture and available tools. Consider the approaches that have proven successful for your organisation and, where possible, retain evidence of your communications.
While email is a useful tool, other options include stand-up meetings, presentations at company-wide gatherings, and even bringing in external experts. There’s no single, universally applicable solution.
Regardless of the methods you choose, document them in your communication plan.
1. What to communicate
What you need to communicate is covered in the standard. You may choose to do the bare minimum for communication or to go a step further. The more you communicate the more you will enhance and improve your information security posture.
Key things to communicate include:
- Location of information security policies
- The information security policies themselves
- How to report an information security incident or breach
- Who is the primary contact for information security
- Information security training
- Information security management reviews that have a dedicated agenda of what needs to be discussed
- Information security measures and monitors
- Information security risks
- Information security treat intelligence
- Information security audit planning
- Continual improvement and changes to the information security management system (ISMS)
2. When to communicate
There’s no prescribed timeframe for all ISMS communications. While many, if not all, elements should be communicated at least annually, numerous aspects can, and often should, be communicated more frequently.
Examples of situations requiring communication include:
- Management Reviews – Every month, every three months or every six months
- Location of information security policies – every three months or every six months or annually
- The information security policies themselves – every three months or every six months or annually
- How to report an information security incident or breach – every three months or every six months or annually
- Who is the primary contact for information security – every three months or every six months or annually
- Information security training – ongoing or every three months or every six months or annually
- Information security measures and monitors – monthly
- Information security risks – monthly
- Information security treat intelligence – monthly
- Information security audit planning – every month, every three months or every six months
- Continual improvement and changes to the information security management system (ISMS) – monthly
3. With whom to communicate
Determining the appropriate recipients for communication involves understanding both individual needs and the requirements of the information security management system (ISMS). While some communications, such as training, will be organisation-wide, others will be targeted at specific groups, like management reviews, risk assessments, incident response teams, and threat intelligence units.
A stakeholder analysis is a valuable tool for identifying key stakeholders and their respective information needs. This process, while seemingly complex initially, becomes straightforward as the ISMS is implemented and its requirements are clarified.
4. Who should communicate
According to ISO 27001 Clause 7.4, the organisation must define who should communicate as a part of its information security management system (ISMS). This is a crucial step for ensuring accountability and clarity. The standard doesn’t prescribe specific job titles but rather requires the organisation to assign roles and responsibilities for communication. For example, a senior manager might be responsible for communicating policies to the entire staff, while a specific department head handles updates relevant to their team. It’s essential to document these roles to ensure everyone knows what is expected of them, from senior management to every employee.
5. How to communicate
Organisations typically employ a variety of communication methods. Common approaches include meetings (team meetings, company updates, quarterly reviews, and personnel reviews), email, and instant messaging platforms. Company bulletin boards, such as SharePoint or Confluence, are also frequently used.
Training itself is a form of communication, and the chosen delivery method (face-to-face, webinar, or via dedicated training tools) impacts how information is conveyed.
Formal communications, such as legal contracts and agreements with staff and third parties, also play a significant role.
When determining the most effective communication strategies, organisations should consider their existing culture and established communication channels. Consulting with HR is highly recommended to gain insights into preferred communication approaches.
How to implement ISO 27001 Clause 7.4
In this step by step implementation checklist to ISO 27001 resource I show you, based on real world experience and best practice, the best way to implement Clause 7.1.
When planning communications take into account the following:
- what to communicate
- when to communicate
- with whom to communicate and
- how to communicate
To satisfy the requirements of ISO 27001 Clause 7.4, organisations must transition from informal updates to a structured communication framework. This implementation guide outlines the lifecycle of security communications, ensuring that every stakeholder receives the right information at the right time through validated channels.
1. Provision a Formal Communication Plan
Document a central communication plan that serves as the authoritative record for all ISMS-related interactions. This plan must be integrated with your Asset Register to ensure data owners are correctly identified.
- Define the specific content: precisely what information is being communicated.
- Establish the timeline: exactly when the communication occurs.
- Identify the audience: with whom the information is shared, including internal staff and external third parties.
- Authorise the sender: specify who is responsible for disseminating the message.
- Formalise the transmission: document the processes and secure channels used for the communication.
- Retain evidence: maintain logs or signed acknowledgments as proof of communication for audit purposes.
2. Execute Security Communications During Onboarding
Formalise the entry process for new staff and third parties by providing immediate clarity on security expectations and individual responsibilities.
- Distribute essential ISMS documentation, including relevant policies and the employee handbook, via secure digital portals.
- Conduct face-to-face or interactive sessions to explain the organisation’s security approach, identifying key personnel and incident reporting procedures.
- Enrol all new hires in mandatory security awareness and GDPR training, ensuring Multi-Factor Authentication (MFA) is active on training accounts.
- Verify comprehension by requiring signed acknowledgments of completion to be stored in personnel records.
3. Manage Ongoing Communications Throughout the Year
Maintain a continuous flow of security information based on evolving risks, business needs, and the specific requirements of the ISO 27001 standard.
- Address emerging threats, such as phishing or risks associated with remote working, through targeted ad-hoc briefings.
- Schedule regular Management Review Meetings to communicate ISMS performance and resource requirements to senior leadership.
- Utilise internal communication channels to provide updates on technical maintenance windows or changes to security controls.
4. Conduct Annual Training and Policy Refreshers
Audit and renew the organisation’s collective security knowledge on an annual basis to ensure compliance remains robust and skills do not stagnate.
- Mandate the completion of general information security awareness and data protection training at least once per year.
- Review and re-distribute core security policies to ensure all stakeholders are aware of the latest version-controlled updates.
- Document annual participation rates as a key metric for the Management Review process.
5. Formalise Offboarding and Termination Communications
Revoke access and communicate remaining legal and contractual obligations to individuals ending their employment or engagement with the organisation.
- Conduct exit interviews to explicitly reiterate ongoing contractual obligations regarding confidentiality and intellectual property.
- Ensure the Rules of Engagement (ROE) for departing staff are followed, particularly regarding the return of assets and the cessation of system access.
- Update the Asset Register and IAM roles immediately to reflect the change in the individual’s status.
6. Update Protocols for Continual Improvement
Refine the communication framework periodically to respond to identified issues, audit findings, and changes in the threat landscape.
- Revise the communication plan following any significant security incident to improve response coordination.
- Incorporate feedback from stakeholders to ensure communication channels remain effective and accessible.
- Ensure all updates are reflected in your ISO 27001 Toolkit to maintain a single source of truth for the ISMS.
Check Your Work?
You built it yourself. Maybe with AI. But will it pass the audit?
Don’t gamble – let an ISO 27001 Lead Auditor check your work.
10 real world examples of ISO 27001 Communications
There are common communications that are going to happen as part of your project’s implementation and throughout the year, the annual cycle of your information security management system.
The following are 10 real world examples of ISO 27001 Communications:
| Communication Category | Implementation Requirement and Example |
|---|---|
| General Awareness | Provision of information security overview training for all staff members. |
| Role-Specific Training | Tailored training for employees on information security requirements within their specific roles. |
| Leadership Engagement | Specialised training for the management team regarding their strategic roles and responsibilities. |
| Framework Education | Educating staff on the ISO 27001 framework and how it governs organisational data protection. |
| Policy Accessibility | Communicating the exact location and access methods for the ISO 27001 policies. |
| Incident Reporting | Providing clear instructions on the process for raising a security incident if a breach or issue occurs. |
| Governance Structure | Formally identifying the individual or role with ultimate responsibility for information security in the organisation. |
| Audit Preparedness | Instructing relevant personnel on how to conduct themselves and provide evidence during an internal or external audit. |
| Technical Security | Delivering technical security training to specialised staff (e.g., IT and Development) regarding secure configurations. |
| Compliance Updates | Regular updates on changes to the legal, regulatory, or contractual security landscape. |
ISO 27001 Communication Plan Example
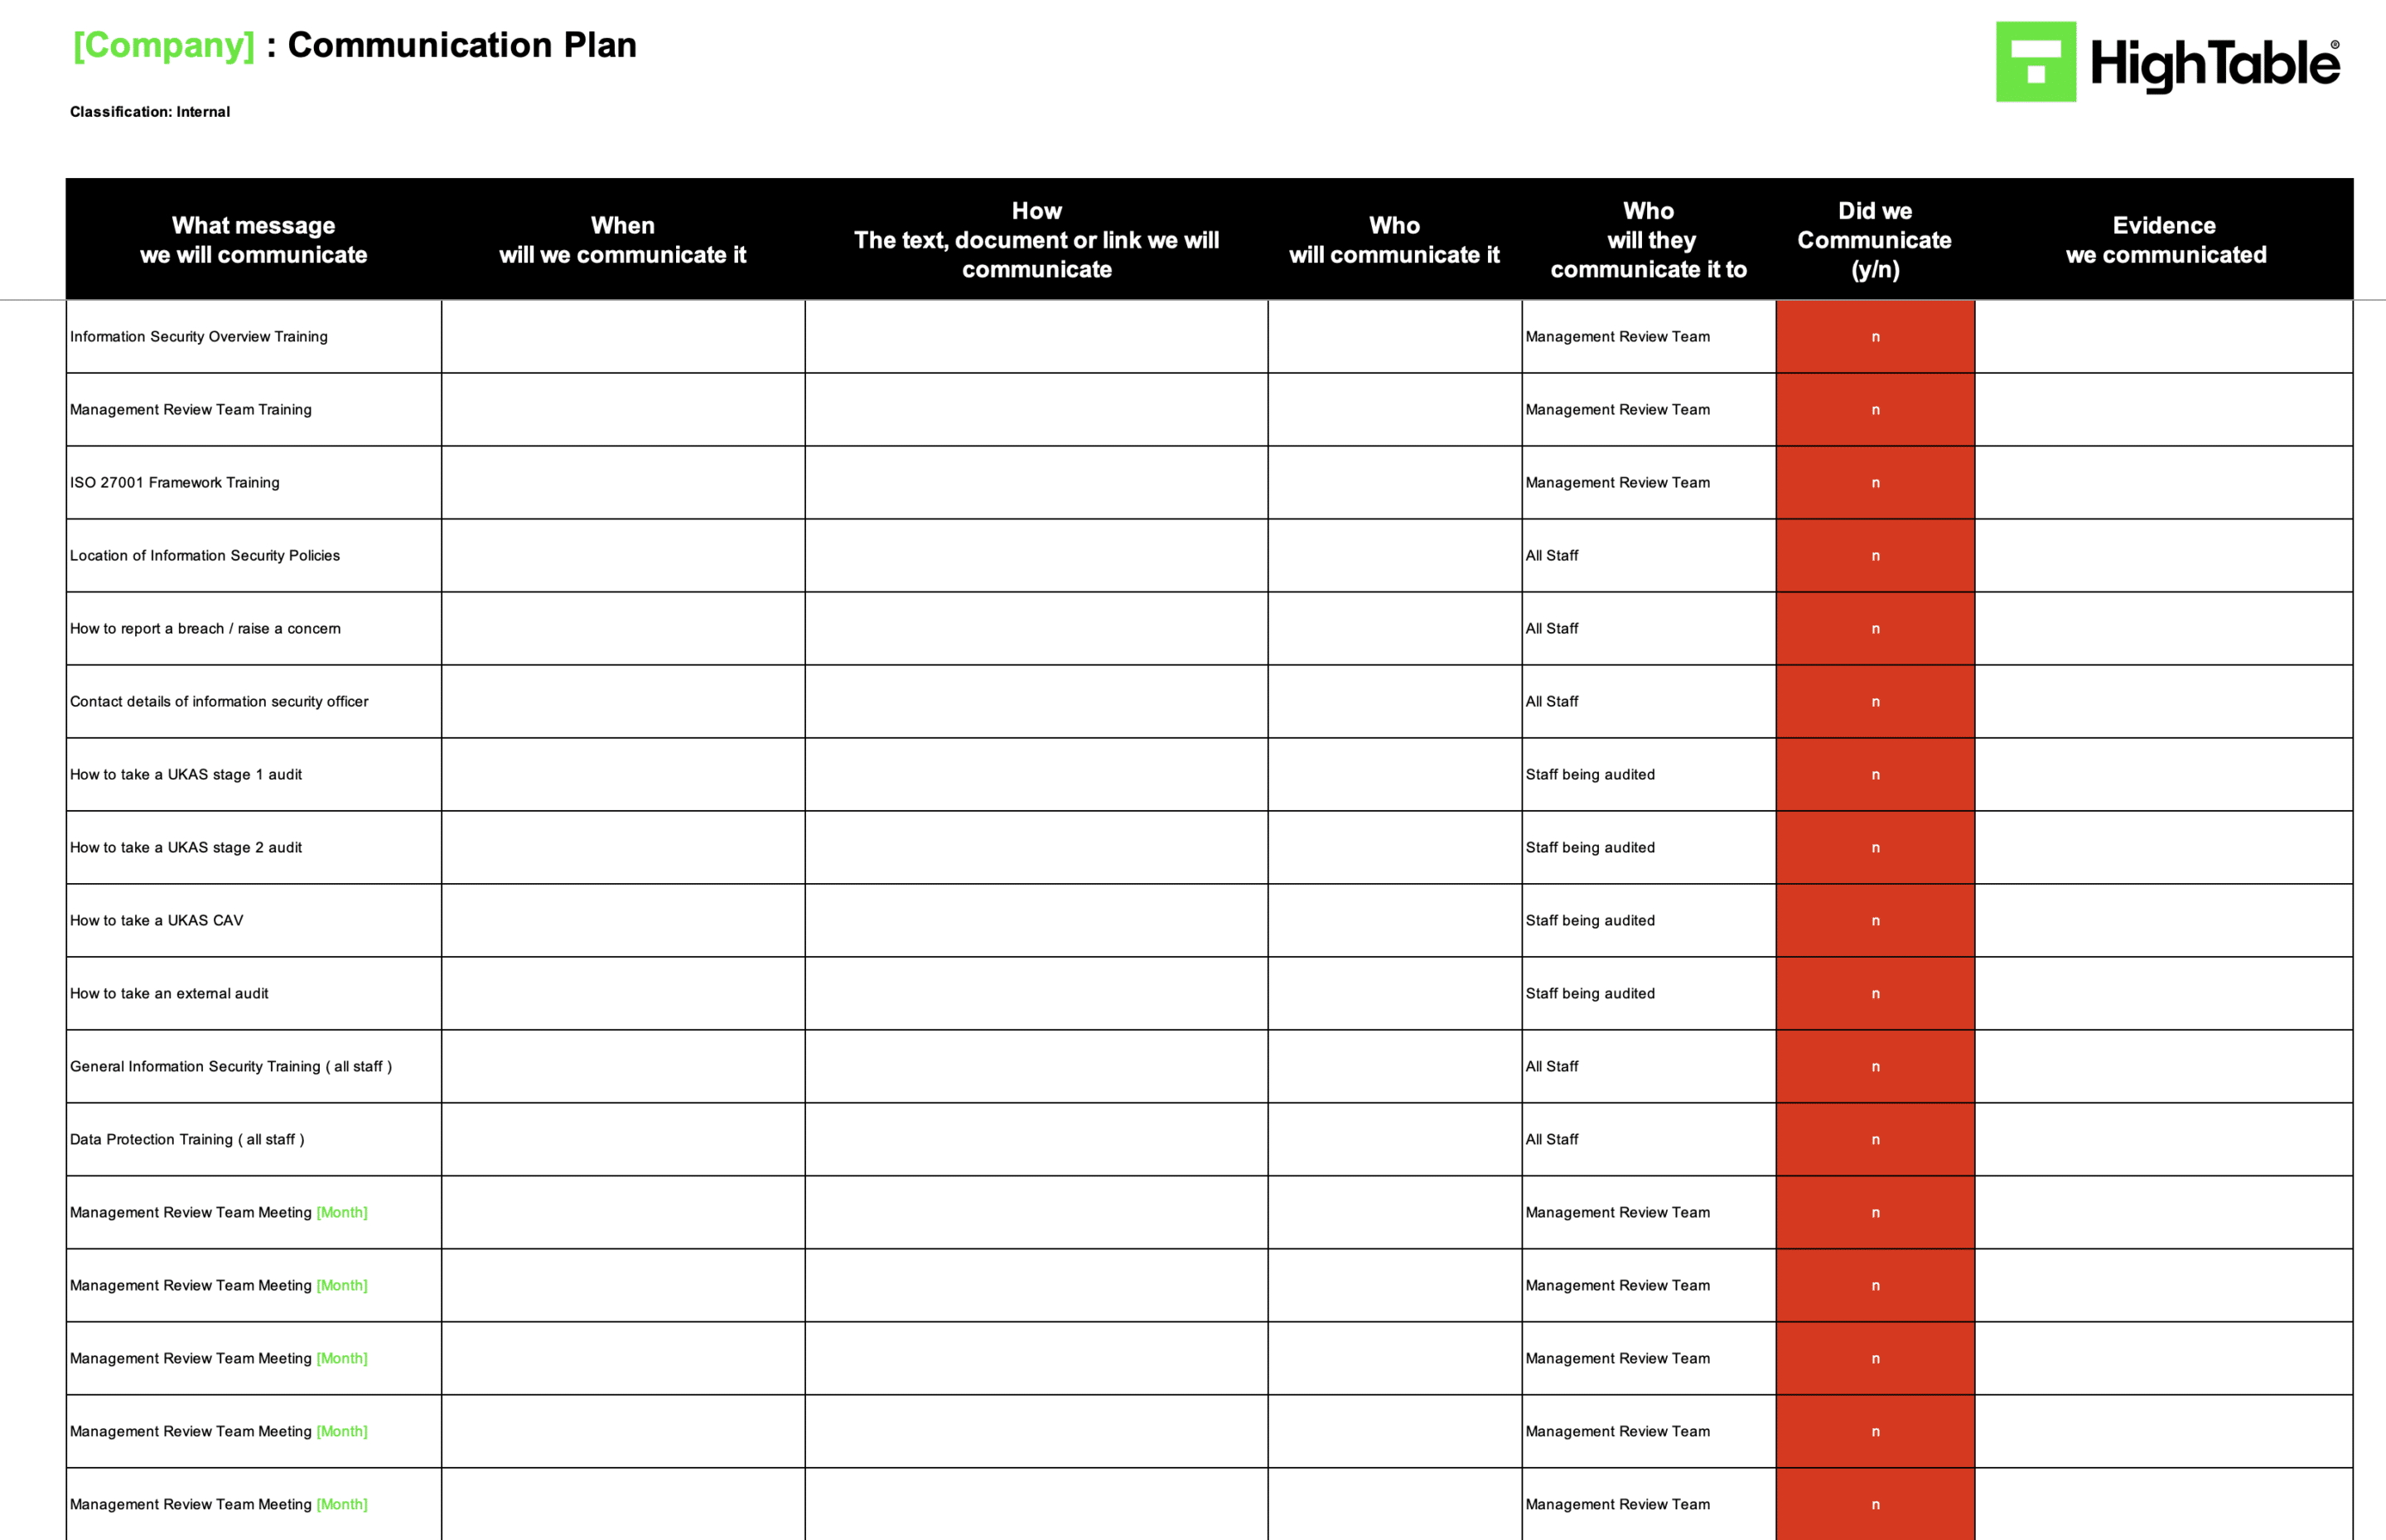
A communication plan is a simple document and this is a practical example of an ISO 27001 communication plan:
ISO 27001 Clause 7.4 Resources Templates
For ISO 27001 Clause 7.1 Resources the entire ISO 27001 toolkit is relevant but in particular the following templates directly support this ISO 27001 clause:
ISO 27001 communication plan template
The ISO 27001 communication plan template is the central document that guides how your organisation shares information, and it’s essential for providing auditors with the evidence they need.
ISO 27001 training and awareness policy template
Your ISO 27001 training and awareness policy is the core document that builds a security-conscious culture, ensuring everyone understands and fulfils their role in protecting the organisation
How to pass the ISO 27001 Clause 7.4 audit
To pass an audit of ISO 27001 Clause 7.4 Communication, you are going to:
- Understand the requirements: Recognise that Clause 7.4 is a mandate for structured, documented information security messaging.
- Establish the 5 Ws: Formally document What is communicated, When it happens, With Whom it occurs, Who performs it, and How the process is effected.
- Map Stakeholders: Identify all internal and external “Interested Parties” and their specific communication needs.
- Create a Communication Matrix: Use a central document to track all recurring and ad-hoc security communications.
- Verify Delivery: Ensure you can provide objective evidence (logs, minutes, sent items) that communications actually took place.
- Review Effectiveness: Demonstrate that you evaluate whether your messages are being understood and acted upon.
Related Controls & Clauses
- No Silos: Communication shouldn’t happen in a vacuum. By linking Clause 7.4 to Incident Management (A 8.3) and Supplier Relationships (A 6.8), you ensure that your Communication Plan covers the high-risk areas that auditors scrutinise most.
- Evidence Efficiency: When you audit Clause 7.4, you are simultaneously gathering evidence for Awareness (7.3) and Management Responsibilities (A 5.4).
ISO 27001 Clause 7.4 FAQ
What are the ISO 27001:2022 Changes to Clause 7.4?
The 2022 update introduces minor simplifications to ISO 27001 Clause 7.4. It removes the explicit requirement of “who shall communicate,” replacing it with “how to communicate,” and eliminates the mandatory need to demonstrate the specific processes of communication. While streamlined, maintaining “who” and “process” remains best practice for audit readiness.
What is the main purpose of Clause 7.4?
The main purpose is to establish, implement, and maintain a robust communication process for the ISMS. This process determines what, when, with whom, and how to communicate regarding information security, ensuring that everyone from top management to external stakeholders is informed of their specific roles and responsibilities.
What are the key elements an organisation must define?
Organisations must explicitly define four key elements for all ISMS-related communications: What to communicate: e.g., security policies, incidents, and audit results. When to communicate: e.g., scheduled updates or immediate incident notifications. With whom to communicate: e.g., employees, customers, regulators, and suppliers. How to communicate: e.g., email, secure meetings, intranet, or formal reports.
Does Clause 7.4 require a formal, documented communication plan?
While ISO 27001 does not explicitly mandate a document titled “Communication Plan,” it requires organisations to maintain “documented information” about their communication processes. Utilising a communication matrix or plan is the most effective way to provide objective evidence of compliance to certification auditors.
Who are the “interested parties” mentioned in this clause?
Interested parties include any entity with a stake in the organisation’s information security. Internal parties encompass employees, management, and IT teams; external parties include customers, suppliers, regulators, auditors, and law enforcement. The organisation must determine and meet the specific communication needs of these groups.
How is Clause 7.4 related to other clauses like 7.2 and 7.3?
Clause 7.4 (Communication) acts as the delivery mechanism for Clause 7.2 (Competence) and Clause 7.3 (Awareness). While the other clauses define the required knowledge and skills, Clause 7.4 defines “how” that information is actually transmitted to the people who need it to maintain ISMS integrity.
What are some examples of what to communicate?
Typical examples of ISMS communications include updates to security policies, results of risk assessments, security awareness training modules, notifications of active security breaches, and periodic reports on the overall performance and health of the ISMS.
How should an organisation handle communication about security incidents?
The communication process must include predefined procedures for reporting incidents. This involves internal reporting to the incident response team and, where necessary, external communication to affected customers or regulatory bodies (such as the ICO) within legal timeframes like the GDPR 72-hour window.
What kind of evidence do auditors look for to confirm compliance?
Auditors look for objective evidence that the communication process is followed and effective. Examples include communication logs, sent-folder archives of newsletters/emails, minutes from Management Review Meetings, training attendance records, and documented feedback from stakeholders.
What is the difference between internal and external communication?
Internal communication focuses on sharing security details with employees and contractors within the organisation to maintain operational security. External communication involves sharing necessary information with parties outside the organisation, such as regulators or partners, often governed by stricter legal or contractual requirements.
How can an organisation ensure its communication is effective?
Effectiveness is ensured by confirming the message was received and understood, not just sent. Organisations should tailor messaging to the audience, use diverse channels, provide feedback mechanisms (like quizzes or surveys), and regularly review the communication plan’s performance against ISMS goals.
Further Reading
- How to conduct an ISO 27001 Management Review Meeting
- ISO 27001 Security Awareness Training Policy Beginner’s Guide
- Record Of Processing Activities (ROPA) Template
About the author
