
ISO 27001:2022 Annex A 8.32 (Change Management) is a mandatory compliance control requiring organizations to formally manage, test, and approve all modifications to information processing facilities, software systems, and the Information Security Management System (ISMS).
In this guide, you will learn how to implement Annex A 8.32 correctly – establishing change logs, risk assessments for hotfixes, and verifiable audit trails – with guidance from Lead Auditor Stuart Barker, founder of High Table and author of the ISO 27001 Toolkit.
Table of contents
- Key Takeaways
- ISO 27001 Annex A 8.32 Purpose & Definition
- Change management guidelines
- How to implement ISO 27001 Change Management (Annex A 8.32)
- 1. Formalise the Change Management Policy and Scope
- 2. Establish a Centralised Request for Change (RFC) Workflow
- 3. Conduct Technical Impact and Security Risk Assessments
- 4. Execute Testing, Validation, and Quality Assurance
- 5. Authorise and Deploy with Rollback Protocols
- 6. Perform Post-Implementation Review (PIR) and Logging
- ISO 27001 Annex A 8.32 Toolkit & Templates
- How to audit ISO 27001 Annex A 8.32
- Related ISO 27001:2022 Annex A Controls
- ISO 27002:2022 Control 8.32 (Change Management)
- ISO 27001 Annex A 8.32 Control Attributes
Key Takeaways
- Changes must be managed and not ad-hoc.
- Its purpose is to stop “good intentions” from causing security incidents, ensuring that every upgrade, patch, or configuration tweak is assessed for risk before it happens.
ISO 27001 Annex A 8.32 Purpose & Definition
The ISO 27001 Standard defines ISO 27001 Annex A 8.32 as:
Changes to information processing facilities and information systems should be subject to change management procedures.
ISO/IEC 27001:2022 Annex A 8.32 Change Management Complete Guide
This rule is a simple idea: You must manage changes in a safe, controlled way.
It means that whenever you plan to change something important about your IT systems, networks, or business processes, you need to check first to see if that change will hurt your security.
You need a clear plan or process that makes you stop and ask:
- What are we changing?
- Why are we changing it?
- Will this change create a new security risk?
- Who needs to say “yes” before we start?
- How will we check it works afterward?
The Consultant-Grade ISMS.
Stop building ISO 27001 from scratch. Steal our playbook. Download the exact, battle-tested documentation a Lead Auditor uses to certify clients. Fully white-labeled, guaranteed to pass, and ready to deploy today.
✓ The complete ISMS
✓ Proven to Pass Certification Audits
✓ 100% White-Label & Brandable
Change management guidelines
You are going to make sure that you have documented change guidelines. These can be standard guidelines or industry best practice, and you likely already do this today, just make sure that this written down, communicated and available to those that need it.
There are nine essential elements of a comprehensive Change Management as covered the control guidance in ISO 27002:2022 Control 8.32 (Change Management):
- Impact Assessment: Thoroughly assess and plan for the potential impact of all planned changes, considering all dependencies.
- Authorisation Controls: Implement robust authorisation controls for all proposed changes.
- Stakeholder Communication: Effectively communicate planned changes to all relevant internal and external stakeholders.
- Rigorous Testing: Establish and execute rigorous testing and acceptance testing processes for all changes.
- Implementation Strategy: Define a clear and detailed implementation strategy, including practical deployment procedures.
- Emergency and Contingency Planning: Develop and maintain comprehensive emergency and contingency plans, including a fallback procedure.
- Comprehensive Record Keeping: Maintain detailed records of all changes and related activities.
- Documentation Updates: Review and update all relevant operating documentation and user procedures to reflect the changes.
- ICT Continuity Plan Review: Review and revise all ICT continuity plans, recovery, and response procedures to accommodate the changes.
For change management you need documented roles, responsibilities, processes and procedures.
Change management is not overly complex although it can be a documentation overhead. Be sure to document everything and have evidence of past changes for the auditor to review.
How to implement ISO 27001 Change Management (Annex A 8.32)
Change management can be a profession in it’s own right and this control is no substitute for that. What we are going to do is manage our changes to the information processing facilities for in-scope products and services and we are going to manage changes to the information security management system.
Included in your change management implementation will be consideration for the following:
- Planning of Change
- Impact Assessment of Change
- Risk Assessment of Change
- Communication of Change
- Test and Acceptance of Change
- Deployment Plans for Changes
- Back out/ rollback Procedures for failed changes
- Records of Change
- Updated Documentation as a result of change
- Updated Business Continuity and Disaster Recovery as a result of change
1. Formalise the Change Management Policy and Scope
Define the governance framework for what constitutes a “change” versus “business as usual” maintenance to prevent unauthorised modifications.
- Define criteria for Standard, Normal, and Emergency changes.
- Appoint a Change Advisory Board (CAB) with cross-functional representation.
- Document a clear “Definition of Ready” for production deployments.
2. Establish a Centralised Request for Change (RFC) Workflow
Provision a technical system of record to capture all modification requests, ensuring a complete audit trail for external compliance audits.
- Implement a ticketing system (e.g., Jira Service Management or ServiceNow) to track RFC status.
- Mandate technical descriptions, business justification, and primary stakeholders for every request.
- Assign unique identifiers to every change to link commits in version control to specific RFCs.
3. Conduct Technical Impact and Security Risk Assessments
Analyze the potential security degradation resulting from a change by evaluating dependencies and vulnerability surfaces.
- Perform automated dependency scanning and SAST/DAST testing for software changes.
- Evaluate the impact on existing IAM roles and network segmentation (VLANs/Firewall rules).
- Execute a formal risk assessment for high-impact changes to identify potential availability or confidentiality breaches.
4. Execute Testing, Validation, and Quality Assurance
Validate the technical integrity of the change in a segregated staging environment that mirrors production configurations.
- Execute User Acceptance Testing (UAT) and document sign-offs from system owners.
- Run regression testing to ensure existing security controls remain effective post-implementation.
- Verify that audit logging remains active and correctly formatted during the testing phase.
5. Authorise and Deploy with Rollback Protocols
Transition changes to production using Principle of Least Privilege (PoLP) and a verified “back-out” strategy.
- Formalise a “Point of No Return” and document detailed rollback procedures for failed deployments.
- Provision temporary elevated access (Just-In-Time access) for engineers performing the deployment.
- Schedule deployments during low-impact windows and communicate the maintenance window to stakeholders.
6. Perform Post-Implementation Review (PIR) and Logging
Finalise the change lifecycle by verifying successful implementation and closing the feedback loop for continuous improvement.
- Analyze system logs and performance metrics to confirm the change achieved the intended result.
- Conduct a Post-Implementation Review (PIR) for any change that resulted in an incident or required a rollback.
- Update configuration management databases (CMDB) and technical documentation to reflect the new state.
The High Table ISO 27001 Internal Audit.
ISO 27001 strictly requires impartiality – you cannot audit your own work. If you implemented the ISMS, you must use an independent expert before the certification body arrives. Book your ISO 27001 Internal Audit with High Table and let Lead Auditor Stuart Barker’s team guarantee your certification readiness.
✓ 100% Independent & Impartial
✓ Conducted by Certified Lead Auditors
✓ Fixed-Price, Zero-Friction Process

ISO 27001 Annex A 8.32 Toolkit & Templates
Change Management Policy Template
It can be confusing to work out what to include in a change management policy or where to start.
An ISO 27001 Policy Template that is pre written and ready to go can save you a lot of heart ache so that is why we have done the heavy lifting with the ISO 27001 Change Management Policy Template.
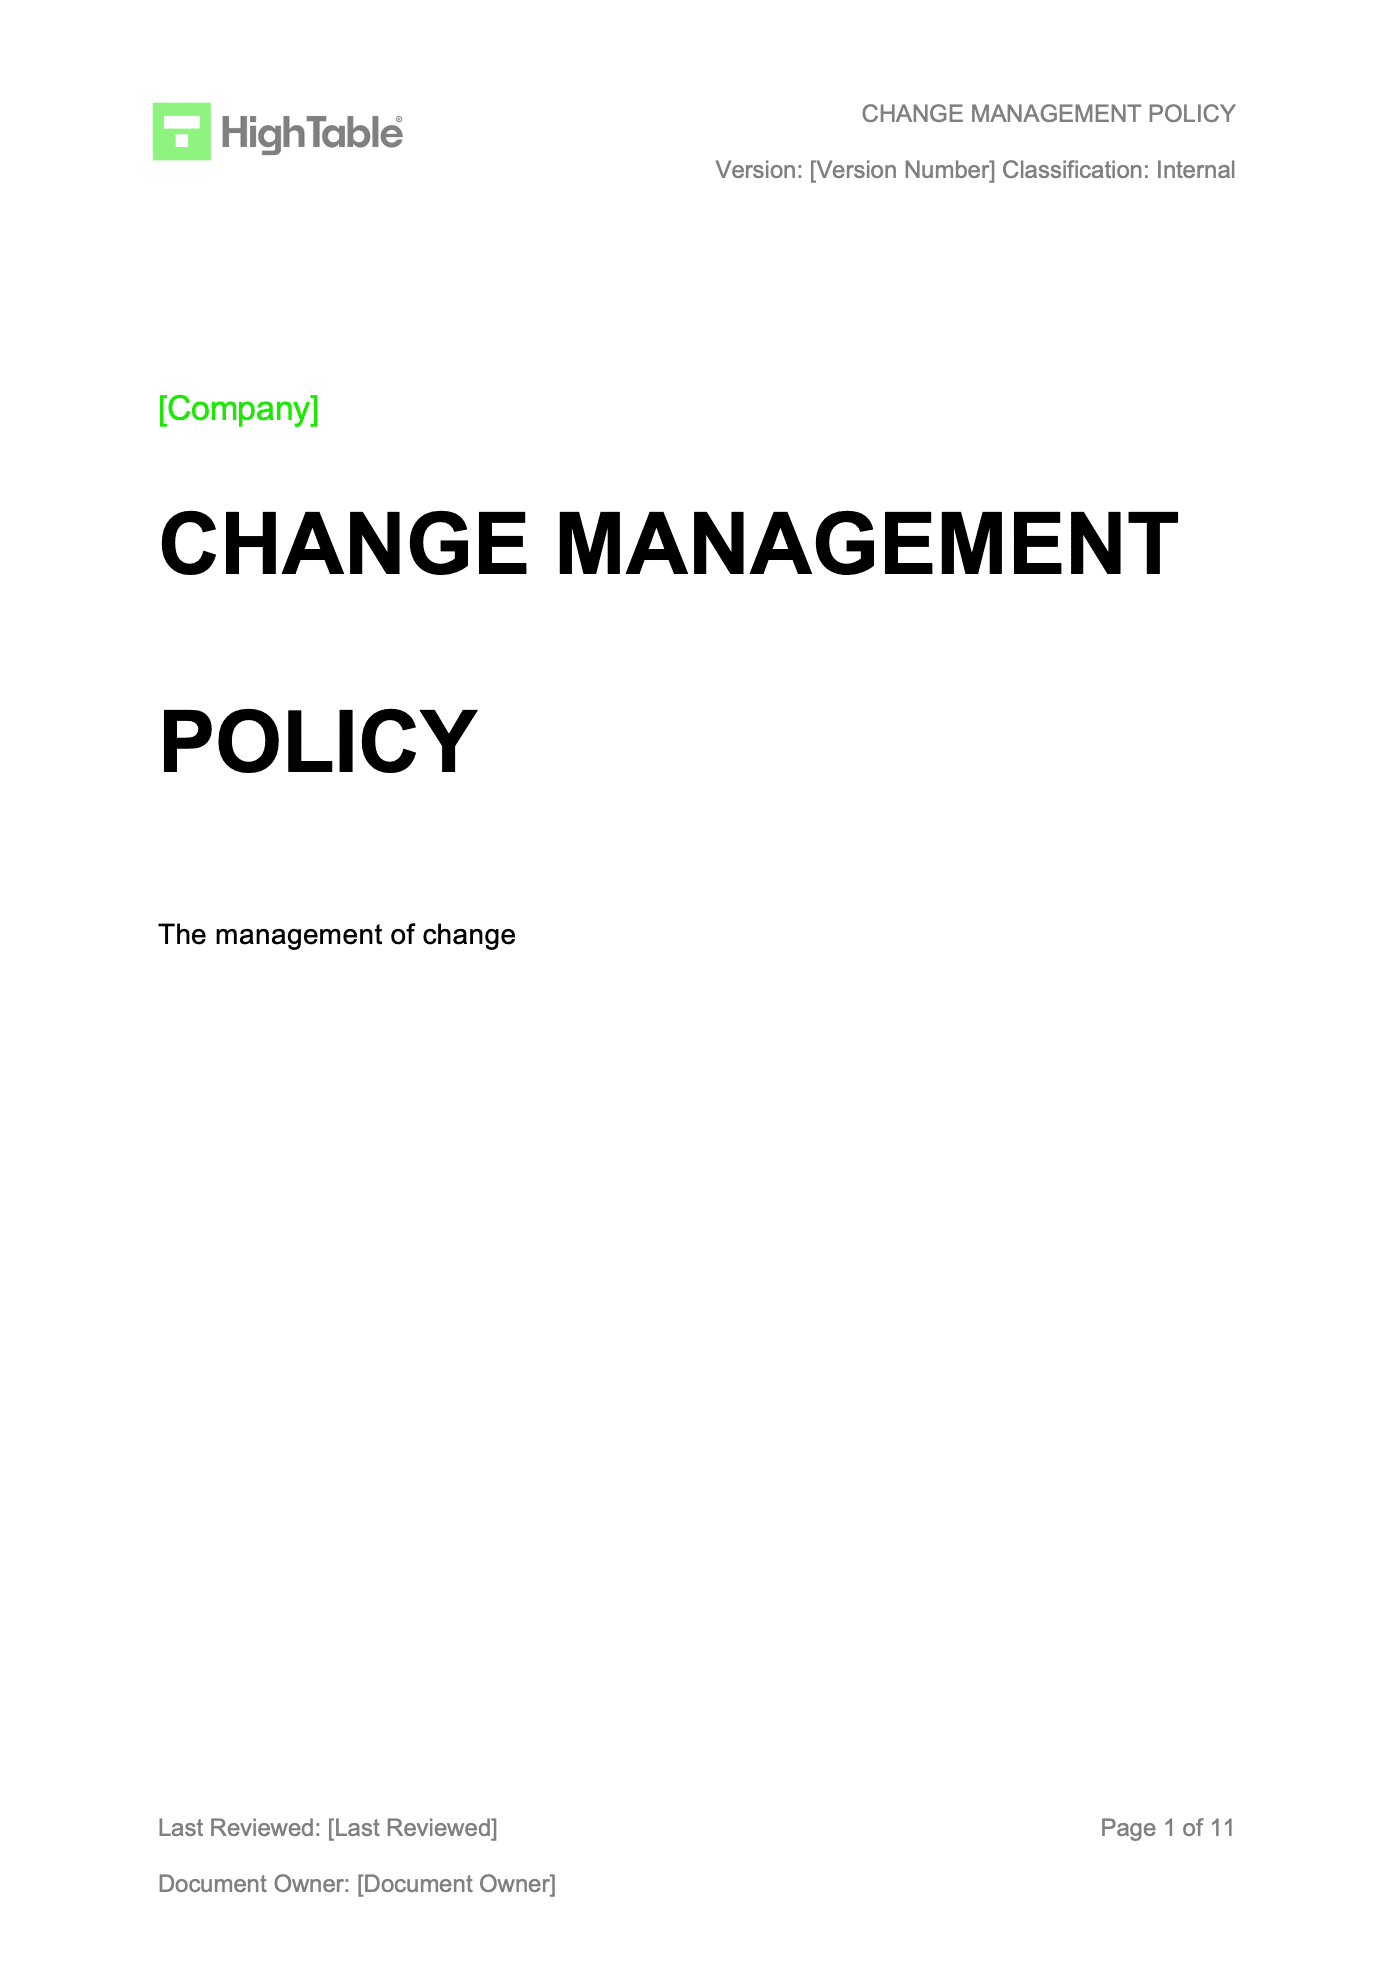
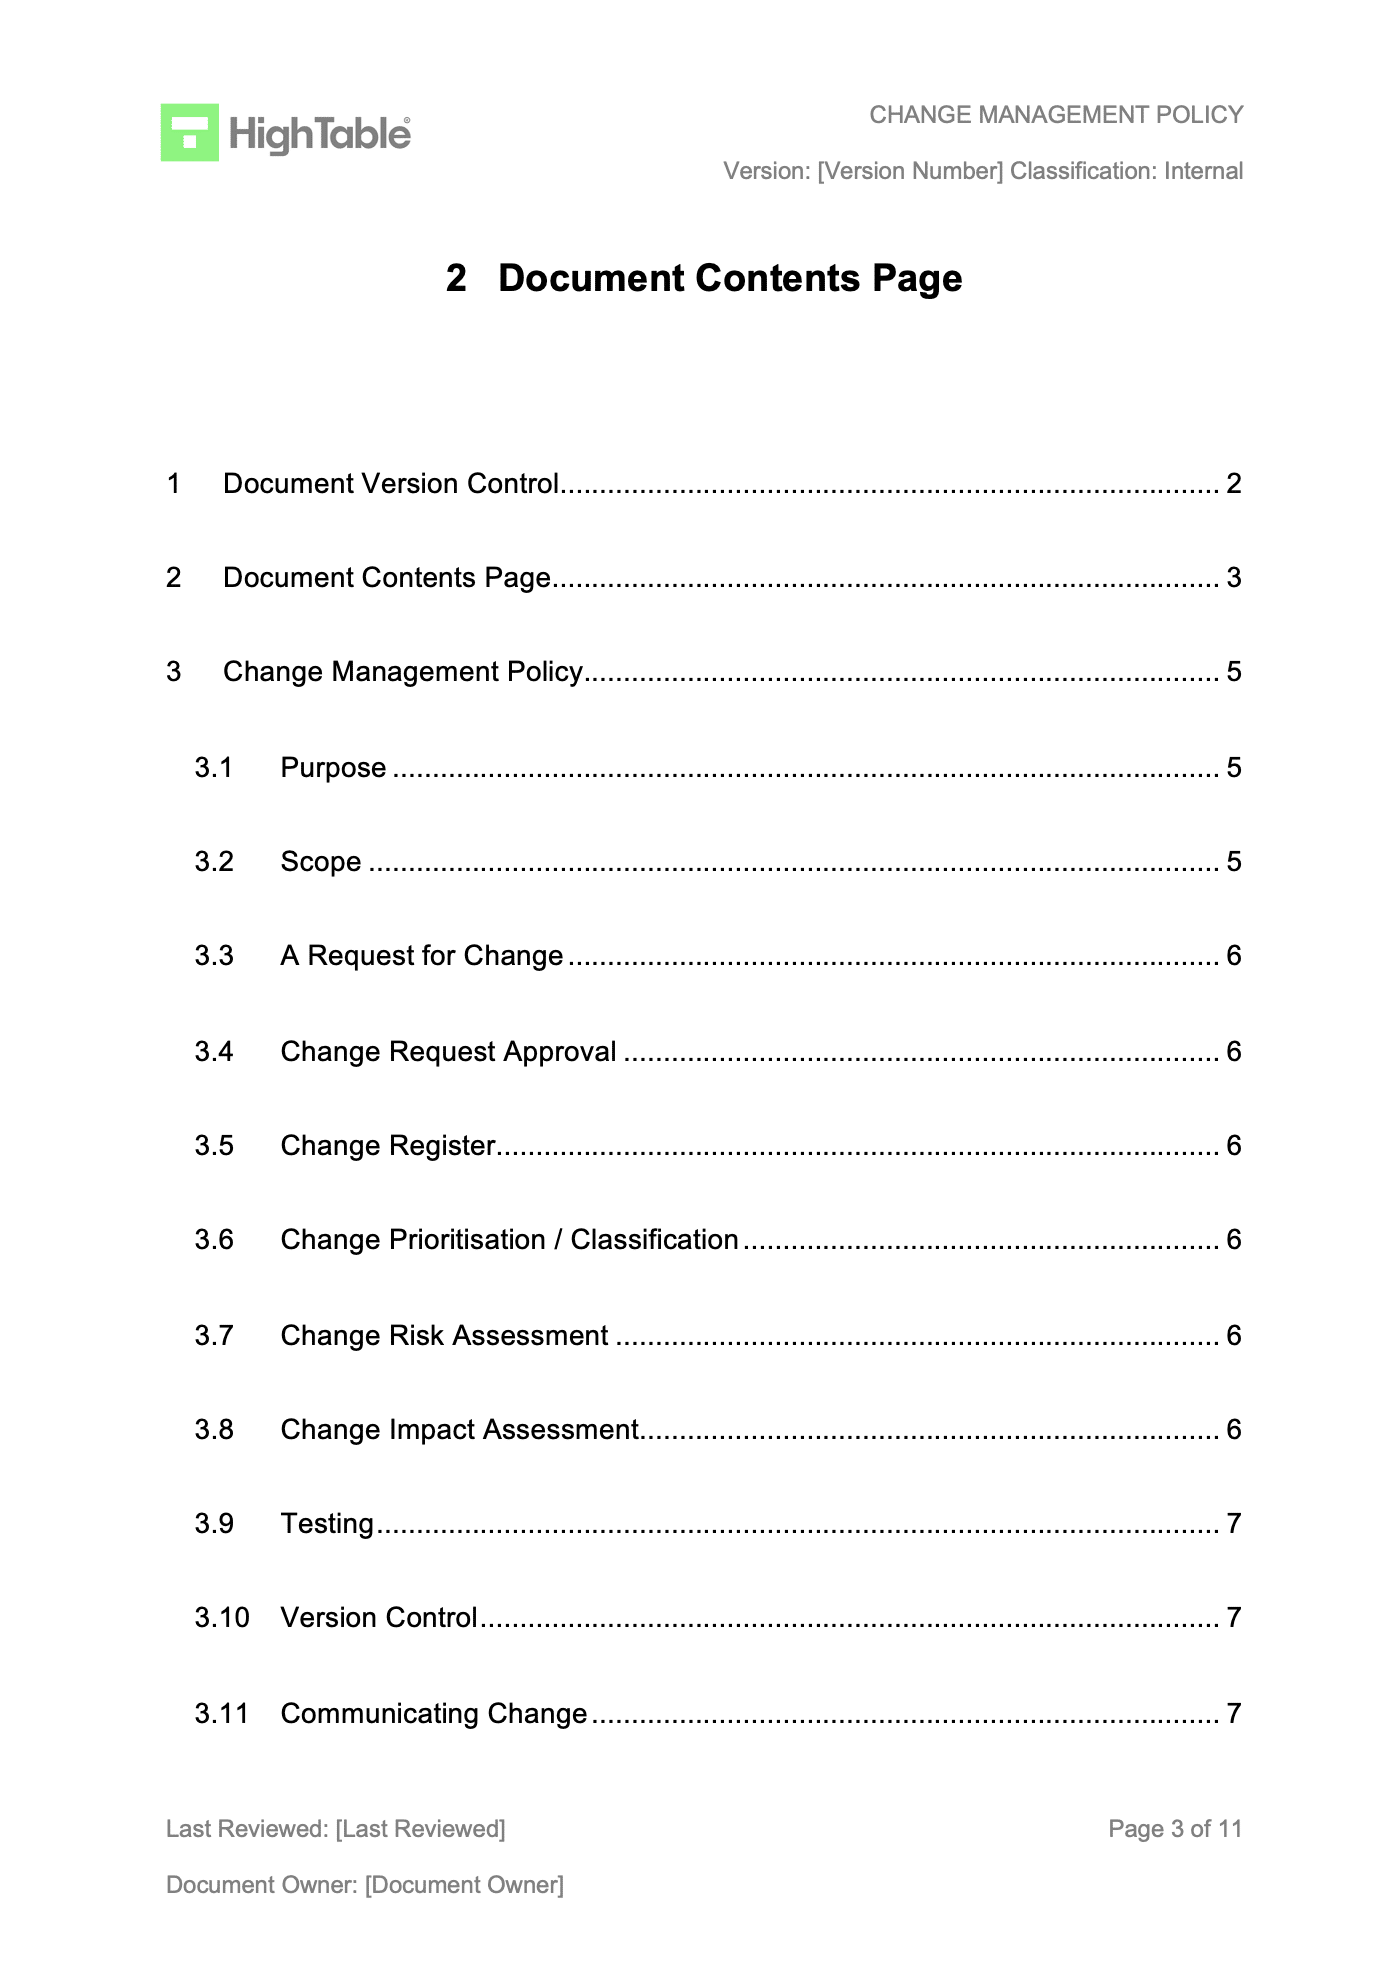
ISO 27001 Change Management Policy Example
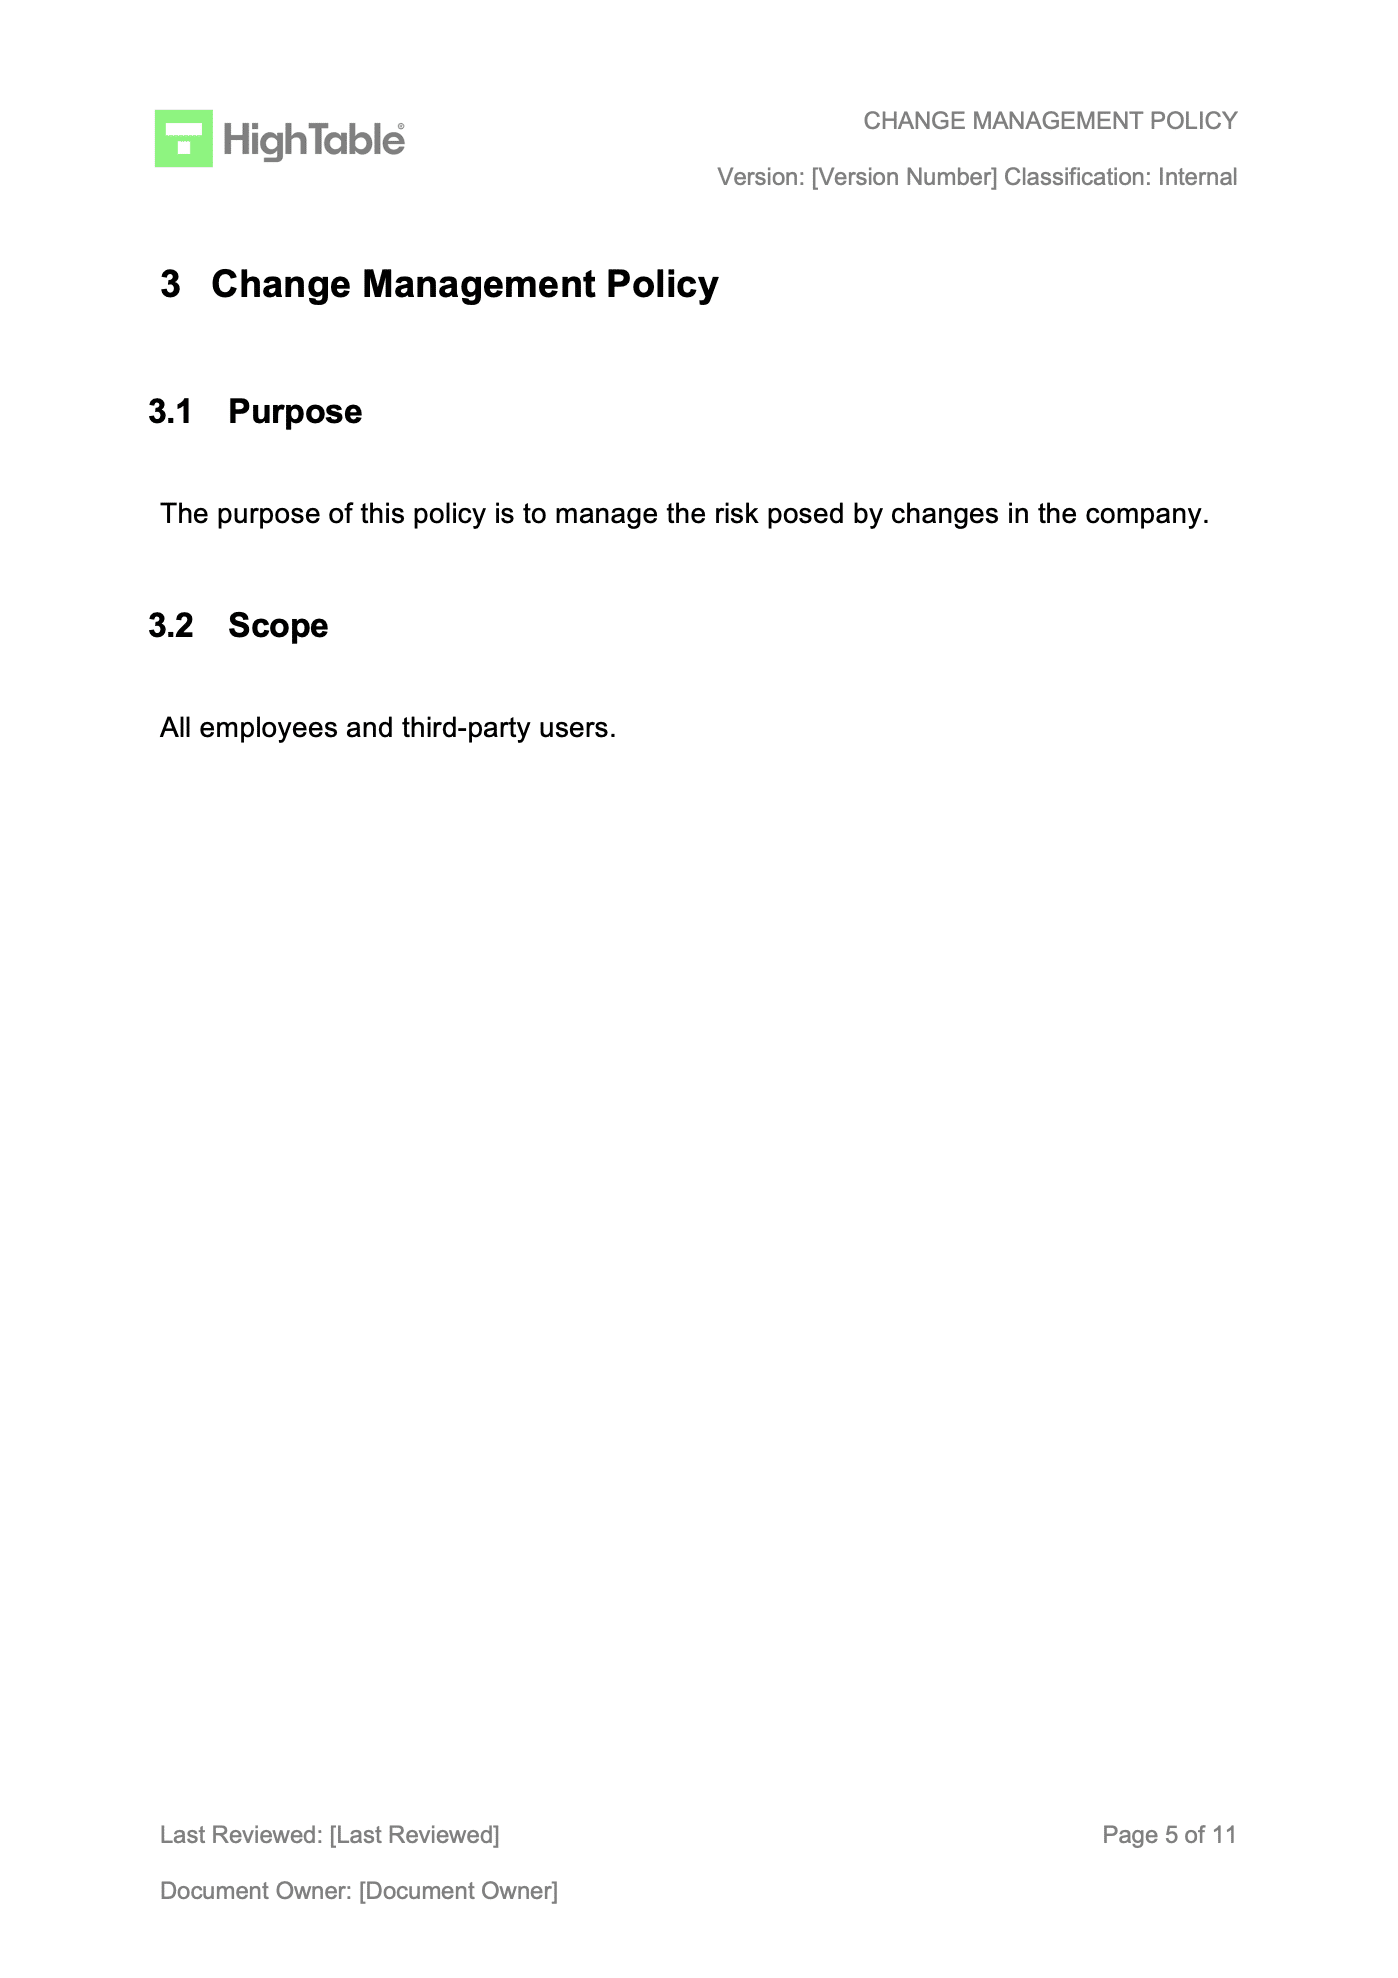
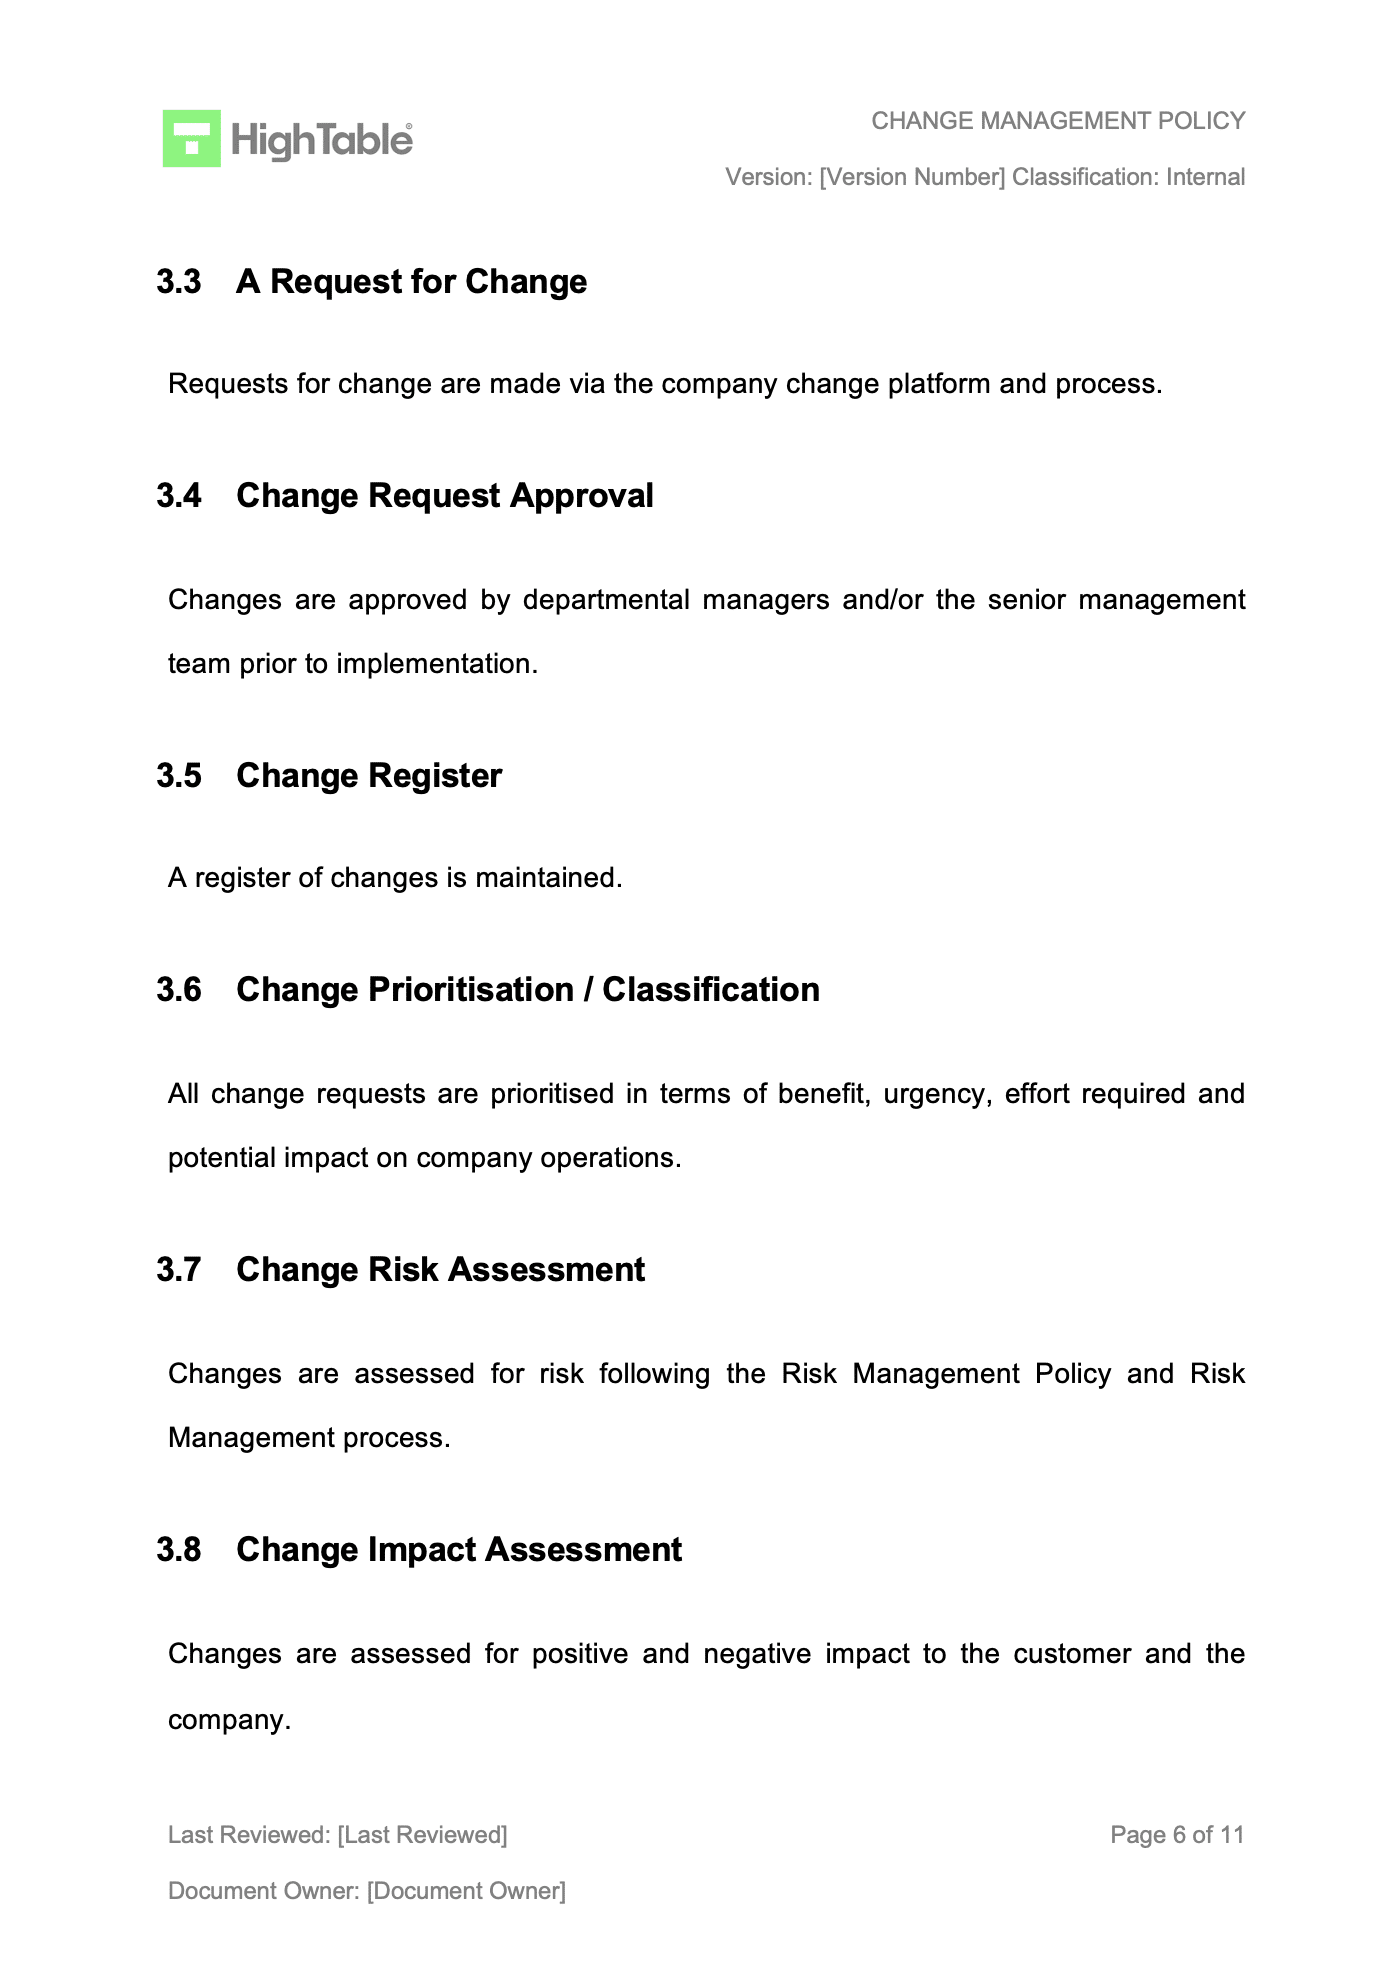
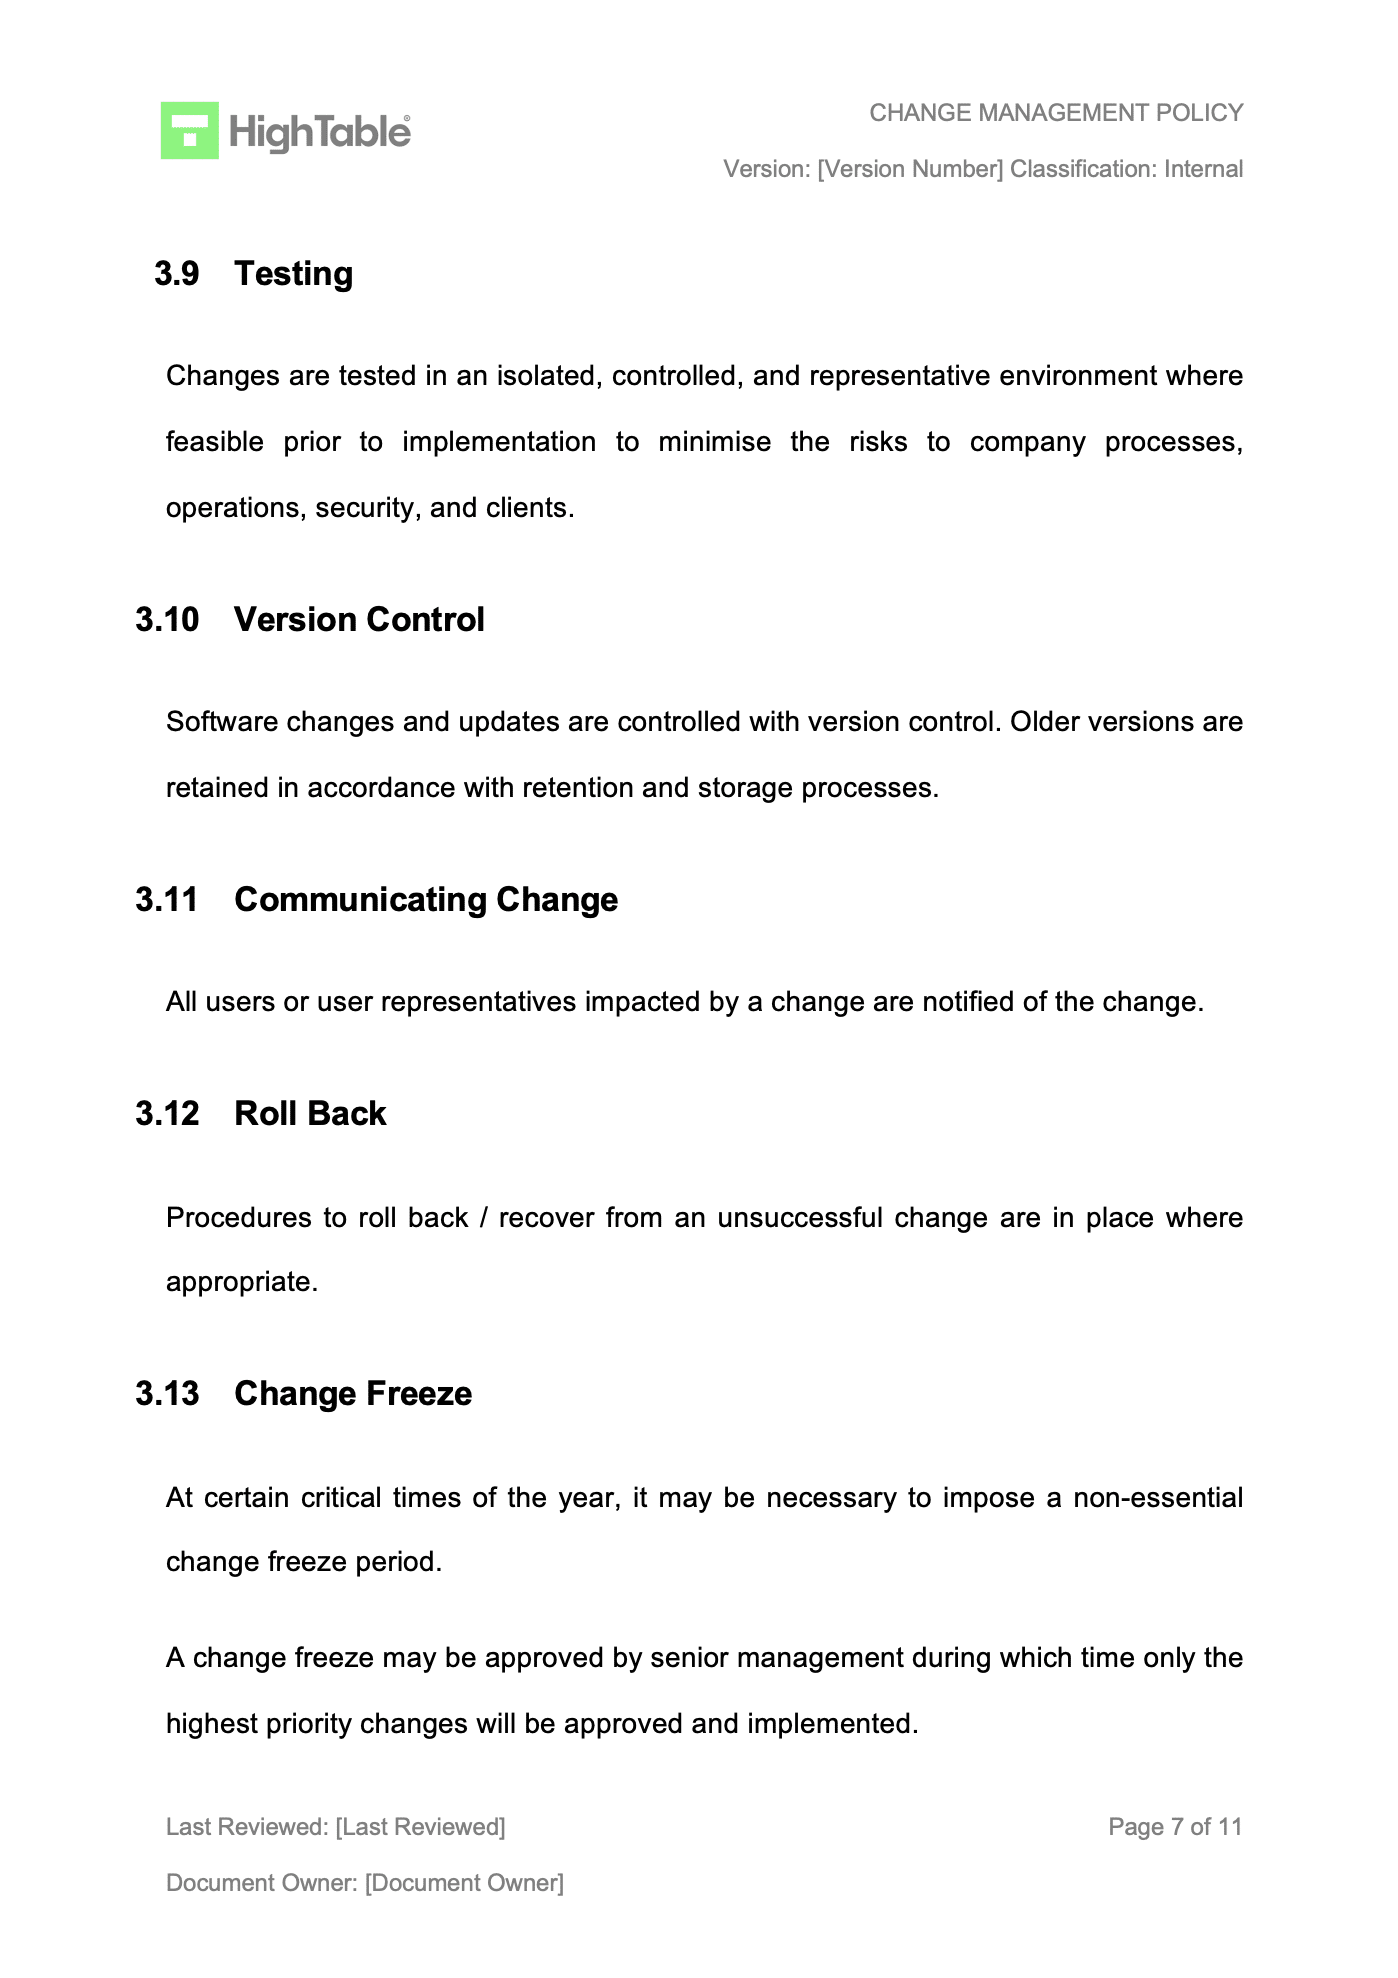
The following is an example change management policy for ISO 27001.
ISO 27001 Toolkit
Everything a business needs to do ISO 27001 and get ISO 27001 certified in the High Table ISO 27001 Toolkit: Business Edition.
How to audit ISO 27001 Annex A 8.32
To conduct an internal audit of ISO 27001 Annex A 8.32 Change Management use the following audit checklist:
- Verify the Change Management Process Documentation
- Gather Evidence of Changes
- Assess the Rigour of Impact Assessments
- Check for Formal Authorisations
- Audit the Implementation and Technical Testing
- Review Communication to Stakeholders
- Audit Post-Implementation Reviews (PIR)
- Review Documented Changes to the ISMS
- Evaluate Integration with Key ISMS Processes
- Assess Continual Improvement of the Process
Related ISO 27001:2022 Annex A Controls
The ISO 27001:2022 standard has specific controls that relate to change management:
- ISO 27001:2022 Annex A 8.29 Security Testing in Development and Acceptance
- ISO 27001:2022 Annex A 5.25 Assessment And Decision On Information Security Events
- ISO 27001: Annex A 8.34 Protection of Information Systems During Audit Testing
ISO 27002:2022 Control 8.32 (Change Management)
ISO 27002 Control 8.32 provides implementation guidance for Change Management.
ISO 27001 Annex A 8.32 Control Attributes
| Control type | Information security properties | Cybersecurity concepts | Operational capabilities | Security domains |
|---|---|---|---|---|
| Preventive | Confidentiality | Protect | Information Protection | Protection |
| Integrity | Application Security | |||
| Availability | System and Network Security |
Stuart Barker
Stuart Barker is a qualified ISO 27001 Lead Auditor and veteran practitioner with over 30 years of experience in systems security and risk management. Holding an MSc in Software and Systems Security, he combines academic rigour with extensive operational experience, including a decade leading Data Governance for General Electric (GE).
He is the founder of High Table and the Lead Consultant driving the world’s number 1 dedicated ISO 27001 Consultancy.
